





CVE-2023-1177: MLflow get-artifact 任意文件读取漏洞
漏洞标题 CVE-2023-1177: MLflow get-artifact 任意文件读取漏洞 漏洞描述 使用 MLflow 模型注册表托管 MLflow 开源项目的用户 mlflow server或者 mlflow ui使用早于 MLflow 2.2.1 的 MLflow 版...
CVE-2015-8399: Atlassian Confluence configuration files read
漏洞标题 CVE-2015-8399: Atlassian Confluence configuration files read 漏洞描述 Atlassian Confluence before 5.9.1 allows remote attackers to read arbitrary files via a crafted reque...
CVE-2023-1020: Steveas WP Live Chat Shoutbox <= 1.4.2 - SQL Injection
漏洞标题 CVE-2023-1020: Steveas WP Live Chat Shoutbox <= 1.4.2 - SQL Injection 漏洞描述 The Steveas WP Live Chat Shoutbox WordPress plugin through 1.4.2 does not sanitise and es...
CVE-2021-24219: All Thrive Themes and Plugins – Unauthenticated Option Update
漏洞标题 CVE-2021-24219: All Thrive Themes and Plugins - Unauthenticated Option Update 漏洞描述 The Thrive Optimize WordPress plugin before 1.4.13.3, Thrive Comments WordPress plug...
CVE-2022-2756: Kavita <0.5.4.1 - Server-Side Request Forgery
漏洞标题 CVE-2022-2756: Kavita <0.5.4.1 - Server-Side Request Forgery 漏洞描述 Kavita before 0.5.4.1 is susceptible to server-side request forgery in GitHub repository kareadita...

对docker中的overlay式网络详解_docker
这篇文章主要介绍了对docker中的overlay式网络详解,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 翻译自docker官方文档,原文:http://docs.docker.com/network/overlay/ ...
(CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞
漏洞标题 (CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞 漏洞描述 (CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞 PoC代码 暂无
Adobe Connect < 12.1.5文件泄露(CVE-2023-22232)
漏洞标题 Adobe Connect < 12.1.5文件泄露(CVE-2023-22232) 漏洞描述 Adobe Connect版本11.4.5(及更早版本)、12.1.5(及较早版本)受到不当访问控制漏洞的影响,该漏洞可能导致绕过安全功...
CVE-2021-24370: WordPress Fancy Product Designer <4.6.9 - Arbitrary File Upload
漏洞标题 CVE-2021-24370: WordPress Fancy Product Designer <4.6.9 - Arbitrary File Upload 漏洞描述 WordPress Fancy Product Designer plugin before 4.6.9 is susceptible to an arbit...
CVE-2018-8823: PrestaShop Responsive Mega Menu Module – Remote Code Execution
漏洞标题 CVE-2018-8823: PrestaShop Responsive Mega Menu Module - Remote Code Execution 漏洞描述 The 'Responsive Mega Menu' module for PrestaShop is prone to a remote code...
CVE-2019-7139: Magento – SQL Injection
漏洞标题 CVE-2019-7139: Magento - SQL Injection 漏洞描述 An unauthenticated user can execute SQL statements that allow arbitrary read access to the underlying database, which cause...
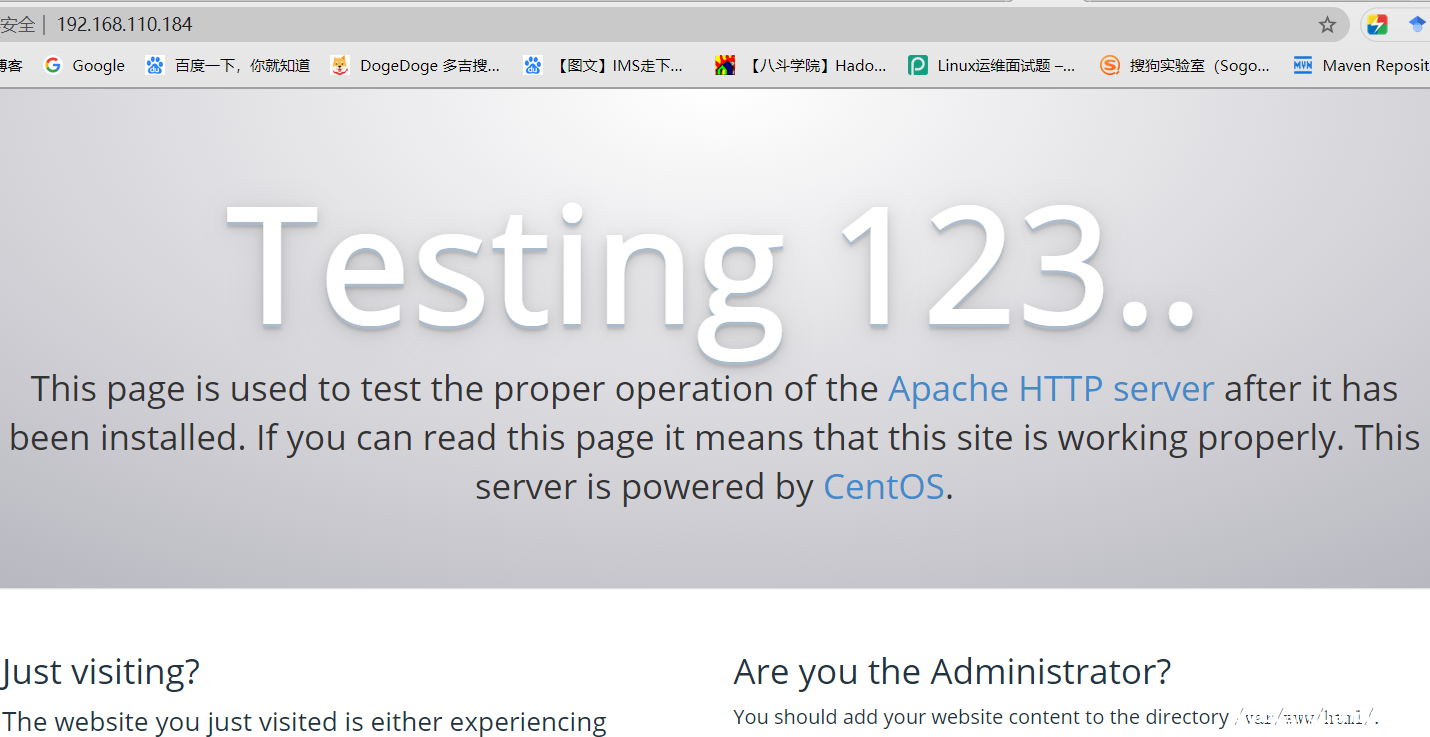
linux下使用Apache搭建文件服务器的步骤_Linux
这篇文章主要介绍了linux下使用Apache搭建文件服务器的步骤,帮助大家更好的搭建服务器,感兴趣的朋友可以了解下 一.关于文件服务器 在一个项目中,如果想把公共软件或者资料共享给项目组成员,...
linux内核copy_{to, from}_user()的思考_Linux
本文即将介绍copy_{to,from}_user()接口的使用应,它是kernel space和user space沟通的桥梁,接下来一起学习学习吧 目录一、什么是copy_{to,from}_user()1、copy_{to,from}_user()对比memcpy()2...
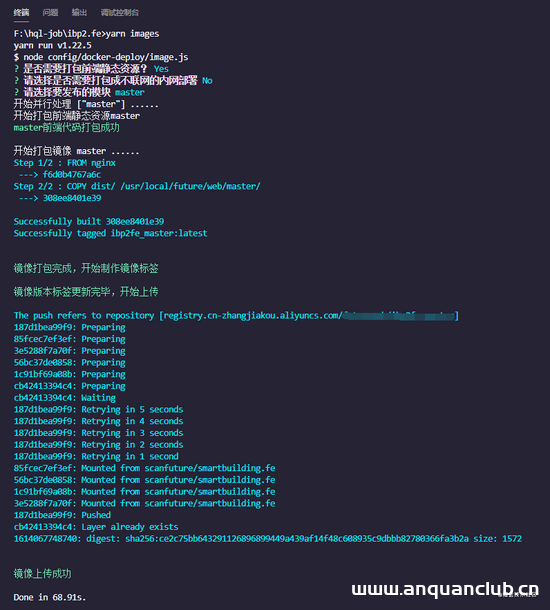
使用脚本一键打包并上传docker镜像的实现代码_docker
这篇文章主要介绍了使用脚本一键打包并上传docker镜像的实现代码,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 笔者搞了一年多微前端项目,一个...
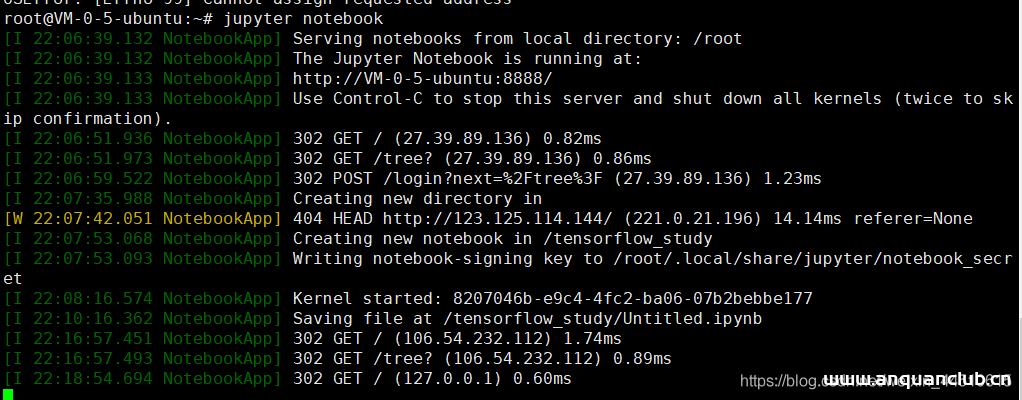
解决服务器运行jupyter notebook方法_服务器其它
这篇文章主要介绍了解决服务器运行jupyter notebook方法,来帮助大家实现服务器跑Jupyter,附含图文以及详细代码,有需要的朋友可以借鉴参考下 目录服务器运行jupyter notebook虚拟环境然后关防...
CVE-2023-5815: News & Blog Designer Pack – WordPress Blog Plugin <= 3.4.1 - Unauthenticated Local File Inclusion
漏洞标题 CVE-2023-5815: News & Blog Designer Pack – WordPress Blog Plugin <= 3.4.1 - Unauthenticated Local File Inclusion 漏洞描述 The News & Blog Designer Pack WordPre...

