





CVE-2022-0817: WordPress BadgeOS <=3.7.0 - SQL Injection
漏洞标题 CVE-2022-0817: WordPress BadgeOS <=3.7.0 - SQL Injection 漏洞描述 WordPress BadgeOS plugin through 3.7.0 contains a SQL injection vulnerability. It does not sanitize an...
Apache OFBiz CVE-2024-32113 目录遍历漏洞
漏洞标题 Apache OFBiz CVE-2024-32113 目录遍历漏洞 漏洞描述 Apache OFBiz 存在目录遍历漏洞,此漏洞是由于未充分验证用户输入的url所导致的。 PoC代码 暂无
copyparty 低于1.8.2 版本存在任意文件读取漏洞(CVE-2023-37474)
漏洞标题 copyparty 低于1.8.2 版本存在任意文件读取漏洞(CVE-2023-37474) 漏洞描述 Copyparty是一个便携式文件服务器,copyparty 低于1.8.2 版本存在任意文件读取漏洞 PoC代码 暂无
CVE-2023-40000: LiteSpeed Cache <= 5.7 - Unauthenticated Stored XSS
漏洞标题 CVE-2023-40000: LiteSpeed Cache <= 5.7 - Unauthenticated Stored XSS 漏洞描述 Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting...
CVE-2022-0948: WordPress Order Listener for WooCommerce <3.2.2 - SQL Injection
漏洞标题 CVE-2022-0948: WordPress Order Listener for WooCommerce <3.2.2 - SQL Injection 漏洞描述 WordPress Order Listener for WooCommerce plugin before 3.2.2 contains a SQL inje...
CVE-2022-1390: WordPress Admin Word Count Column 2.2 – Local File Inclusion
漏洞标题 CVE-2022-1390: WordPress Admin Word Count Column 2.2 - Local File Inclusion 漏洞描述 The plugin does not validate the path parameter given to readfile(), which could allow...
CVE-2023-4596: WordPress Plugin Forminator 1.24.6 – Arbitrary File Upload
漏洞标题 CVE-2023-4596: WordPress Plugin Forminator 1.24.6 - Arbitrary File Upload 漏洞描述 The Forminator plugin for WordPress is vulnerable to arbitrary file uploads due to file ...
CVE-2017-14524: OpenText Documentum Administrator 7.2.0180.0055 – Open Redirect
漏洞标题 CVE-2017-14524: OpenText Documentum Administrator 7.2.0180.0055 - Open Redirect 漏洞描述 OpenText Documentum Administrator 7.2.0180.0055 is susceptible to multiple open re...
CVE-2023-38879: openSIS v9.0 – Path Traversal
漏洞标题 CVE-2023-38879: openSIS v9.0 - Path Traversal 漏洞描述 A path traversal vulnerability exists in openSIS Classic Community Edition v9.0 via the 'filename' paramet...
Carel pCOWeb
漏洞标题 Carel pCOWeb <B1.2.4 XSS (CVE-2019-11370) 漏洞描述 B1.2.4之前的Carel pCOWeb易受存储的跨站点脚本攻击,如config/pw_snmp.html“系统联系人”字段所示。 PoC代码 暂无
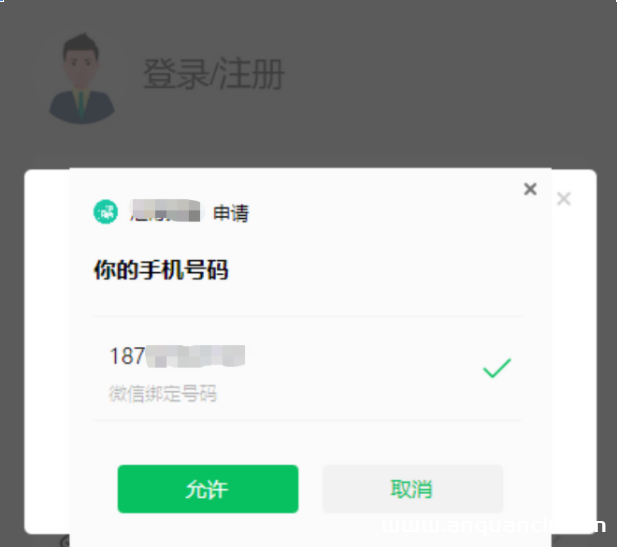
微信小程序SessionKey导致的任意手机号接管
如果小程序存在手机号快捷登录,首先需要获取微信用户绑定的手机号。先调用wx.login接口,由用户主动触发来获取手机号。微信小程序存在EncryptedData、SessionKey、IV来进行加密的机制,Encrypt...
(CVE-2025-55747) XWiki Platform配置文件信息泄露漏洞
漏洞标题 (CVE-2025-55747) XWiki Platform配置文件信息泄露漏洞 漏洞描述 (CVE-2025-55747) XWiki Platform配置文件信息泄露漏洞 PoC代码 暂无
CVE-2017-5638: Apache Struts 2 – Remote Command Execution S2-045 S2-046
漏洞标题 CVE-2017-5638: Apache Struts 2 - Remote Command Execution S2-045 S2-046 漏洞描述 Apache Struts 2 2.3.x before 2.3.32 and 2.5.x before 2.5.10.1 is vulnerable to remote comm...
CVE-2017-9791: Apache Struts2 S2-053 – Remote Code Execution
漏洞标题 CVE-2017-9791: Apache Struts2 S2-053 - Remote Code Execution 漏洞描述 Apache Struts 2.1.x and 2.3.x with the Struts 1 plugin might allow remote code execution via a malici...
CVE-2023-25573: Metersphere – Arbitrary File Read
漏洞标题 CVE-2023-25573: Metersphere - Arbitrary File Read 漏洞描述 Metersphere is an open source continuous testing platform. In affected versions an improper access control vulne...
CVE-2023-29357: Microsoft SharePoint – Authentication Bypass
漏洞标题 CVE-2023-29357: Microsoft SharePoint - Authentication Bypass 漏洞描述 Microsoft SharePoint Server Elevation of Privilege Vulnerability PoC代码

