





CVE-2021-29622: Prometheus – Open Redirect
漏洞标题 CVE-2021-29622: Prometheus - Open Redirect 漏洞描述 Prometheus 2.23.0 through 2.26.0 and 2.27.0 contains an open redirect vulnerability. To ensure a seamless transition to...
CVE-2010-1345: Joomla! Component Cookex Agency CKForms – Local File Inclusion
漏洞标题 CVE-2010-1345: Joomla! Component Cookex Agency CKForms - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Cookex Agency CKForms (com_ckforms) compo...
CVE-2010-1714: Joomla! Component Arcade Games 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1714: Joomla! Component Arcade Games 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Arcade Games (com_arcadegames) component 1.0 f...
CVE-2024-5230: FleetCart 4.1.1 – Information Disclosure
漏洞标题 CVE-2024-5230: FleetCart 4.1.1 - Information Disclosure 漏洞描述 Issues with information disclosure in redirect responses. Accessing the majority of the website's pag...
CVE-2020-35713: Belkin Linksys RE6500 <1.0.012.001 - Remote Command Execution
漏洞标题 CVE-2020-35713: Belkin Linksys RE6500 <1.0.012.001 - Remote Command Execution 漏洞描述 Belkin LINKSYS RE6500 devices before 1.0.012.001 allow remote attackers to execut...
CVE-2019-18394: Ignite Realtime Openfire <=4.4.2 - Server-Side Request Forgery
漏洞标题 CVE-2019-18394: Ignite Realtime Openfire <=4.4.2 - Server-Side Request Forgery 漏洞描述 Ignite Realtime Openfire through version 4.4.2 allows attackers to send arbitrar...

Docker网络原理及自定义网络详细解析_docker
一般使用自定义网络,自定义网络使用network创建,创建时可以指定子网网段及网关等信息,在创建并启动容器时指定使用的网络,今天通过本文给大家介绍Docker网络原理及自定义网络的相关知识,感...
CVE-2010-0696: Joomla! Component Jw_allVideos – Arbitrary File Retrieval
漏洞标题 CVE-2010-0696: Joomla! Component Jw_allVideos - Arbitrary File Retrieval 漏洞描述 A directory traversal vulnerability in includes/download.php in the JoomlaWorks AllVideos...
CVE-2020-35476: OpenTSDB 2.4.0 Remote Code Execution
漏洞标题 CVE-2020-35476: OpenTSDB 2.4.0 Remote Code Execution 漏洞描述 A remote code execution vulnerability occurs in OpenTSDB through 2.4.0 via command injection in the yrange pa...
bugbounty技巧聚合20211124
漏洞报告 【XVIDEOS 】No-Rate limit of current password on delete account endpoint(http://www.xvideos.com/account/close) http://hackerone.com/reports/1392287 【DigitalOcean】Blind X...
Apache APISIX 默认密钥漏洞(CVE-2020-13945)
漏洞标题 Apache APISIX 默认密钥漏洞(CVE-2020-13945) 漏洞描述 Apache APISIX是一个高性能API网关。在用户未指定管理员Token或使用了默认配置文件的情况下,ApacheAPISIX将使用默认的管理员...
某src之报错页面导致的大量日志信息泄露
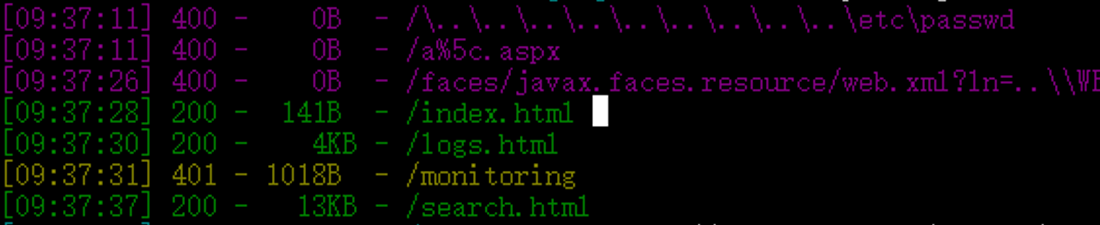
0x01 某天下午在看安全小天地资产时候发现了一个状态码为200,返回包却存在报错信息的报错界面。 由于漏洞已经修复,报错信息已经无,请自行脑补,大概就是报错出了一大堆东西,其中有个参数为...
CVE-2020-15895: D-Link DIR-816L 2.x – Cross-Site Scripting
漏洞标题 CVE-2020-15895: D-Link DIR-816L 2.x - Cross-Site Scripting 漏洞描述 D-Link DIR-816L devices 2.x before 1.10b04Beta02 contains a cross-site scripting vulnerability. In the ...
CVE-2024-13496: GamiPress <= 2.8.9 - SQL Injection
漏洞标题 CVE-2024-13496: GamiPress <= 2.8.9 - SQL Injection 漏洞描述 GamiPress WordPress plugin version 2.8.9 and below suffers from an SQL injection vulnerability due to insuff...
CVE-2022-0434: WordPress Page Views Count <2.4.15 - SQL Injection
漏洞标题 CVE-2022-0434: WordPress Page Views Count <2.4.15 - SQL Injection 漏洞描述 WordPress Page Views Count plugin prior to 2.4.15 contains an unauthenticated SQL injection v...
每日云安全技术资讯20220224
k8s多云 OpenShift 解决方案-RHACM http://telegra.ph/Red-Hat-and-Intel-Use-Red-Hat-Advanced-Cluster-Management-RHACM-for-Kubernetes-to-Manage-a-Multicloud-OpenShift-Solution---Hybri-...

