




linux No space left on device由索引节点(inode)爆满引发500问题_Linux
这篇文章主要介绍了linux No space left on device由索引节点(inode)爆满引发500问题,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小...

ubuntu中编写shell脚本开机自动启动(推荐)_Linux
这篇文章主要介绍了ubuntu中编写shell脚本开机自动启动,本文给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 编写脚本是为了不用手动去开启各种服务(也是为了偷懒哈哈) ...
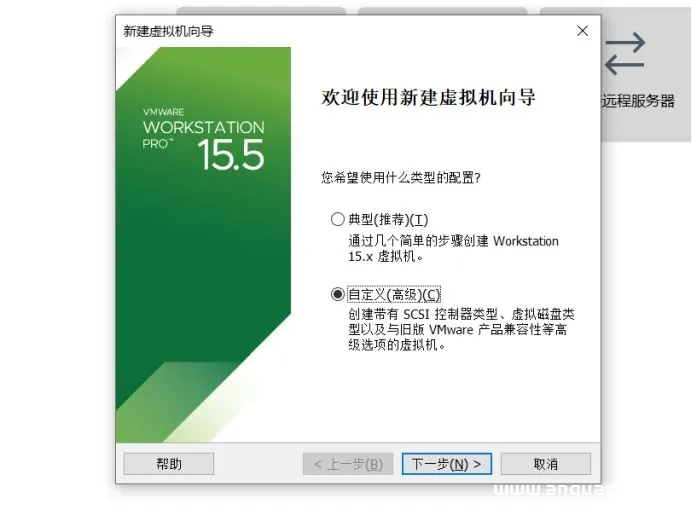
在VMware上 安装 centos8的详细教程_VMware
这篇文章主要介绍了VMware 安装 centos8的详细教程,本文图文并茂给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 centos官网地址 http://www.centos.org/ 首先下载好自己...

CVE-2020-24949: PHP-Fusion 9.03.50 – Remote Code Execution
漏洞标题 CVE-2020-24949: PHP-Fusion 9.03.50 - Remote Code Execution 漏洞描述 PHP-Fusion 9.03.50 downloads/downloads.php allows an authenticated user (not admin) to send a crafted r...
CVE-2015-9323: 404 to 301 <= 2.0.2 - Authenticated Blind SQL Injection
漏洞标题 CVE-2015-9323: 404 to 301 <= 2.0.2 - Authenticated Blind SQL Injection 漏洞描述 The 404 to 301 – Redirect, Log and Notify 404 Errors WordPress plugin was affected by a...

人物 | 悬镜安全宁戈:高山流水遇知音,湖畔筑梦中国心
2022年3月22日,悬镜安全宣布完成B轮融资。三年前,悬镜的CEO子芽,这位未名湖畔的筑梦人,接受了安在的采访,那时的悬镜刚刚完成产品由十年磨一剑的前沿技术研究到商业化落地的打磨实践阶段。...
CVE-2024-29972: Zyxel NAS326 Firmware < V5.21(AAZF.17)C0 - NsaRescueAngel Backdoor Account
漏洞标题 CVE-2024-29972: Zyxel NAS326 Firmware < V5.21(AAZF.17)C0 - NsaRescueAngel Backdoor Account 漏洞描述 The command injection vulnerability in the CGI program "remote_...
CVE-2025-8286: Güralp Systems FMUS Series – Unauthenticated Access
漏洞标题 CVE-2025-8286: Güralp Systems FMUS Series - Unauthenticated Access 漏洞描述 Güralp Systems FMUS Series Seismic Monitoring Devices expose an unauthenticated Telnet-based ...
CVE-2015-9414: WordPress Symposium <=15.8.1 - Cross-Site Scripting
漏洞标题 CVE-2015-9414: WordPress Symposium <=15.8.1 - Cross-Site Scripting 漏洞描述 WordPress Symposium through 15.8.1 contains a reflected cross-site scripting vulnerability v...
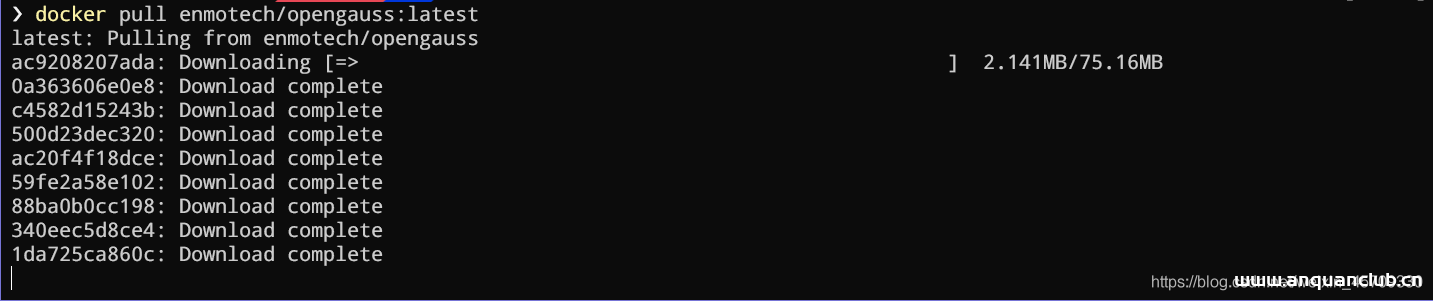
docker配置openGauss数据库的方法详解_docker
这篇文章主要介绍了docker配置openGauss数据库,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 For Windows User 在docker中使用openGauss ...
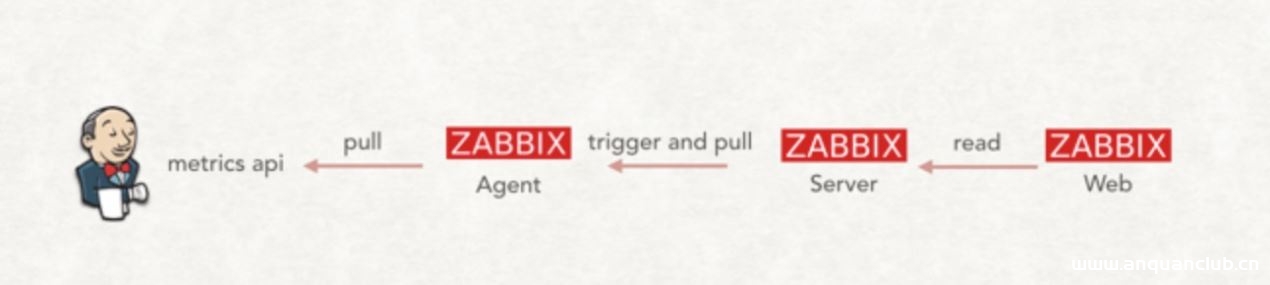
基于zabbix实现监控Jenkins过程详解_zabbix
这篇文章主要介绍了基于zabbix实现监控Jenkins过程详解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、监控架构图 二、实现思路 在 J...
CVE-2018-19877: Adiscon LogAnalyzer <4.1.7 - Cross-Site Scripting
漏洞标题 CVE-2018-19877: Adiscon LogAnalyzer <4.1.7 - Cross-Site Scripting 漏洞描述 Adiscon LogAnalyzer before 4.1.7 contains a cross-site scripting vulnerability in the 'r...
CVE-2025-2747: Kentico Xperience 13 CMS – Staging Service Authentication Bypass (WT-2025-0006)
漏洞标题 CVE-2025-2747: Kentico Xperience 13 CMS - Staging Service Authentication Bypass (WT-2025-0006) 漏洞描述 An authentication bypass vulnerability in Kentico Xperience allows ...
阿里云 OSS对象存储攻防
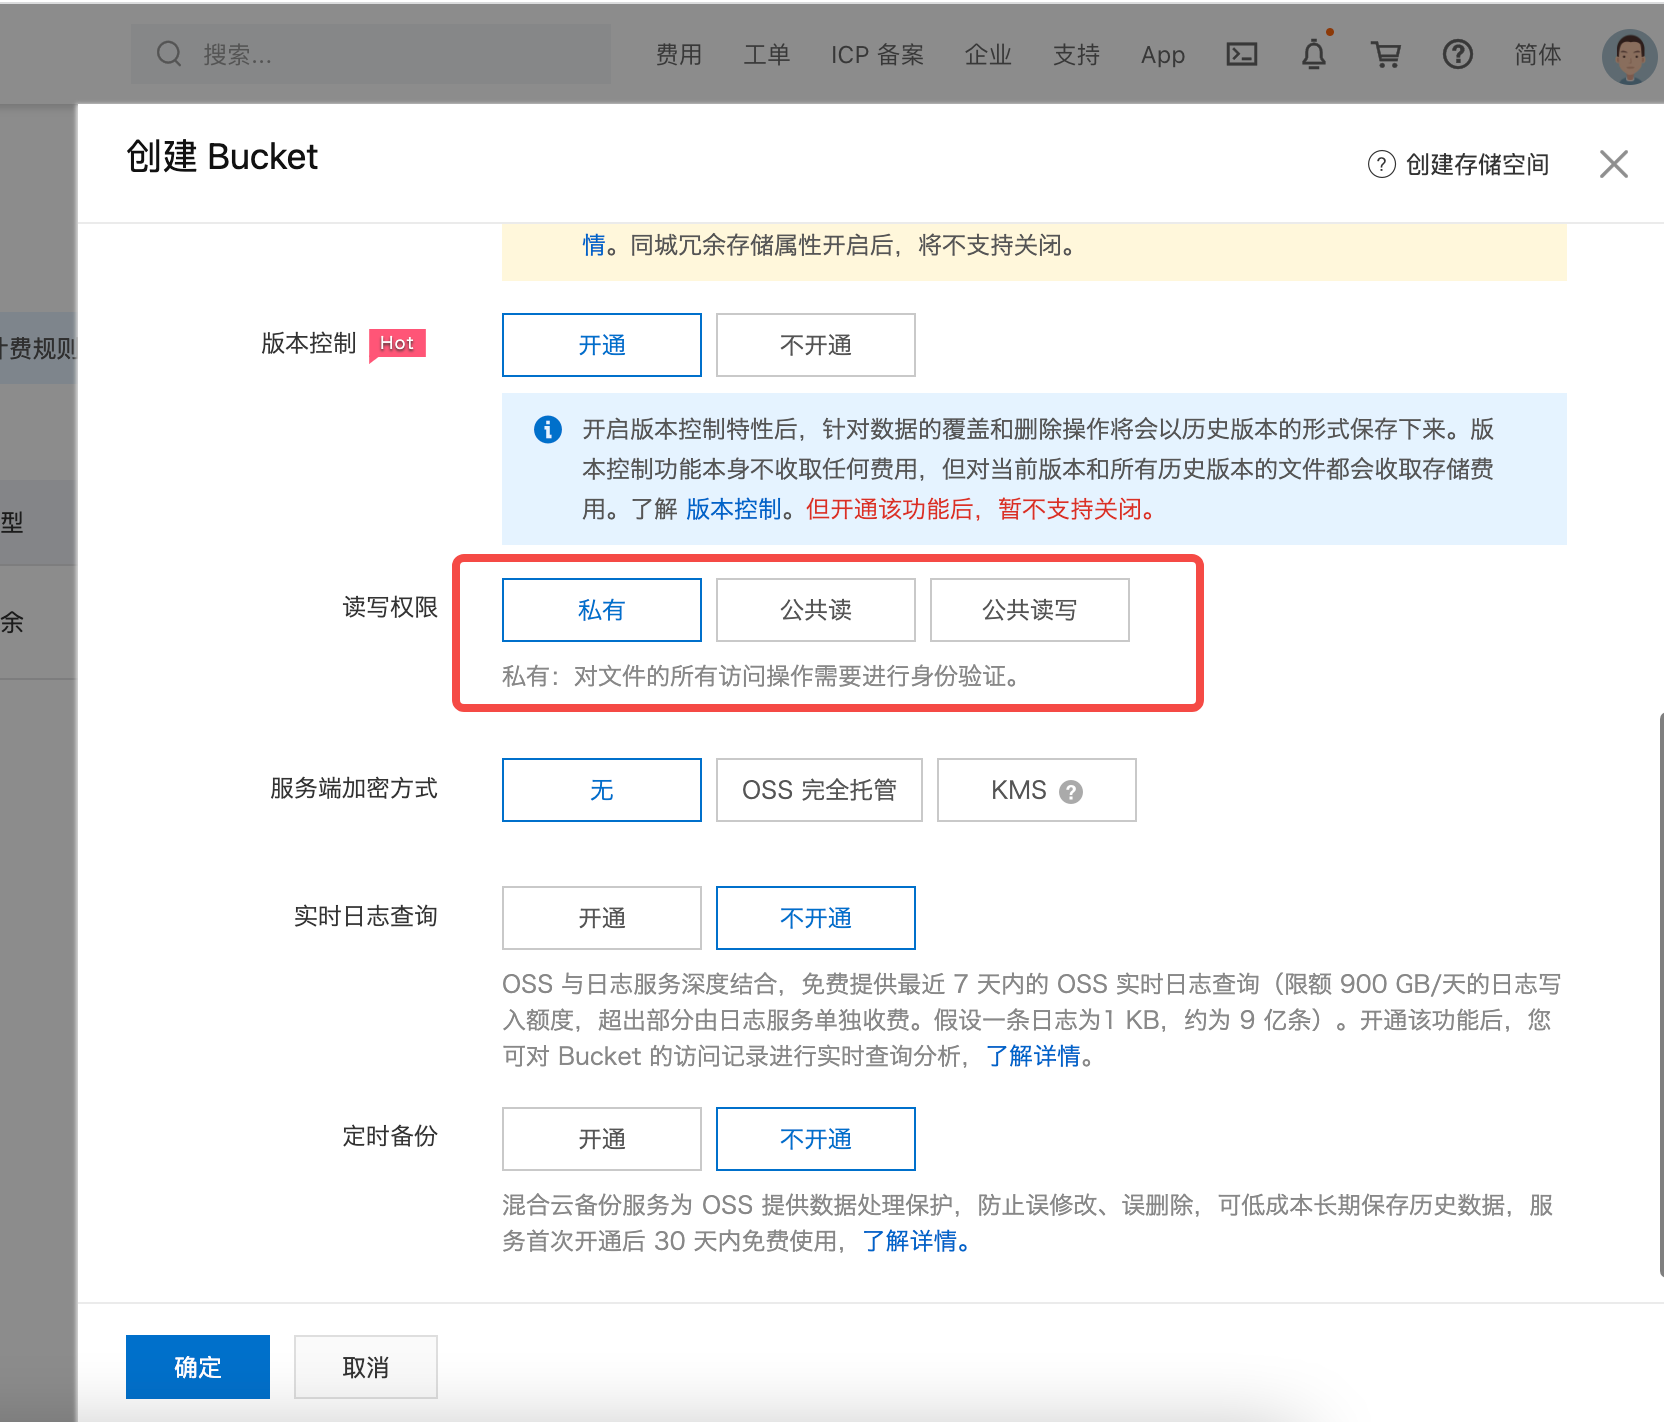
阿里云 OSS对象存储攻防 本文分为两个部分 第一部分介绍OSS对象存储攻防的方式 第二部分为真实漏洞案例 1、Bucket权限配置错误-公开访问 在创建Bucket桶时,默认是private的权限,如果在错误的...
CVE-2025-24963: Vitest Browser Mode – Local File Read
漏洞标题 CVE-2025-24963: Vitest Browser Mode - Local File Read 漏洞描述 Vitest is a testing framework powered by Vite. The `__screenshot-error` handler on the browser mode HTTP ser...
CVE-2025-3515: Contact Form 7 Drag and Drop Multiple File Upload – Arbitrary File Upload
漏洞标题 CVE-2025-3515: Contact Form 7 Drag and Drop Multiple File Upload - Arbitrary File Upload 漏洞描述 The Drag and Drop Multiple File Upload for Contact Form 7 plugin for Word...

