
最新发布第1004页

CVE-2020-16846: SaltStack Shell Injection
漏洞标题 CVE-2020-16846: SaltStack Shell Injection 漏洞描述 An issue was discovered in SaltStack Salt through 3002. Sending crafted web requests to the Salt API, with the SSH clien...
 2020年4月9日 16:25
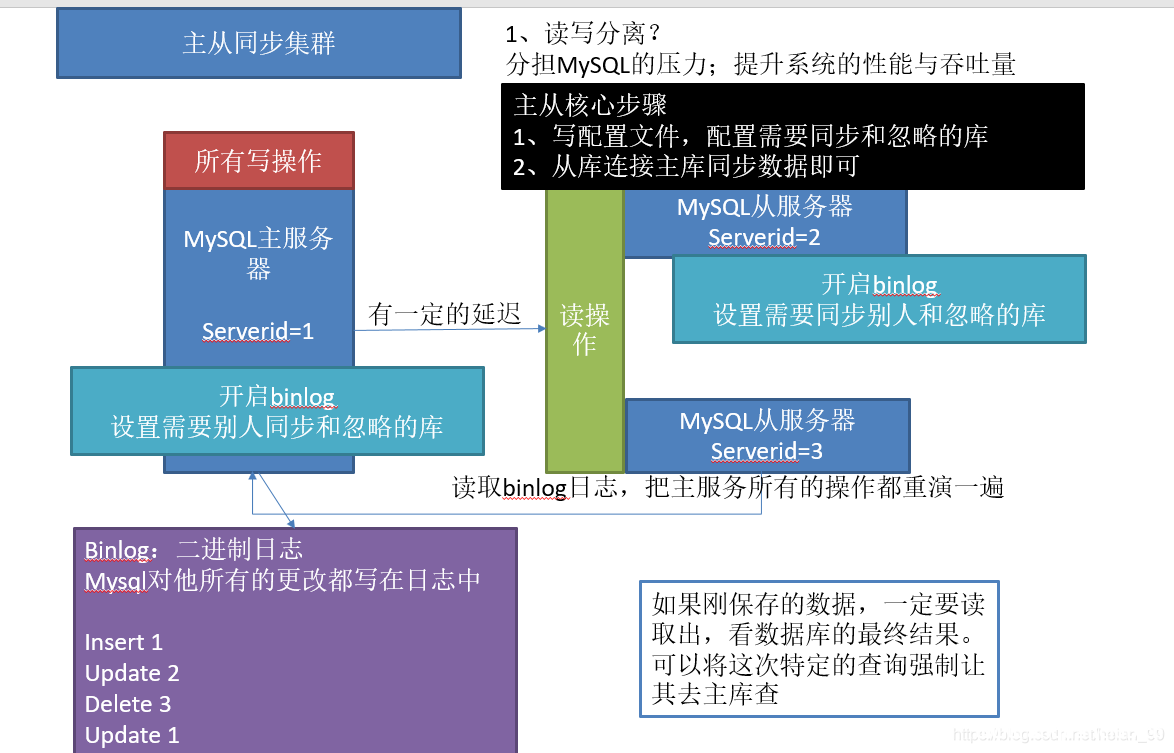
docker实现mysql主从复制的示例代码_docker
Docker它不香吗?即省去了安装Mysql所需要的步骤,有多个容器之间相互资源独立,IP互不冲突,具有一定的参考价值,感兴趣的可以了解一下 目录一、概述1、原理2、实现三、创建Slave实例四、主从配...
2022年6月15日 22:42
bugbounty技巧聚合20211220
漏洞报告 【Judge.me】 html 注入 http://hackerone.com/reports/1036995 【Flickr 】使用 AWS Cognito API 接管 Flickr 账户 http://hackerone.com/reports/1342088 【MTN Group】注册时邮件内...
2022年3月10日 23:38CVE-2019-15889: WordPress Download Manager <2.9.94 - Cross-Site Scripting
漏洞标题 CVE-2019-15889: WordPress Download Manager <2.9.94 - Cross-Site Scripting 漏洞描述 WordPress Download Manager plugin before 2.9.94 contains a cross-site scripting vulne...
2019年5月6日 01:43CVE-2024-8883: Keycloak – Open Redirect
漏洞标题 CVE-2024-8883: Keycloak - Open Redirect 漏洞描述 A misconfiguration flaw was found in Keycloak. This issue can allow an attacker to redirect users to an arbitrary URL if a...
2024年6月10日 00:56CVE-2020-22165: PHPGurukul Hospital Management System 4.0 – SQL Injection
漏洞标题 CVE-2020-22165: PHPGurukul Hospital Management System 4.0 - SQL Injection 漏洞描述 PHPGurukul Hospital Management System in PHP v4.0 has a SQL injection vulnerability in \...
2020年8月3日 02:47CVE-2024-36401: GeoServer RCE in Evaluating Property Name Expressions
漏洞标题 CVE-2024-36401: GeoServer RCE in Evaluating Property Name Expressions 漏洞描述 In the GeoServer version prior to 2.25.1, 2.24.3 and 2.23.5 of GeoServer, multiple OGC reque...
2024年12月13日 08:19CVE-2022-39986: RaspAP 2.8.7 – Unauthenticated Command Injection
漏洞标题 CVE-2022-39986: RaspAP 2.8.7 - Unauthenticated Command Injection 漏洞描述 A Command injection vulnerability in RaspAP 2.8.0 thru 2.8.7 allows unauthenticated attackers to ...
2022年1月15日 22:09Aviatrix Controller 6.x 任意文件上传(CVE-2021-40870)
漏洞标题 Aviatrix Controller 6.x 任意文件上传(CVE-2021-40870) 漏洞描述 Aviatrix Controller是一个集中控制面板,用于编排和管理各种网络和连接解决方案。在 6.5-1804.1922 之前的 Aviatrix...
2021年10月26日 02:15CVE-2023-6360: WordPress My Calendar <3.4.22 - SQL Injection
漏洞标题 CVE-2023-6360: WordPress My Calendar <3.4.22 - SQL Injection 漏洞描述 WordPress My Calendar plugin versions before 3.4.22 are vulnerable to an unauthenticated SQL injec...
2023年6月23日 23:52CVE-2020-29597: IncomCMS 2.0 – Arbitrary File Upload
漏洞标题 CVE-2020-29597: IncomCMS 2.0 - Arbitrary File Upload 漏洞描述 IncomCMS 2.0 has a an insecure file upload vulnerability in modules/uploader/showcase/script.php. This allows...
2020年7月26日 04:40Atlassian Confluence CVE-2023-22527 远程命令执行漏洞
漏洞标题 Atlassian Confluence CVE-2023-22527 远程命令执行漏洞 漏洞描述 Atlassian Confluence存在远程命令执行漏洞,此漏洞是对用户的数据缺乏校验导致的。 PoC代码 暂无
2023年7月16日 11:16CVE-2020-14181: Jira Server and Data Center – Information Disclosure
漏洞标题 CVE-2020-14181: Jira Server and Data Center - Information Disclosure 漏洞描述 Jira Server and Data Center is susceptible to information disclosure. An attacker can enumera...
2020年4月5日 02:24CVE-2023-50094: reNgine 2.2.0 – Command Injection
漏洞标题 CVE-2023-50094: reNgine 2.2.0 - Command Injection 漏洞描述 reNgine before 2.1.2 allows OS Command Injection if an adversary has a valid session ID. The attack places shell...
2023年9月24日 22:16MongoDB Zlib 信息泄露漏洞(CVE-2025-14847)
漏洞标题 MongoDB Zlib 信息泄露漏洞(CVE-2025-14847) 漏洞描述 MongoDB Server 在其使用 Zlib 压缩协议的通信实现中存在长度字段不匹配漏洞,当协议头中的长度字段与实际数据长度不一致时,...
2025年5月30日 13:07CVE-2018-5233: Grav CMS <1.3.0 - Cross-Site Scripting
漏洞标题 CVE-2018-5233: Grav CMS <1.3.0 - Cross-Site Scripting 漏洞描述 Grav CMS before 1.3.0 is vulnerable to cross-site scripting via system/src/Grav/Common/Twig/Twig.php and ...
2018年11月21日 13:09
2026年10月10日 11:45
2026年10月9日 11:45
2026年10月8日 11:45
2026年10月7日 15:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

