
最新发布第1016页

CVE-2025-49706: Microsoft SharePoint Server – Authentication Bypass
漏洞标题 CVE-2025-49706: Microsoft SharePoint Server - Authentication Bypass 漏洞描述 Improper authentication in Microsoft Office SharePoint allows an unauthorized attacker to perf...
 2025年12月11日 00:26
Atom CMS CVE-2022-25487 远程代码执行漏洞
漏洞标题 Atom CMS CVE-2022-25487 远程代码执行漏洞 漏洞描述 Atom CMS CVE-2022-25487 远程 PoC代码 暂无
2022年4月27日 17:33Apache Druid Kafka Connect 远程代码执行漏洞(CVE-2023-25194)
漏洞标题 Apache Druid Kafka Connect 远程代码执行漏洞(CVE-2023-25194) 漏洞描述 Apache Druid 是一个开源的分布式数据存储和分析系统。它设计用于处理大规模的实时数据,并提供快速的交互...
2023年1月28日 20:30CVE-2023-4113: PHPJabbers Service Booking Script 1.0 – Cross Site Scripting
漏洞标题 CVE-2023-4113: PHPJabbers Service Booking Script 1.0 - Cross Site Scripting 漏洞描述 A vulnerability was found in PHP Jabbers Service Booking Script 1.0. It has been decla...
2023年2月24日 06:54CVE-2022-0165: WordPress Page Builder KingComposer <=2.9.6 - Open Redirect
漏洞标题 CVE-2022-0165: WordPress Page Builder KingComposer <=2.9.6 - Open Redirect 漏洞描述 WordPress Page Builder KingComposer 2.9.6 and prior does not validate the id paramet...
2022年4月7日 05:56CVE-2021-37538: PrestaShop SmartBlog <4.0.6 - SQL Injection
漏洞标题 CVE-2021-37538: PrestaShop SmartBlog <4.0.6 - SQL Injection 漏洞描述 PrestaShop SmartBlog by SmartDataSoft < 4.0.6 is vulnerable to a SQL injection vulnerability in ...
2021年7月19日 04:04
致远OA getSessionList.jsp Session泄漏漏洞
致远OA办公自动化软件,用于OA办公自动化软件的开发销售。2010年,用友致远更名为致远协创。2017年更名为致远互联。北京致远互联软件股份有限公司(简称:致远互联)成立于2002年3月,总部设立...

 2023年1月31日 17:48
CVE-2021-35250: SolarWinds Serv-U 15.3 – Directory Traversal
漏洞标题 CVE-2021-35250: SolarWinds Serv-U 15.3 - Directory Traversal 漏洞描述 SolarWinds Serv-U 15.3 is susceptible to local file inclusion, which may allow an attacker access to ...
2021年12月12日 17:41
从0开始简单部署腾讯云服务器的方法步骤_Linux
这篇文章主要介绍了从0开始简单部署腾讯云服务器的方法步骤,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 ...
2023年10月25日 21:01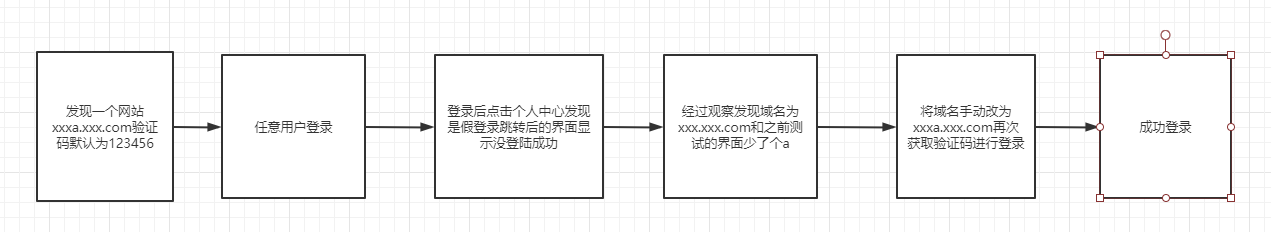
一次奇葩的任意用户登录
在安全小天地测试某src时发现一个界面,域名为xxxa.xxx.com,是一个登录界面,发现该界面支持使用手机号登录以及注册功能,测试后发现该网站使用的短信验证码为123456 因此用脚趾头都能想出来的...
2022年3月10日 23:36CVE-2019-11869: WordPress Yuzo <5.12.94 - Cross-Site Scripting
漏洞标题 CVE-2019-11869: WordPress Yuzo <5.12.94 - Cross-Site Scripting 漏洞描述 WordPress Yuzo Related Posts plugin before 5.12.94 is vulnerable to cross-site scripting because...
2019年3月7日 11:08CVE-2024-2782: WordPress FluentForms <= 5.1.16 - Broken Access Control
漏洞标题 CVE-2024-2782: WordPress FluentForms <= 5.1.16 - Broken Access Control 漏洞描述 The Contact Form Plugin by Fluent Forms for Quiz, Survey, and Drag & Drop WP Form Bu...
2024年10月8日 08:57CVE-2019-2767: Oracle Business Intelligence Publisher – XML External Entity Injection
漏洞标题 CVE-2019-2767: Oracle Business Intelligence Publisher - XML External Entity Injection 漏洞描述 Oracle Business Intelligence Publisher is vulnerable to an XML external enti...
2019年3月4日 21:51CVE-2021-36748: PrestaHome Blog for PrestaShop <1.7.8 - SQL Injection
漏洞标题 CVE-2021-36748: PrestaHome Blog for PrestaShop <1.7.8 - SQL Injection 漏洞描述 PrestaHome Blog for PrestaShop prior to version 1.7.8 is vulnerable to a SQL injection (b...
2021年4月21日 12:05CVE-2019-9874: Sitecore Experience Platform – Deserialization of Untrusted Data
漏洞标题 CVE-2019-9874: Sitecore Experience Platform - Deserialization of Untrusted Data 漏洞描述 Sitecore Experience Platform before 8.2 Update-7 and 9.0 before Update-2 is vulner...
2019年12月22日 16:19
记一次针对违规APP失败的实战渗透测试
前言 前几天晚上,基本上已经准备休息了,隔壁大佬突然发来一个网址,并附言是一个裸聊诈骗APP,需要帮忙看看,继而就有了这篇文章。 首先声明,由于本人技术问题,并没有拿到服务器权限。撰写...
2024年1月20日 14:43
2026年10月10日 11:45
2026年10月9日 11:45
2026年10月8日 11:45
2026年10月7日 15:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

