
最新发布第1019页

CVE-2022-32772: WWBN AVideo 11.6 – Cross-Site Scripting
漏洞标题 CVE-2022-32772: WWBN AVideo 11.6 - Cross-Site Scripting 漏洞描述 WWBN AVideo 11.6 contains a cross-site scripting vulnerability in the footer alerts functionality via the ...
 2022年4月2日 17:44
CVE-2021-27310: Clansphere CMS 2011.4 – Cross-Site Scripting
漏洞标题 CVE-2021-27310: Clansphere CMS 2011.4 - Cross-Site Scripting 漏洞描述 Clansphere CMS 2011.4 contains an unauthenticated reflected cross-site scripting vulnerability via th...
2021年7月22日 10:20CVE-2021-25281: SaltStack Salt <3002.5 - Auth Bypass
漏洞标题 CVE-2021-25281: SaltStack Salt <3002.5 - Auth Bypass 漏洞描述 SaltStack Salt before 3002.5 does not honor eauth credentials for the wheel_async client, allowing attacke...
2021年2月18日 22:50CVE-2025-2539: File Away <= 3.9.9.0.1 - Missing Authorization to Unauthenticated Arbitrary File Read
漏洞标题 CVE-2025-2539: File Away <= 3.9.9.0.1 - Missing Authorization to Unauthenticated Arbitrary File Read 漏洞描述 The File Away plugin for WordPress is vulnerable to unauth...
2025年6月13日 23:09
全球业务关闭,年收入百亿物流公司Expeditors遭受网络攻击
物流和货运代理巨头Expeditors International是总部位于美国西雅图的财富500强公司,在 100 多个国家和地区拥有上万名员工,去年年收入超过百亿。上周日,Expeditors宣布确认了一起网络攻击事件...
2022年3月10日 23:40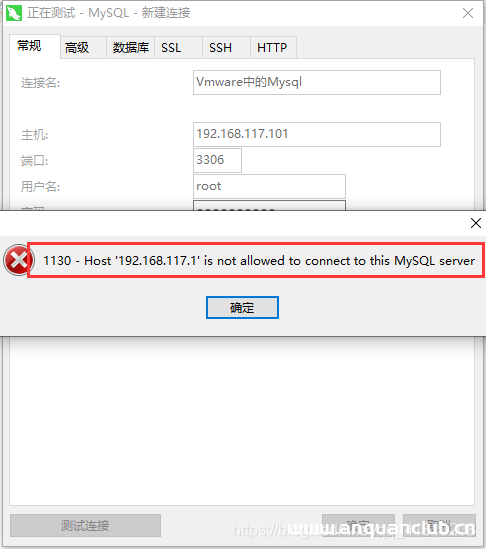
解决Navicat无法连接 VMware中Centos系统中的 MySQL服务器的问题_VMware
这篇文章主要介绍了解决Navicat无法连接 VMware中Centos系统中的 MySQL服务器的问题,本文通过图文并茂的形式给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以...
2022年7月4日 20:08CVE-2010-1471: Joomla! Component Address Book 1.5.0 – Local File Inclusion
漏洞标题 CVE-2010-1471: Joomla! Component Address Book 1.5.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the AddressBook (com_addressbook) component 1.5....
2010年10月31日 21:22CVE-2020-5405: Spring Cloud Config – Local File Inclusion
漏洞标题 CVE-2020-5405: Spring Cloud Config - Local File Inclusion 漏洞描述 Spring Cloud Config versions 2.2.x prior to 2.2.2, 2.1.x prior to 2.1.7, and older unsupported versions ...
2020年3月1日 02:00CVE-2021-38156: Nagios XI < 5.8.6 - Cross-Site Scripting
漏洞标题 CVE-2021-38156: Nagios XI < 5.8.6 - Cross-Site Scripting 漏洞描述 In Nagios XI before 5.8.6, XSS exists in the dashboard page (/dashboards/#) when administrative users ...
2021年6月27日 16:03CVE-2022-32430: Lin CMS Spring Boot – Default JWT Token
漏洞标题 CVE-2022-32430: Lin CMS Spring Boot - Default JWT Token 漏洞描述 An access control issue in Lin CMS Spring Boot v0.2.1 allows attackers to access the backend information a...
2022年12月10日 05:35CVE-2023-31478: GL.iNET SSID Key Disclosure
漏洞标题 CVE-2023-31478: GL.iNET SSID Key Disclosure 漏洞描述 An issue was discovered on GL.iNet devices before 3.216. An API endpoint reveals information about the Wi-Fi configura...
2023年8月3日 13:42CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read
漏洞标题 CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read 漏洞描述 WordPress MultiSafepay for WooCommerce plugin through 4.13.1 contains an ...
2022年7月22日 03:59confluence 远程代码执行漏洞(CVE-2019-3396)
漏洞标题 confluence 远程代码执行漏洞(CVE-2019-3396) 漏洞描述 Confluence是一个专业的企业知识管理与协同软件,常用于构建企业wiki。它强大的编辑和站点管理特征能够帮助团队成员之间共享信...
2019年5月16日 02:47CVE-2014-9119: WordPress DB Backup <=4.5 - Local File Inclusion
漏洞标题 CVE-2014-9119: WordPress DB Backup <=4.5 - Local File Inclusion 漏洞描述 WordPress Plugin DB Backup 4.5 and possibly prior versions are prone to a local file inclusion ...
2014年4月13日 20:18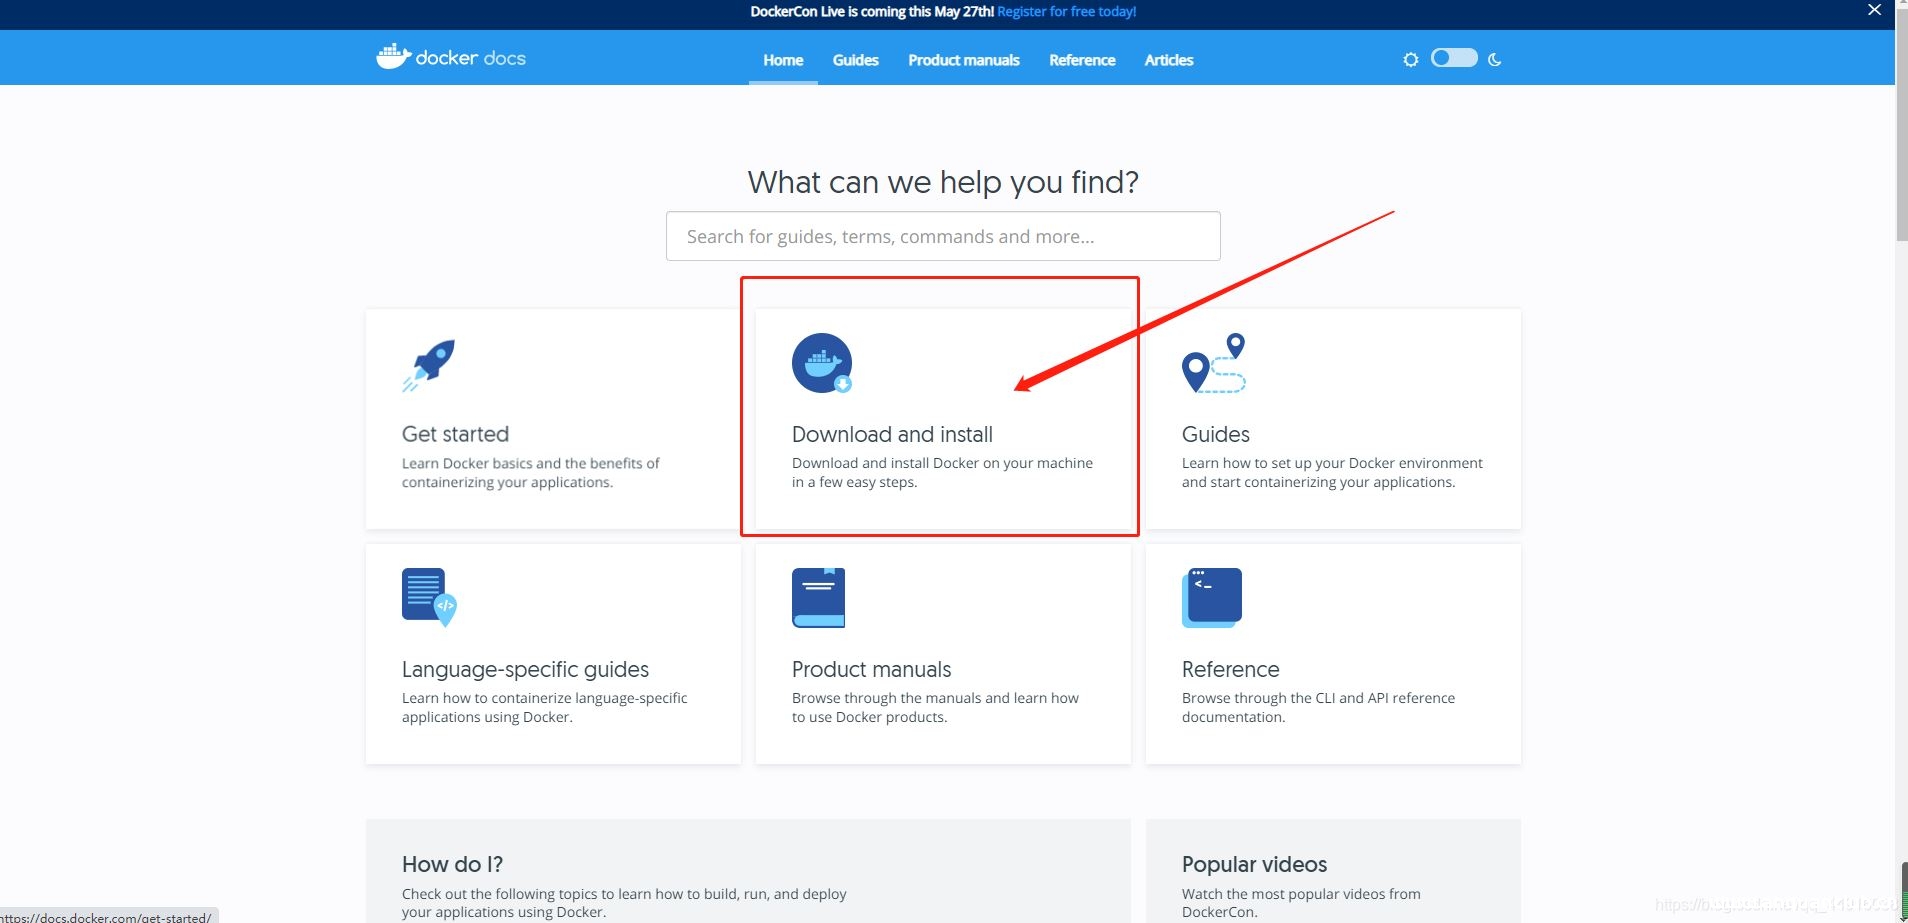
通过idea打包项目到docker的操作方法_docker
这篇文章主要介绍了通过idea打包项目到docker的操作方法,本文通过图文并茂的形式给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 很多小伙伴一直想知道...
2022年6月15日 09:43CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion
漏洞标题 CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion 漏洞描述 An issue was discovered in phpMyAdmin 4.8.x before 4.8.2, in which an attacker can include (view and potent...
2018年10月6日 05:58
2026年10月16日 11:45
2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

