
最新发布第1021页

CVE-2017-12149: Java/Jboss Deserialization [RCE]
漏洞标题 CVE-2017-12149: Java/Jboss Deserialization [RCE] 漏洞描述 In Jboss Application Server as shipped with Red Hat Enterprise Application Platform 5.2, it was found that the do...
 2017年12月25日 23:13
浅谈Nginx 中的两种限流方式_nginx
这篇文章主要介绍了浅谈Nginx 中的两种限流方式,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 系统设计时一般会预估负载,当系统暴露在公网中时,恶意攻击或正常突发流量...
2023年3月6日 21:03CVE-2023-4112: PHPJabbers Shuttle Booking Software 1.0 – Cross Site Scripting
漏洞标题 CVE-2023-4112: PHPJabbers Shuttle Booking Software 1.0 - Cross Site Scripting 漏洞描述 The attacker can send to victim a link containing a malicious URL in an email or ins...
2023年7月7日 00:38CVE-2023-4451: Cockpit – Cross-Site Scripting
漏洞标题 CVE-2023-4451: Cockpit - Cross-Site Scripting 漏洞描述 Cross-site Scripting (XSS) - Reflected in GitHub repository cockpit-hq/cockpit prior to 2.6.4. PoC代码
2023年10月28日 14:46CVE-2019-10405: Jenkins <=2.196 - Cookie Exposure
漏洞标题 CVE-2019-10405: Jenkins <=2.196 - Cookie Exposure 漏洞描述 Jenkins through 2.196, LTS 2.176.3 and earlier prints the value of the cookie on the /whoAmI/ URL despite it ...
2019年4月23日 16:11
浅谈红队中的提权(连载第四篇)
受限于个人水平,文中难免会出现错误或者描述不当的地方,还望各位在评论处指出,望谅解。 0x00 前言 续接上文浅谈红队中的权限维持(连载第三篇) 当拿下目标后,难免会遇到拿下的权限只是一个...
2022年3月10日 23:39CVE-2022-31793: muhttpd <=1.1.5 - Local Inclusion
漏洞标题 CVE-2022-31793: muhttpd <=1.1.5 - Local Inclusion 漏洞描述 muhttpd 1.1.5 and before are vulnerable to unauthenticated local file inclusion. The vulnerability allows ret...
2022年5月12日 11:08CVE-2019-5591: FortiOS – Insecure LDAP Configuration Detection
漏洞标题 CVE-2019-5591: FortiOS - Insecure LDAP Configuration Detection 漏洞描述 The FortiGate LDAP configuration was detected to be insecure due to missing ca-cert, secure LDAPS, ...
2019年2月3日 10:55CVE-2018-16761: Eventum <3.4.0 - Open Redirect
漏洞标题 CVE-2018-16761: Eventum <3.4.0 - Open Redirect 漏洞描述 Eventum before 3.4.0 contains an open redirect vulnerability. An attacker can redirect a user to a malicious sit...
2018年2月5日 22:45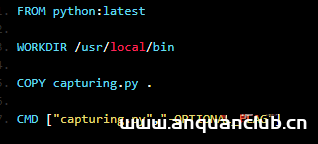
python脚本在docker上运行的方法_docker
在本篇文章里小编给各位分享的是关于python脚本在docker上运行的方法内容,有需要的朋友们可以学习下。 首先为docker镜像创建一个特定的项目目录.例如: mkdir /home/pi/Desktop/teasr/capturin...
2024年3月5日 21:17CraftCMS SEOmatic 模板注入漏洞(CVE-2021-41749)
漏洞标题 CraftCMS SEOmatic 模板注入漏洞(CVE-2021-41749) 漏洞描述 在Craft CMS 3高达3.4.11的SEOmatic插件中,未经身份验证的攻击者可以执行服务器端。模板注入,允许远程代码执行。 PoC代码...
2021年7月6日 06:09CVE-2021-22214: Gitlab CE/EE 10.5 – Server-Side Request Forgery
漏洞标题 CVE-2021-22214: Gitlab CE/EE 10.5 - Server-Side Request Forgery 漏洞描述 GitLab CE/EE versions starting from 10.5 are susceptible to a server-side request forgery vulnerab...
2021年3月25日 21:30CVE-2021-37305: Jeecg Boot <= 2.4.5 - Sensitive Information Disclosure
漏洞标题 CVE-2021-37305: Jeecg Boot <= 2.4.5 - Sensitive Information Disclosure 漏洞描述 Jeecg Boot <= 2.4.5 API interface has unauthorized access and leaks sensitive informa...
2021年11月8日 08:49CVE-2022-2383: WordPress Feed Them Social <3.0.1 - Cross-Site Scripting
漏洞标题 CVE-2022-2383: WordPress Feed Them Social <3.0.1 - Cross-Site Scripting 漏洞描述 WordPress Feed Them Social plugin before 3.0.1 contains a reflected cross-site scriptin...
2022年2月19日 16:25CVE-2021-24746: WordPress Sassy Social Share Plugin <3.3.40 - Cross-Site Scripting
漏洞标题 CVE-2021-24746: WordPress Sassy Social Share Plugin <3.3.40 - Cross-Site Scripting 漏洞描述 WordPress plugin Sassy Social Share < 3.3.40 contains a reflected cross-s...
2021年6月28日 04:20CVE-2019-9670: Synacor Zimbra Collaboration <8.7.11p10 - XML External Entity Injection
漏洞标题 CVE-2019-9670: Synacor Zimbra Collaboration <8.7.11p10 - XML External Entity Injection 漏洞描述 Synacor Zimbra Collaboration Suite 8.7.x before 8.7.11p10 has an XML ext...
2019年4月13日 11:33
2026年10月11日 11:45
2026年10月10日 11:45
2026年10月9日 11:45
2026年10月8日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

