
最新发布第106页

CVE-2025-1302: JSONPath Plus < 10.3.0 - Remote Code Execution
漏洞标题 CVE-2025-1302: JSONPath Plus < 10.3.0 - Remote Code Execution 漏洞描述 Versions of the package jsonpath-plus before 10.3.0 are vulnerable to Remote Code Execution (RCE)...
 2025年8月9日 09:36
CVE-2025-5605: WSO2 Management Console – Authentication Bypass
漏洞标题 CVE-2025-5605: WSO2 Management Console - Authentication Bypass 漏洞描述 An authentication bypass vulnerability exists in the Management Console of multiple WSO2 products. ...
2025年6月23日 13:04CVE-2021-28149: Hongdian H8922 3.0.5 Devices – Local File Inclusion
漏洞标题 CVE-2021-28149: Hongdian H8922 3.0.5 Devices - Local File Inclusion 漏洞描述 Hongdian H8922 3.0.5 devices are vulnerable to local file inclusion. The /log_download.cgi log...
2021年7月6日 11:29CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion
漏洞标题 CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion 漏洞描述 An issue was discovered in phpMyAdmin 4.8.x before 4.8.2, in which an attacker can include (view and potent...
2018年11月19日 04:41Adobe ColdFusion CVE-2024-20767 任意文件读取漏洞
漏洞标题 Adobe ColdFusion CVE-2024-20767 任意文件读取漏洞 漏洞描述 Adobe ColdFusion中存在任意文件读取漏洞,此漏洞是由于未充分验证用户输入file_name参数的数据所导致的。 PoC代码 暂无
2024年5月29日 22:27CVE-2021-35587: Oracle Access Manager – Remote Code Execution
漏洞标题 CVE-2021-35587: Oracle Access Manager - Remote Code Execution 漏洞描述 The Oracle Access Manager portion of Oracle Fusion Middleware (component: OpenSSO Agent) is vulnerab...
2021年2月9日 13:30CVE-2023-37728: IceWarp Webmail Server v10.2.1 – Cross Site Scripting
漏洞标题 CVE-2023-37728: IceWarp Webmail Server v10.2.1 - Cross Site Scripting 漏洞描述 Icewarp Icearp v10.2.1 was discovered to contain a cross-site scripting (XSS) vulnerability ...
2023年4月28日 03:55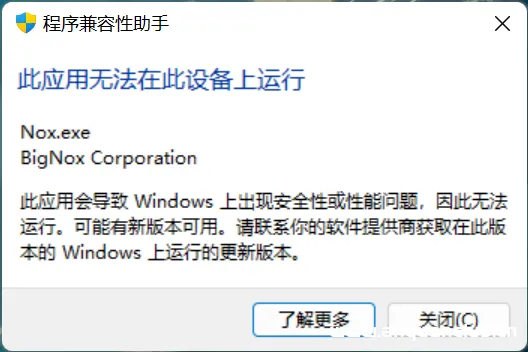
解决夜神模拟器在win11/win10上无法运行的措施
感谢作者:Endest_player提供的分享,这里仅作转载 大佬原文地址:http://www.bilibili.com/read/cv17864186/ windows功能里根本没有hyper-V选项?一键关闭hyper-V不起作用? 的确,经过一番搜...

 2023年1月14日 17:07
CVE-2025-55523: Agent-Zero 0.8.0 – 0.9.4 – Arbitrary File Download
漏洞标题 CVE-2025-55523: Agent-Zero 0.8.0 - 0.9.4 - Arbitrary File Download 漏洞描述 Agent-Zero v0.8.0 - 0.9.4 contains a path traversal caused by improper validation in /api/downl...
2025年3月10日 07:22CVE-2017-7855: IceWarp WebMail 11.3.1.5 – Cross-Site Scripting
漏洞标题 CVE-2017-7855: IceWarp WebMail 11.3.1.5 - Cross-Site Scripting 漏洞描述 IceWarp WebMail 11.3.1.5 is vulnerable to cross-site scripting via the language parameter. PoC代码
2017年4月10日 06:25
安恒信息苗春雨:学以致用产教融合,全方位助力网络安全人才体系建设
3月11日,西湖论剑·第五届中国杭州网络安全技能大赛(以下简称“大赛”)决赛在杭州拉开帷幕。作为首届全球数字贸易博览会的亮点单元,本次大赛由杭州市公安局、共青团杭州市委、杭州市学生联...
2022年3月16日 09:15CVE-2023-4911: Looney Tunables Linux – Local Privilege Escalation
漏洞标题 CVE-2023-4911: Looney Tunables Linux - Local Privilege Escalation 漏洞描述 A buffer overflow was discovered in the GNU C Library's dynamic loader ld.so while processi...
2023年3月27日 12:28CVE-2021-21978: VMware View Planner <4.6 SP1- Remote Code Execution
漏洞标题 CVE-2021-21978: VMware View Planner <4.6 SP1- Remote Code Execution 漏洞描述 VMware View Planner 4.x prior to 4.6 Security Patch 1 contains a remote code execution vuln...
2021年6月14日 09:36CVE-2024-0305: Ncast busiFacade – Remote Command Execution
漏洞标题 CVE-2024-0305: Ncast busiFacade - Remote Command Execution 漏洞描述 The Ncast Yingshi high-definition intelligent recording and playback system is a newly developed audio ...
2024年1月3日 11:21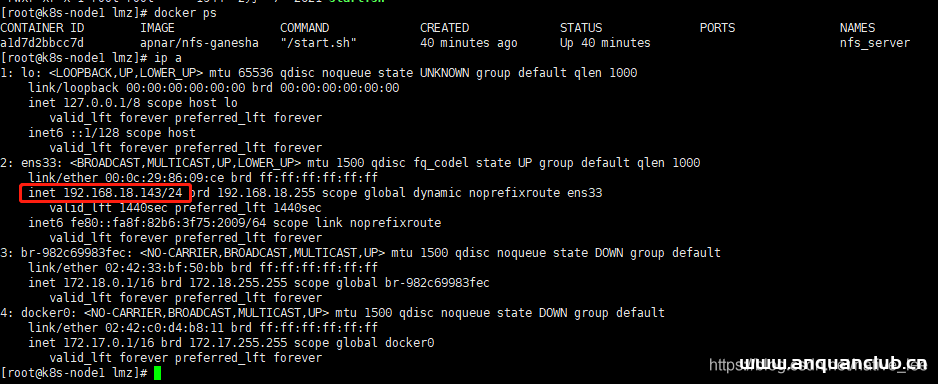
使用Docker的NFS-Ganesha镜像搭建nfs服务器的详细过程_docker
这篇文章主要介绍了使用Docker的NFS-Ganesha镜像搭建nfs服务器,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录一、NFS-Ganesha的简介二、NFS...
2022年6月23日 08:40CVE-2017-5645: Apache Log4j Server – Deserialization Command Execution
漏洞标题 CVE-2017-5645: Apache Log4j Server - Deserialization Command Execution 漏洞描述 In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to ...
2017年5月21日 05:11
2026年10月14日 11:45
2026年10月13日 11:45
2026年10月12日 11:45
2026年10月11日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

