
最新发布第108页

威胁情报获取(GitHub)
有时开发稍不注意会将带有配置信息的源码传至GitHub,这时可以利用一些语法辅助我们找到敏感信息,github dorks: filename:.npmrc _auth filename:.dockercfg auth extension:pem private exte...
 2022年3月10日 23:32
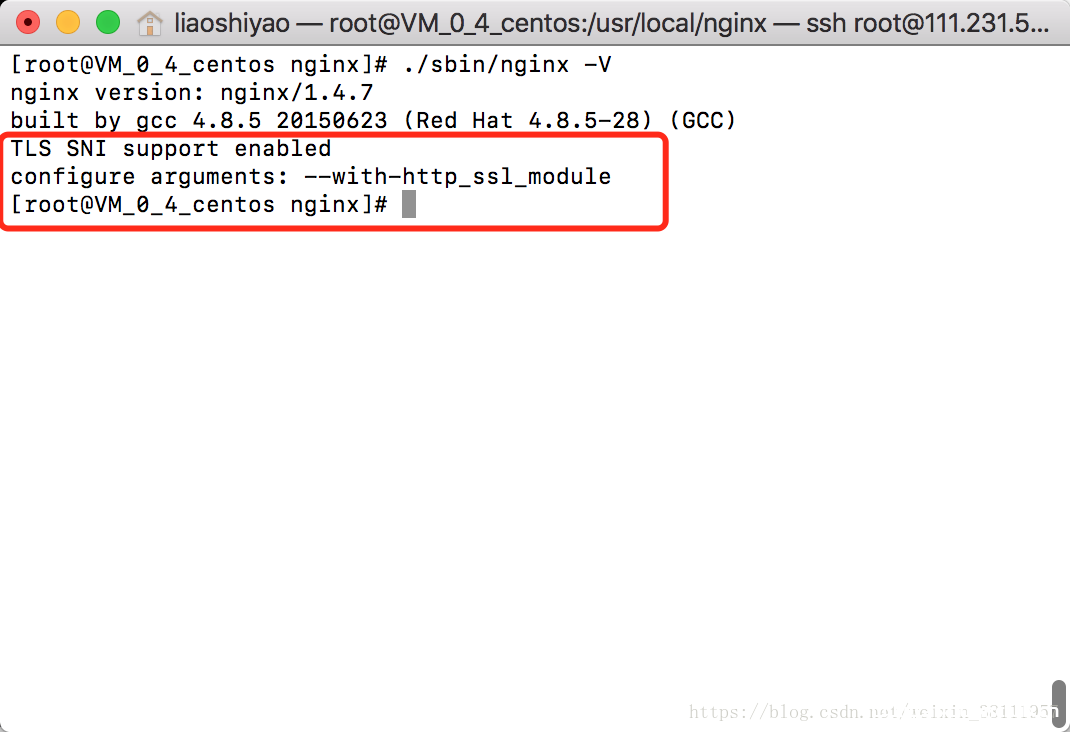
Nginx配置SSL证书出错解决方案_nginx
这篇文章主要介绍了Nginx配置SSL证书出错解决方案,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、引言 当我们的Linux服务器上当中发...
2022年12月29日 20:28
CVE-2025-3515: Contact Form 7 Drag and Drop Multiple File Upload – Arbitrary File Upload
漏洞标题 CVE-2025-3515: Contact Form 7 Drag and Drop Multiple File Upload - Arbitrary File Upload 漏洞描述 The Drag and Drop Multiple File Upload for Contact Form 7 plugin for Word...
2025年10月17日 00:02
[RoarCTF 2019]Easy Calc – buu刷题笔记
题目 题目打开是这样的查看源码 <!--I've set up WAF to ensure security.--> <script> $('#calc').submit(function(){ $.ajax({ url:'calc.php?num='+encodeURIComponent($('#content')....

 2023年1月13日 20:02

msf可视化远控平台——Kage
相关阅读 简介 Kage是Metasploit RPC 服务器的GUI 工具,它可以帮助初学者更好的理解和学习Metasploit。该工具还处于开发中,支持的功能有限,要使用它需要安装Metasploit和npm。 Kage具有Windo...
2022年4月1日 18:36
URL Rewrite Module 2.1 URL重写模块规则写法_服务器其它
URL重写模块是IIS的扩展,可作为独立IIS Server的下载下载,并且还预先安装在Windows Azure网站(WAWS)上的任何网站上,供您使用,本教程将指导您完成如何为URL重写模块创建和测试一组重写规则...
2022年12月26日 20:22Commvault /commandcenter/deployServiceCommcell.do 文件上传漏洞(CVE-2025-34028)
漏洞标题 Commvault /commandcenter/deployServiceCommcell.do 文件上传漏洞(CVE-2025-34028) 漏洞描述 Commvault是一款数据保护或网络弹性解决方案,为企业备份和复制套件。 Commva...
2025年4月6日 04:42CVE-2010-2857: Joomla! Component Music Manager – Local File Inclusion
漏洞标题 CVE-2010-2857: Joomla! Component Music Manager - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Music Manager component for Joomla! allows remote...
2010年12月12日 17:50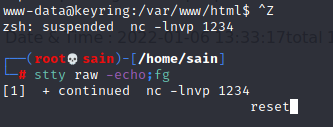
Linux 反向 shell 升级为完全可用的 TTY shell
升级远程 shell(仅限 Unix 机器) 通常,在通过 nc 捕获 shell 之后,会在一个功能非常有限的 shell 中。例如没有命令历史记录(并使用向上“”和“向下”箭头循环浏览它们)和文件名称、命令...
2022年4月1日 18:36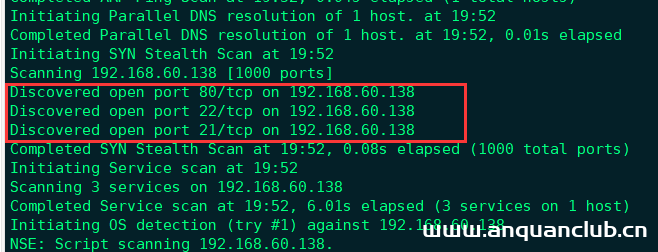
Vulnhub 靶场 DRIPPING BLUES: 1
前期准备: 靶机地址:http://www.vulnhub.com/entry/dripping-blues-1,744/ kali攻击机ip:192.168.60.128靶机地址:192.168.660.138 注:这个靶机有坑,别钻死胡同。 一、信息收集 1.使用nmap...
2022年3月26日 20:27
尽快升级!西部数据将结束对旧版My Cloud OS的支持
近日,西部数据(全球知名数据存储厂商)宣布将结束对前几代My Cloud OS的支持。如果用户的设备与My Cloud OS 5不兼容,将失去远程访问权限,并且旧版本设备不再能得到安全修复或技术支持。若用...
2022年3月10日 23:39CVE-2025-24963: Vitest Browser Mode – Local File Read
漏洞标题 CVE-2025-24963: Vitest Browser Mode - Local File Read 漏洞描述 Vitest is a testing framework powered by Vite. The `__screenshot-error` handler on the browser mode HTTP ser...
2025年10月18日 19:22CVE-2021-45467: Control Web Panel (CWP) – File Inclusion
漏洞标题 CVE-2021-45467: Control Web Panel (CWP) - File Inclusion 漏洞描述 In CWP (Control Web Panel, previously CentOS Web Panel) before version 0.9.8.1107, an unauthenticated att...
2021年8月28日 13:50Bylancer Quicklancer CVE-2024-7188 SQL注入漏洞
漏洞标题 Bylancer Quicklancer CVE-2024-7188 SQL注入漏洞 漏洞描述 Bylancer Quicklancer是Bylancer公司的一个自由职业者平台。Bylancer Quicklancer 存在SQL注入漏洞。此漏洞是由于对用户发...
2024年10月28日 09:28CVE-2025-34077: WordPress Pie Register <= 3.7.1.4 - Authentication Bypass
漏洞标题 CVE-2025-34077: WordPress Pie Register <= 3.7.1.4 - Authentication Bypass 漏洞描述 An authentication bypass vulnerability exists in the WordPress Pie Register plugin ≤...
2025年9月13日 07:31Atlassian Jira 信息泄露(CVE-2019-3401)
漏洞标题 Atlassian Jira 信息泄露(CVE-2019-3401) 漏洞描述 Jira 7.13.3之前版本和8.1.1之前版本8.0.0中的ManageFilters.jspa资源允许远程攻击者通过不正确的授权检查枚举用户名。 PoC代码 暂...
2019年9月20日 06:33
2026年10月13日 11:45
2026年10月12日 11:45
2026年10月11日 11:45
2026年10月10日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

