
最新发布第113页

CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution
漏洞标题 CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution 漏洞描述 CloudPanel 2 before 2.3.1 has insecure file-manager cookie authentication. PoC代码
 2023年11月27日 10:06
CVE-2024-0593: WordPress Simple Job Board – Unauthorized Data Access
漏洞标题 CVE-2024-0593: WordPress Simple Job Board - Unauthorized Data Access 漏洞描述 The Simple Job Board plugin for WordPress is vulnerable to unauthorized data access due to in...
2024年7月31日 07:45CVE-2016-1000139: WordPress Infusionsoft Gravity Forms <=1.5.11 - Cross-Site Scripting
漏洞标题 CVE-2016-1000139: WordPress Infusionsoft Gravity Forms <=1.5.11 - Cross-Site Scripting 漏洞描述 WordPress plugin Infusionsoft 1.5.11 and before contains a reflected cro...
2016年3月20日 12:27
全球范围多家知名平台受波及,亚马逊云服务中断
12月7日,亚马逊云服务(AWS,Amazon Web Services)在US-EAST-1区域陷入网络中断。全球许多平台、服务都依赖于AWS运行,当亚马逊网络中断时,这些平台及服务也会中断,这导致世界各地用户都不...
2022年3月10日 23:39CVE-2021-3019: ffay lanproxy Directory Traversal
漏洞标题 CVE-2021-3019: ffay lanproxy Directory Traversal 漏洞描述 ffay lanproxy 0.1 is susceptible to a directory traversal vulnerability that could let attackers read /../conf/co...
2021年9月7日 20:30CVE-2024-5910: Palo Alto Expedition – Admin Account Takeover
漏洞标题 CVE-2024-5910: Palo Alto Expedition - Admin Account Takeover 漏洞描述 Missing authentication for a critical function in Palo Alto Networks Expedition can lead to an Expedi...
2024年12月23日 22:45CVE-2018-10823: D-Link Routers – Remote Command Injection
漏洞标题 CVE-2018-10823: D-Link Routers - Remote Command Injection 漏洞描述 D-Link DWR-116 through 1.06, DWR-512 through 2.02, DWR-712 through 2.02, DWR-912 through 2.02, DWR-921 t...
2018年7月11日 02:18CVE-2019-14470: WordPress UserPro 4.9.32 – Cross-Site Scripting
漏洞标题 CVE-2019-14470: WordPress UserPro 4.9.32 - Cross-Site Scripting 漏洞描述 WordPress UserPro 4.9.32 is vulnerable to reflected cross-site scripting because the Instagram PHP...
2019年7月12日 21:00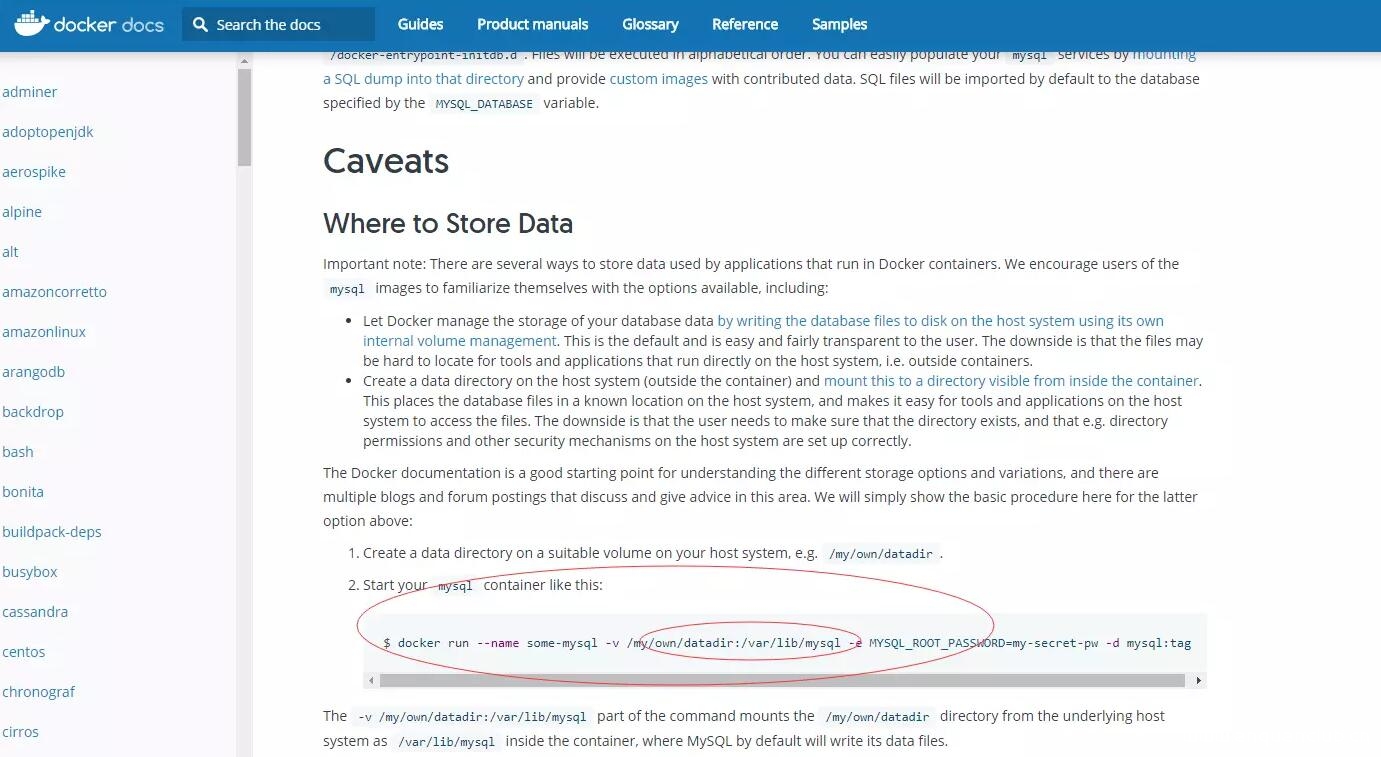
解决docker重启redis,mysql数据丢失的问题_docker
这篇文章主要介绍了解决docker重启redis,mysql数据丢失的问题,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 官方文档: 所以 mysql应如下启动: docker run -p 3306:3306 ...
2023年1月3日 21:23CVE-2023-46359: cPH2 Charging Station v1.87.0 – OS Command Injection
漏洞标题 CVE-2023-46359: cPH2 Charging Station v1.87.0 - OS Command Injection 漏洞描述 An OS command injection vulnerability in Hardy Barth cPH2 Ladestation v1.87.0 and earlier, ma...
2023年10月18日 12:36CVE-2022-41800: F5 BIG-IP Appliance Mode – Command Injection
漏洞标题 CVE-2022-41800: F5 BIG-IP Appliance Mode - Command Injection 漏洞描述 When running in Appliance mode, an authenticated user assigned the Administrator role may bypass Appl...
2022年3月11日 16:58CVE-2023-23489: WordPress Easy Digital Downloads 3.1.0.2/3.1.0.3 – SQL Injection
漏洞标题 CVE-2023-23489: WordPress Easy Digital Downloads 3.1.0.2/3.1.0.3 - SQL Injection 漏洞描述 WordPress Easy Digital Downloads plugin 3.1.0.2 and 3.1.0.3 contains a SQL inject...
2023年12月29日 15:53
-CVE-2017-12635 CouchDB垂直越权漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现-CVE-2017-12635 CouchDB垂直越权漏洞 Apache CouchDB是一个开源数据库,专注于易用性和成为'完全拥抱web的数据库'。它是一个使用JSON...
2023年2月2日 14:59CVE-2022-34267: RWS WorldServer – Authentication Bypass
漏洞标题 CVE-2022-34267: RWS WorldServer - Authentication Bypass 漏洞描述 An issue was discovered in RWS WorldServer before 11.7.3. Adding a token parameter with the value of 02 by...
2022年3月4日 11:54
ENScan 一款企业信息收集工具
背景 本项目为 狼组信息化平台 功能项目,该项目开源 程序主要对百度爱企查 API和接口进行封装可获取 企业基本信息(法人、电话、公司地址等等) 企业ICP备案号以及网站 企业APP...

 2023年1月13日 20:12
CVE-2017-18536: WordPress Stop User Enumeration <=1.3.7 - Cross-Site Scripting
漏洞标题 CVE-2017-18536: WordPress Stop User Enumeration <=1.3.7 - Cross-Site Scripting 漏洞描述 WordPress Stop User Enumeration 1.3.7 and earlier are vulnerable to unauthentica...
2017年11月5日 20:29
2026年9月16日 11:45
2026年9月15日 11:45
2026年9月14日 11:45
2026年9月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月2日 09:46
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

