
最新发布第11页

CVE-2025-61757: Oracle Identity Manager REST WebServices – Authentication Bypass
漏洞标题 CVE-2025-61757: Oracle Identity Manager REST WebServices - Authentication Bypass 漏洞描述 Vulnerability in the Identity Manager product of Oracle Fusion Middleware (compon...
 2025年9月8日 05:17
CVE-2022-29272: Nagios XI <5.8.5 - Open Redirect
漏洞标题 CVE-2022-29272: Nagios XI <5.8.5 - Open Redirect 漏洞描述 Nagios XI through 5.8.5 contains an open redirect vulnerability in the login function. An attacker can redirec...
2022年1月21日 06:48CVE-2025-0108: PAN-OS Management Interface – Path Confusion to Authentication Bypass
漏洞标题 CVE-2025-0108: PAN-OS Management Interface - Path Confusion to Authentication Bypass 漏洞描述 A vulnerability in PAN-OS management interface allows authentication bypass t...
2025年3月13日 07:10CVE-2021-24300: WordPress WooCommerce <1.13.22 - Cross-Site Scripting
漏洞标题 CVE-2021-24300: WordPress WooCommerce <1.13.22 - Cross-Site Scripting 漏洞描述 WordPress WooCommerce before 1.13.22 contains a reflected cross-site scripting vulnerabil...
2021年2月21日 22:59CVE-2023-35078: Ivanti Endpoint Manager Mobile (EPMM) – Authentication Bypass
漏洞标题 CVE-2023-35078: Ivanti Endpoint Manager Mobile (EPMM) - Authentication Bypass 漏洞描述 Ivanti Endpoint Manager Mobile (EPMM), formerly MobileIron Core, through 11.10 allow...
2023年6月6日 22:03CVE-2021-21345: XStream < 1.4.16 - Remote Code Execution
漏洞标题 CVE-2021-21345: XStream < 1.4.16 - Remote Code Execution 漏洞描述 XStream before 1.4.16 is susceptible to remote code execution. An attacker who has sufficient rights c...
2021年5月12日 08:00CVE-2021-24931: WordPress Secure Copy Content Protection and Content Locking <2.8.2 - SQL Injection
漏洞标题 CVE-2021-24931: WordPress Secure Copy Content Protection and Content Locking <2.8.2 - SQL Injection 漏洞描述 WordPress Secure Copy Content Protection and Content Lockin...
2021年8月16日 08:21CVE-2022-0952: WordPress Sitemap by click5 <1.0.36 - Missing Authorization
漏洞标题 CVE-2022-0952: WordPress Sitemap by click5 <1.0.36 - Missing Authorization 漏洞描述 WordPress Sitemap by click5 plugin before 1.0.36 is susceptible to missing authoriza...
2022年12月24日 08:56CVE-2010-1494: Joomla! Component AWDwall 1.5.4 – Local File Inclusion
漏洞标题 CVE-2010-1494: Joomla! Component AWDwall 1.5.4 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the AWDwall (com_awdwall) component 1.5.4 for Joomla!...
2010年1月21日 12:44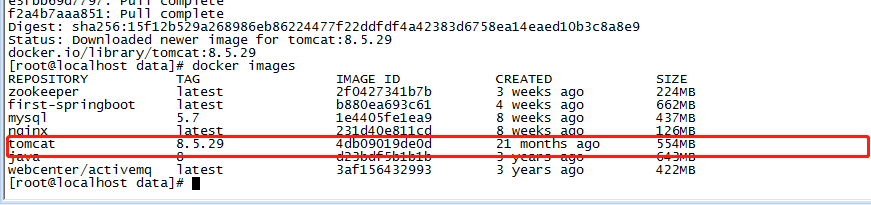
docker安装tomcat dubbo-admin实例技巧_docker
在本篇文章里小编给大家整理的是关于docker安装tomcat dubbo-admin实例技巧,有需要的朋友们可以参考下。 1、下载tomcat 镜像 docker pull tomcat:8.5.29 2、验证镜像 docker images 3、安装tom...
2024年6月9日 20:56CVE-2022-22947: Spring Cloud Gateway Code Injection
漏洞标题 CVE-2022-22947: Spring Cloud Gateway Code Injection 漏洞描述 Applications using Spring Cloud Gateway prior to 3.1.1+ and 3.0.7+ are vulnerable to a code injection attack w...
2022年6月14日 09:16CVE-2024-48248: NAKIVO Backup & Replication任意文件读取漏洞
漏洞标题 CVE-2024-48248: NAKIVO Backup & Replication任意文件读取漏洞 漏洞描述 NAKIVO Backup & Replication 是一款专注于虚拟化、云端及混合环境的备份与灾难恢复的解决方案。攻击...
2024年6月25日 16:46CVE-2017-8229: Amcrest IP Camera Web Management – Data Exposure
漏洞标题 CVE-2017-8229: Amcrest IP Camera Web Management - Data Exposure 漏洞描述 Amcrest IPM-721S V2.420.AC00.16.R.20160909 devices allow an unauthenticated attacker to download t...
2017年1月11日 08:58CVE-2021-31755: Tenda Router AC11 – Remote Command Injection
漏洞标题 CVE-2021-31755: Tenda Router AC11 - Remote Command Injection 漏洞描述 Tenda Router AC11 is susceptible to remote command injection vulnerabilities in the web-based managem...
2021年1月8日 12:03
bugbounty技巧聚合20211202
漏洞报告 【VK.com】XSS http://hackerone.com/reports/1115763 【 VK.com】#1343280 Получаем название и аватарку (50x50) частной группы. http://ha...
2022年3月10日 23:33CVE-2023-47643: SuiteCRM Unauthenticated Graphql Introspection
漏洞标题 CVE-2023-47643: SuiteCRM Unauthenticated Graphql Introspection 漏洞描述 Graphql Introspection is enabled without authentication, exposing the scheme defining all object ty...
2023年10月26日 03:38
2026年9月16日 11:45
2026年9月15日 11:45
2026年9月14日 11:45
2026年9月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月2日 09:46
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

