
最新发布第128页

CVE-2021-26085: Atlassian Confluence Server – Local File Inclusion
漏洞标题 CVE-2021-26085: Atlassian Confluence Server - Local File Inclusion 漏洞描述 Atlassian Confluence Server allows remote attackers to view restricted resources via local file...
 2021年3月28日 02:54
Apache ShardingSphere CVE-2022-22733远程代码执行漏洞
漏洞标题 Apache ShardingSphere CVE-2022-22733远程代码执行漏洞 漏洞描述 Apache ShardingSphere存在远程代码执行漏洞,此漏洞是缺乏校验导致的。 PoC代码 暂无
2022年11月15日 22:27CVE-2018-14574: Django – Open Redirect
漏洞标题 CVE-2018-14574: Django - Open Redirect 漏洞描述 Django 1.11.x before 1.11.15 and 2.0.x before 2.0.8 contains an open redirect vulnerability. If django.middleware.common.Co...
2018年11月27日 03:59CVE-2021-24145: WordPress Modern Events Calendar Lite <5.16.5 - Authenticated Arbitrary File Upload
漏洞标题 CVE-2021-24145: WordPress Modern Events Calendar Lite <5.16.5 - Authenticated Arbitrary File Upload 漏洞描述 WordPress Modern Events Calendar Lite plugin before 5.16.5 ...
2021年7月25日 19:05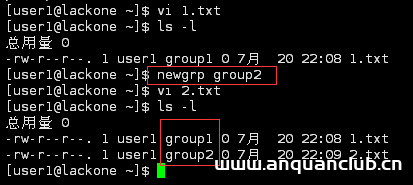
linux用户和组命令实例分析【切换、添加用户、权限控制等】_Linux
这篇文章主要介绍了linux用户和组命令,结合实例形式分析了Linux系统切换、添加用户、权限控制等相关命令与使用技巧,需要的朋友可以参考下 本文实例讲述了linux用户和组命令。分享给大家供大家参...
2024年3月11日 20:28CVE-2014-4561: Ultimate Weather Plugin <= 1.0 - Cross-Site Scripting
漏洞标题 CVE-2014-4561: Ultimate Weather Plugin <= 1.0 - Cross-Site Scripting 漏洞描述 The ultimate-weather plugin 1.0 for WordPress contains a cross-site scripting vulnerabilit...
2014年2月9日 10:11Belkin N150 路径遍历(CVE-2014-2962)
漏洞标题 Belkin N150 路径遍历(CVE-2014-2962) 漏洞描述 固件版本低于1.00.08的Belkin N150 F9K1009 v1路由器上的webproccgi模块中存在路径遍历漏洞,远程攻击者可借助getpage参数中的完整路径...
2014年5月31日 15:29CVE-2019-13462: Lansweeper Unauthenticated SQL Injection
漏洞标题 CVE-2019-13462: Lansweeper Unauthenticated SQL Injection 漏洞描述 Lansweeper before 7.1.117.4 allows unauthenticated SQL injection. PoC代码
2019年5月8日 23:05CVE-2020-16952: Microsoft SharePoint – Remote Code Execution
漏洞标题 CVE-2020-16952: Microsoft SharePoint - Remote Code Execution 漏洞描述 Microsoft SharePoint is vulnerable to a remote code execution when the software fails to check the so...
2020年8月29日 09:02CVE-2014-6271: ShellShock – Remote Code Execution
漏洞标题 CVE-2014-6271: ShellShock - Remote Code Execution 漏洞描述 GNU Bash through 4.3 processes trailing strings after function definitions in the values of environment variable...
2014年12月7日 14:40CVE-2016-8706: Memcached Server SASL Authentication – Remote Code Execution
漏洞标题 CVE-2016-8706: Memcached Server SASL Authentication - Remote Code Execution 漏洞描述 An integer overflow in process_bin_sasl_auth function in Memcached, which is responsib...
2016年2月23日 21:07CVE-2023-1263: Coming Soon & Maintenance < 4.1.7 - Unauthenticated Post/Page Access
漏洞标题 CVE-2023-1263: Coming Soon & Maintenance < 4.1.7 - Unauthenticated Post/Page Access 漏洞描述 The plugin does not restrict access to published and non protected post...
2023年1月14日 20:32cPanel低于11.109.9999.116存在XSS漏洞(CVE-2023-29489)
漏洞标题 cPanel低于11.109.9999.116存在XSS漏洞(CVE-2023-29489) 漏洞描述 cPanel 是一套在网页寄存业中最享负盛名的商业软件,是基于于 Linux 和 BSD 系统及以 PHP开发且性质为闭源软件;提供...
2023年4月5日 14:12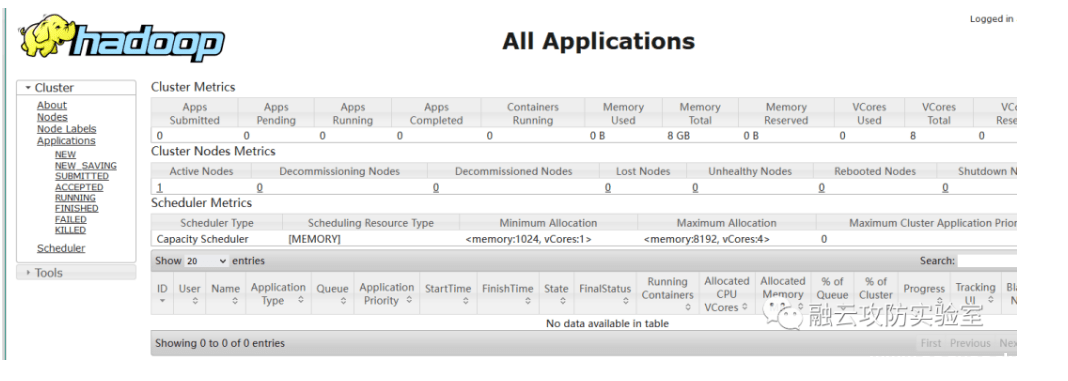
-Hadoop Restful API未授权
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现-Hadoop Restful API未授权 Hadoop是一个由Apache基金会所开发的分布式系统基础架构,Hadoop通过ResourceManager REST API,可以让⽤户...

 2023年2月8日 14:11
CVE-2022-24260: VoipMonitor – Pre-Auth SQL Injection
漏洞标题 CVE-2022-24260: VoipMonitor - Pre-Auth SQL Injection 漏洞描述 A SQL injection vulnerability in Voipmonitor GUI before v24.96 allows attackers to escalate privileges to the...
2022年9月17日 03:12CVE-2019-5129: YouPHPTube Encoder 2.3 – Command Injection
漏洞标题 CVE-2019-5129: YouPHPTube Encoder 2.3 - Command Injection 漏洞描述 Exploitable unauthenticated command injections exist in YouPHPTube Encoder 2.3 a plugin for providing en...
2019年8月15日 14:58
2026年10月17日 11:45
2026年10月16日 11:45
2026年10月15日 11:45
2026年10月14日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

