
最新发布第12页

CVE-2023-3077: MStore API < 3.9.8 - SQL Injection
漏洞标题 CVE-2023-3077: MStore API < 3.9.8 - SQL Injection 漏洞描述 The MStore API WordPress plugin before 3.9.8 is vulnerable to Blind SQL injection via the product_id paramete...
 2023年8月8日 22:58
CVE-2022-44951: Rukovoditel <= 3.2.1 - Cross Site Scripting
漏洞标题 CVE-2022-44951: Rukovoditel <= 3.2.1 - Cross Site Scripting 漏洞描述 Rukovoditel v3.2.1 was discovered to contain a stored cross-site scripting (XSS) vulnerability in t...
2022年9月19日 18:09CVE-2021-24169: WordPress Advanced Order Export For WooCommerce <3.1.8 - Authenticated Cross-Site Scripting
漏洞标题 CVE-2021-24169: WordPress Advanced Order Export For WooCommerce <3.1.8 - Authenticated Cross-Site Scripting 漏洞描述 WordPress Advanced Order Export For WooCommerce plu...
2021年6月23日 22:13Apache OFBiz RMI反序列化前台命令执行(CVE-2021-26295)
漏洞标题 Apache OFBiz RMI反序列化前台命令执行(CVE-2021-26295) 漏洞描述 OFBiz是基于Java的Web框架,包括实体引擎,服务引擎和基于小部件的UI。近日,Apache OFBiz官方发布安全更新。Apache ...
2021年7月28日 02:02Ureport v2.1.7 CVE-2023-24189 XXE漏洞
漏洞标题 Ureport v2.1.7 CVE-2023-24189 XXE漏洞 漏洞描述 Ureport v2.1.7 CVE-2023-24189 XXE漏洞 日期: 2024-02-07 | 影响软件: Ureport v2.1.7 | PoC代码
2023年5月17日 10:43CVE-2010-2507: Joomla! Component Picasa2Gallery 1.2.8 – Local File Inclusion
漏洞标题 CVE-2010-2507: Joomla! Component Picasa2Gallery 1.2.8 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Picasa2Gallery (com_picasa2gallery) compon...
2010年9月21日 16:49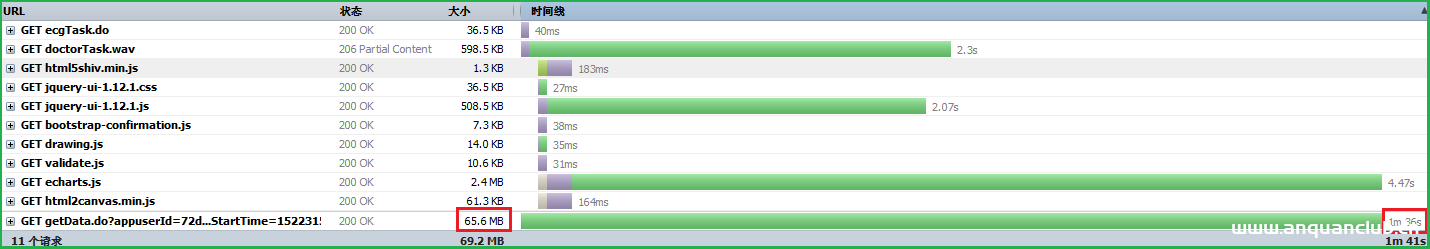
GZIP压缩Tomcat并提升web性能过程图解_Tomcat
这篇文章主要介绍了GZIP压缩Tomcat并提升web性能过程图解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、前言 最近做了个项目,遇到...
2024年2月14日 20:30CVE-2023-2648: Weaver E-Office 9.5 – Remote Code Execution
漏洞标题 CVE-2023-2648: Weaver E-Office 9.5 - Remote Code Execution 漏洞描述 A vulnerability was found in Weaver E-Office 9.5. It has been classified as critical. This affects an u...
2023年12月9日 01:55CVE-2022-1392: WordPress Videos sync PDF <=1.7.4 - Local File Inclusion
漏洞标题 CVE-2022-1392: WordPress Videos sync PDF <=1.7.4 - Local File Inclusion 漏洞描述 WordPress Videos sync PDF 1.7.4 and prior does not validate the p parameter before usin...
2022年6月6日 15:01CVE-2024-22024: Ivanti Pulse Connect Secure VPN XXE
漏洞标题 CVE-2024-22024: Ivanti Pulse Connect Secure VPN XXE 漏洞描述 An XML external entity or XXE vulnerability in the SAML component of Ivanti Connect Secure (9.x, 22.x), Ivanti...
2024年12月10日 10:01
解决docker拉取mysql镜像太慢的情况_docker
这篇文章主要介绍了解决docker拉取mysql镜像太慢的情况,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 docker拉取mysql镜像半个小时依然没有成功,改用阿里云镜像加速器。 ...
2022年7月22日 21:36CVE-2020-25540: ThinkAdmin 6 – Local File Inclusion
漏洞标题 CVE-2020-25540: ThinkAdmin 6 - Local File Inclusion 漏洞描述 ThinkAdmin version 6 is affected by a local file inclusion vulnerability because an unauthorized attacker can ...
2020年9月6日 14:42CVE-2024-48651: ProFTPD ≤ 1.3.8b – Privilege Escalation via mod_sql
漏洞标题 CVE-2024-48651: ProFTPD ≤ 1.3.8b - Privilege Escalation via mod_sql 漏洞描述 ProFTPD versions through 1.3.8b (before commit cec01cc) contain a vulnerability in the mod_sq...
2024年4月21日 05:59CVE-2021-45793: Slims9 Bulian 9.4.2 – SQL Injection
漏洞标题 CVE-2021-45793: Slims9 Bulian 9.4.2 - SQL Injection 漏洞描述 Slims9 Bulian 9.4.2 is affected by SQL injection in lib/comment.inc.php. User data can be obtained. PoC代码
2021年1月9日 11:31CVE-2024-7332: TOTOLINK CP450 v4.1.0cu.747_B20191224 – Hard-Coded Password Vulnerability
漏洞标题 CVE-2024-7332: TOTOLINK CP450 v4.1.0cu.747_B20191224 - Hard-Coded Password Vulnerability 漏洞描述 A critical vulnerability has been discovered in TOTOLINK CP450 version 4....
2024年3月30日 05:18CVE-2016-3978: Fortinet FortiOS – Open Redirect/Cross-Site Scripting
漏洞标题 CVE-2016-3978: Fortinet FortiOS - Open Redirect/Cross-Site Scripting 漏洞描述 FortiOS Web User Interface in 5.0.x before 5.0.13, 5.2.x before 5.2.3, and 5.4.x before 5.4.0...
2016年6月21日 11:06
2026年10月10日 11:45
2026年10月9日 11:45
2026年10月8日 11:45
2026年10月7日 15:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

