
最新发布第135页

CVE-2012-0392: Apache Struts2 S2-008 RCE
漏洞标题 CVE-2012-0392: Apache Struts2 S2-008 RCE 漏洞描述 The CookieInterceptor component in Apache Struts before 2.3.1.1 does not use the parameter-name whitelist, which allows r...
 2012年4月26日 07:38
CVE-2025-46818: Redis Lua Sandbox < 8.2.2 - Cross-User Escape
漏洞标题 CVE-2025-46818: Redis Lua Sandbox < 8.2.2 - Cross-User Escape 漏洞描述 Redis is an open source, in-memory database that persists on disk. Versions 8.2.1 and below allow...
2025年8月27日 19:49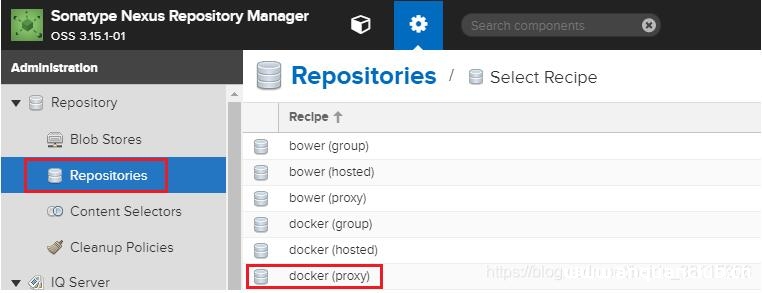
利用nexus作为私库进行代理docker,进行上传和下载镜像操作_docker
这篇文章主要介绍了利用nexus作为私库进行代理docker,进行上传和下载镜像操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 一、nexus的配置 1.创建docker proxy 用于从外...
2023年1月22日 21:29Apache Struts2(S2-062)远程代码执行漏洞(CVE-2021-31805)
漏洞标题 Apache Struts2(S2-062)远程代码执行漏洞(CVE-2021-31805) 漏洞描述 Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Apache Struts< 2.5.30存在OGNL表达式注入漏...
2021年9月23日 20:54
Tomcat将配置文件放在外部的解决方法_Tomcat
这篇文章主要给大家介绍了关于Tomcat将配置文件放在外部的相关资料,对平时工作来说还是挺实用的,需要的朋友们下面随着小编一起来看看吧 问题 我们在平常开发的时候, 如果要把项目部署到Tomcat...
2022年6月15日 09:45CVE-2022-3590: WordPress <= 6.2 - Server Side Request Forgery
漏洞标题 CVE-2022-3590: WordPress <= 6.2 - Server Side Request Forgery 漏洞描述 WordPress is affected by an unauthenticated blind SSRF in the pingback feature. Because of a TOCT...
2022年11月8日 18:03
如何解决点击 tomcat9.exe闪退的问题_Tomcat
这篇文章主要介绍了如何解决点击 tomcat9.exe闪退的问题,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 有读者联系问,怎么tomcat启动都会出现问...
2022年7月2日 20:37CVE-2023-27847: PrestaShop xipblog – SQL Injection
漏洞标题 CVE-2023-27847: PrestaShop xipblog - SQL Injection 漏洞描述 In the blog module (xipblog), an anonymous user can perform SQL injection. Even though the module has been patc...
2023年6月23日 23:15CVE-2024-4956: Nexus Repository Manager 文件读取漏洞
漏洞标题 CVE-2024-4956: Nexus Repository Manager 文件读取漏洞 漏洞描述 Path Traversal in Sonatype Nexus Repository 3 allows an unauthenticated attacker to read system files. Fixed ...
2024年1月23日 04:07
如何提升Idea启动速度与Tomcat日志乱码问题_Tomcat
这篇文章主要介绍了提升Idea启动速度与Tomcat日志乱码问题,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录前言Idea启动速度Tomcat日志乱码前...
2022年8月20日 21:53CVE-2025-49002: DataEase 远程代码执行漏洞
漏洞标题 CVE-2025-49002: DataEase 远程代码执行漏洞 漏洞描述 CVE-2025-49002 是由于H2数据库模块没有严格过滤用户输入的JDBC连接参数,可使用大小写绕过补丁。攻击者可利用这些漏洞实现未授...
2025年10月29日 21:13CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion
漏洞标题 CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion 漏洞描述 Suprema BioStar before 2.8.2 Video Extension allows remote attackers can read arbitrary files fro...
2020年7月26日 09:51CVE-2025-58434: Flowise <= 3.0.5 - Account Takeover
漏洞标题 CVE-2025-58434: Flowise <= 3.0.5 - Account Takeover 漏洞描述 Flowise versions 3.0.5 and earlier had a vulnerability in the forgot-password endpoint, which returned vali...
2025年11月16日 10:08CVE-2020-12800: WordPress Contact Form 7 <1.3.3.3 - Remote Code Execution
漏洞标题 CVE-2020-12800: WordPress Contact Form 7 <1.3.3.3 - Remote Code Execution 漏洞描述 WordPress Contact Form 7 before 1.3.3.3 allows unrestricted file upload and remote co...
2020年1月12日 00:07CVE-2023-33629: H3C Magic R300-2100M – Remote Code Execution
漏洞标题 CVE-2023-33629: H3C Magic R300-2100M - Remote Code Execution 漏洞描述 H3C Magic R300 version R300-2100MV100R004 was discovered to contain a stack overflow via the Deltrigg...
2023年12月24日 17:20CVE-2022-29153: HashiCorp Consul/Consul Enterprise – Server-Side Request Forgery
漏洞标题 CVE-2022-29153: HashiCorp Consul/Consul Enterprise - Server-Side Request Forgery 漏洞描述 HashiCorp Consul and Consul Enterprise up to 1.9.16, 1.10.9, and 1.11 are suscept...
2022年2月2日 04:12
2026年10月16日 11:45
2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

