
最新发布第138页

CVE-2022-22897: PrestaShop AP Pagebuilder <= 2.4.4 - SQL Injection
漏洞标题 CVE-2022-22897: PrestaShop AP Pagebuilder <= 2.4.4 - SQL Injection 漏洞描述 A SQL injection vulnerability in the product_all_one_img and image_product parameters of the...
 2022年2月2日 19:42
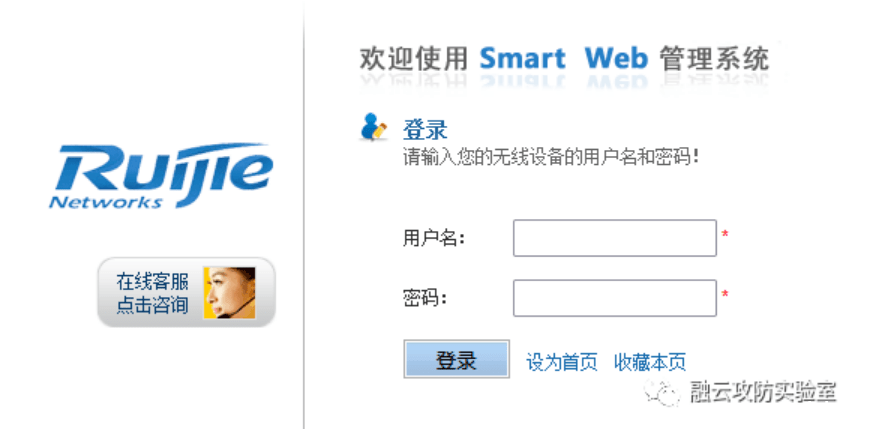
锐捷 Smartweb管理系统 命令注入漏洞(未公布)
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 锐捷 Smartweb管理系统 命令注入漏洞(未公布) 锐捷网络是一家拥有包括交换机、路由器、软件、安全防火墙、无线产品、存储等全系列的...
2026年2月13日 12:53
奇葩漏洞面面观
下载地址:http://i0x0fy4ibf.feishu.cn/file/boxcnP2siX6p3DN3YjKEomok3kb 简介 0x00 众里寻他千百度 0x01 精骛八极,心游万仞 0x02 天下大事,必作于细 0x03 不破楼兰终不还 0x04 工欲善其事,...
2022年3月10日 23:37CVE-2015-7377: WordPress Pie-Register <2.0.19 - Cross-Site Scripting
漏洞标题 CVE-2015-7377: WordPress Pie-Register <2.0.19 - Cross-Site Scripting 漏洞描述 WordPress Pie Register before 2.0.19 contains a reflected cross-site scripting vulnerabili...
2015年8月29日 05:13CVE-2018-1000861: Jenkins – Remote Command Injection
漏洞标题 CVE-2018-1000861: Jenkins - Remote Command Injection 漏洞描述 Jenkins 2.153 and earlier and LTS 2.138.3 and earlier are susceptible to a remote command injection via stapl...
2018年12月10日 18:51CVE-2018-19458: PHP Proxy 3.0.3 – Local File Inclusion
漏洞标题 CVE-2018-19458: PHP Proxy 3.0.3 - Local File Inclusion 漏洞描述 PHP Proxy 3.0.3 is susceptible to local file inclusion vulnerabilities that allow unauthenticated users to ...
2018年12月21日 16:13CVE-2023-2272: Tiempo.com <= 0.1.2 - Cross-Site Scripting
漏洞标题 CVE-2023-2272: Tiempo.com <= 0.1.2 - Cross-Site Scripting 漏洞描述 Tiempo.com before 0.1.2 is susceptible to cross-site scripting via the page parameter due to insuffic...
2023年1月30日 19:03CVE-2023-2780: Mlflow <2.3.1 - Local File Inclusion Bypass
漏洞标题 CVE-2023-2780: Mlflow <2.3.1 - Local File Inclusion Bypass 漏洞描述 Path Traversal: '\..\filename' in GitHub repository mlflow/mlflow prior to 2.3.1. PoC代码
2023年6月30日 19:53SSRF(服务端请求伪造)《⽩帽⼦讲漏洞修复与防御》书籍样稿
地址:http://i0x0fy4ibf.feishu.cn/file/boxcn1w1nZXPVtJa8lVa7wsw8Fg 简介: 0x01 漏洞介绍 0x02 漏洞代码 0x03 漏洞复现 0x04 漏洞危害 0x05 修复方案 0x06 漏洞场景
2022年3月10日 23:37CVE-2023-46347: PrestaShop Step by Step products Pack – SQL Injection
漏洞标题 CVE-2023-46347: PrestaShop Step by Step products Pack - SQL Injection 漏洞描述 In the module “Step by Step products Pack” (ndk_steppingpack) up to 1.5.6 from NDK Design ...
2023年3月10日 15:34CirCarLifeScada停车场自动化管理系统repository-信息泄漏(CVE-2018-16668)
漏洞标题 CirCarLifeScada停车场自动化管理系统repository-信息泄漏(CVE-2018-16668) 漏洞描述 【漏洞对象】Circontrol CirCarLife Scada 【漏洞描述】 Circontrol CirCarLifeScada是西班牙Circ...
2018年10月19日 05:55CVE-2025-55523: Agent-Zero 0.8.0 – 0.9.4 – Arbitrary File Download
漏洞标题 CVE-2025-55523: Agent-Zero 0.8.0 - 0.9.4 - Arbitrary File Download 漏洞描述 Agent-Zero v0.8.0 - 0.9.4 contains a path traversal caused by improper validation in /api/downl...
2025年3月10日 07:22CVE-2017-14725: WordPress < 4.8.2 - Authenticated Open Redirect
漏洞标题 CVE-2017-14725: WordPress < 4.8.2 - Authenticated Open Redirect 漏洞描述 WordPress versions before 4.8.2 contain an open redirect caused by improper validation in wp-ad...
2017年6月11日 02:46CVE-2022-46888: NexusPHP <1.7.33 - Cross-Site Scripting
漏洞标题 CVE-2022-46888: NexusPHP <1.7.33 - Cross-Site Scripting 漏洞描述 NexusPHP before 1.7.33 contains multiple cross-site scripting vulnerabilities via the secret parameter ...
2022年9月6日 12:44CVE-2023-7028: GitLab – Account Takeover via Password Reset
漏洞标题 CVE-2023-7028: GitLab - Account Takeover via Password Reset 漏洞描述 An issue has been discovered in GitLab CE/EE affecting all versions from 16.1 prior to 16.1.6, 16.2 pr...
2023年11月15日 11:20CVE-2023-45852: Viessmann Vitogate 300 – Remote Code Execution
漏洞标题 CVE-2023-45852: Viessmann Vitogate 300 - Remote Code Execution 漏洞描述 In Vitogate 300 2.1.3.0, /cgi-bin/vitogate.cgi allows an unauthenticated attacker to bypass authent...
2023年12月13日 21:10
2026年10月14日 11:45
2026年10月13日 11:45
2026年10月12日 11:45
2026年10月11日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

