
最新发布第147页

CVE-2010-2036: Joomla! Component Percha Fields Attach 1.0 – Directory Traversal
漏洞标题 CVE-2010-2036: Joomla! Component Percha Fields Attach 1.0 - Directory Traversal 漏洞描述 A directory traversal vulnerability in the Percha Fields Attach (com_perchafieldsa...
 2010年12月24日 17:03
CVE-2021-44228: Apache Log4j2 Remote Code Injection
漏洞标题 CVE-2021-44228: Apache Log4j2 Remote Code Injection 漏洞描述 Apache Log4j2 <=2.14.1 JNDI features used in configuration, log messages, and parameters do not protect aga...
2021年2月26日 10:15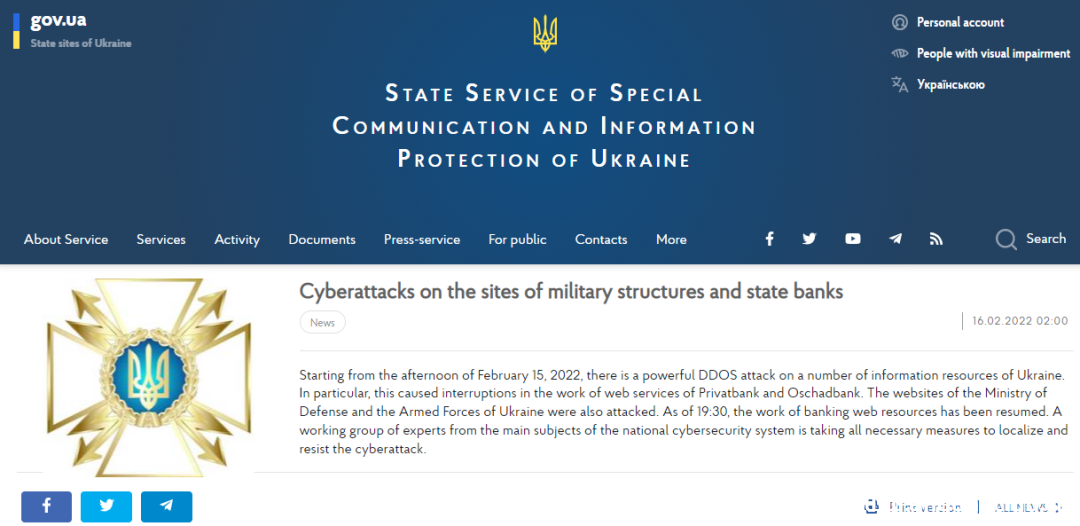
乌克兰国防部及国有银行网站因DDoS攻击而关闭
据报道,乌克兰国防部和武装部队以及该国的两家国有银行Privatbank(乌克兰最大的银行)和Oschadbank(国家储蓄银行)的官方门户网站于2月15日受到分布式拒绝服务(DDoS)攻击。 本次网络...
2022年3月10日 23:40CVE-2020-16952: Microsoft SharePoint – Remote Code Execution
漏洞标题 CVE-2020-16952: Microsoft SharePoint - Remote Code Execution 漏洞描述 Microsoft SharePoint is vulnerable to a remote code execution when the software fails to check the so...
2020年8月29日 09:02CVE-2019-11248: Debug Endpoint pprof – Exposure Detection
漏洞标题 CVE-2019-11248: Debug Endpoint pprof - Exposure Detection 漏洞描述 The debugging endpoint /debug/pprof is exposed over the unauthenticated Kubelet healthz port. This debug...
2019年5月3日 00:16CVE-2010-2035: Joomla! Component Percha Gallery 1.6 Beta – Directory Traversal
漏洞标题 CVE-2010-2035: Joomla! Component Percha Gallery 1.6 Beta - Directory Traversal 漏洞描述 A directory traversal vulnerability in the Percha Gallery (com_perchagallery) compo...
2010年4月7日 11:15CVE-2023-6909: Mlflow <2.9.2 - Path Traversal
漏洞标题 CVE-2023-6909: Mlflow <2.9.2 - Path Traversal 漏洞描述 Path Traversal: '\..\filename' in GitHub repository mlflow/mlflow prior to 2.9.2. PoC代码
2023年9月18日 22:49CVE-2023-6018: Mlflow – Arbitrary File Write
漏洞标题 CVE-2023-6018: Mlflow - Arbitrary File Write 漏洞描述 An attacker can overwrite any file on the server hosting MLflow without any authentication. PoC代码
2023年1月28日 18:48CVE-2023-3306: 锐捷(ruijie)RG-EW1200G路由器 远程命令执行(需登录)
漏洞标题 CVE-2023-3306: 锐捷(ruijie)RG-EW1200G路由器 远程命令执行(需登录) 漏洞描述 Ruijie Networks RG-EW1200G是中国锐捷网络(Ruijie Networks)公司的一款无线路由器。 Ruijie Networks...
2023年6月30日 10:13CVE-2019-6703: Total Donations Plugin for WordPress < 2.0.6 - Arbitrary Options Update
漏洞标题 CVE-2019-6703: Total Donations Plugin for WordPress < 2.0.6 - Arbitrary Options Update 漏洞描述 Incorrect access control in migla_ajax_functions.php in the Calmar Webme...
2019年6月17日 12:01CVE-2021-21972: VMware vSphere Client (HTML5) – Remote Code Execution
漏洞标题 CVE-2021-21972: VMware vSphere Client (HTML5) - Remote Code Execution 漏洞描述 VMware vCenter vSphere Client (HTML5) contains a remote code execution vulnerability in a vC...
2021年4月17日 02:50CVE-2022-0220: WordPress GDPR & CCPA <1.9.27 - Cross-Site Scripting
漏洞标题 CVE-2022-0220: WordPress GDPR & CCPA <1.9.27 - Cross-Site Scripting 漏洞描述 WordPress GDPR & CCPA plugin before 1.9.27 contains a cross-site scripting vulnerab...
2022年10月21日 16:12CVE-2021-24498: WordPress Calendar Event Multi View <1.4.01 - Cross-Site Scripting
漏洞标题 CVE-2021-24498: WordPress Calendar Event Multi View <1.4.01 - Cross-Site Scripting 漏洞描述 WordPress Calendar Event Multi View plugin before 1.4.01 contains an unauthe...
2021年12月30日 04:31CVE-2024-10908: FastChat – Open Redirect
漏洞标题 CVE-2024-10908: FastChat - Open Redirect 漏洞描述 Detects an open redirect vulnerability in lm-sys/fastchat version 0.2.36, which allows attackers to redirect users to mal...
2024年7月23日 06:12Adobe Commerce/Magento SessionReaper /customer/address_file/upload 文件上传漏洞(CVE-2025-54236)
漏洞标题 Adobe Commerce/Magento SessionReaper /customer/address_file/upload 文件上传漏洞(CVE-2025-54236) 漏洞描述 Adobe Commerce是一款由Adobe公司开发的电子商务平台,广泛应用于全...
2025年1月11日 22:04CVE-2010-1658: Joomla! Component NoticeBoard 1.3 – Local File Inclusion
漏洞标题 CVE-2010-1658: Joomla! Component NoticeBoard 1.3 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Code-Garage NoticeBoard (com_noticeboard) compo...
2010年2月10日 16:32
2026年10月18日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

