
最新发布第14页

CVE-2022-22947: Spring Cloud Gateway Code Injection
漏洞标题 CVE-2022-22947: Spring Cloud Gateway Code Injection 漏洞描述 Applications using Spring Cloud Gateway prior to 3.1.1+ and 3.0.7+ are vulnerable to a code injection attack w...
 2022年12月27日 16:07
CVE-2010-0219: Apache Axis2 Default Login
漏洞标题 CVE-2010-0219: Apache Axis2 Default Login 漏洞描述 Apache Axis2, as used in dswsbobje.war in SAP BusinessObjects Enterprise XI 3.2, CA ARCserve D2D r15, and other products...
2010年11月11日 04:38CVE-2021-41773: Apache 2.4.49 – Path Traversal and Remote Code Execution
漏洞标题 CVE-2021-41773: Apache 2.4.49 - Path Traversal and Remote Code Execution 漏洞描述 A flaw was found in a change made to path normalization in Apache HTTP Server 2.4.49. An ...
2021年7月15日 17:03CVE-2024-32735: CyberPower – Missing Authentication
漏洞标题 CVE-2024-32735: CyberPower - Missing Authentication 漏洞描述 An issue regarding missing authentication for certain utilities exists in CyberPower PowerPanel Enterprise pri...
2024年10月12日 22:09
如何快速批量替换文件名部分文字
问题场景 有热心网友问有没有方法可以快速替换文件的前缀或者后缀? 解决方案 您可以先下载个everything 我们这里搜索想批量替换的前缀,譬如【安全小天地】我想替换成其他的 我们搜索看到有下...

 2023年1月13日 19:58
CVE-2024-37728: OfficeWeb365 Indexs Interface – Arbitrary File Read
漏洞标题 CVE-2024-37728: OfficeWeb365 Indexs Interface - Arbitrary File Read 漏洞描述 There is any file reading in the officeWeb365 Indexs interface. PoC代码
2024年2月29日 15:27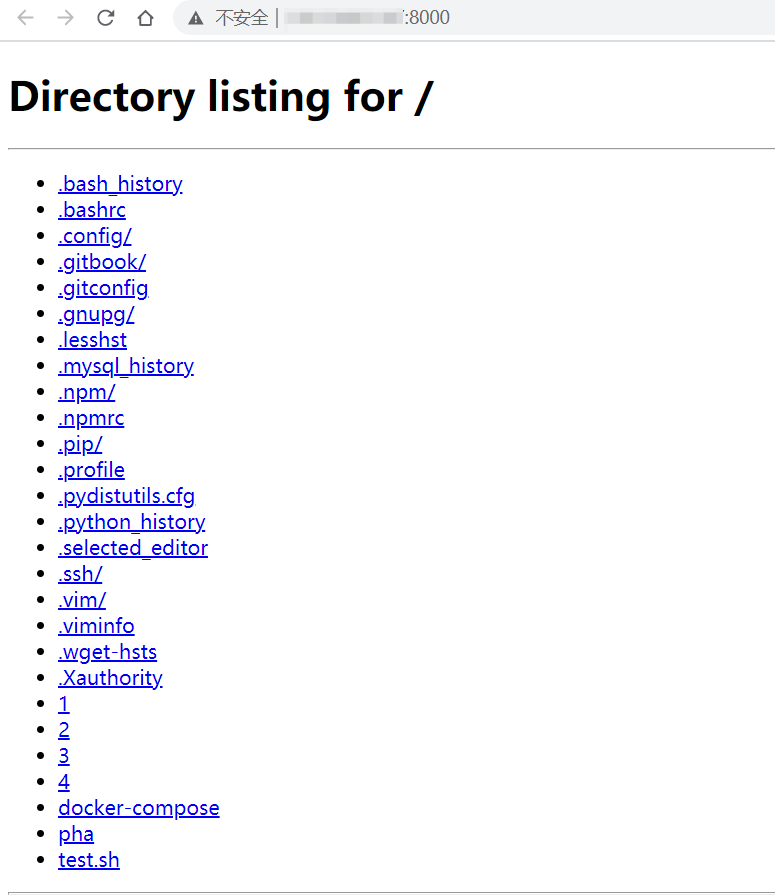
寻找python开启web服务中的宝藏
测试过程中,有时需要临时用python开启web服务,默认是允许目录浏览的,如果不及时关闭进程,可能会被窃取当前目录中的文件。 fofa(也可以尝试添加python2的服务器版本): ((server='SimpleHTTP/...
2022年3月10日 23:34CVE-2022-25082: TOTOLink – Unauthenticated Command Injection
漏洞标题 CVE-2022-25082: TOTOLink - Unauthenticated Command Injection 漏洞描述 TOTOLink A950RG V5.9c.4050_B20190424 and V4.1.2cu.5204_B20210112 were discovered to contain a command...
2022年4月13日 16:01CVE-2022-3869: Froxlor < 0.10.38.2. - HTML Injection
漏洞标题 CVE-2022-3869: Froxlor < 0.10.38.2. - HTML Injection 漏洞描述 HTML Injection in GitHub repository froxlor/froxlor prior to 0.10.38.2. PoC代码
2022年8月7日 13:01CVE-2024-4348: osCommerce v4.0 – Cross-site Scripting
漏洞标题 CVE-2024-4348: osCommerce v4.0 - Cross-site Scripting 漏洞描述 A vulnerability, which was classified as problematic, was found in osCommerce 4. Affected is an unknown func...
2024年11月27日 09:02CVE-2020-0618: Microsoft SQL Server Reporting Services – Remote Code Execution
漏洞标题 CVE-2020-0618: Microsoft SQL Server Reporting Services - Remote Code Execution 漏洞描述 Microsoft SQL Server Reporting Services is vulnerable to a remote code execution vu...
2020年6月25日 10:10CVE-2010-0219: Apache Axis2 Default Login
漏洞标题 CVE-2010-0219: Apache Axis2 Default Login 漏洞描述 Apache Axis2, as used in dswsbobje.war in SAP BusinessObjects Enterprise XI 3.2, CA ARCserve D2D r15, and other products...
2010年9月25日 08:49CVE-2021-25298: Nagios XI 5.5.6-5.7.5 – Authenticated Remote Command Injection
漏洞标题 CVE-2021-25298: Nagios XI 5.5.6-5.7.5 - Authenticated Remote Command Injection 漏洞描述 Nagios XI 5.5.6 through 5.7.5 is susceptible to authenticated remote command inject...
2021年5月28日 06:20CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 – Privilege Escalation
漏洞标题 CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 - Privilege Escalation 漏洞描述 Privilege escalation vulnerability exists in the Frontend Logi...
2025年6月10日 10:05CVE-2020-9376: D-Link DIR-610 Devices – Information Disclosure
漏洞标题 CVE-2020-9376: D-Link DIR-610 Devices - Information Disclosure 漏洞描述 D-Link DIR-610 devices allow information disclosure via SERVICES=DEVICE.ACCOUNT%0AAUTHORIZED_GROUP=...
2020年8月12日 13:44CVE-2025-22457: Ivanti Connect Secure – Stack-based Buffer Overflow
漏洞标题 CVE-2025-22457: Ivanti Connect Secure - Stack-based Buffer Overflow 漏洞描述 Ivanti Connect Secure before version 22.7R2.6, Ivanti Policy Secure before version 22.7R1.4, a...
2025年12月14日 18:12
2026年10月28日 11:45
2026年10月27日 11:46
2026年10月26日 11:45
2026年10月25日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

