
最新发布第158页

Apache ActiveMQ CVE-2023-46604 远程代码执行 – 阶段1:漏洞利用尝试
漏洞标题 Apache ActiveMQ CVE-2023-46604 远程代码执行 - 阶段1:漏洞利用尝试 漏洞描述 Apache ActiveMQ存在远程代码执行漏洞。此漏洞是由于ActiveMQ对用户的输入反序列化后缺乏校验导致的。...
 2023年3月5日 22:17
CVE-2018-5233: Grav CMS <1.3.0 - Cross-Site Scripting
漏洞标题 CVE-2018-5233: Grav CMS <1.3.0 - Cross-Site Scripting 漏洞描述 Grav CMS before 1.3.0 is vulnerable to cross-site scripting via system/src/Grav/Common/Twig/Twig.php and ...
2018年10月21日 10:12CVE-2023-3479: Hestiacp <= 1.7.7 - Cross-Site Scripting
漏洞标题 CVE-2023-3479: Hestiacp <= 1.7.7 - Cross-Site Scripting 漏洞描述 Cross-site Scripting (XSS) - Reflected in GitHub repository hestiacp/hestiacp prior to 1.7.8. PoC代码
2023年6月6日 22:37CVE-2020-35985: Rukovoditel <= 2.7.2 - Cross Site Scripting
漏洞标题 CVE-2020-35985: Rukovoditel <= 2.7.2 - Cross Site Scripting 漏洞描述 A stored cross site scripting (XSS) vulnerability in the 'Global Lists" feature of Rukovo...
2020年8月27日 00:16CVE-2024-10783: WordPress Plugin MainWP Child – Authentication Bypass
漏洞标题 CVE-2024-10783: WordPress Plugin MainWP Child - Authentication Bypass 漏洞描述 The plugin is vulnerable to an authentication bypass that allows an unauthenticated user to ...
2024年10月27日 00:30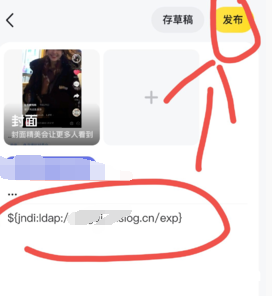
挖洞随手记1
挖洞之捡漏ssrf和log4j的小tips 以发帖为例(通俗易懂) 前言:挖洞要一步一步看,一步一步走 1:咱就是说,发帖 2:然后这个时候宝子们就可以看看有没有请求dnslog 成功(一般情况是没有的,dd...
2022年3月10日 23:30CVE-2010-1478: Joomla! Component Jfeedback 1.2 – Local File Inclusion
漏洞标题 CVE-2010-1478: Joomla! Component Jfeedback 1.2 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Ternaria Informatica Jfeedback! (com_jfeedback) c...
2010年9月7日 02:04CVE-2024-48651: ProFTPD ≤ 1.3.8b – Privilege Escalation via mod_sql
漏洞标题 CVE-2024-48651: ProFTPD ≤ 1.3.8b - Privilege Escalation via mod_sql 漏洞描述 ProFTPD versions through 1.3.8b (before commit cec01cc) contain a vulnerability in the mod_sq...
2024年3月9日 16:30CVE-2025-52970: Fortinet FortiWeb – Authentication Bypass to Admin Privilege
漏洞标题 CVE-2025-52970: Fortinet FortiWeb - Authentication Bypass to Admin Privilege 漏洞描述 A improper handling of parameters in Fortinet FortiWeb versions 7.6.3 and below, vers...
2025年6月20日 21:26Citrix ADC 远程代码执行(CVE-2019-19781)
漏洞标题 Citrix ADC 远程代码执行(CVE-2019-19781) 漏洞描述 Citrix旗下多款交付控制器和网关存在RCE漏洞,攻击者在无需身份验证的情况下就可执行任意命令。CitrixADC(NetScalers)中的目录穿...
2019年7月1日 18:49CVE-2025-34291: Langflow AI <= 1.6.9 - CORS Misconfiguration
漏洞标题 CVE-2025-34291: Langflow AI <= 1.6.9 - CORS Misconfiguration 漏洞描述 Langflow AI versions 1.6.9 and earlier are vulnerable to a CORS misconfiguration that allows any o...
2025年5月4日 10:39CVE-2023-48788: Fortinet Forticlient Endpoint Management Server – SQL Injection
漏洞标题 CVE-2023-48788: Fortinet Forticlient Endpoint Management Server - SQL Injection 漏洞描述 A improper neutralization of special elements used in an sql command ('sql in...
2023年4月3日 00:52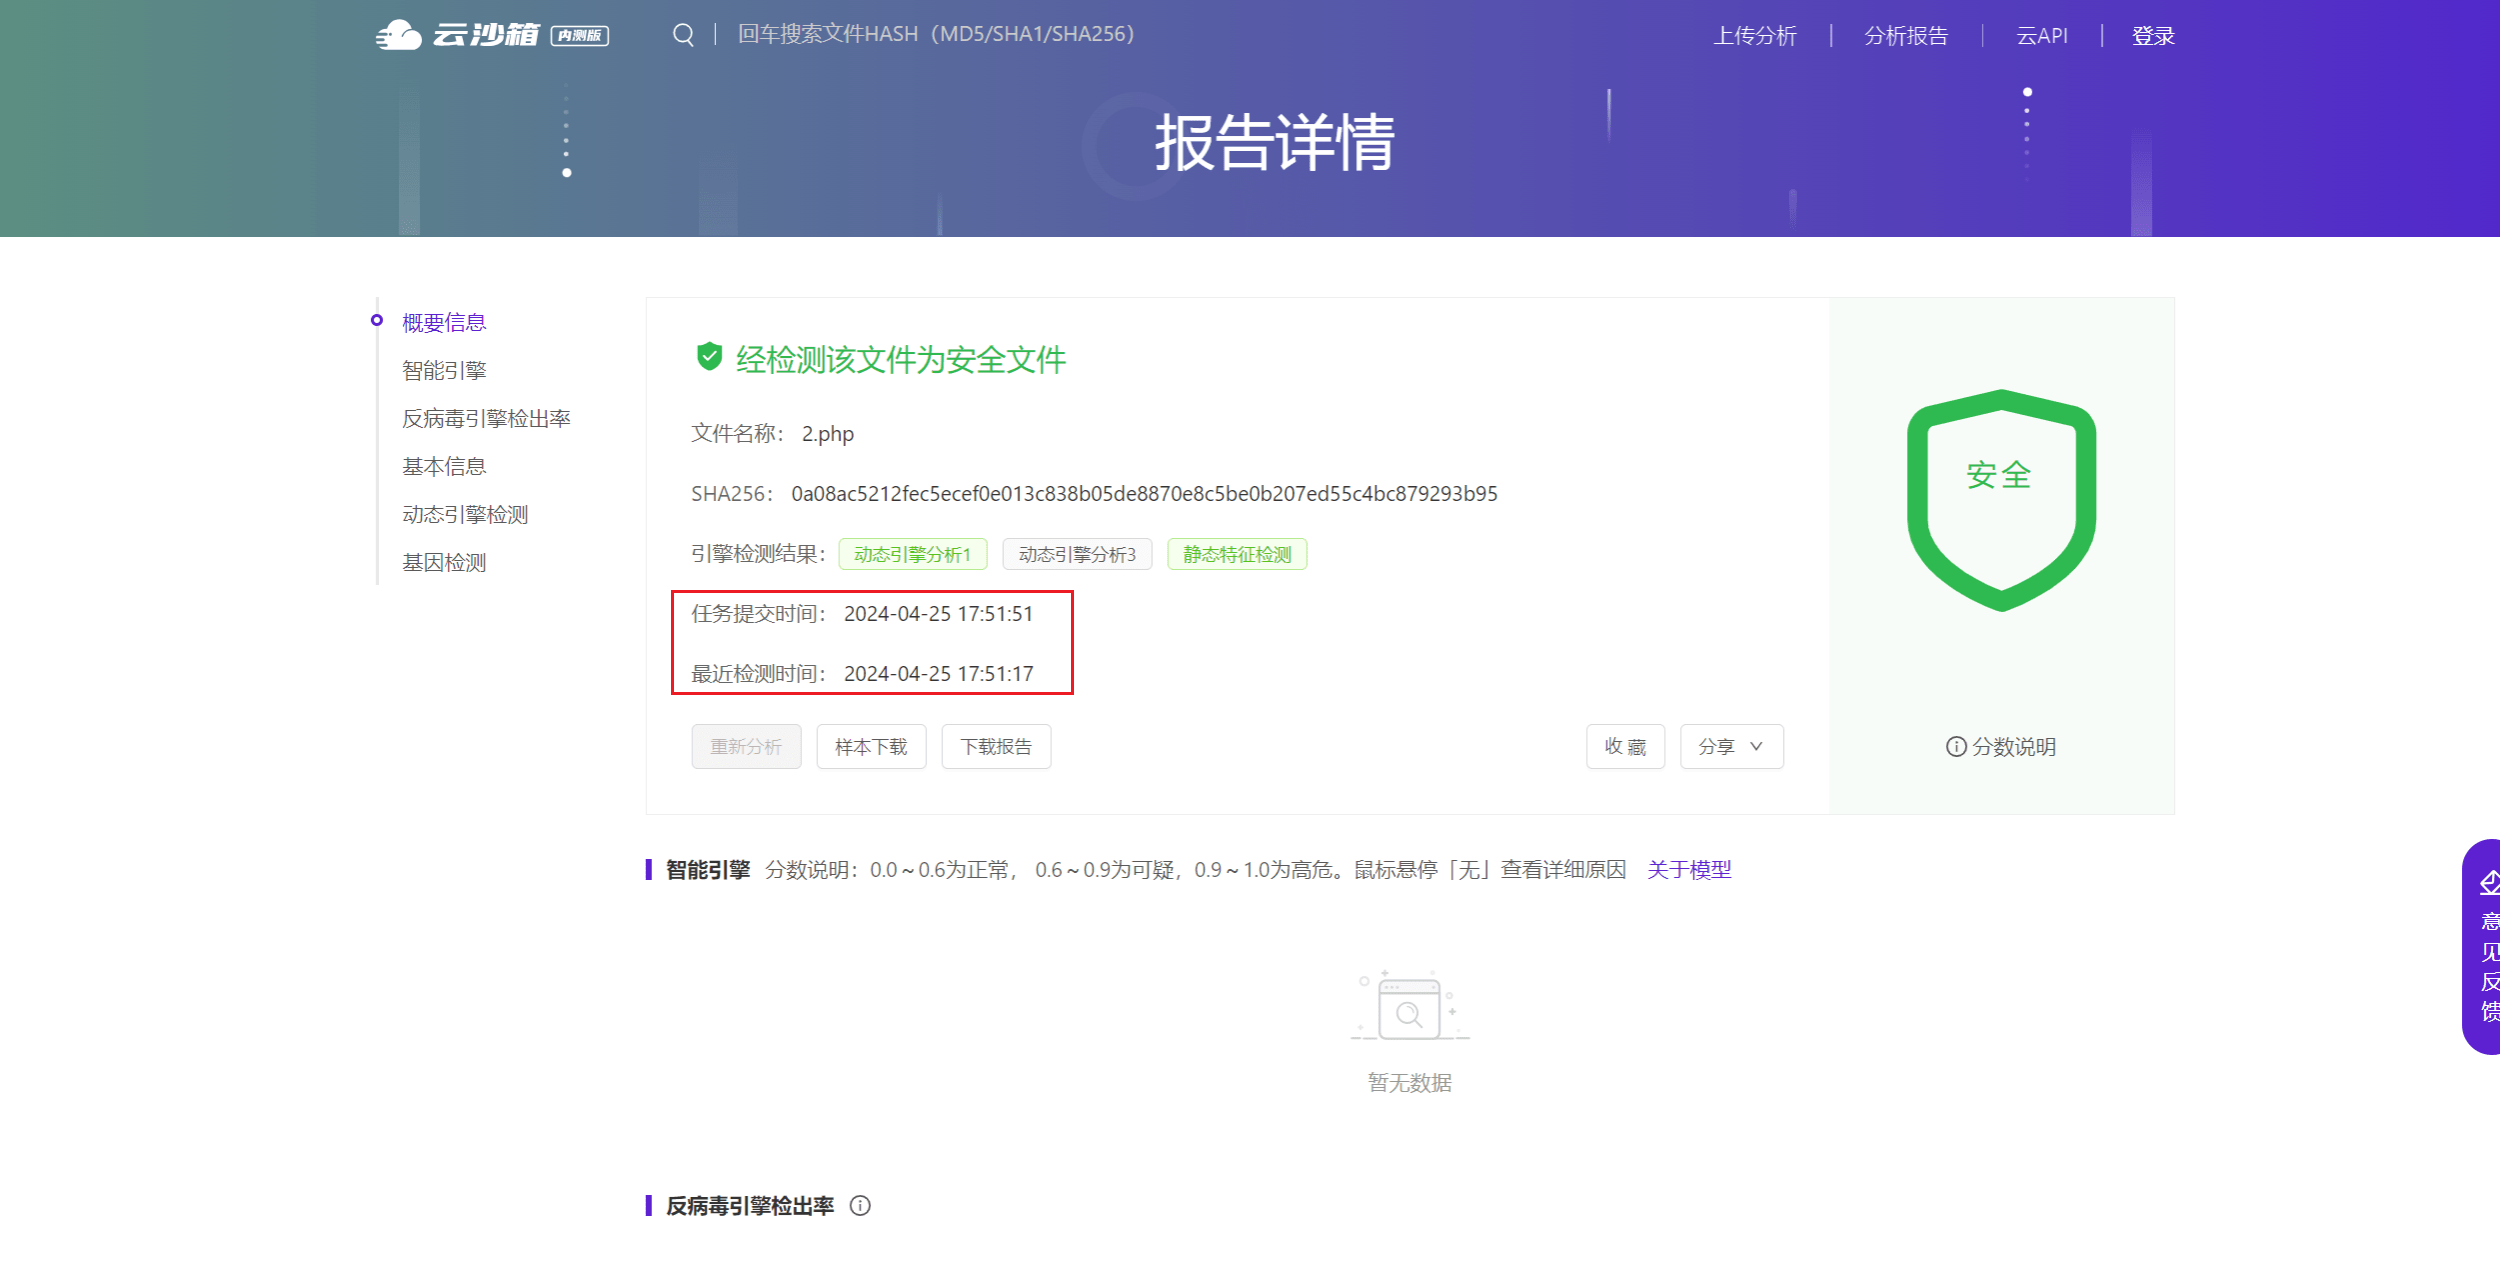
最新webshell免杀过在线查杀平台(php版)
前言 很长一段时间没有更新文章了,今天分享一篇今天下午刚刚出来的php免杀webshell,主要是对函数system进行混淆,然后执行命令 免杀思路 总得来说,目前的主流免杀主要有以下几种: 分析统计...

 2024年4月25日 23:05
CVE-2018-11222: Pandora FMS <=7.0NG.722 - Remote Code Execution
漏洞标题 CVE-2018-11222: Pandora FMS <=7.0NG.722 - Remote Code Execution 漏洞描述 Pandora FMS versions <=7.0NG.722 are vulnerable to unauthenticated remote code execution by ...
2018年12月5日 00:49CVE-2025-2711: Yonyou UFIDA ERP-NC V5.0 – Cross-Site Scripting
漏洞标题 CVE-2025-2711: Yonyou UFIDA ERP-NC V5.0 - Cross-Site Scripting 漏洞描述 Yonyou UFIDA ERP-NC V5.0 is vulnerable to reflected cross-site scripting (XSS) via the langcode par...
2025年9月19日 05:33CVE-2024-2961: PHP – LFR to Remote Code Execution
漏洞标题 CVE-2024-2961: PHP - LFR to Remote Code Execution 漏洞描述 PHP Local File Read vulnerability leading to Remote Code Execution PoC代码
2024年4月14日 23:54
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

