
最新发布第158页

Aspera Faspex CVE-2022-47986 远程代码执行漏洞
漏洞标题 Aspera Faspex CVE-2022-47986 远程代码执行漏洞 漏洞描述 Aspera Faspex CVE-2022-47986 远程 PoC代码 暂无
 2022年5月16日 23:40
CVE-2025-1025: Cockpit < 2.4.1 - Arbitrary File Upload
漏洞标题 CVE-2025-1025: Cockpit < 2.4.1 - Arbitrary File Upload 漏洞描述 Versions of the package cockpit-hq/cockpit before 2.4.1 are vulnerable to Arbitrary File Upload where an...
2025年7月7日 21:19CVE-2021-28169: Eclipse Jetty ConcatServlet – Information Disclosure
漏洞标题 CVE-2021-28169: Eclipse Jetty ConcatServlet - Information Disclosure 漏洞描述 Eclipse Jetty through 9.4.40, through 10.0.2, and through 11.0.2 is susceptible to informatio...
2021年12月6日 08:22
[第一章 web入门]粗心的小李 – buu刷题笔记
打开题目就告诉我们是git泄露,那没办法,我们就查询git备份下载呗 GitHack的下载安装 下载地址:http://github.com/lijiejie/GitHack在GitHub上下载源码的压缩包后解压即可使用 需要使用python...

 2022年4月27日 19:20
CVE-2018-5230: Atlassian Jira Confluence – Cross-Site Scripting
漏洞标题 CVE-2018-5230: Atlassian Jira Confluence - Cross-Site Scripting 漏洞描述 Atlassian Jira Confluence before version 7.6.6, from version 7.7.0 before version 7.7.4, from vers...
2018年8月7日 06:13CVE-2022-0441: MasterStudy LMS <2.7.6 - Improper Access Control
漏洞标题 CVE-2022-0441: MasterStudy LMS <2.7.6 - Improper Access Control 漏洞描述 WordPress MasterStudy LMS plugin before 2.7.6 is susceptible to improper access control. The pl...
2022年1月20日 16:52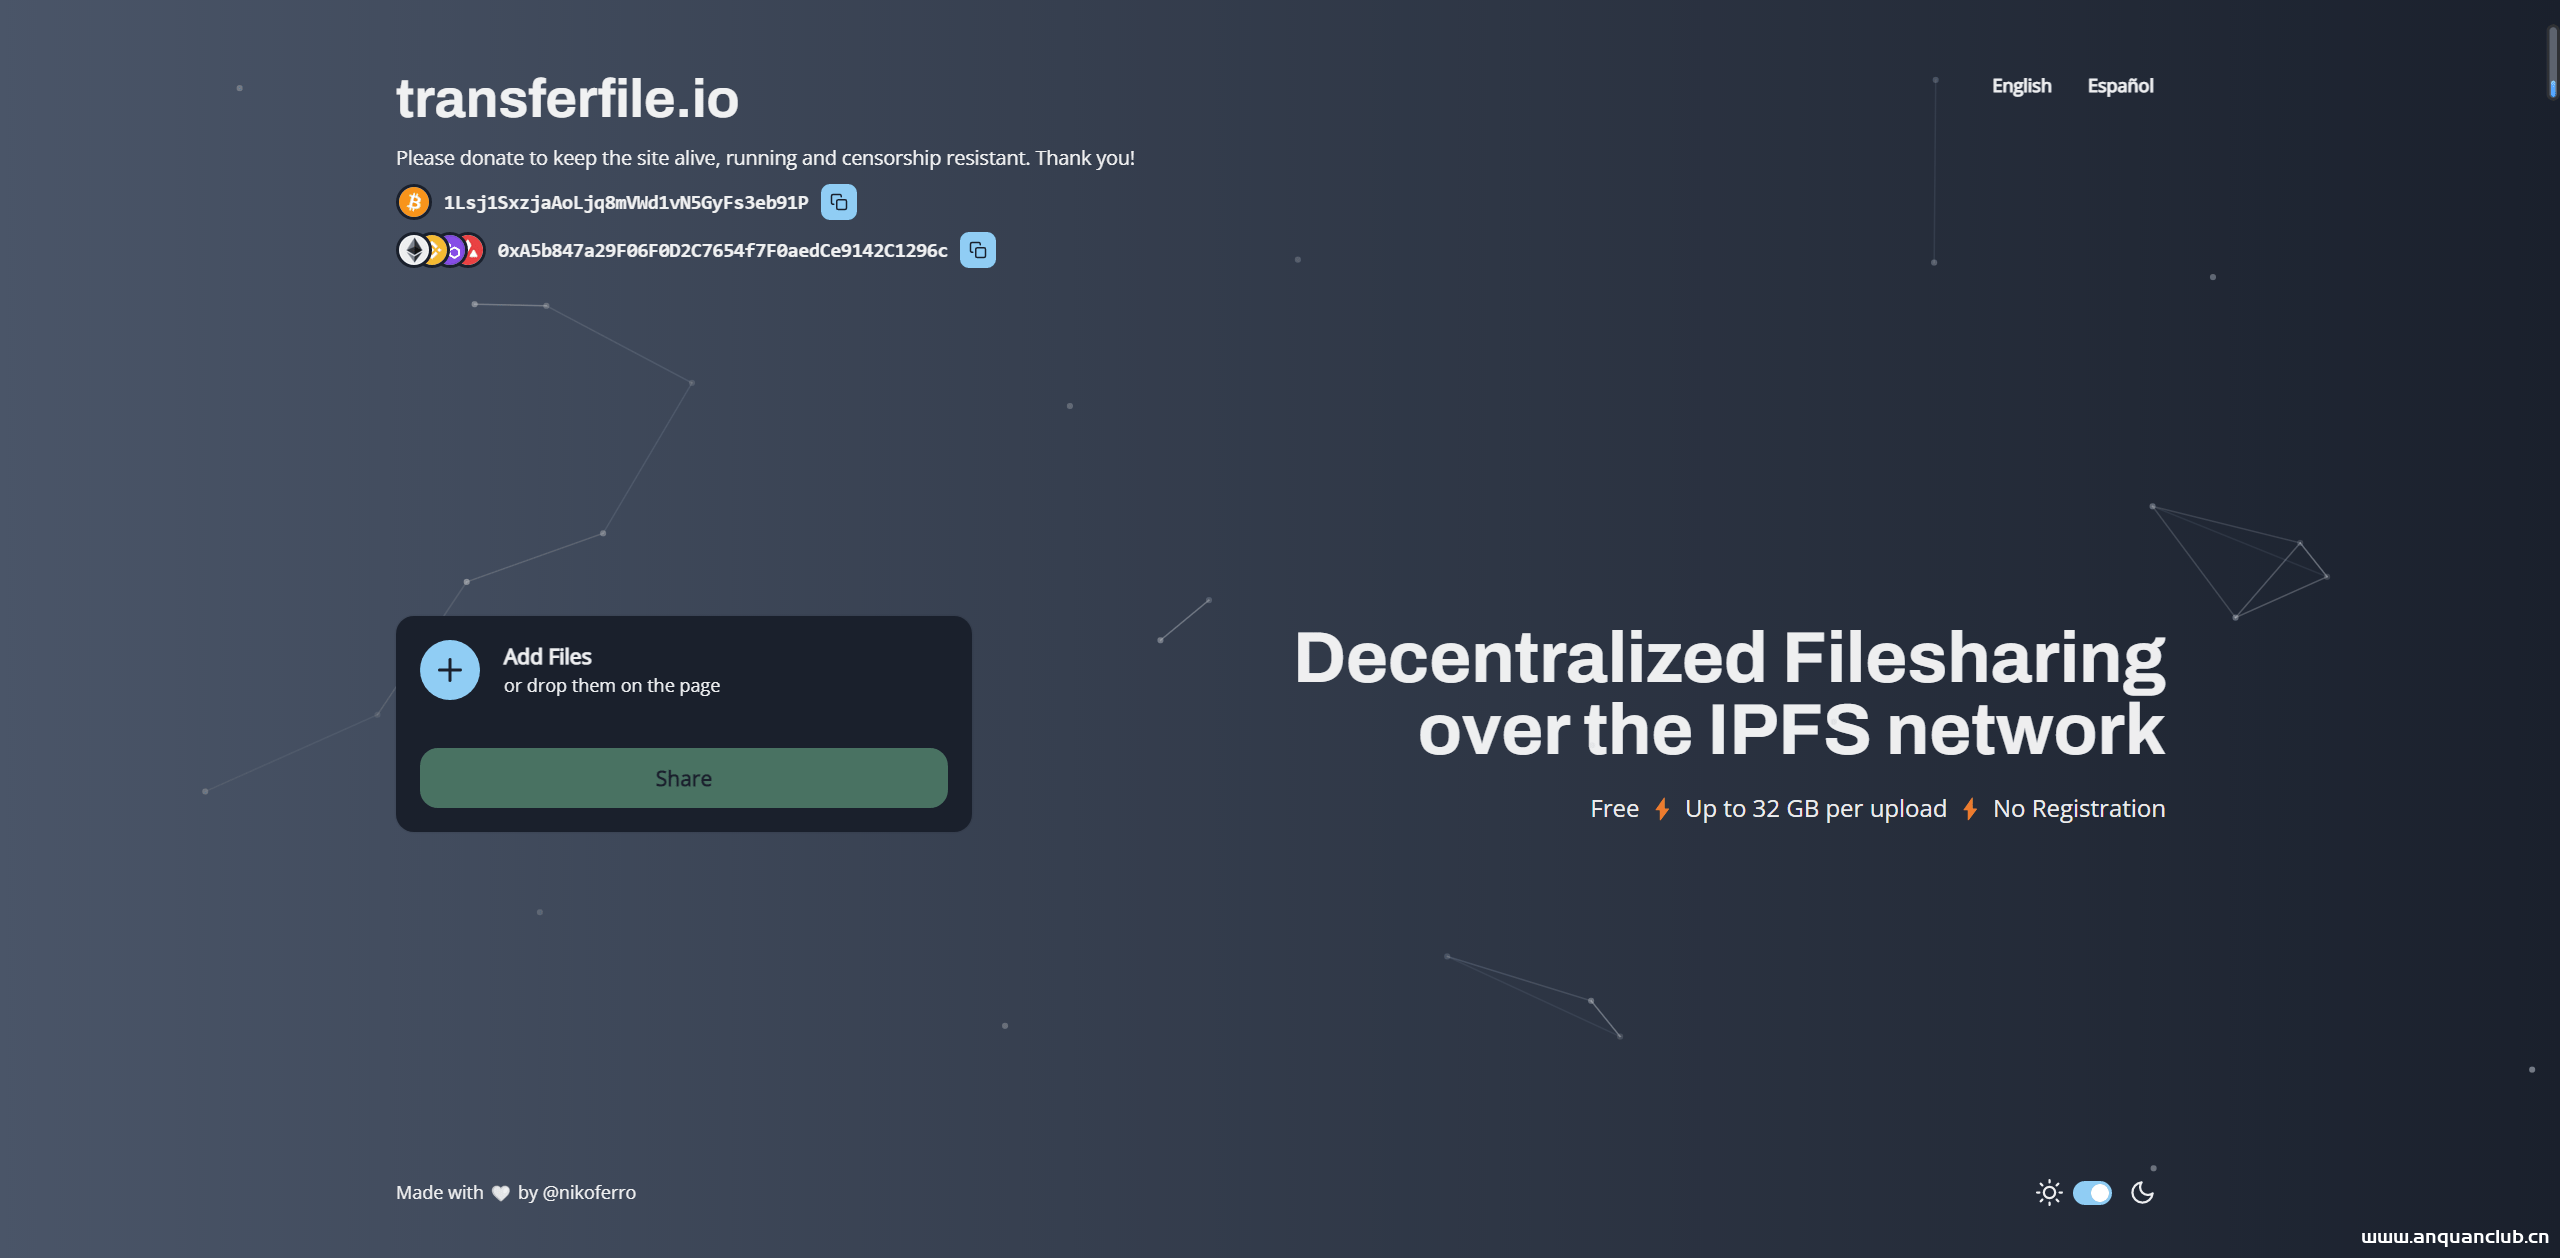
Transferfile – 一个免费的分散式文件共享服务
前言 在线文件共享是一项危险的活动。首先,机密信息很容易落入坏人手中;其次,文件本身存储了大量的识别性数据:数字指纹、地理位置、IP地址等。您可以把自身的在线匿名性提高到200%,但如果...
2023年2月4日 15:03CVE-2010-1956: Joomla! Component Gadget Factory 1.0.0 – Local File Inclusion
漏洞标题 CVE-2010-1956: Joomla! Component Gadget Factory 1.0.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Gadget Factory (com_gadgetfactory) compone...
2010年5月31日 09:13CVE-2018-13380: Fortinet FortiOS – Cross-Site Scripting
漏洞标题 CVE-2018-13380: Fortinet FortiOS - Cross-Site Scripting 漏洞描述 Fortinet FortiOS 6.0.0 to 6.0.4, 5.6.0 to 5.6.7, 5.4.0 to 5.4.12, 5.2 and below versions under SSL VPN web...
2018年3月20日 08:44CVE-2021-33851: WordPress Customize Login Image <3.5.3 - Cross-Site Scripting
漏洞标题 CVE-2021-33851: WordPress Customize Login Image <3.5.3 - Cross-Site Scripting 漏洞描述 WordPress Customize Login Image plugin prior to 3.5.3 contains a cross-site scrip...
2021年4月27日 11:58CVE-2023-27032: PrestaShop AdvancedPopupCreator – SQL Injection
漏洞标题 CVE-2023-27032: PrestaShop AdvancedPopupCreator - SQL Injection 漏洞描述 In the module “Advanced Popup Creator” (advancedpopupcreator) from Idnovate for PrestaShop, a gu...
2023年9月22日 04:30CVE-2019-10475: Jenkins build-metrics 1.3 – Cross-Site Scripting
漏洞标题 CVE-2019-10475: Jenkins build-metrics 1.3 - Cross-Site Scripting 漏洞描述 Jenkins build-metrics 1.3 is vulnerable to a reflected cross-site scripting vulnerability that al...
2019年7月23日 05:26CVE-2022-0783: Multiple Shipping Address Woocommerce < 2.0 - SQL Injection
漏洞标题 CVE-2022-0783: Multiple Shipping Address Woocommerce < 2.0 - SQL Injection 漏洞描述 The Multiple Shipping Address Woocommerce plugin before 2.0 does not properly saniti...
2022年6月1日 19:15CVE-2021-41277 Metabase 信息泄露漏洞
漏洞标题 CVE-2021-41277 Metabase 信息泄露漏洞 漏洞描述 CVE-2021-41277 Metabase 信息泄露漏洞 PoC代码 暂无
2021年11月21日 10:50CVE-2025-3415: Grafana – Exposes DingDing API Keys
漏洞标题 CVE-2025-3415: Grafana - Exposes DingDing API Keys 漏洞描述 An incident occurred where the DingDing alerting integration URL was inadvertently exposed to viewers due to a ...
2025年1月12日 11:26CVE-2022-3869: Froxlor < 0.10.38.2. - HTML Injection
漏洞标题 CVE-2022-3869: Froxlor < 0.10.38.2. - HTML Injection 漏洞描述 HTML Injection in GitHub repository froxlor/froxlor prior to 0.10.38.2. PoC代码
2022年12月2日 00:33
2026年11月4日 11:45
2026年11月3日 11:46
2026年11月2日 11:45
2026年11月2日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53
2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

