
最新发布第160页

CVE-2020-11441: phpMyAdmin 5.0.2 – CRLF Injection
漏洞标题 CVE-2020-11441: phpMyAdmin 5.0.2 - CRLF Injection 漏洞描述 phpMyAdmin 5.0.2 allows CRLF injection, as demonstrated by %0D%0Astring%0D%0A inputs to login form fields causin...
 2020年6月17日 06:53
CVE-2022-1390: WordPress Admin Word Count Column 2.2 – Local File Inclusion
漏洞标题 CVE-2022-1390: WordPress Admin Word Count Column 2.2 - Local File Inclusion 漏洞描述 The plugin does not validate the path parameter given to readfile(), which could allow...
2022年11月17日 21:31CVE-2025-34291: Langflow AI <= 1.6.9 - CORS Misconfiguration
漏洞标题 CVE-2025-34291: Langflow AI <= 1.6.9 - CORS Misconfiguration 漏洞描述 Langflow AI versions 1.6.9 and earlier are vulnerable to a CORS misconfiguration that allows any o...
2025年9月25日 20:59CVE-2023-43208: NextGen Healthcare Mirth Connect – Remote Code Execution
漏洞标题 CVE-2023-43208: NextGen Healthcare Mirth Connect - Remote Code Execution 漏洞描述 Unauthenticated remote code execution vulnerability in NextGen Healthcare Mirth Connect b...
2023年6月3日 18:32CVE-2010-1354: Joomla! Component VJDEO 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1354: Joomla! Component VJDEO 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the VJDEO (com_vjdeo) component 1.0 and 1.0.1 for Joomla!...
2010年3月20日 00:18CVE-2024-28000: WordPress LiteSpeed Cache – Unauthenticated Privilege Escalation to Admin
漏洞标题 CVE-2024-28000: WordPress LiteSpeed Cache - Unauthenticated Privilege Escalation to Admin 漏洞描述 Incorrect Privilege Assignment vulnerability in LiteSpeed Technologies L...
2024年1月7日 11:19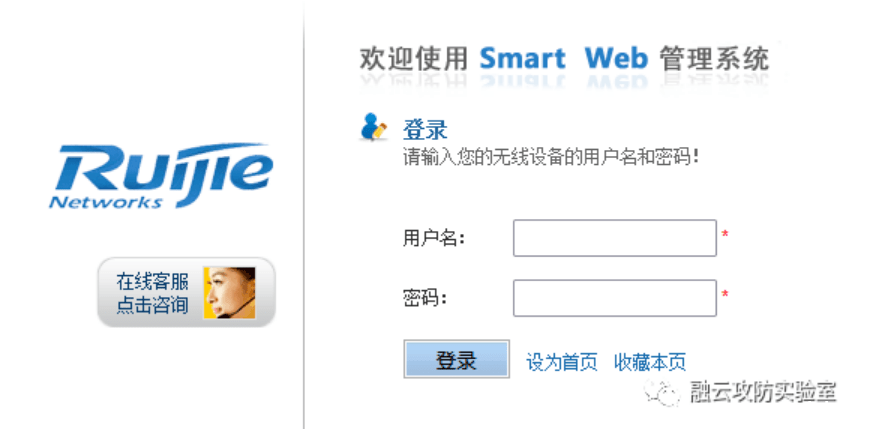
锐捷 Smartweb管理系统 命令注入漏洞(未公布)
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 锐捷 Smartweb管理系统 命令注入漏洞(未公布) 锐捷网络是一家拥有包括交换机、路由器、软件、安全防火墙、无线产品、存储等全系列的...
2026年2月13日 12:53CVE-2018-7700: DedeCMS 5.7SP2 – Cross-Site Request Forgery/Remote Code Execution
漏洞标题 CVE-2018-7700: DedeCMS 5.7SP2 - Cross-Site Request Forgery/Remote Code Execution 漏洞描述 DedeCMS 5.7SP2 is susceptible to cross-site request forgery with a corresponding ...
2018年11月30日 22:25
Manjaro安装CUDA实现教程解析_服务器其它
这篇文章主要介绍了Manjaro安装CUDA实现教程解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 去年年底安装将我的Thinkpad T450的双系...
2023年3月17日 20:29CVE-2023-23489: WordPress Easy Digital Downloads 3.1.0.2/3.1.0.3 – SQL Injection
漏洞标题 CVE-2023-23489: WordPress Easy Digital Downloads 3.1.0.2/3.1.0.3 - SQL Injection 漏洞描述 WordPress Easy Digital Downloads plugin 3.1.0.2 and 3.1.0.3 contains a SQL inject...
2023年9月8日 13:36CVE-2025-53770: Microsoft SharePoint Server – Remote Code Execution (ToolShell)
漏洞标题 CVE-2025-53770: Microsoft SharePoint Server - Remote Code Execution (ToolShell) 漏洞描述 Deserialization of untrusted data in on-premises Microsoft SharePoint Server allow...
2025年7月17日 14:16CVE-2024-36991: Splunk Enterprise – Local File Inclusion
漏洞标题 CVE-2024-36991: Splunk Enterprise - Local File Inclusion 漏洞描述 In Splunk Enterprise on Windows versions below 9.2.2, 9.1.5, and 9.0.10, an attacker could perform a path...
2024年7月29日 15:25CVE-2020-17518: Apache Flink 1.5.1 – Local File Inclusion
漏洞标题 CVE-2020-17518: Apache Flink 1.5.1 - Local File Inclusion 漏洞描述 Apache Flink 1.5.1 is vulnerable to local file inclusion because of a REST handler that allows file uplo...
2020年5月12日 00:48CVE-2022-37122: Carel pCOWeb HVAC BACnet Gateway 2.1.0 – Path Traversal
漏洞标题 CVE-2022-37122: Carel pCOWeb HVAC BACnet Gateway 2.1.0 - Path Traversal 漏洞描述 Carel pCOWeb HVAC BACnet Gateway 2.1.0 contains an unauthenticated arbitrary file disclosu...
2022年1月29日 02:20CVE-2025-31125: Vite Development Server – Path Traversal
漏洞标题 CVE-2025-31125: Vite Development Server - Path Traversal 漏洞描述 Path traversal vulnerability in Vite development server's @fs endpoint allows attackers to access fi...
2025年7月1日 17:11CVE-2022-1916: WordPress Active Products Tables for WooCommerce <1.0.5 - Cross-Site Scripting
漏洞标题 CVE-2022-1916: WordPress Active Products Tables for WooCommerce <1.0.5 - Cross-Site Scripting 漏洞描述 WordPress Active Products Tables for WooCommerce plugin prior to ...
2022年11月19日 23:03
2026年10月28日 11:45
2026年10月27日 11:46
2026年10月26日 11:45
2026年10月25日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

