
最新发布第165页

ConnectWise ScreenConnect CVE-2024-1709身份验证绕过漏洞
漏洞标题 ConnectWise ScreenConnect CVE-2024-1709身份验证绕过漏洞 漏洞描述 ConnectWise ScreenConnect存在身份验证绕过漏洞,此漏洞是由于对url验证不充分导致的,特殊的url可绕过验证并访...
 2024年1月29日 18:01
CVE-2023-0126: SonicWall SMA1000 LFI
漏洞标题 CVE-2023-0126: SonicWall SMA1000 LFI 漏洞描述 Pre-authentication path traversal vulnerability in SMA1000 firmware version 12.4.2, which allows an unauthenticated attacker ...
2023年7月26日 06:26CVE-2024-4434: LearnPress WordPress LMS Plugin <= 4.2.6.5 - SQL Injection
漏洞标题 CVE-2024-4434: LearnPress WordPress LMS Plugin <= 4.2.6.5 - SQL Injection 漏洞描述 The LearnPress WordPress LMS Plugin plugin for WordPress is vulnerable to time-based ...
2024年3月13日 13:48CVE-2023-20864: VMware Aria Operations for Logs – Unauthenticated Remote Code Execution
漏洞标题 CVE-2023-20864: VMware Aria Operations for Logs - Unauthenticated Remote Code Execution 漏洞描述 VMware Aria Operations for Logs contains a deserialization vulnerability. ...
2023年9月12日 22:47CVE-2021-45046-DAST: Apache Log4j2 – Remote Code Injection
漏洞标题 CVE-2021-45046-DAST: Apache Log4j2 - Remote Code Injection 漏洞描述 Apache Log4j2 Thread Context Lookup Pattern is vulnerable to remote code execution in certain non-defau...
2021年1月19日 16:21CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 – Privilege Escalation
漏洞标题 CVE-2025-3605: WordPress Frontend Login and Registration Blocks Plugin 1.0.7 - Privilege Escalation 漏洞描述 Privilege escalation vulnerability exists in the Frontend Logi...
2025年6月25日 14:55CVE-2022-29303: SolarView Compact 6.00 – OS Command Injection
漏洞标题 CVE-2022-29303: SolarView Compact 6.00 - OS Command Injection 漏洞描述 SolarView Compact 6.00 was discovered to contain a command injection vulnerability via conf_mail.php...
2022年2月22日 02:01
Tomcat常见异常及解决方案代码实例_Tomcat
这篇文章主要介绍了Tomcat常见异常及解决方案代码实例,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 公司项目,开发语言为java,中间件...
2024年2月15日 21:44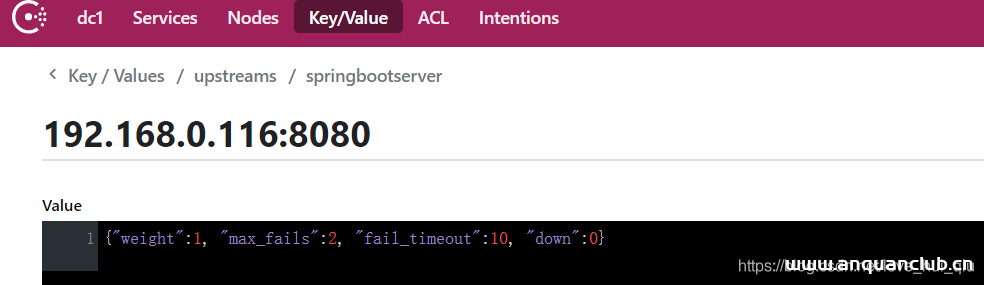
Nginx + consul + upsync 完成动态负载均衡的方法详解_nginx
这篇文章主要介绍了Nginx + consul + upsync 完成动态负载均衡,需要的朋友可以参考下 目录前置知识DNS域名解析过程 外网映射 nginx 核心知识什么是nginx应用场景名词解释Nginx + cons...
2023年3月6日 21:03CData Sync CVE-2024-31851 路径遍历漏洞
漏洞标题 CData Sync CVE-2024-31851 路径遍历漏洞 漏洞描述 CData sync存在路径遍历漏洞,此漏洞是由于/ui/接口对用户的请求验证不当造成的。 PoC代码 暂无
2024年10月20日 03:11CVE-2022-1916: WordPress Active Products Tables for WooCommerce <1.0.5 - Cross-Site Scripting
漏洞标题 CVE-2022-1916: WordPress Active Products Tables for WooCommerce <1.0.5 - Cross-Site Scripting 漏洞描述 WordPress Active Products Tables for WooCommerce plugin prior to ...
2022年12月24日 04:24CVE-2011-5106: WordPress Plugin Flexible Custom Post Type < 0.1.7 - Cross-Site Scripting
漏洞标题 CVE-2011-5106: WordPress Plugin Flexible Custom Post Type < 0.1.7 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in edit-post.php in the Flexible ...
2011年5月2日 17:23
欧盟数据主管命令欧洲刑警组织删除与犯罪无关的个人数据
根据欧盟数据保护监管机构EDPS于1月10日发布的新闻稿,EDPS已于一周前下令欧洲刑警组织删除与犯罪活动没有明确关联的个人的数据,以减少对公民个人权力和自由的侵犯。 此前,欧洲刑警组织...
2022年3月10日 23:39CVE-2023-0527: Online Security Guards Hiring System – Cross-Site Scripting
漏洞标题 CVE-2023-0527: Online Security Guards Hiring System - Cross-Site Scripting 漏洞描述 A vulnerability was found in PHPGurukul Online Security Guards Hiring System 1.0 and cl...
2023年6月11日 03:24CVE-2023-3845: MooDating 1.2 – Cross-Site Scripting
漏洞标题 CVE-2023-3845: MooDating 1.2 - Cross-Site Scripting 漏洞描述 A vulnerability was found in mooSocial mooDating 1.2. It has been rated as problematic. Affected by this issue...
2023年10月14日 12:53
商城的一些逻辑漏洞
之前挖火线的一个私密项目,我参加的时候项目已经开启好几天了,之后在商城的地方挖到了一些漏洞,有几个还是值得分享一下的 一个赠品替换的漏洞 商城里有个满299送赠品的活动,大概是说价格超...
2022年3月10日 23:32
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

