
最新发布第171页

CVE-2024-3848: Mlflow < 2.11.0 - Path Traversal
漏洞标题 CVE-2024-3848: Mlflow < 2.11.0 - Path Traversal 漏洞描述 A path traversal vulnerability exists in mlflow/mlflow version 2.11.0, identified as a bypass for the previousl...
 2024年5月7日 06:13
CVE-2023-21839: Oracle WebLogic Server – Unauthorized Access
漏洞标题 CVE-2023-21839: Oracle WebLogic Server - Unauthorized Access 漏洞描述 Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Su...
2023年7月16日 07:36CVE-2021-40822: Geoserver – Server-Side Request Forgery
漏洞标题 CVE-2021-40822: Geoserver - Server-Side Request Forgery 漏洞描述 GeoServer through 2.18.5 and 2.19.x through 2.19.2 allows server-side request forgery via the option for s...
2021年10月28日 12:05CVE-2023-41265: Qlik Sense Enterprise – HTTP Request Smuggling
漏洞标题 CVE-2023-41265: Qlik Sense Enterprise - HTTP Request Smuggling 漏洞描述 An HTTP Request Tunneling vulnerability found in Qlik Sense Enterprise for Windows for versions May...
2023年2月15日 05:11CirCarLife停车管理系统device-id页面-敏感信息泄漏(CVE-2018-16671)
漏洞标题 CirCarLife停车管理系统device-id页面-敏感信息泄漏(CVE-2018-16671) 漏洞描述 【漏洞对象】Circontrol CirCarLife Scada 【漏洞描述】 Circontrol CirCarLifeScada是西班牙Circontrol...
2018年1月3日 00:49CVE-2021-28854: VICIdial Sensitive Information Disclosure
漏洞标题 CVE-2021-28854: VICIdial Sensitive Information Disclosure 漏洞描述 VICIdial's Web Client is susceptible to information disclosure because it contains many sensitive f...
2021年10月6日 05:27CVE-2018-7193: osTicket < 1.10.2 - Cross-Site Scripting
漏洞标题 CVE-2018-7193: osTicket < 1.10.2 - Cross-Site Scripting 漏洞描述 Cross-site scripting (XSS) vulnerability in /scp/directory.php in Enhancesoft osTicket before 1.10.2 al...
2018年1月19日 20:02
浅析Linux resolv.conf_Linux
这篇文章主要介绍了Linux resolv.conf的相关资料,帮助大家更好的理解和学习Linux,感兴趣的朋友可以了解下 1.简介 resolv.conf是各种操作系统域名系统解析器(DNS Resolver)的配置文件。每当...
2023年6月15日 20:47CVE-2022-23854: AVEVA InTouch Access Anywhere Secure Gateway – Local File Inclusion
漏洞标题 CVE-2022-23854: AVEVA InTouch Access Anywhere Secure Gateway - Local File Inclusion 漏洞描述 AVEVA InTouch Access Anywhere Secure Gateway is vulnerable to local file inclu...
2022年12月19日 11:13CVE-2023-41621: Emlog Pro v2.1.14 – Cross-Site Scripting
漏洞标题 CVE-2023-41621: Emlog Pro v2.1.14 - Cross-Site Scripting 漏洞描述 Cross Site Scripting (XSS) vulnerability in Emlog Pro v2.1.14 via /admin/store.php. PoC代码
2023年11月12日 16:48Docker 清理的常用方法及问题_docker
这篇文章主要介绍了Docker 清理的常用方法及问题,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 如果你使用 docker 进行大规模开发,但是没有清...
2022年8月19日 21:59CVE-2023-25194: Apache Druid Kafka Connect – Remote Code Execution
漏洞标题 CVE-2023-25194: Apache Druid Kafka Connect - Remote Code Execution 漏洞描述 The vulnerability has the potential to enable a remote attacker with authentication to run any ...
2023年10月12日 16:44CVE-2022-28508: MantisBT < 2.25.2 - Cross-Site Scripting
漏洞标题 CVE-2022-28508: MantisBT < 2.25.2 - Cross-Site Scripting 漏洞描述 MantisBT before 2.25.2 contains a cross-site scripting vulnerability in browser_search_plugin.php. The...
2022年11月24日 02:00CVE-2021-27877: Veritas Backup Exec – Broken Authentication
漏洞标题 CVE-2021-27877: Veritas Backup Exec - Broken Authentication 漏洞描述 An issue was discovered in Veritas Backup Exec before 21.2. It supports multiple authentication scheme...
2021年6月29日 15:02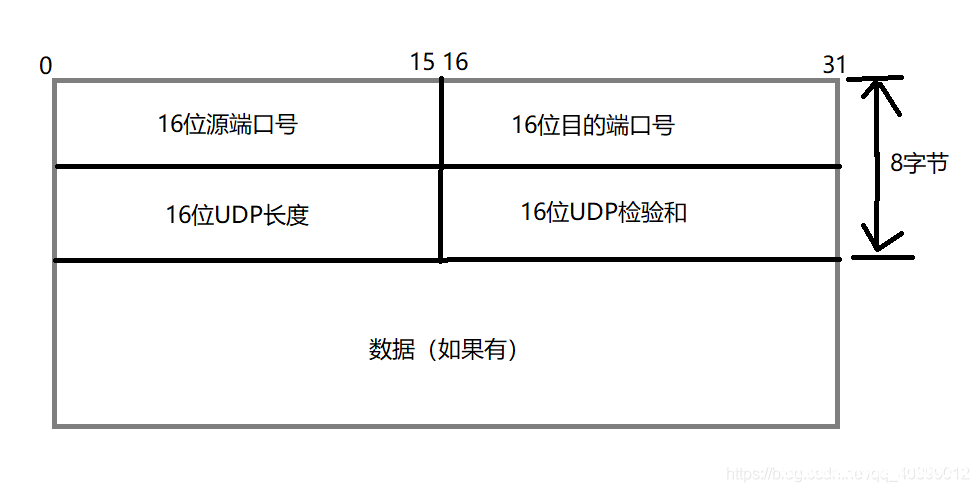
linux对于UDP的学习_Linux
本文将学习linux对于UDP的学习,UDP(用户数据报协议)没有连接的,是面向数据报的,是不可靠,点进来的小伙伴一起来学习吧 目录一、UDP、linux基础介绍二、对于各函数使用1、对于socket函数的...
2022年6月17日 10:00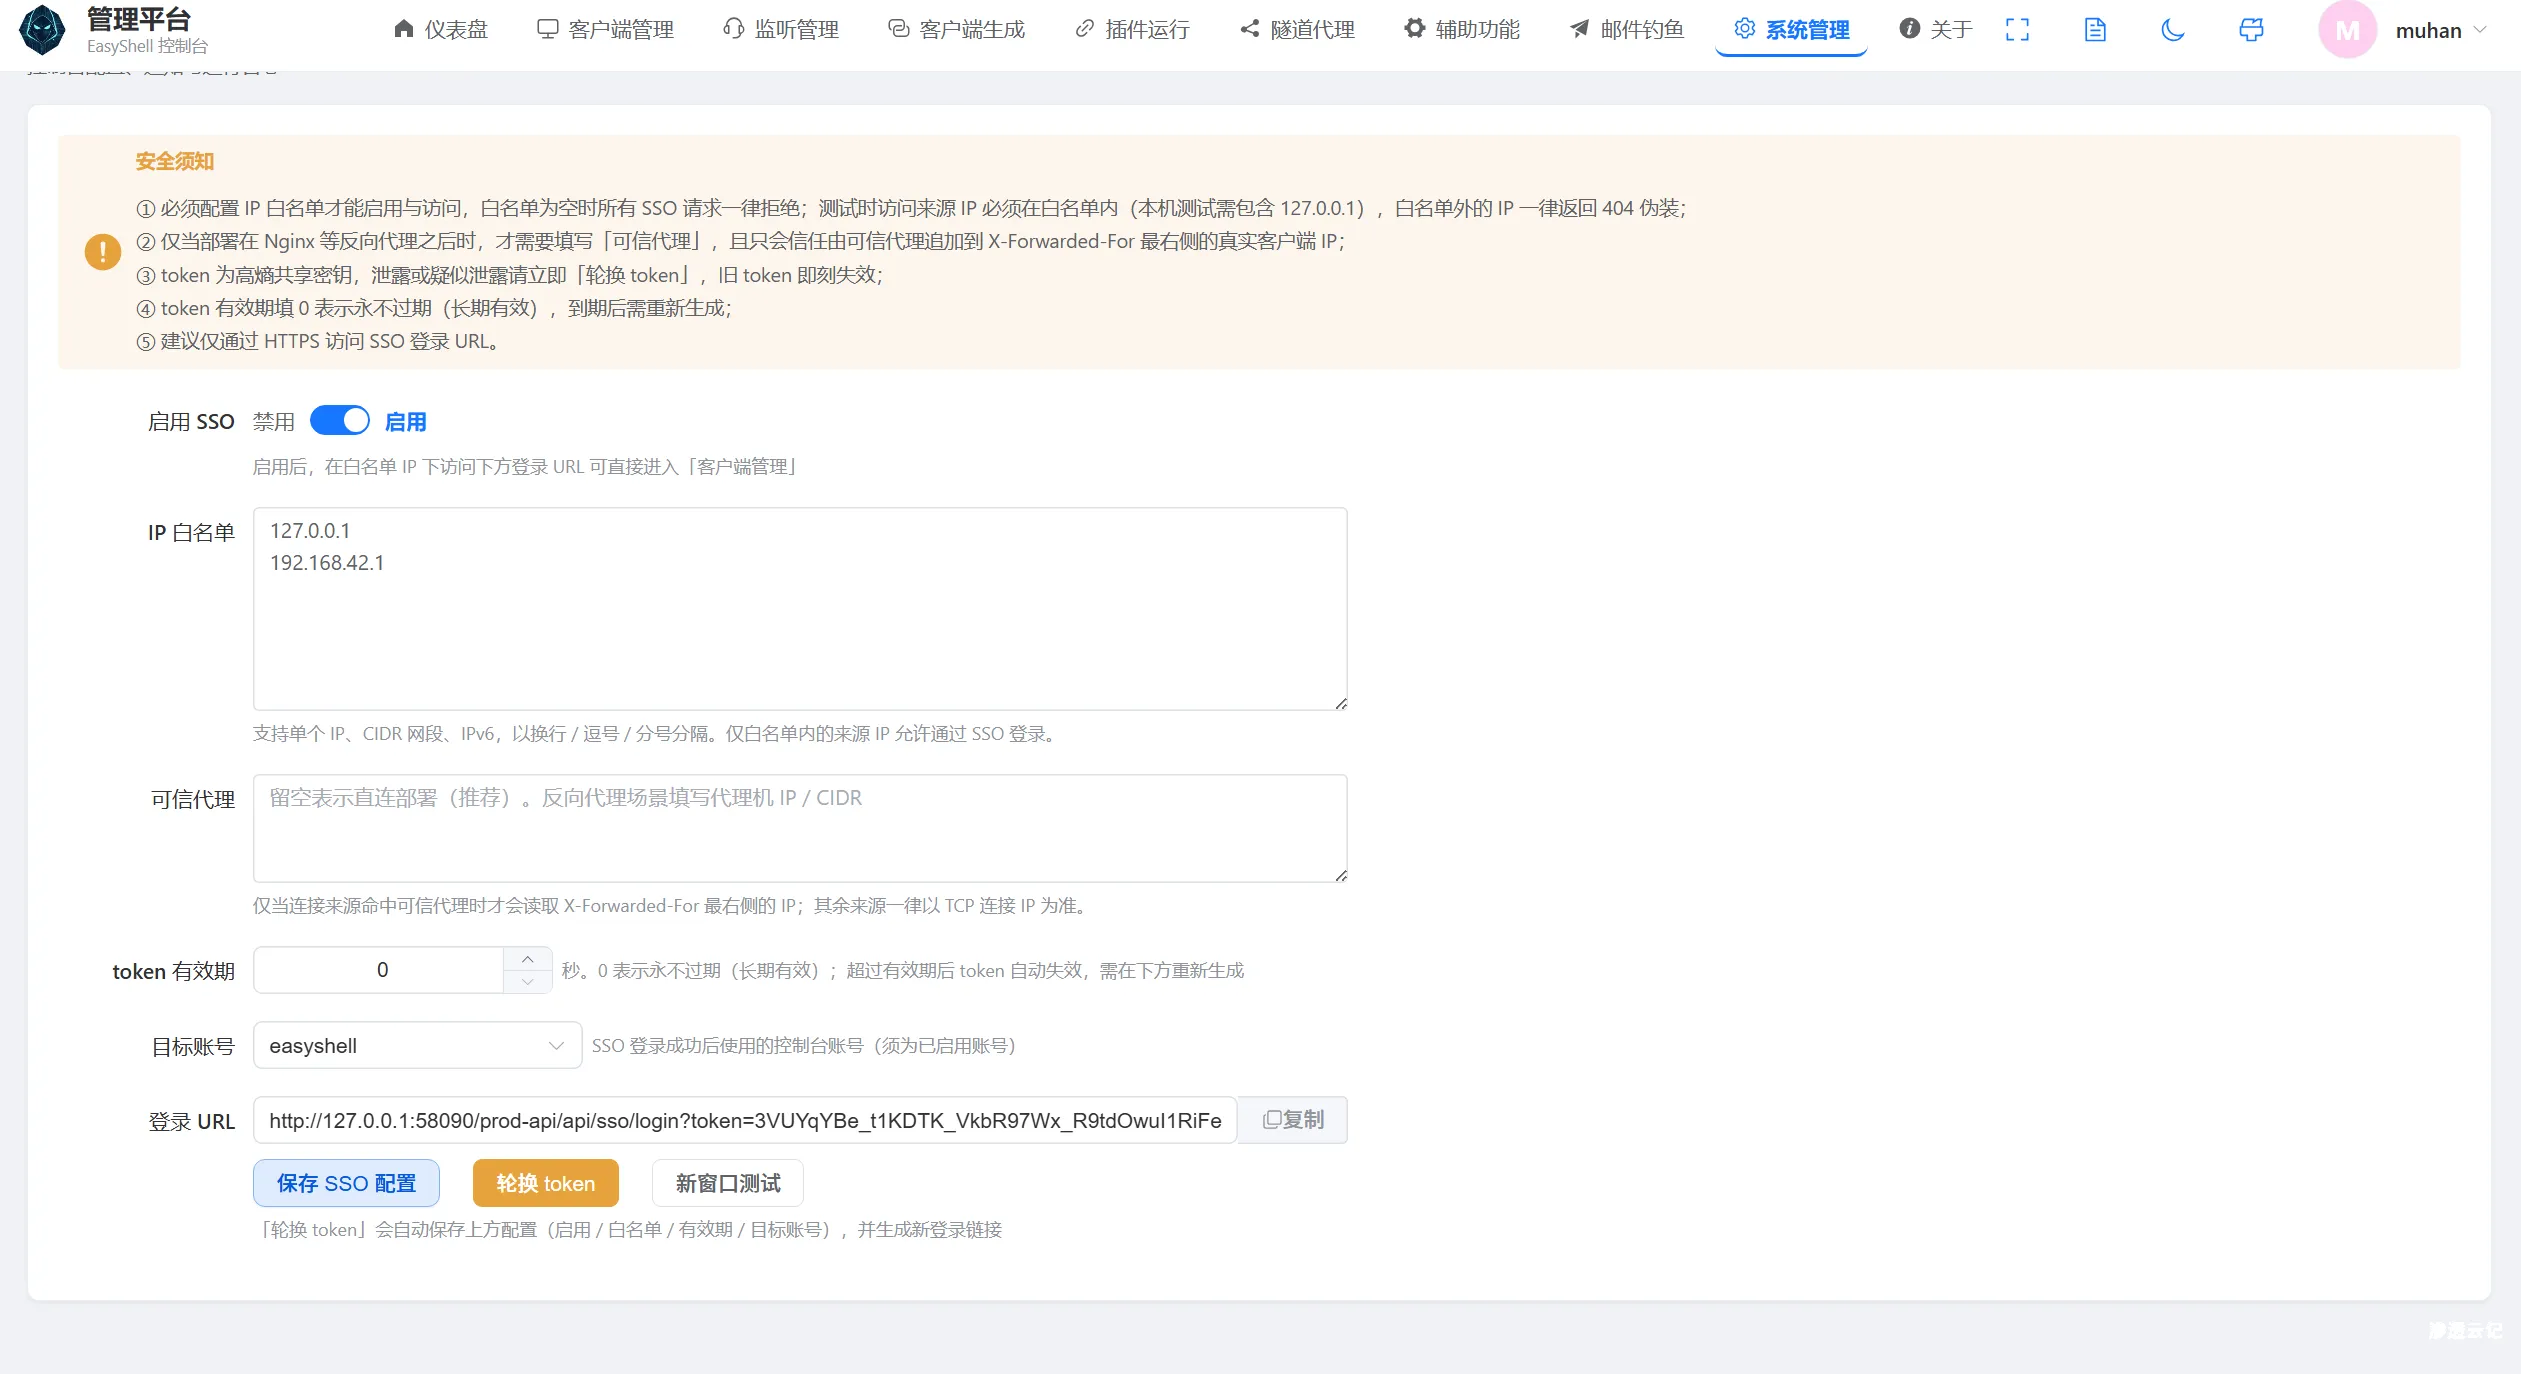
【工具更新】EasyShell v2.8 版本更新,新增stowaway多级网络上线、sso单点登录支持各位师傅将easyshell无缝嵌入各自的redteam工具中
更新说明 感谢各位师傅们的热心测试,发现了诸多bug,目前已经修复的有: 修复前端界面刷新异常与卡顿的bug, 修复隧道代理流量特征被捕获的情况, 修复ws协议无法上线的bug, 新增系统sso本地单点...

 2026年8月29日 19:12

2026年11月5日 11:45
2026年11月4日 11:45
2026年11月3日 11:46
2026年11月2日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

