
最新发布第187页

CVE-2021-24278: WordPress Contact Form 7 <2.3.4 - Arbitrary Nonce Generation
漏洞标题 CVE-2021-24278: WordPress Contact Form 7 <2.3.4 - Arbitrary Nonce Generation 漏洞描述 WordPress Contact Form 7 before version 2.3.4 allows unauthenticated users to use ...
 2021年5月10日 07:12
CVE-2021-22873: Revive Adserver <5.1.0 - Open Redirect
漏洞标题 CVE-2021-22873: Revive Adserver <5.1.0 - Open Redirect 漏洞描述 Revive Adserver before 5.1.0 contains an open redirect vulnerability via the dest, oadest, and ct0 param...
2021年8月4日 20:57
[极客大挑战 2019]BabySQL – buu刷题笔记
自从前几次网站被日,我对我的网站做了严格的过滤,你们这些黑客死心吧!!! 尝试登录 admin'# ,登录成功,但相较于以前做的那个sql题,这个flag铁定错的 Your password is 'fd7055ec3060d96f...

 2022年4月15日 15:17
CVE-2024-29269: Telesquare TLR-2005KSH – Remote Command Execution
漏洞标题 CVE-2024-29269: Telesquare TLR-2005KSH - Remote Command Execution 漏洞描述 Telesquare Tlr-2005Ksh is a Sk Telecom Lte router from South Korea's Telesquare company.Tel...
2024年7月1日 04:22CVE-2023-3848: MooDating 1.2 – Cross-site scripting
漏洞标题 CVE-2023-3848: MooDating 1.2 - Cross-site scripting 漏洞描述 A vulnerability, which was classified as problematic, has been found in mooSocial mooDating 1.2. This issue af...
2023年2月10日 12:51CVE-2021-37704: phpfastcache – phpinfo Resource Exposure
漏洞标题 CVE-2021-37704: phpfastcache - phpinfo Resource Exposure 漏洞描述 phpinfo() is susceptible to resource exposure in unprotected composer vendor folders via phpfastcache/php...
2021年11月6日 19:27CVE-2019-25152: Abandoned Cart Lite for WooCommerce < 5.2.0 - Cross-Site Scripting
漏洞标题 CVE-2019-25152: Abandoned Cart Lite for WooCommerce < 5.2.0 - Cross-Site Scripting 漏洞描述 The Abandoned Cart Lite for WooCommerce and Abandoned Cart Pro for WooCommer...
2019年7月10日 12:13CVE-2023-40751: PHPJabbers Fundraising Script v1.0 – Cross-Site Scripting
漏洞标题 CVE-2023-40751: PHPJabbers Fundraising Script v1.0 - Cross-Site Scripting 漏洞描述 PHPJabbers Fundraising Script v1.0 is vulnerable to Cross Site Scripting (XSS) via the &...
2023年7月24日 11:40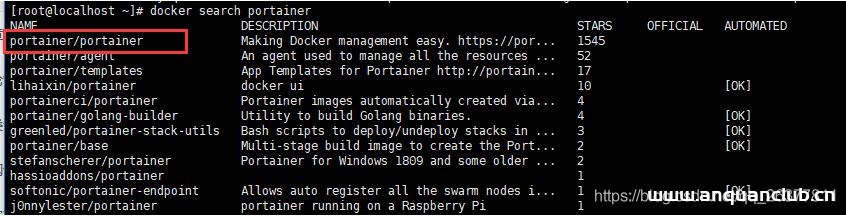
docker可视化工具Portainer部署并汉化的操作_docker
这篇文章主要介绍了docker可视化工具Portainer部署并汉化的操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 #docker search #docker pull portainer 1.拉取镜像后下载汉...
2022年7月9日 21:16CVE-2021-22005: VMware vCenter Server – Arbitrary File Upload
漏洞标题 CVE-2021-22005: VMware vCenter Server - Arbitrary File Upload 漏洞描述 VMware vCenter Server contains an arbitrary file upload vulnerability in the Analytics service. A ma...
2021年6月19日 04:51CVE-2023-6360: WordPress My Calendar <3.4.22 - SQL Injection
漏洞标题 CVE-2023-6360: WordPress My Calendar <3.4.22 - SQL Injection 漏洞描述 WordPress My Calendar plugin versions before 3.4.22 are vulnerable to an unauthenticated SQL injec...
2023年8月11日 23:12CVE-2023-39109: rConfig 3.9.4 – Server-Side Request Forgery
漏洞标题 CVE-2023-39109: rConfig 3.9.4 - Server-Side Request Forgery 漏洞描述 rconfig v3.9.4 was discovered to contain a Server-Side Request Forgery (SSRF) via the path_a parameter...
2023年4月2日 18:00Apache OFBiz webtools/control/ProgramExport 远程代码执行漏洞(CVE-2023-51467)
漏洞标题 Apache OFBiz webtools/control/ProgramExport 远程代码执行漏洞(CVE-2023-51467) 漏洞描述 Apache OFBiz 在 webtools/control/ProgramExport存在代码执行漏洞,攻击者可通过该漏洞...
2023年2月11日 03:17CVE-2023-37999: HT Mega – Absolute Addons for Elementor <= 2.2.0 - Missing Authorization to Privilege Escalation
漏洞标题 CVE-2023-37999: HT Mega – Absolute Addons for Elementor <= 2.2.0 - Missing Authorization to Privilege Escalation 漏洞描述 The HT Mega plugin for WordPress is vulnerabl...
2023年6月9日 02:32CVE-2023-4596: WordPress Plugin Forminator 1.24.6 – Arbitrary File Upload
漏洞标题 CVE-2023-4596: WordPress Plugin Forminator 1.24.6 - Arbitrary File Upload 漏洞描述 The Forminator plugin for WordPress is vulnerable to arbitrary file uploads due to file ...
2023年1月5日 03:21CVE-2017-17731: DedeCMS 5.7 – SQL Injection
漏洞标题 CVE-2017-17731: DedeCMS 5.7 - SQL Injection 漏洞描述 DedeCMS through 5.7 has SQL Injection via the $_FILES superglobal to plus/recommend.php. PoC代码
2017年12月30日 05:36
2026年9月24日 11:46
2026年9月23日 11:46
2026年9月22日 11:45
2026年9月21日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

