
最新发布第196页

CVE-2021-24145: WordPress Modern Events Calendar Lite <5.16.5 - Authenticated Arbitrary File Upload
漏洞标题 CVE-2021-24145: WordPress Modern Events Calendar Lite <5.16.5 - Authenticated Arbitrary File Upload 漏洞描述 WordPress Modern Events Calendar Lite plugin before 5.16.5 ...
 2021年1月31日 06:19
CVE-2023-27847: PrestaShop xipblog – SQL Injection
漏洞标题 CVE-2023-27847: PrestaShop xipblog - SQL Injection 漏洞描述 In the blog module (xipblog), an anonymous user can perform SQL injection. Even though the module has been patc...
2023年4月4日 13:46CVE-2018-9205: Drupal avatar_uploader v7.x-1.0-beta8 – Local File Inclusion
漏洞标题 CVE-2018-9205: Drupal avatar_uploader v7.x-1.0-beta8 - Local File Inclusion 漏洞描述 In avatar_uploader v7.x-1.0-beta8 the view.php program doesn't restrict file path...
2018年10月7日 19:02Casdoor 1.13.0-SQL注入(CVE-2022-24124)
漏洞标题 Casdoor 1.13.0-SQL注入(CVE-2022-24124) 漏洞描述 Casdoor 是一个基于 OAuth 2.0 / OIDC 的 UI 优先集中认证 / 单点登录 (SSO) 平台。该平台存在sql注入漏洞 PoC代码 暂无
2022年6月15日 06:42CVE-2007-4504: Joomla! RSfiles <=1.0.2 - Local File Inclusion
漏洞标题 CVE-2007-4504: Joomla! RSfiles <=1.0.2 - Local File Inclusion 漏洞描述 Joomla! RSfiles 1.0.2 and earlier is susceptible to local file inclusion in index.php in the RSfi...
2007年11月18日 08:21CVE-2014-2383: Dompdf < v0.6.0 - Local File Inclusion
漏洞标题 CVE-2014-2383: Dompdf < v0.6.0 - Local File Inclusion 漏洞描述 A vulnerability in dompdf.php in dompdf before 0.6.1, when DOMPDF_ENABLE_PHP is enabled, allows context-d...
2014年8月31日 20:49Atlassian Jira 用户枚举(CVE-2019-3403)
漏洞标题 Atlassian Jira 用户枚举(CVE-2019-3403) 漏洞描述 8.1.1之前的Jira通过searchOwnerUserName参数中的ConfigurePortalPages.jspa资源包含跨站点脚本漏洞。 PoC代码 暂无
2019年7月24日 08:27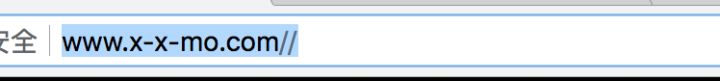
nginx配置域名访问时域名后出现两个斜杠//的解决方法_nginx
最近这两天重新写了一下我的个人网站,在阿里云新买了一台服务器,配置好以后出现了一个问题,就是输入域名后域名地址会自动在后面追加两个斜杆,需要的朋友可以参考下 最近这两天重新写了一下我...
2023年10月9日 20:03Atlassian Confluence CVE-2023-22527 远程命令执行漏洞
漏洞标题 Atlassian Confluence CVE-2023-22527 远程命令执行漏洞 漏洞描述 Atlassian Confluence存在远程命令执行漏洞,此漏洞是对用户的数据缺乏校验导致的。 PoC代码 暂无
2023年10月14日 01:25CVE-2022-1597: WordPress WPQA <5.4 - Cross-Site Scripting
漏洞标题 CVE-2022-1597: WordPress WPQA <5.4 - Cross-Site Scripting 漏洞描述 WordPress WPQA plugin prior to 5.4 contains a reflected cross-site scripting vulnerability. It does n...
2022年2月20日 11:44CVE-2022-46443: Bangresto – SQL Injection
漏洞标题 CVE-2022-46443: Bangresto - SQL Injection 漏洞描述 Bangresto 1.0 is vulnberable to SQL Injection via the itemqty%5B%5D parameter. PoC代码
2022年3月8日 06:30CVE-2021-28149: Hongdian H8922 3.0.5 Devices – Local File Inclusion
漏洞标题 CVE-2021-28149: Hongdian H8922 3.0.5 Devices - Local File Inclusion 漏洞描述 Hongdian H8922 3.0.5 devices are vulnerable to local file inclusion. The /log_download.cgi log...
2021年7月6日 11:29CVE-2024-10914: D-Link NAS – Command Injection via Name Parameter
漏洞标题 CVE-2024-10914: D-Link NAS - Command Injection via Name Parameter 漏洞描述 A vulnerability was found in D-Link DNS-320, DNS-320LW, DNS-325 and DNS-340L up to 20241028. It ...
2024年5月27日 12:30CVE-2021-44515: Zoho ManageEngine Desktop Central – Remote Code Execution
漏洞标题 CVE-2021-44515: Zoho ManageEngine Desktop Central - Remote Code Execution 漏洞描述 Zoho ManageEngine Desktop Central contains an authentication bypass vulnerability that c...
2021年10月25日 18:31CVE-2023-27179: GDidees CMS v3.9.1 – Arbitrary File Download
漏洞标题 CVE-2023-27179: GDidees CMS v3.9.1 - Arbitrary File Download 漏洞描述 GDidees CMS v3.9.1 and lower was discovered to contain an arbitrary file download vulenrability via t...
2023年11月10日 13:34
还在让浏览器保存密码?小心遭恶意软件窃取
12月28日,韩国最大杀毒软件公司安博士Ahnlab发布了一份研究报告,警告有一款名为RedLine Stealer的恶意软件正在窃取Web浏览器存储的密码。 Ahnlab是韩国首家从事开发杀毒软件的企业,于19...
2022年3月10日 23:34
2026年9月29日 11:45
2026年9月28日 11:45
2026年9月27日 11:45
2026年9月26日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

