
最新发布第210页

CVE-2024-43441: Apache HugeGraph-Server <1.5.0 - Authentication Bypass
漏洞标题 CVE-2024-43441: Apache HugeGraph-Server <1.5.0 - Authentication Bypass 漏洞描述 Apache HugeGraph-Server versions prior to 1.5.0 contain an authentication bypass vulnera...
 2024年10月2日 04:27
CVE-2024-10571: Chartify – WordPress Chart Plugin < 2.9.6 - Local File Inclusion
漏洞标题 CVE-2024-10571: Chartify – WordPress Chart Plugin < 2.9.6 - Local File Inclusion 漏洞描述 The Chartify – WordPress Chart Plugin plugin for WordPress is vulnerable to ...
2024年1月27日 08:58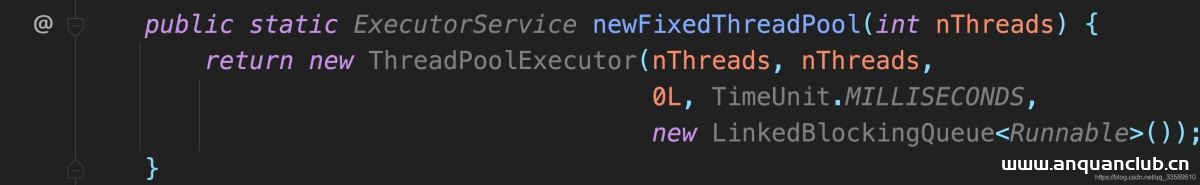
Tomcat修正JDK原生线程池bug的实现原理_Tomcat
这篇文章主要介绍了Tomcat是如何修正JDK原生线程池bug的,本文通过实例代码给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 为提高处理能力和并发度,We...
2022年6月18日 20:46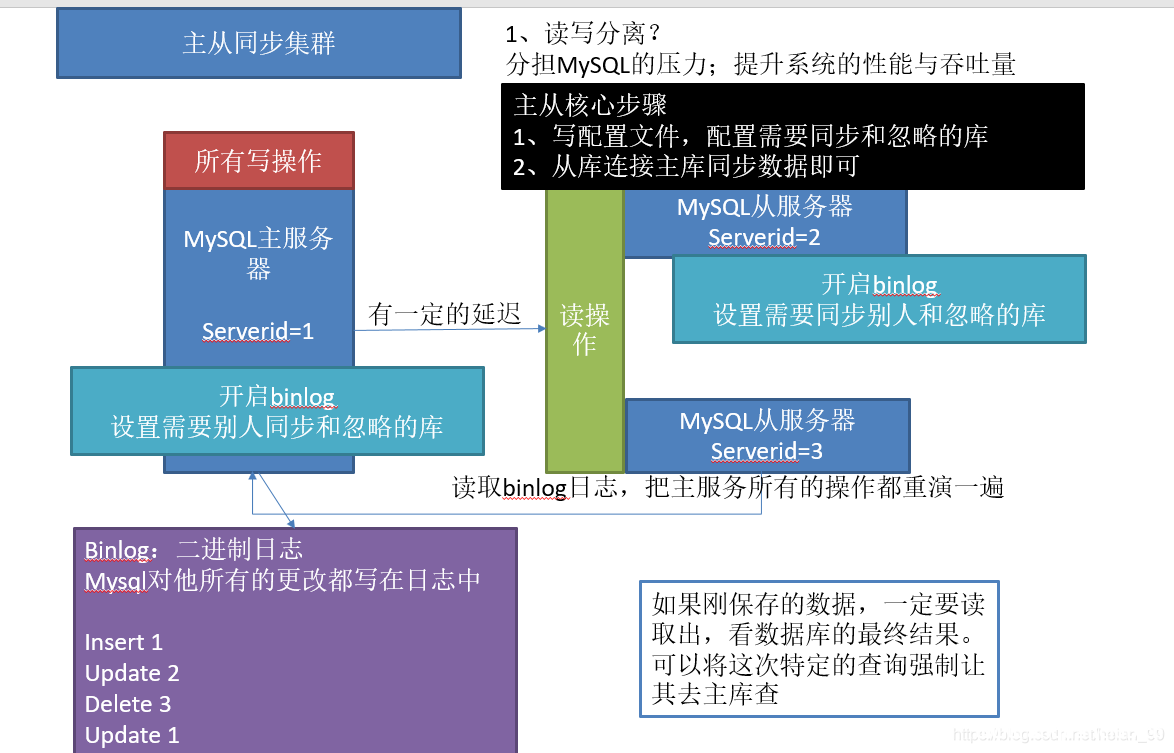
docker实现mysql主从复制的示例代码_docker
Docker它不香吗?即省去了安装Mysql所需要的步骤,有多个容器之间相互资源独立,IP互不冲突,具有一定的参考价值,感兴趣的可以了解一下 目录一、概述1、原理2、实现三、创建Slave实例四、主从配...
2022年6月15日 22:42CVE-2024-3673: Web Directory Free < 1.7.3 - Local File Inclusion
漏洞标题 CVE-2024-3673: Web Directory Free < 1.7.3 - Local File Inclusion 漏洞描述 The Web Directory Free WordPress plugin before 1.7.3 does not validate a parameter before usin...
2024年9月8日 04:35CVE-2010-1478: Joomla! Component Jfeedback 1.2 – Local File Inclusion
漏洞标题 CVE-2010-1478: Joomla! Component Jfeedback 1.2 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Ternaria Informatica Jfeedback! (com_jfeedback) c...
2010年10月19日 17:58
浅谈红队中的提权(连载第四篇)
受限于个人水平,文中难免会出现错误或者描述不当的地方,还望各位在评论处指出,望谅解。 0x00 前言 续接上文浅谈红队中的权限维持(连载第三篇) 当拿下目标后,难免会遇到拿下的权限只是一个...
2022年3月10日 23:39CVE-2022-4059: Cryptocurrency Widgets Pack < 2.0 - SQL Injection
漏洞标题 CVE-2022-4059: Cryptocurrency Widgets Pack < 2.0 - SQL Injection 漏洞描述 The plugin does not sanitise and escape some parameter before using it in a SQL statement via ...
2022年8月11日 04:35CVE-2024-51228: TOTOLINK CX-A3002RU – Remote Code Execution
漏洞标题 CVE-2024-51228: TOTOLINK CX-A3002RU - Remote Code Execution 漏洞描述 An issue in TOTOLINK-CX-A3002RU V1.0.4-B20171106.1512 and TOTOLINK-CX-N150RT V2.1.6-B20171121.1002 and...
2024年1月8日 12:32CVE-2021-30461: VoipMonitor <24.61 - Remote Code Execution
漏洞标题 CVE-2021-30461: VoipMonitor <24.61 - Remote Code Execution 漏洞描述 VoipMonitor prior to 24.61 is susceptible to remote code execution vulnerabilities because of its us...
2021年1月14日 21:51Adobe Commerce/Magento SessionReaper /customer/address_file/upload 文件上传漏洞(CVE-2025-54236)
漏洞标题 Adobe Commerce/Magento SessionReaper /customer/address_file/upload 文件上传漏洞(CVE-2025-54236) 漏洞描述 Adobe Commerce是一款由Adobe公司开发的电子商务平台,广泛应用于全...
2025年6月17日 09:39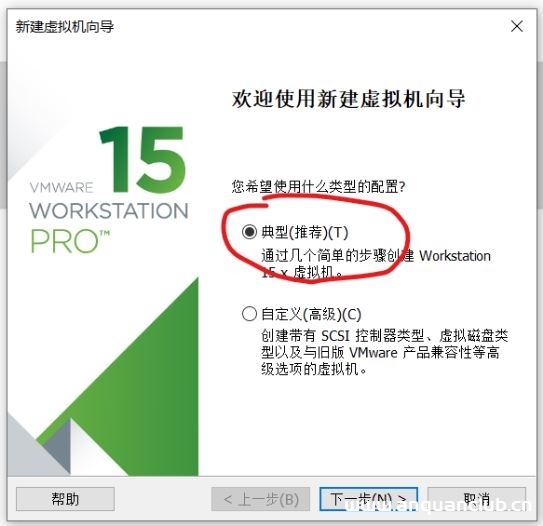
VMwarea虚拟机安装win7操作系统的教程图解_VMware
这篇文章主要介绍了VMwarea虚拟机安装win7操作系统的教程,本文图文并茂给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 VMwarea的安装过程就不演示了,主要看看如何装入wi...
2024年6月26日 20:09CVE-2022-4059: Cryptocurrency Widgets Pack < 2.0 - SQL Injection
漏洞标题 CVE-2022-4059: Cryptocurrency Widgets Pack < 2.0 - SQL Injection 漏洞描述 The plugin does not sanitise and escape some parameter before using it in a SQL statement via ...
2022年8月29日 13:27Ametys CMS CVE-2022-26159信息泄露漏洞
漏洞标题 Ametys CMS CVE-2022-26159信息泄露漏洞 漏洞描述 Ametys CMS 存在信息泄露漏洞,此漏洞是缺乏校验导致的。 PoC代码 暂无
2022年9月18日 23:37CVE-2025-2746: Kentico Xperience 13 CMS – Staging Service Authentication Bypass (WT-2025-0011)
漏洞标题 CVE-2025-2746: Kentico Xperience 13 CMS - Staging Service Authentication Bypass (WT-2025-0011) 漏洞描述 Before Kentico Xperience 13 Hotfix 173, this vulnerability can be e...
2025年5月11日 07:25CVE-2025-11833: Post SMTP <= 3.6.0 - Email Log Disclosure
漏洞标题 CVE-2025-11833: Post SMTP <= 3.6.0 - Email Log Disclosure 漏洞描述 Post SMTP WordPress plugin <= 3.6.0 contains an unauthorized data access vulnerability caused by m...
2025年8月16日 04:19
2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
2026年10月12日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

