
最新发布第212页
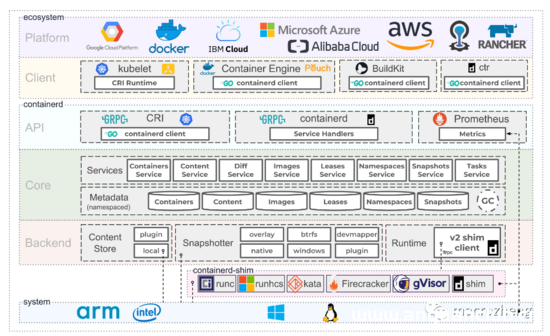
再见 Docker如何5分钟转型 containerd_docker
这篇文章主要介绍了再见 Docker如何5分钟转型 containerd,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 Docker作为非常流行的容器技术,之前经...
 2022年8月31日 21:08
空白页面第二种利用
这个页面也是src的,简单打个码,刚开始访问是这个样子滴 我记得我上一篇文章说了xray联动,那这篇就不说了,简单的探测一下,比如nmap,发现这个只有22跟80开放 那没办法,跑一手目录看看,看...
2022年3月10日 23:30
业界首个!腾讯云原生一站式微服务管理框架Femas开源
3月16日,腾讯云宣布正式开源业界首个云原生标准的一站式微服务管理框架—— Femas 。作为腾讯云微服务平台 TSF 的开源版本,Femas将在云原生组件“北极星”(PolarisMesh)子项目下对外开源,...
2022年3月17日 08:07
Adobe Coldfusion绕过身份验证(CVE-2023-26347)
漏洞标题 Adobe Coldfusion绕过身份验证(CVE-2023-26347) 漏洞描述 Adobe ColdFusion 版本2023.5 (及更早版本)和2021.11(及更早版本)存在不正确的访问控制漏洞,可能导致安全功能被绕过。未经身...
2023年1月12日 06:02CVE-2021-24997: WordPress Guppy <=1.1 - Information Disclosure
漏洞标题 CVE-2021-24997: WordPress Guppy <=1.1 - Information Disclosure 漏洞描述 WordPress Guppy plugin through 1.1 is susceptible to an API disclosure vulnerability. This can a...
2021年7月6日 05:14CVE-2010-1429: Red Hat JBoss Enterprise Application Platform – Sensitive Information Disclosure
漏洞标题 CVE-2010-1429: Red Hat JBoss Enterprise Application Platform - Sensitive Information Disclosure 漏洞描述 Red Hat JBoss Enterprise Application Platform 4.2 before 4.2.0.CP0...
2010年6月15日 02:47CVE-2018-1000600: Jenkins GitHub Plugin <=1.29.1 - Server-Side Request Forgery
漏洞标题 CVE-2018-1000600: Jenkins GitHub Plugin <=1.29.1 - Server-Side Request Forgery 漏洞描述 Jenkins GitHub Plugin 1.29.1 and earlier is susceptible to server-side request f...
2018年4月27日 08:25CVE-2025-32969: XWiki REST API Query – SQL Injection
漏洞标题 CVE-2025-32969: XWiki REST API Query - SQL Injection 漏洞描述 A SQL injection vulnerability exists in XWiki's REST API query endpoint. An unauthenticated attacker can...
2025年6月6日 18:58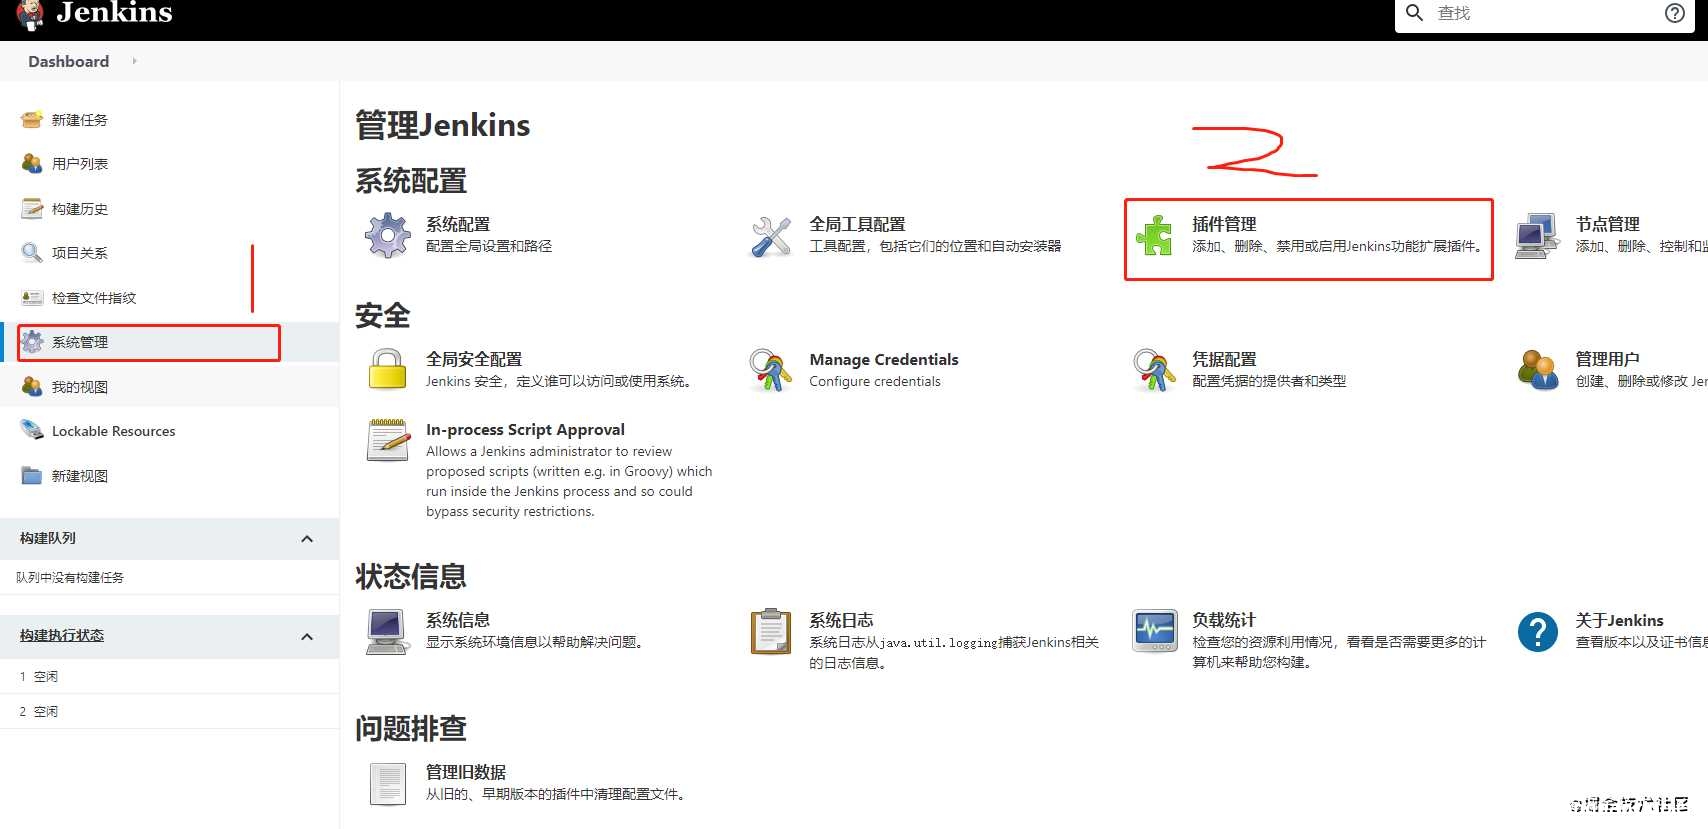
jenkins+gitlab+nginx部署前端应用实现_docker
在日常开发中,往往可能同时多个项目并行进行开发,本文介绍了jenkins+gitlab+nginx部署前端应用实现,感兴趣的可以了解一下 目录相关依赖安装 docker docker安装jenkinsdocker 安装 nginx 小结...
2022年6月15日 09:45CVE-2023-32243: WordPress Elementor Lite 5.7.1 – Arbitrary Password Reset
漏洞标题 CVE-2023-32243: WordPress Elementor Lite 5.7.1 - Arbitrary Password Reset 漏洞描述 Improper Authentication vulnerability in WPDeveloper Essential Addons for Elementor allo...
2023年4月19日 12:13CVE-2023-43323: mooSocial 3.1.8 – External Service Interaction
漏洞标题 CVE-2023-43323: mooSocial 3.1.8 - External Service Interaction 漏洞描述 mooSocial 3.1.8 is vulnerable to external service interaction via multiple parameters in the post f...
2023年2月16日 10:48CVE-2022-1768: WordPress RSVPMaker <=9.3.2 - SQL Injection
漏洞标题 CVE-2022-1768: WordPress RSVPMaker <=9.3.2 - SQL Injection 漏洞描述 WordPress RSVPMaker plugin through 9.3.2 contains a SQL injection vulnerability due to insufficient ...
2022年11月30日 04:42Belkin N150 路径遍历(CVE-2014-2962)
漏洞标题 Belkin N150 路径遍历(CVE-2014-2962) 漏洞描述 固件版本低于1.00.08的Belkin N150 F9K1009 v1路由器上的webproccgi模块中存在路径遍历漏洞,远程攻击者可借助getpage参数中的完整路径...
2014年6月9日 07:59CVE-2019-25213: WordPress Advanced Access Manager – Path Traversal
漏洞标题 CVE-2019-25213: WordPress Advanced Access Manager - Path Traversal 漏洞描述 The Advanced Access Manager plugin for WordPress is vulnerable to Unauthenticated Arbitrary Fil...
2019年5月9日 23:54CVE-2024-13161: Ivanti EPM – Credential Coercion Vulnerability in GetHashForSingleFile
漏洞标题 CVE-2024-13161: Ivanti EPM - Credential Coercion Vulnerability in GetHashForSingleFile 漏洞描述 A vulnerability in Ivanti Endpoint Manager (EPM) allows an unauthenticated ...
2024年8月30日 21:12
那些年我们一起学XSS
那些年我们一起学XSS 下载地址:http://i0x0fy4ibf.feishu.cn/file/boxcneWUeidPmbE15ZSYtydSSOg
2022年3月10日 23:37
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

