
最新发布第222页

CVE-2024-7714: AI Assistant with ChatGPT by AYS <= 2.0.9 - Unauthenticated AJAX Calls
漏洞标题 CVE-2024-7714: AI Assistant with ChatGPT by AYS <= 2.0.9 - Unauthenticated AJAX Calls 漏洞描述 The plugin lacks sufficient access controls allowing an unauthenticated u...
 2024年8月1日 05:16
CVE-2010-1314: Joomla! Component Highslide 1.5 – Local File Inclusion
漏洞标题 CVE-2010-1314: Joomla! Component Highslide 1.5 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Highslide JS (com_hsconfig) component 1.5 and 2.0...
2010年12月3日 16:24CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload
漏洞标题 CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload 漏洞描述 The WooCommerce Checkout Field Manager WordPress plugin before 18.0 does not v...
2022年1月30日 23:23CVE-2020-27361: Akkadian Provisioning Manager 4.50.02 – Sensitive Information Disclosure
漏洞标题 CVE-2020-27361: Akkadian Provisioning Manager 4.50.02 - Sensitive Information Disclosure 漏洞描述 Akkadian Provisioning Manager 4.50.02 could allow viewing of sensitive in...
2020年11月8日 15:45CVE-2021-32618: Python Flask-Security – Open Redirect
漏洞标题 CVE-2021-32618: Python Flask-Security - Open Redirect 漏洞描述 Python Flask-Security contains an open redirect vulnerability. Existing code validates that the URL specifie...
2021年9月6日 06:23
安全小天地携手渗透云记祝大家龙年快乐
您有一份新年红包请注意查收(✪ω✪) 龙游天下,锦绣前程,安全小天地祝您龙年一帆风顺,神采飞扬,收获满满。 欢迎大家关注公众号:渗透云记 回复关键词领取支付宝口令红包:龙年吉祥 先到先得,数...

 2024年2月9日 20:53
CVE-2022-1013: WordPress Personal Dictionary <1.3.4 - Blind SQL Injection
漏洞标题 CVE-2022-1013: WordPress Personal Dictionary <1.3.4 - Blind SQL Injection 漏洞描述 WordPress Personal Dictionary plugin before 1.3.4 contains a blind SQL injection vuln...
2022年8月17日 03:35CVE-2023-25346: ChurchCRM 4.5.3 – Cross-Site Scripting
漏洞标题 CVE-2023-25346: ChurchCRM 4.5.3 - Cross-Site Scripting 漏洞描述 A reflected cross-site scripting (XSS) vulnerability in ChurchCRM 4.5.3 allows remote attackers to inject a...
2023年3月12日 23:02CVE-2024-5057: WordPress Easy Digital Downloads <= 3.2.12 - SQL Injection
漏洞标题 CVE-2024-5057: WordPress Easy Digital Downloads <= 3.2.12 - SQL Injection 漏洞描述 Improper Neutralization of Special Elements used in an SQL Command ('SQL Injecti...
2024年2月20日 16:02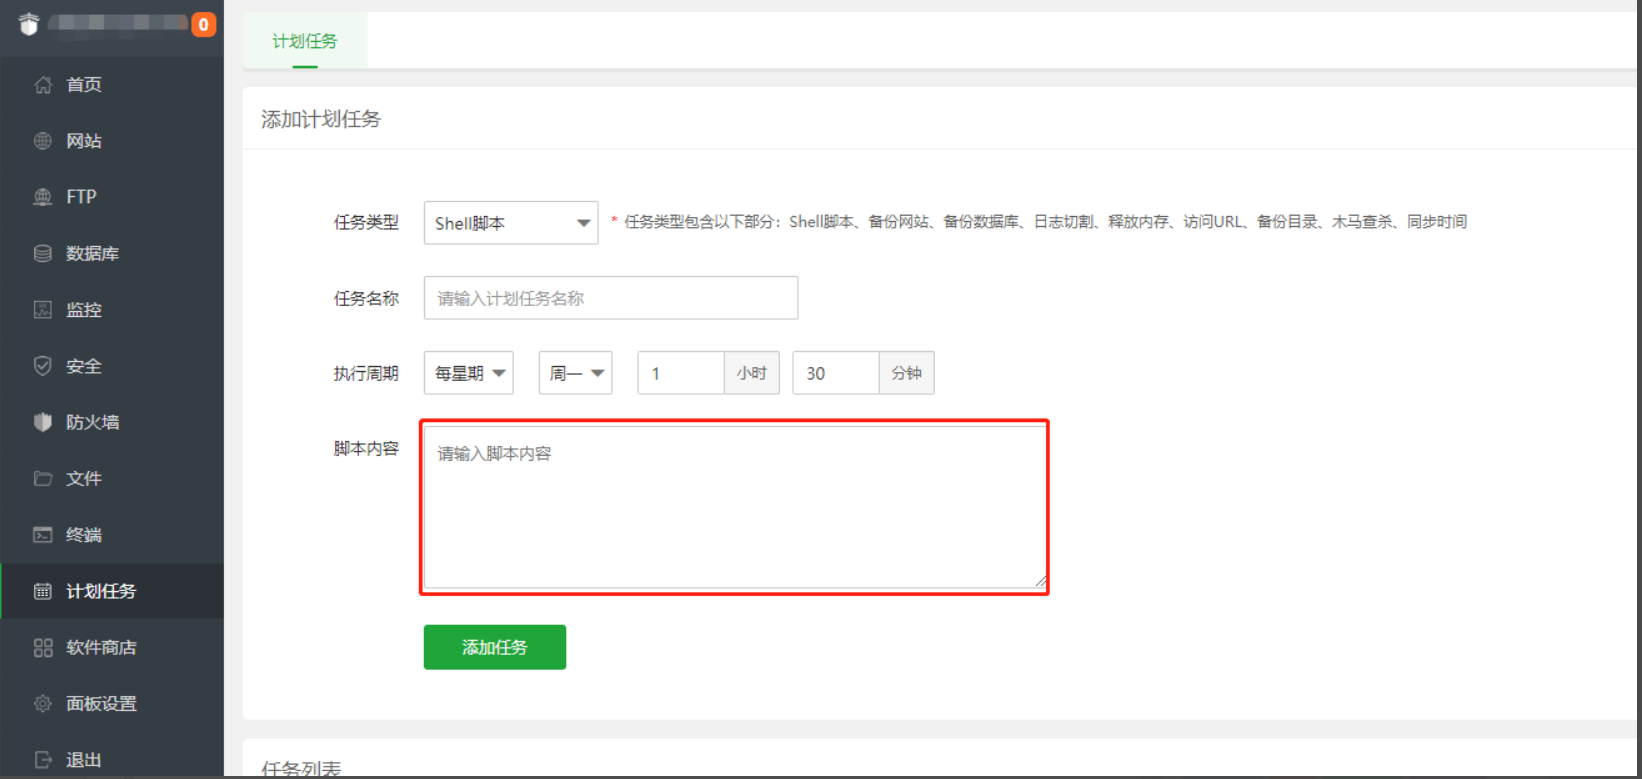
【服务器运维】如何定时清理服务器内的临时图片/日志
问题场景 服务器零时图片太多,怎么定时清理呢 解决方案 命令行 我们可以用一行命令就解决 find /www/wwwroot/qbl -mtime +7 -name '*.png' -exec rm -rf {} \; find后面跟要查找的目录,/www/w...
2023年1月13日 19:59CVE-2023-30150: PrestaShop leocustomajax 1.0 & 1.0.0 – SQL Injection
漏洞标题 CVE-2023-30150: PrestaShop leocustomajax 1.0 & 1.0.0 - SQL Injection 漏洞描述 PrestaShop leocustomajax 1.0 and 1.0.0 are vulnerable to SQL Injection via modules/leocus...
2023年12月18日 17:44CVE-2021-31316: CentOS Web Panel – SQL Injection
漏洞标题 CVE-2021-31316: CentOS Web Panel - SQL Injection 漏洞描述 The unprivileged user portal part of CentOS Web Panel is affected by a SQL Injection via the 'idsession'...
2021年10月6日 13:59CVE-2021-25298: Nagios XI 5.5.6-5.7.5 – Authenticated Remote Command Injection
漏洞标题 CVE-2021-25298: Nagios XI 5.5.6-5.7.5 - Authenticated Remote Command Injection 漏洞描述 Nagios XI 5.5.6 through 5.7.5 is susceptible to authenticated remote command inject...
2021年4月28日 13:18CVE-2015-1000010: WordPress Simple Image Manipulator < 1.0 - Local File Inclusion
漏洞标题 CVE-2015-1000010: WordPress Simple Image Manipulator < 1.0 - Local File Inclusion 漏洞描述 WordPress Simple Image Manipulator 1.0 is vulnerable to local file inclusion ...
2015年9月22日 16:06CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion
漏洞标题 CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion 漏洞描述 Suprema BioStar before 2.8.2 Video Extension allows remote attackers can read arbitrary files fro...
2020年4月18日 21:19CVE-2025-49001: Dataease JWT 认证绕过漏洞
漏洞标题 CVE-2025-49001: Dataease JWT 认证绕过漏洞 漏洞描述 CVE-2025-49001 是由于JWT校验机制错误导致攻击者可伪造JWT令牌绕过身份验证流程 fofa: body="/js/index-0.0.0-dataease.js...
2025年1月13日 13:41
2026年11月11日 11:45
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

