
最新发布第222页

CVE-2021-24150: WordPress Like Button Rating <2.6.32 - Server-Side Request Forgery
漏洞标题 CVE-2021-24150: WordPress Like Button Rating <2.6.32 - Server-Side Request Forgery 漏洞描述 WordPress Like Button Rating plugin before 2.6.32 is susceptible to server-s...
 2021年6月9日 20:22
CVE-2023-1671: Sophos Web Appliance – Remote Code Execution
漏洞标题 CVE-2023-1671: Sophos Web Appliance - Remote Code Execution 漏洞描述 A pre-auth command injection vulnerability in the warn-proceed handler of Sophos Web Appliance older t...
2023年8月3日 02:22CVE-2023-3368: Chamilo LMS <= v1.11.20 Unauthenticated Command Injection
漏洞标题 CVE-2023-3368: Chamilo LMS <= v1.11.20 Unauthenticated Command Injection 漏洞描述 Command injection in `/main/webservices/additional_webservices.php` in Chamilo LMS <...
2023年7月21日 11:41BIBLIOsoft BIBLIOpac 2008(CVE-2018-16139)
漏洞标题 BIBLIOsoft BIBLIOpac 2008(CVE-2018-16139) 漏洞描述 BIBLIOsoft BIBLIOpac2008通过bin/wxis.exe/BIBLIOpac/的db或action参数包含一个跨站点脚本漏洞,该漏洞允许远程攻击者注入任意w...
2018年6月5日 12:07CVE-2020-24903: Cute Editor for ASP.NET 6.4 – Cross-Site Scripting
漏洞标题 CVE-2020-24903: Cute Editor for ASP.NET 6.4 - Cross-Site Scripting 漏洞描述 Cute Editor for ASP.NET 6.4 contains a cross-site scripting vulnerability. An attacker can inje...
2020年5月4日 16:17CVE-2021-3018: IPeakCMS 3.5 – SQL Injection
漏洞标题 CVE-2021-3018: IPeakCMS 3.5 - SQL Injection 漏洞描述 ipeak Infosystems ibexwebCMS 3.5 contains an unauthenticated Boolean-based SQL injection caused by unsanitized 'i...
2021年5月5日 18:04CVE-2022-29005: Online Birth Certificate System 1.2 – Stored Cross-Site Scripting
漏洞标题 CVE-2022-29005: Online Birth Certificate System 1.2 - Stored Cross-Site Scripting 漏洞描述 Online Birth Certificate System 1.2 contains multiple stored cross-site scriptin...
2022年7月14日 02:51CVE-2017-5983: JIRA Workflow Designer Plugin in Atlassian JIRA Server > 6.3.0 – Remote Code Execution (XXE)
漏洞标题 CVE-2017-5983: JIRA Workflow Designer Plugin in Atlassian JIRA Server > 6.3.0 - Remote Code Execution (XXE) 漏洞描述 The JIRA Workflow Designer Plugin in Atlassian JIRA...
2017年8月8日 10:18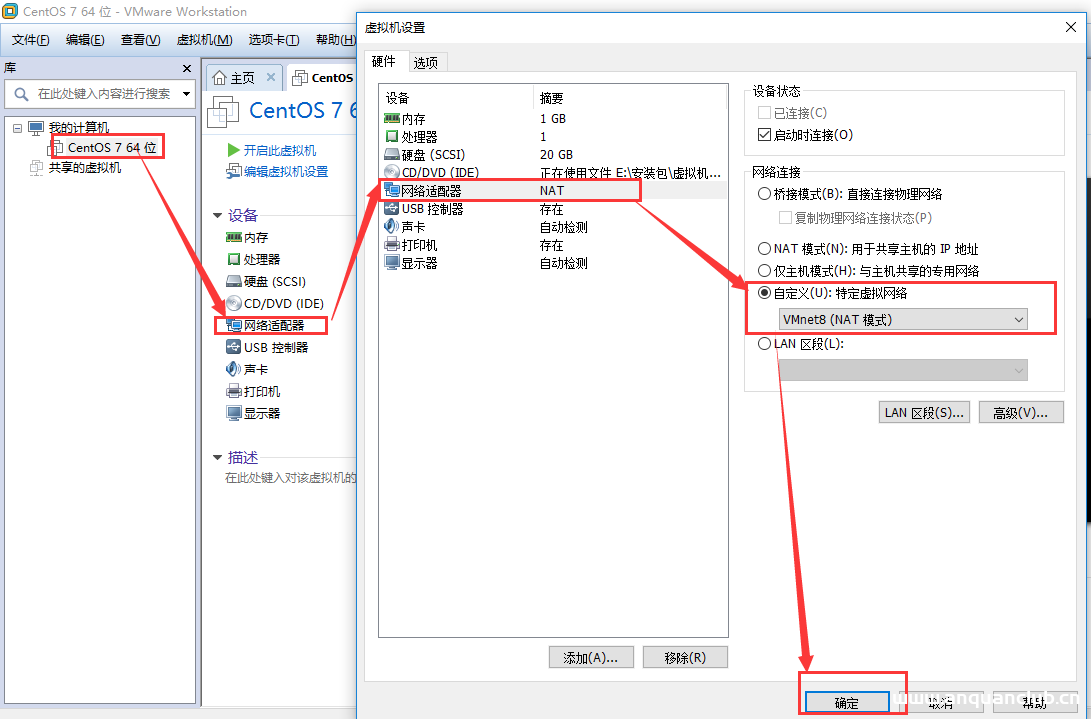
用xshell连接VMware中的Linux的方法步骤(2种)_VMware
这篇文章主要介绍了用xshell连接VMware中的Linux的方法步骤(2种),文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 ...
2023年10月22日 21:34CVE-2022-1221: WordPress Gwyn’s Imagemap Selector <=0.3.3 - Cross-Site Scripting
漏洞标题 CVE-2022-1221: WordPress Gwyn's Imagemap Selector <=0.3.3 - Cross-Site Scripting 漏洞描述 Wordpress Gwyn's Imagemap Selector plugin 0.3.3 and prior contains a...
2022年2月28日 04:19CVE-2022-0148: WordPress All-in-one Floating Contact Form <2.0.4 - Cross-Site Scripting
漏洞标题 CVE-2022-0148: WordPress All-in-one Floating Contact Form <2.0.4 - Cross-Site Scripting 漏洞描述 WordPress All-in-one Floating Contact Form, Call, Chat, and 50+ Social ...
2022年11月10日 00:13CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call
漏洞标题 CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call 漏洞描述 WordPress WooCommerce plugin before 3.1.2 does not have authorisation and CSRF checks in ...
2022年7月12日 01:58CVE-2022-1386: WordPress Fusion Builder <3.6.2 - Server-Side Request Forgery
漏洞标题 CVE-2022-1386: WordPress Fusion Builder <3.6.2 - Server-Side Request Forgery 漏洞描述 WordPress Fusion Builder plugin before 3.6.2 is susceptible to server-side request...
2022年7月23日 13:46CVE-2020-7961: Liferay Portal RCE 反序列化命令执行漏洞
漏洞标题 CVE-2020-7961: Liferay Portal RCE 反序列化命令执行漏洞 漏洞描述 Liferay Portal CE是一款用来快速构建网站的开源系统。其7.2.0 GA1及以前的版本API接口中存在一处反序列化漏洞,利...
2020年8月1日 02:01CVE-2020-15415: DrayTek Vigor – Command Injection
漏洞标题 CVE-2020-15415: DrayTek Vigor - Command Injection 漏洞描述 DrayTek Vigor devices contain a command injection vulnerability in the cvmcfgupload functionality. The vulnerabi...
2020年10月1日 01:36CVE-2021-21805: Advantech R-SeeNet 2.4.12 – OS Command Injection
漏洞标题 CVE-2021-21805: Advantech R-SeeNet 2.4.12 - OS Command Injection 漏洞描述 Advantech R-SeeNet 2.4.12 is susceptible to remote OS command execution via the ping.php script f...
2021年1月28日 01:41
2026年11月12日 11:45
2026年11月11日 11:45
2026年11月10日 11:45
2026年11月9日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

