
最新发布第223页

CVE-2018-19386: SolarWinds Database Performance Analyzer 11.1.457 – Cross-Site Scripting
漏洞标题 CVE-2018-19386: SolarWinds Database Performance Analyzer 11.1.457 - Cross-Site Scripting 漏洞描述 SolarWinds Database Performance Analyzer 11.1.457 contains a reflected cr...
 2018年2月19日 09:49
CVE-2020-10199: Nexus Repository before 3.21.2 allows JavaEL Injection
漏洞标题 CVE-2020-10199: Nexus Repository before 3.21.2 allows JavaEL Injection 漏洞描述 漏洞触发需要任意账户权限 body="Nexus Repository Manager" app="Nexus-Reposito...
2020年2月20日 13:47
bugbounty技巧聚合20220119
漏洞报告 通过 post auth SSRF 窃取管理 JWT (CVE-2021-22056) http://blog.assetnote.io/2022/01/17/workspace-one-access-ssrf/ 挖洞技巧 Top 10 web hacking techniques of 2021 - PortSwigg...
2022年3月10日 23:33CVE-2020-12800: WordPress Contact Form 7 <1.3.3.3 - Remote Code Execution
漏洞标题 CVE-2020-12800: WordPress Contact Form 7 <1.3.3.3 - Remote Code Execution 漏洞描述 WordPress Contact Form 7 before 1.3.3.3 allows unrestricted file upload and remote co...
2020年2月25日 21:45删除docker images中为none的镜像操作_docker
这篇文章主要介绍了删除docker images中为none的镜像操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 由于平时一直使用docker build 命令才生成一个镜像,有时候由于代...
2022年8月4日 20:36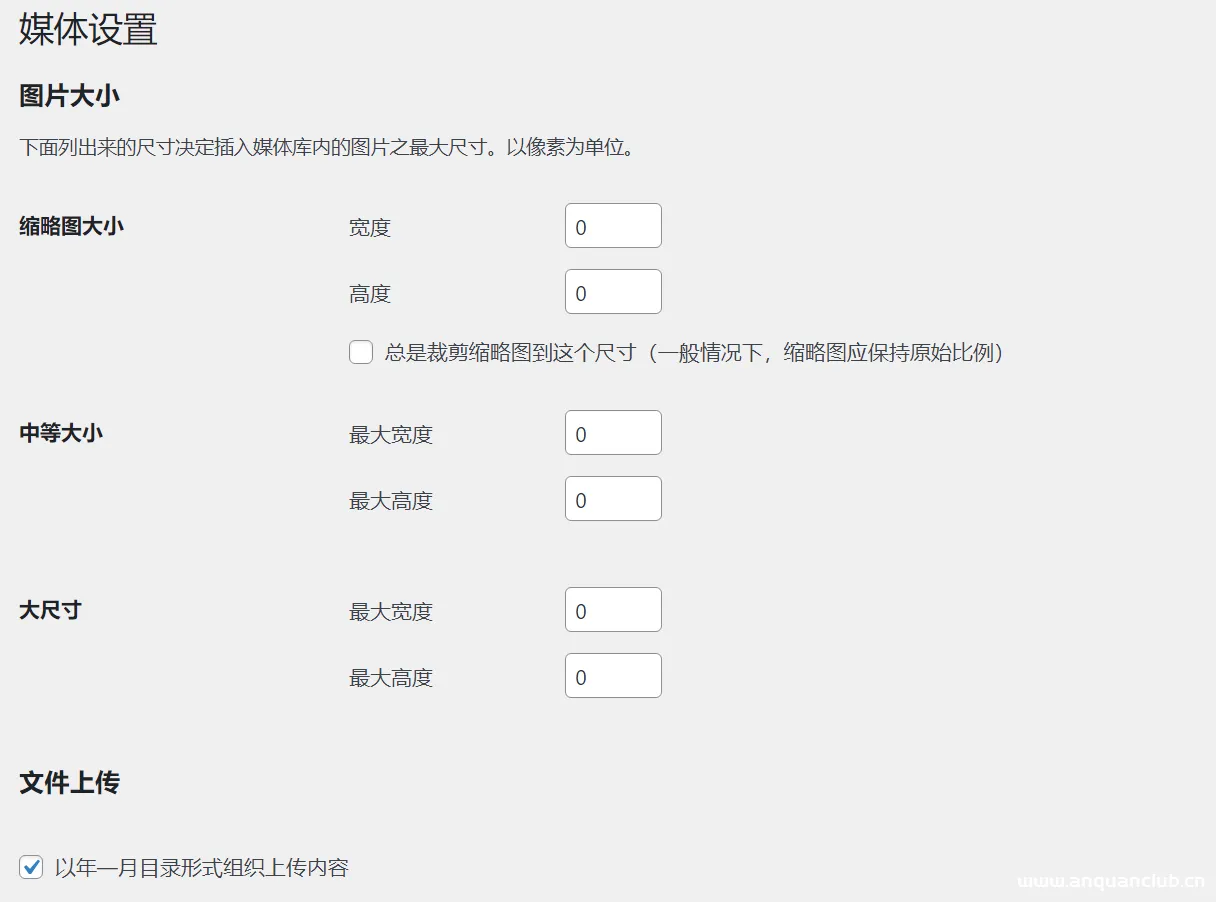
wordpress彻底关闭自动生成缩略图,节约服务器资源空间(附清理缩略图脚本)
前言 WordPress上传图片如何禁止自动生成缩略图呢?我们在使用WordPress程序的时候上传的图片会自动生成缩略图,还会占用我们的空间内容。那么我们如何来禁止呢?今天安全小天地给大家总结了禁...

 2023年1月13日 19:33
CVE-2024-39887: Apache Superset < 4.0.2 - SQL Injection
漏洞标题 CVE-2024-39887: Apache Superset < 4.0.2 - SQL Injection 漏洞描述 An SQL Injection vulnerability in Apache Superset exists due to improper neutralization of special elem...
2024年6月23日 14:39CVE-2021-45811: osTicket 1.15.x – SQL Injection
漏洞标题 CVE-2021-45811: osTicket 1.15.x - SQL Injection 漏洞描述 A SQL injection vulnerability in the "Search" functionality of "tickets.php" page in osTicket ...
2021年12月14日 15:43CVE-2024-2928: MLflow < 2.11.3 - Path Traversal
漏洞标题 CVE-2024-2928: MLflow < 2.11.3 - Path Traversal 漏洞描述 MLflow versions prior to 2.11.3 are vulnerable to a Path Traversal attack due to improper URI fragment parsing....
2024年7月6日 15:15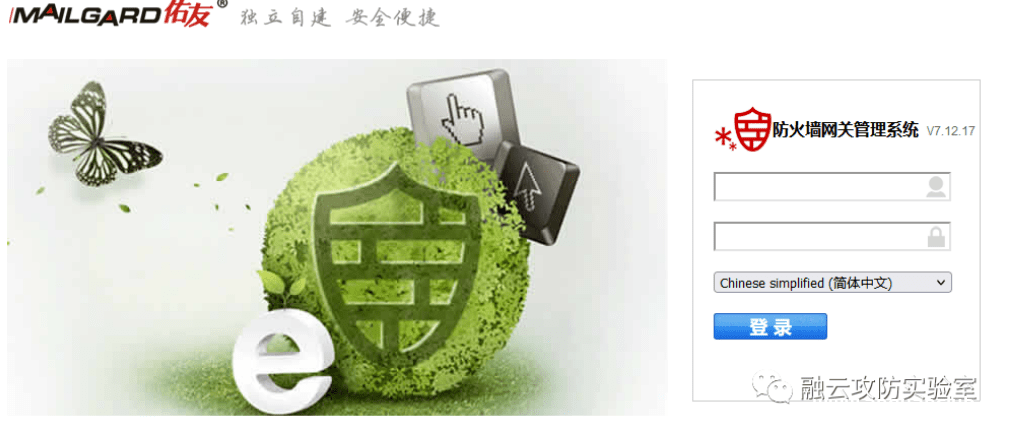
佑友防火墙 后台命令执行漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 佑友防火墙 后台命令执行漏洞 佑友防火墙+路由,保障您的网络更安全更稳定。弥补传统路由器因内外人数增加带来的网络延迟和不稳定问题...
2026年2月13日 12:53CVE-2023-30212: OURPHP <= 7.2.0 - Cross Site Scripting
漏洞标题 CVE-2023-30212: OURPHP <= 7.2.0 - Cross Site Scripting 漏洞描述 OURPHP <= 7.2.0 is vulnerale to Cross Site Scripting (XSS) via /client/manage/ourphp_out.php. PoC代码
2023年10月31日 07:15CVE-2022-1439: Microweber <1.2.15 - Cross-Site Scripting
漏洞标题 CVE-2022-1439: Microweber <1.2.15 - Cross-Site Scripting 漏洞描述 Microweber prior to 1.2.15 contains a reflected cross-site scripting vulnerability. An attacker can ex...
2022年8月20日 11:18CVE-2025-47204: Bootstrap Multiselect <= 1.1.2 - Cross-Site Scripting
漏洞标题 CVE-2025-47204: Bootstrap Multiselect <= 1.1.2 - Cross-Site Scripting 漏洞描述 A PHP script in the source code release echoes arbitrary POST data. If a developer adopts...
2025年1月15日 06:32CVE-2023-1671: Sophos Web Appliance – Remote Code Execution
漏洞标题 CVE-2023-1671: Sophos Web Appliance - Remote Code Execution 漏洞描述 A pre-auth command injection vulnerability in the warn-proceed handler of Sophos Web Appliance older t...
2023年2月16日 23:52CVE-2025-6204: DELMIA Apriso – Command Injection
漏洞标题 CVE-2025-6204: DELMIA Apriso - Command Injection 漏洞描述 An Improper Control of Generation of Code (code injection / file upload → RCE) vulnerability affecting DELMIA Ap...
2025年11月8日 10:57CVE-2024-32640: Mura/Masa CMS – SQL Injection
漏洞标题 CVE-2024-32640: Mura/Masa CMS - SQL Injection 漏洞描述 The Mura/Masa CMS is vulnerable to SQL Injection. PoC代码
2024年4月6日 09:33
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

