
最新发布第225页

CVE-2022-42746: CandidATS 3.0.0 – Cross-Site Scripting.
漏洞标题 CVE-2022-42746: CandidATS 3.0.0 - Cross-Site Scripting. 漏洞描述 CandidATS 3.0.0 contains a cross-site scripting vulnerability via the indexFile parameter of the ajax.php ...
 2022年3月30日 03:04
CVE-2022-32417: PBootCMS RCE
漏洞标题 CVE-2022-32417: PBootCMS RCE 漏洞描述 fofa: app="PBOOTCMS" PoC代码
2022年3月30日 13:05CVE-2005-0850: FileZilla Server < 0.9.6 - DoS via MS-DOS Device Names
漏洞标题 CVE-2005-0850: FileZilla Server < 0.9.6 - DoS via MS-DOS Device Names 漏洞描述 FileZilla Server versions prior to 0.9.6 are vulnerable to denial of service when process...
2005年4月21日 19:53CVE-2005-0850: FileZilla Server < 0.9.6 - DoS via MS-DOS Device Names
漏洞标题 CVE-2005-0850: FileZilla Server < 0.9.6 - DoS via MS-DOS Device Names 漏洞描述 FileZilla Server versions prior to 0.9.6 are vulnerable to denial of service when process...
2005年6月7日 17:01CVE-2005-0851: FileZilla Server < 0.9.6 - DoS via MODE Z Infinite Loop
漏洞标题 CVE-2005-0851: FileZilla Server < 0.9.6 - DoS via MODE Z Infinite Loop 漏洞描述 FileZilla Server versions prior to 0.9.6 are vulnerable to denial of service when using ...
2005年2月16日 08:14CVE-2022-32417: PBootCMS RCE
漏洞标题 CVE-2022-32417: PBootCMS RCE 漏洞描述 fofa: app="PBOOTCMS" PoC代码
2022年11月17日 00:49CVE-2005-3634: SAP Web Application Server 6.x/7.0 – Open Redirect
漏洞标题 CVE-2005-3634: SAP Web Application Server 6.x/7.0 - Open Redirect 漏洞描述 frameset.htm in the BSP runtime in SAP Web Application Server (WAS) 6.10 through 7.00 allows rem...
2005年6月11日 07:32CVE-2005-3634: SAP Web Application Server 6.x/7.0 – Open Redirect
漏洞标题 CVE-2005-3634: SAP Web Application Server 6.x/7.0 - Open Redirect 漏洞描述 frameset.htm in the BSP runtime in SAP Web Application Server (WAS) 6.10 through 7.00 allows rem...
2005年12月30日 06:44CVE-2005-3344: Horde Groupware Unauthenticated Admin Access
漏洞标题 CVE-2005-3344: Horde Groupware Unauthenticated Admin Access 漏洞描述 Horde Groupware contains an administrative account with a blank password, which allows remote attacker...
2005年10月26日 10:48CVE-2024-11305: Altenergy Power Control Software – SQL Injection
漏洞标题 CVE-2024-11305: Altenergy Power Control Software - SQL Injection 漏洞描述 A vulnerability classified as critical was found in Altenergy Power Control Software up to 202411...
2024年5月5日 18:36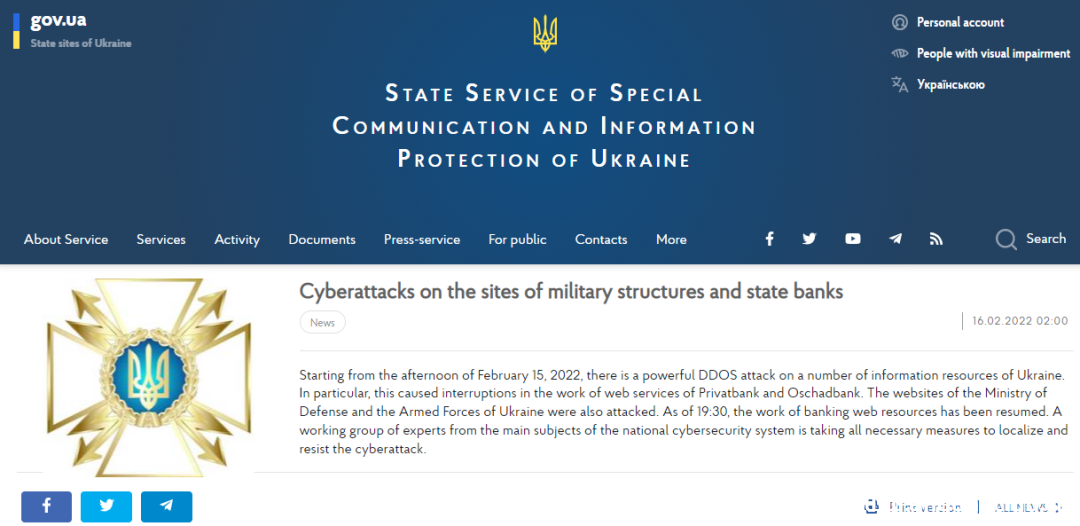
乌克兰国防部及国有银行网站因DDoS攻击而关闭
据报道,乌克兰国防部和武装部队以及该国的两家国有银行Privatbank(乌克兰最大的银行)和Oschadbank(国家储蓄银行)的官方门户网站于2月15日受到分布式拒绝服务(DDoS)攻击。 本次网络...
2022年3月10日 23:40CVE-2022-22947: Spring Cloud Gateway Code Injection
漏洞标题 CVE-2022-22947: Spring Cloud Gateway Code Injection 漏洞描述 Applications using Spring Cloud Gateway prior to 3.1.1+ and 3.0.7+ are vulnerable to a code injection attack w...
2022年3月27日 16:10
日本丰田汽车因供应商遭网络攻击被迫停产
昨日,日本知名汽车制造商丰田汽车(Toyota Motor Corporation)发布了一则公告,由于其提供汽车内外饰零部件的供应商小岛冲压工业(Kojima Industries Corporation)遭受网络攻击,丰田被迫暂...
2022年3月10日 23:40
CVE-2022-4375: Mingsoft MCMS – SQL Injection
漏洞标题 CVE-2022-4375: Mingsoft MCMS - SQL Injection 漏洞描述 SQL injection vulnerability in Mingsoft MCMS up to 5.2.9 via the sqlWhere parameter in /cms/category/list. PoC代码
2022年7月26日 06:44CVE-2020-26214: Alerta < 8.1.0 - Authentication Bypass
漏洞标题 CVE-2020-26214: Alerta < 8.1.0 - Authentication Bypass 漏洞描述 Alerta prior to version 8.1.0 is prone to authentication bypass when using LDAP as an authorization prov...
2020年6月15日 09:44
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

