
最新发布第226页
PDF解析器html/XSS 实现SSRF
上次安全小天地审核整理SSRF的时候找我沟通,聊到了PDF的SSRF,当时答应了找找之前的存档写个文档。遂写下改小菜文。大佬们勿喷。(文章写于去年,随便记录的文章,可能存在逻辑或者图片的丢失...
 2022年3月10日 23:37

CVE-2019-5128: YouPHPTube Encoder – Arbitrary File Write
漏洞标题 CVE-2019-5128: YouPHPTube Encoder - Arbitrary File Write 漏洞描述 Exploitable unauthenticated command injections exist in YouPHPTube Encoder 2.3 a plugin for providing enc...
2019年4月3日 19:21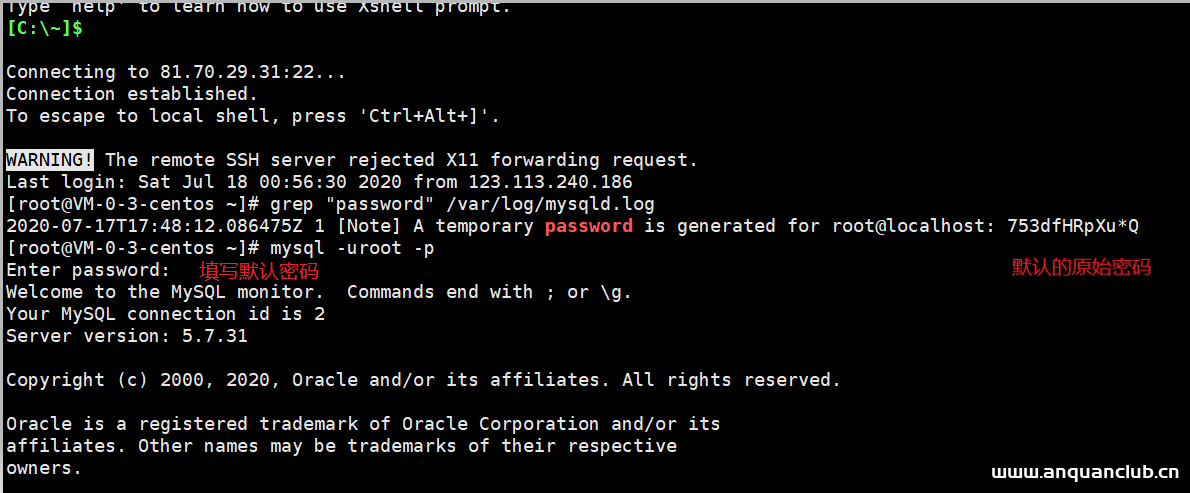
服务器Centos部署MySql并连接Navicat过程详解_Linux
这篇文章主要介绍了服务器Centos部署MySql并连接Navicat过程详解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 (1)服务器配置: [root@l...
2023年9月12日 21:25
印尼央行确认遭受勒索软件攻击
1月20日,印度尼西亚共和国中央银行——印度尼西亚银行(BANK INDONESIA)通信部执行主任Erwin Haryono证实,银行于上个月遭受了勒索软件攻击。中央银行有着管理货币部门、维持支付系统和金融系...
2022年3月10日 23:34CVE-2022-28955: D-Link DIR-816L – Improper Access Control
漏洞标题 CVE-2022-28955: D-Link DIR-816L - Improper Access Control 漏洞描述 D-Link DIR-816L_FW206b01 is susceptible to improper access control. An attacker can access folders folde...
2022年3月6日 09:22CVE-2016-1000129: WordPress defa-online-image-protector <=3.3 - Cross-Site Scripting
漏洞标题 CVE-2016-1000129: WordPress defa-online-image-protector <=3.3 - Cross-Site Scripting 漏洞描述 WordPress defa-online-image-protector 3.3 and before contains a reflected ...
2016年4月3日 17:52CVE-2021-20124: Draytek VigorConnect 6.0-B3 – Local File Inclusion
漏洞标题 CVE-2021-20124: Draytek VigorConnect 6.0-B3 - Local File Inclusion 漏洞描述 Draytek VigorConnect 1.6.0-B3 is susceptible to local file inclusion in the file download funct...
2021年3月2日 05:52CVE-2017-18505: BestWebSoft’s Twitter < 2.55 - Cross-Site Scripting
漏洞标题 CVE-2017-18505: BestWebSoft's Twitter < 2.55 - Cross-Site Scripting 漏洞描述 The twitter-plugin plugin before 2.55 for WordPress has XSS. PoC代码
2017年2月14日 01:04CVE-2021-22911: Rocket.Chat <=3.13 - NoSQL Injection
漏洞标题 CVE-2021-22911: Rocket.Chat <=3.13 - NoSQL Injection 漏洞描述 Rocket.Chat 3.11, 3.12 and 3.13 contains a NoSQL injection vulnerability which allows unauthenticated acce...
2021年5月16日 14:40CVE-2023-30150: PrestaShop leocustomajax 1.0 & 1.0.0 – SQL Injection
漏洞标题 CVE-2023-30150: PrestaShop leocustomajax 1.0 & 1.0.0 - SQL Injection 漏洞描述 PrestaShop leocustomajax 1.0 and 1.0.0 are vulnerable to SQL Injection via modules/leocus...
2023年5月15日 07:24CVE-2023-32068: XWiki – Open Redirect
漏洞标题 CVE-2023-32068: XWiki - Open Redirect 漏洞描述 XWiki Platform is vulnerable to open redirect attacks due to improper validation of the xredirect parameter. This allows an ...
2023年5月2日 19:52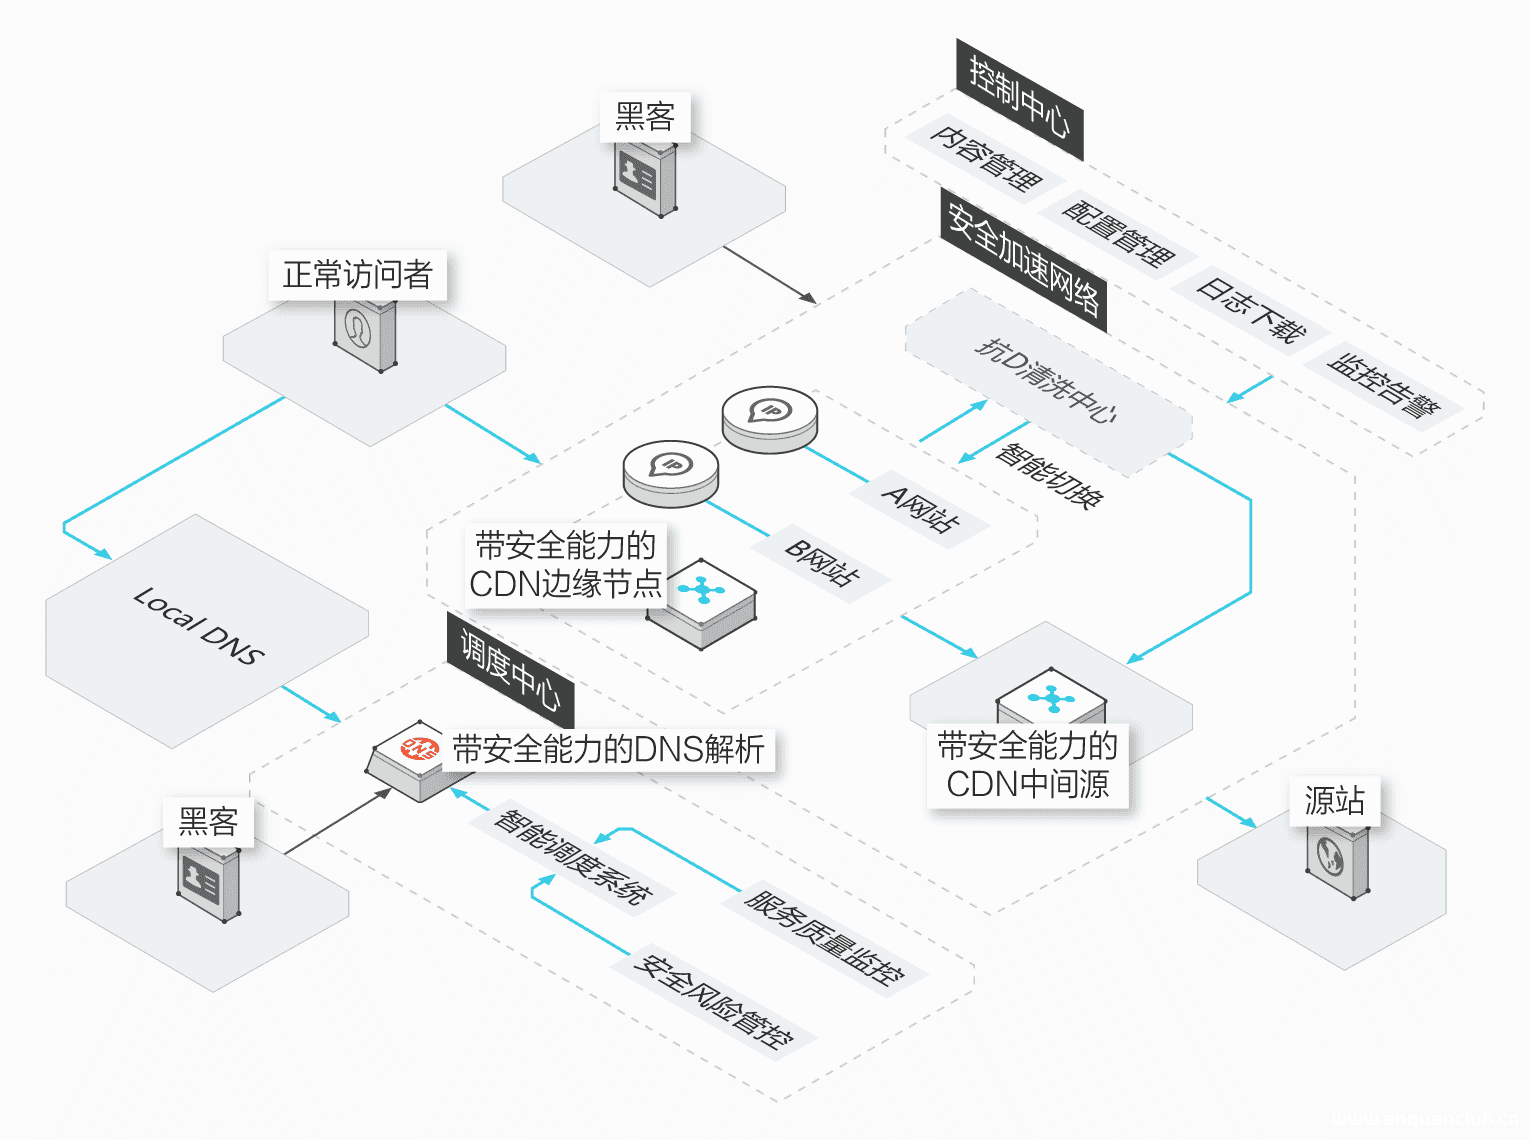
网站加速之CDN、SCDN、DCDN区别在哪?如何选择?_服务器其它
阿里云CDN(内容分发网络)是用户比较熟悉的,那么什么是SCDN?SCDN和CDN有什么区别? 1、CDN 是网站中最常用的加速功能。通过分布式服务器布局,把网站业务内容缓存到各地的云服务器中,供访客...
2024年6月7日 20:30CVE-2021-21315: Node.JS System Information Library <5.3.1 - Remote Command Injection
漏洞标题 CVE-2021-21315: Node.JS System Information Library <5.3.1 - Remote Command Injection 漏洞描述 Node.JS System Information Library System before version 5.3.1 is suscepti...
2021年9月3日 02:02CVE-2019-14205: WordPress Nevma Adaptive Images <0.6.67 - Local File Inclusion
漏洞标题 CVE-2019-14205: WordPress Nevma Adaptive Images <0.6.67 - Local File Inclusion 漏洞描述 WordPress Nevma Adaptive Images plugin before 0.6.67 allows remote attackers to ...
2019年4月3日 00:11CVE-2025-1562: Recover WooCommerce Cart Abandonment, Newsletter, Email Marketing, Marketing Automation By FunnelKit – Broken Access Control
漏洞标题 CVE-2025-1562: Recover WooCommerce Cart Abandonment, Newsletter, Email Marketing, Marketing Automation By FunnelKit - Broken Access Control 漏洞描述 The Recover WooCommerc...
2025年3月24日 22:07CVE-2022-0349: WordPress NotificationX <2.3.9 - SQL Injection
漏洞标题 CVE-2022-0349: WordPress NotificationX <2.3.9 - SQL Injection 漏洞描述 WordPress NotificationX plugin prior to 2.3.9 contains a SQL injection vulnerability. The plugin ...
2022年3月1日 06:13
2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
2026年10月12日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

