
最新发布第226页

CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover
漏洞标题 CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover 漏洞描述 The Motors theme for WordPress is vulnerable to pri...
 2025年12月29日 16:41
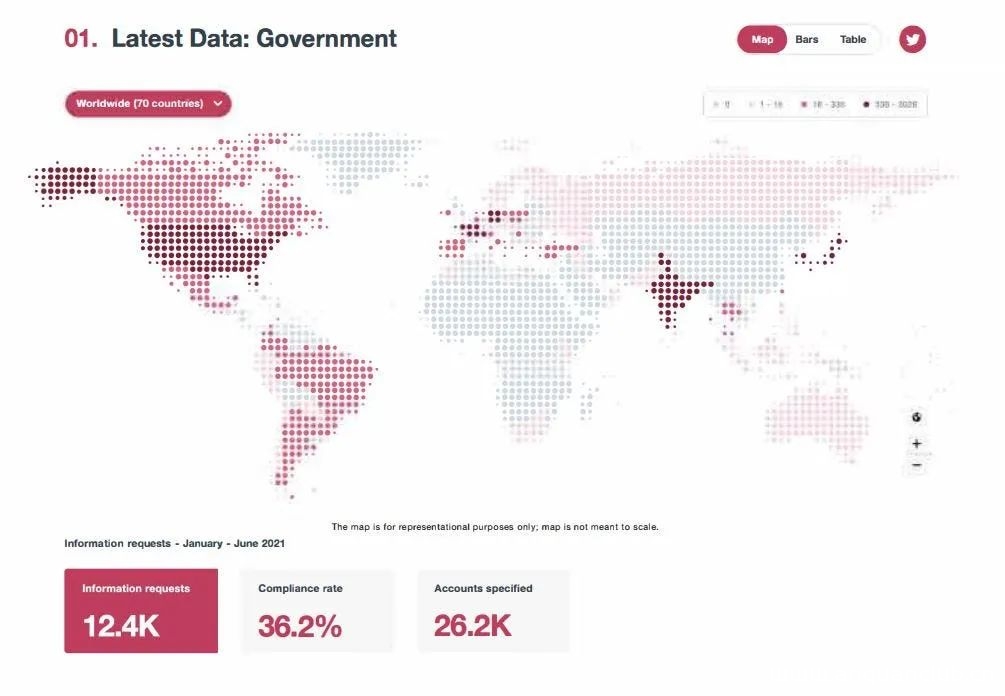
推特透明度报告:美国政府索要的信息最多
1月25日,推特Twitter透明度中心公布了一份透明度报告,以让用户了解世界范围内各国政府向他们提出的要求。 推特认为透明度有利于保护持续受到威胁的开放互联网,并且对于追究公司和政府的...
2022年3月10日 23:40CVE-2022-32772: WWBN AVideo 11.6 – Cross-Site Scripting
漏洞标题 CVE-2022-32772: WWBN AVideo 11.6 - Cross-Site Scripting 漏洞描述 WWBN AVideo 11.6 contains a cross-site scripting vulnerability in the footer alerts functionality via the ...
2022年5月6日 06:14
俄罗斯拟将苹果、微软等59家撤出俄罗斯的西方企业收归国有
据俄《消息报》,俄罗斯政府正在推进一项计划——将苹果等制裁俄罗斯的西方公司国有化。周四,该计划得到了俄罗斯总统弗拉基米尔·普京的支持,这意味着政府将可要求法院下令对因非商业原因撤出...
2022年3月16日 09:15Adobe Commerce CVE-2022-24086 远程代码执行漏洞
漏洞标题 Adobe Commerce CVE-2022-24086 远程代码执行漏洞 漏洞描述 Adobe Commerce CVE-2022-24086 远程 PoC代码 暂无
2022年2月25日 01:47CVE-2025-22457: Ivanti Connect Secure – Stack-based Buffer Overflow
漏洞标题 CVE-2025-22457: Ivanti Connect Secure - Stack-based Buffer Overflow 漏洞描述 Ivanti Connect Secure before version 22.7R2.6, Ivanti Policy Secure before version 22.7R1.4, a...
2025年12月14日 18:12CVE-2025-51501: Microweber CMS2.0 – Cross-Site Scripting
漏洞标题 CVE-2025-51501: Microweber CMS2.0 - Cross-Site Scripting 漏洞描述 Reflected Cross-Site Scripting (XSS) in the `id` parameter of the `live_edit.module_settings` API endpoin...
2025年1月9日 12:56CVE-2025-26793: FREEDOM Administration – Default Login
漏洞标题 CVE-2025-26793: FREEDOM Administration - Default Login 漏洞描述 The Web GUI configuration panel of Hirsch (formerly Identiv and Viscount) Enterphone MESH through 2024 ship...
2025年1月10日 19:43CVE-2025-6197: Open Redirect via Organization Switching
漏洞标题 CVE-2025-6197: Open Redirect via Organization Switching 漏洞描述 An open redirect vulnerability has been identified in Grafana OSS organization switching functionality. Pr...
2025年1月10日 17:17CVE-2025-68645: Zimbra Collaboration – Local File Inclusion
漏洞标题 CVE-2025-68645: Zimbra Collaboration - Local File Inclusion 漏洞描述 Zimbra Collaboration (ZCS) 10.0 and 10.1 contain a local file inclusion caused by improper handling of...
2025年11月23日 02:38CVE-2025-34085: WordPress Simple File List <=4.2.2 - Remote Code Execution
漏洞标题 CVE-2025-34085: WordPress Simple File List <=4.2.2 - Remote Code Execution 漏洞描述 An unrestricted file upload vulnerability in the WordPress Simple File List plugin b...
2025年11月22日 22:18CVE-2025-40630: IceWarp Mail Server ≤11.4.0 – Open Redirect
漏洞标题 CVE-2025-40630: IceWarp Mail Server ≤11.4.0 - Open Redirect 漏洞描述 IceWarp Mail Server version 11.4.0 and below contains an open redirect vulnerability that allows atta...
2025年7月15日 05:33CVE-2025-34031: Moodle Jmol Filter 6.1 – Local File Inclusion
漏洞标题 CVE-2025-34031: Moodle Jmol Filter 6.1 - Local File Inclusion 漏洞描述 Moodle Jmol Filter 6.1 is vulnerable to local file inclusion through the jsmol.php file, allowing at...
2025年8月9日 03:35CVE-2025-2748: Kentico Xperience CMS – Unauthenticated Stored XSS
漏洞标题 CVE-2025-2748: Kentico Xperience CMS - Unauthenticated Stored XSS 漏洞描述 The Kentico Xperience application does not fully validate or filter files uploaded via the multi...
2025年11月15日 08:57CVE-2025-34045: WeiPHP 5.0 – Path Traversal
漏洞标题 CVE-2025-34045: WeiPHP 5.0 - Path Traversal 漏洞描述 WeiPHP 5.0 contains a path traversal caused by insufficient input validation of the picUrl parameter in /public/index....
2025年11月13日 05:46CVE-2025-34040: Zhiyuan OA Platform – Arbitrary File Upload
漏洞标题 CVE-2025-34040: Zhiyuan OA Platform - Arbitrary File Upload 漏洞描述 An arbitrary file upload vulnerability exists in the Zhiyuan OA platform 5.0, 5.1 - 5.6sp1, 6.0 - 6.1s...
2025年11月10日 10:10
2026年10月20日 11:45
2026年10月19日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

