
最新发布第228页

CVE-2016-10960: WordPress wSecure Lite < 2.4 - Remote Code Execution
漏洞标题 CVE-2016-10960: WordPress wSecure Lite < 2.4 - Remote Code Execution 漏洞描述 WordPress wsecure plugin before 2.4 is susceptible to remote code execution via shell meta...
 2016年9月24日 05:29
CVE-2018-10088: XiongMai uc-httpd 1.0.0 – Buffer Overflow
漏洞标题 CVE-2018-10088: XiongMai uc-httpd 1.0.0 - Buffer Overflow 漏洞描述 Buffer overflow in XiongMai uc-httpd 1.0.0 has unspecified impact and attack vectors, a different vulner...
2018年5月6日 11:37CVE-2024-39646: WordPress Custom 404 Pro <= 3.11.1 - Reflected XSS
漏洞标题 CVE-2024-39646: WordPress Custom 404 Pro <= 3.11.1 - Reflected XSS 漏洞描述 Improper Neutralization of Input During Web Page Generation (XSS or 'Cross-site Scripti...
2024年6月17日 08:48CVE-2025-31125: Vite Development Server – Path Traversal
漏洞标题 CVE-2025-31125: Vite Development Server - Path Traversal 漏洞描述 Path traversal vulnerability in Vite development server's @fs endpoint allows attackers to access fi...
2025年6月20日 03:27cPanel低于11.109.9999.116存在XSS漏洞(CVE-2023-29489)
漏洞标题 cPanel低于11.109.9999.116存在XSS漏洞(CVE-2023-29489) 漏洞描述 cPanel 是一套在网页寄存业中最享负盛名的商业软件,是基于于 Linux 和 BSD 系统及以 PHP开发且性质为闭源软件;提供...
2023年4月19日 17:47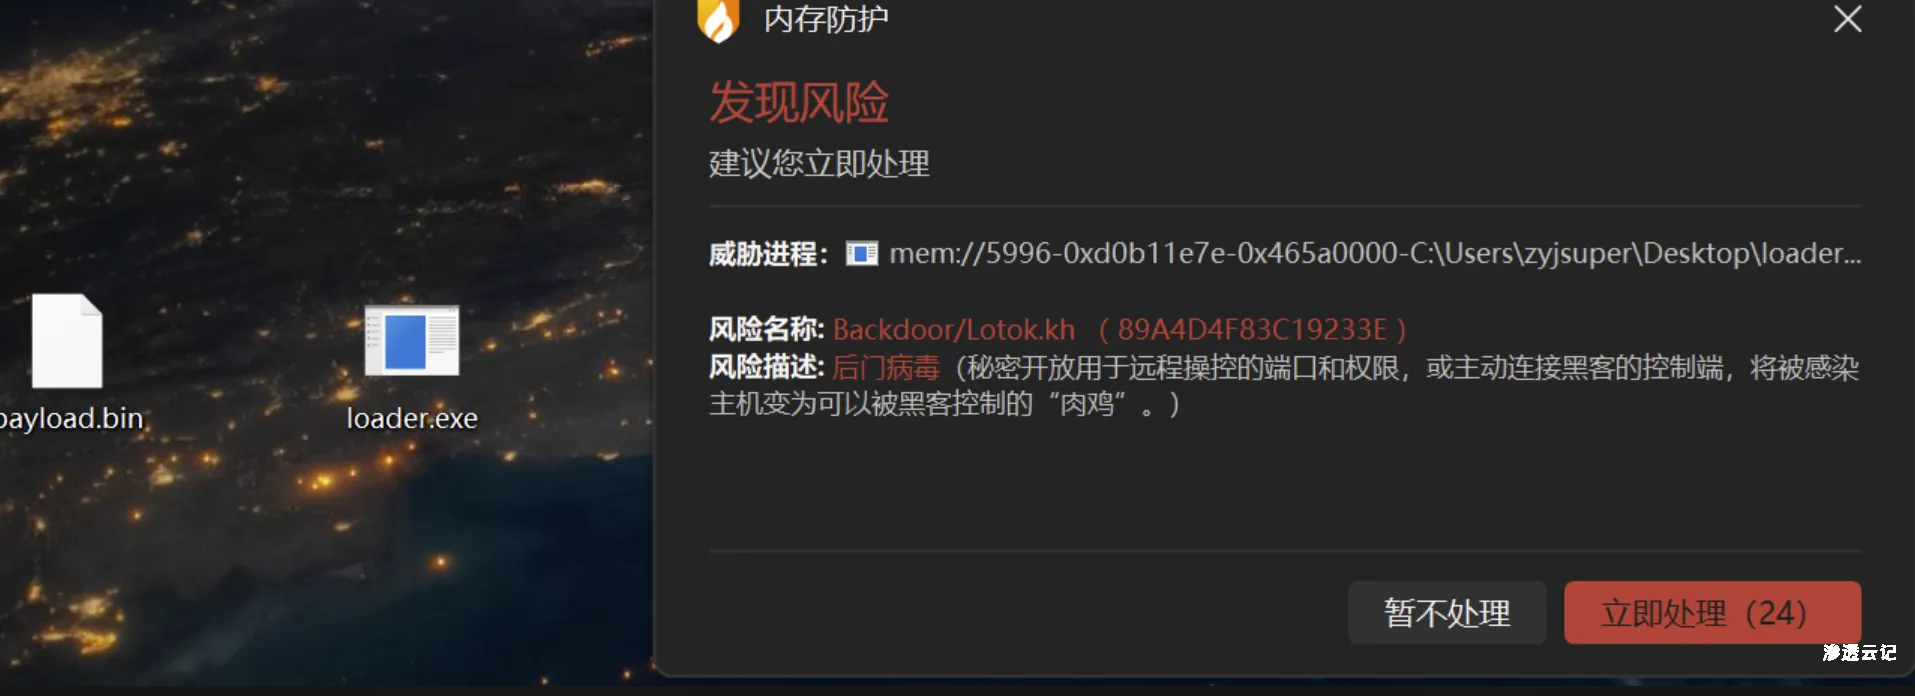
【工具更新】EasyShell v2.6 版本更新,1. 新增邮件钓鱼模块,支持stageless客户端一键添加邮件压缩包、2.修复shellcode内存告警情况等bug
更新说明 感谢各位师傅们的热心测试,发现了诸多bug,目前已经修复的有: 修复shellcode执行火绒内存告警的bug 优化屏幕截屏,设置为低中高三挡 优化文件管理展示 更新linux旧系统交互式shell执...

 2026年8月5日 23:23
CVE-2025-34026: Versa Concerto Actuator Endpoint – Authentication Bypass
漏洞标题 CVE-2025-34026: Versa Concerto Actuator Endpoint - Authentication Bypass 漏洞描述 An authentication bypass vulnerability affected the Spring Boot Actuator endpoints in Ver...
2025年4月20日 18:37CVE-2017-10075: Oracle Content Server – Cross-Site Scripting
漏洞标题 CVE-2017-10075: Oracle Content Server - Cross-Site Scripting 漏洞描述 Oracle Content Server version 11.1.1.9.0, 12.2.1.1.0 and 12.2.1.2.0 are susceptible to cross-site scr...
2017年7月18日 04:59
一行代码教你如何隐藏Linux进程_Linux
这篇文章主要介绍了一行代码教你如何隐藏Linux进程,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 总有朋友问隐藏...
2023年7月15日 20:53CVE-2023-4596: WordPress Plugin Forminator 1.24.6 – Arbitrary File Upload
漏洞标题 CVE-2023-4596: WordPress Plugin Forminator 1.24.6 - Arbitrary File Upload 漏洞描述 The Forminator plugin for WordPress is vulnerable to arbitrary file uploads due to file ...
2023年6月3日 21:18CVE-2022-1058: Gitea <1.16.5 - Open Redirect
漏洞标题 CVE-2022-1058: Gitea <1.16.5 - Open Redirect 漏洞描述 Gitea before 1.16.5 is susceptible to open redirect via GitHub repository go-gitea/gitea. An attacker can redirect...
2022年9月26日 15:38CVE-2021-44228: Apache Log4j2 Remote Code Injection
漏洞标题 CVE-2021-44228: Apache Log4j2 Remote Code Injection 漏洞描述 Apache Log4j2 <=2.14.1 JNDI features used in configuration, log messages, and parameters do not protect aga...
2021年3月22日 06:27CVE-2024-5947: Deep Sea Electronics DSE855 – Authentication Bypass
漏洞标题 CVE-2024-5947: Deep Sea Electronics DSE855 - Authentication Bypass 漏洞描述 Deep Sea Electronics DSE855 Configuration Backup Missing Authentication Information Disclosure ...
2024年12月12日 17:03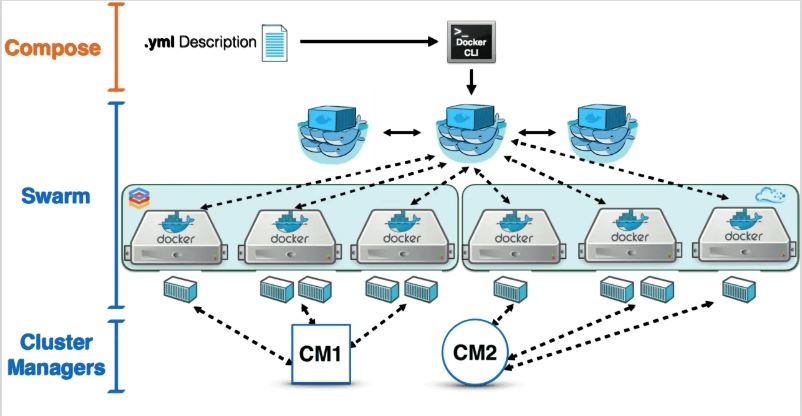
Docker 搭建集群MongoDB的实现步骤_docker
这篇文章主要介绍了Docker 搭建集群MongoDB的实现步骤,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 前言 由于公...
2023年5月25日 20:03CVE-2024-28397: pyload-ng js2py – Remote Code Execution
漏洞标题 CVE-2024-28397: pyload-ng js2py - Remote Code Execution 漏洞描述 An issue in the component js2py.disable_pyimport() of js2py up to v0.74 allows attackers to execute arbitr...
2024年2月9日 06:22CVE-2022-24682: Zimbra Collaboration Suite < 8.8.15 - Improper Encoding
漏洞标题 CVE-2022-24682: Zimbra Collaboration Suite < 8.8.15 - Improper Encoding 漏洞描述 An issue was discovered in the Calendar feature in Zimbra Collaboration Suite 8.8.x bef...
2022年3月26日 12:27
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
2026年11月3日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

