
最新发布第231页

CVE-2018-10822: D-Link Routers – Local File Inclusion
漏洞标题 CVE-2018-10822: D-Link Routers - Local File Inclusion 漏洞描述 D-Link routers DWR-116 through 1.06, DIR-140L through 1.02, DIR-640L through 1.02,DWR-512 through 2.02,DWR-7...
 2018年1月17日 13:21
CVE-2020-8512: IceWarp WebMail Server <=11.4.4.1 - Cross-Site Scripting
漏洞标题 CVE-2020-8512: IceWarp WebMail Server <=11.4.4.1 - Cross-Site Scripting 漏洞描述 IceWarp Webmail Server through 11.4.4.1 contains a cross-site scripting vulnerability i...
2020年8月25日 05:13copyparty 低于1.8.2 版本存在任意文件读取漏洞(CVE-2023-37474)
漏洞标题 copyparty 低于1.8.2 版本存在任意文件读取漏洞(CVE-2023-37474) 漏洞描述 Copyparty是一个便携式文件服务器,copyparty 低于1.8.2 版本存在任意文件读取漏洞 PoC代码 暂无
2023年1月10日 18:43CVE-2020-24391: Mongo-Express – Remote Code Execution
漏洞标题 CVE-2020-24391: Mongo-Express - Remote Code Execution 漏洞描述 Mongo-Express before 1.0.0 is susceptible to remote code execution because it uses safer-eval to validate us...
2020年11月10日 00:12CVE-2023-26255: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion
漏洞标题 CVE-2023-26255: STAGIL Navigation for Jira Menu & Themes <2.0.52 - Local File Inclusion 漏洞描述 STAGIL Navigation for Jira Menu & Themes plugin before 2.0.52 i...
2023年1月8日 22:59CVE-2023-1317: osTicket < v1.16.6 - Cross-Site Scripting
漏洞标题 CVE-2023-1317: osTicket < v1.16.6 - Cross-Site Scripting 漏洞描述 Cross-site Scripting (XSS) - Reflected in GitHub repository osticket/osticket prior to v1.16.6. PoC代...
2023年7月22日 22:55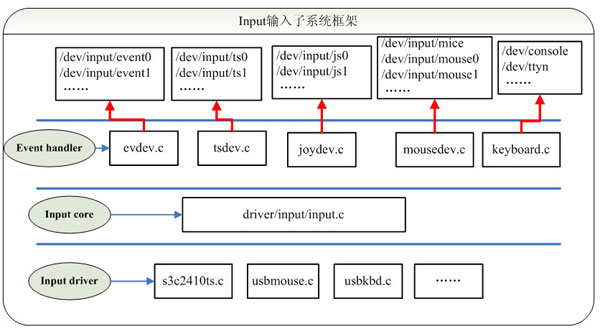
Linux输入子系统框架原理解析_Linux
这篇文章主要介绍了Linux输入子系统框架原理解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 input输入子系统框架 linux输入子系统(l...
2023年5月19日 20:10CVE-2018-7314: Joomla! Component PrayerCenter 3.0.2 – SQL Injection
漏洞标题 CVE-2018-7314: Joomla! Component PrayerCenter 3.0.2 - SQL Injection 漏洞描述 SQL Injection exists in the PrayerCenter 3.0.2 component for Joomla! via the sessionid paramet...
2018年9月10日 13:53CVE-2010-1340: Joomla! Component com_jresearch – ‘Controller’ Local File Inclusion
漏洞标题 CVE-2010-1340: Joomla! Component com_jresearch - 'Controller' Local File Inclusion 漏洞描述 A directory traversal vulnerability in jresearch.php in the J!Researc...
2010年5月13日 17:21
全球业务关闭,年收入百亿物流公司Expeditors遭受网络攻击
物流和货运代理巨头Expeditors International是总部位于美国西雅图的财富500强公司,在 100 多个国家和地区拥有上万名员工,去年年收入超过百亿。上周日,Expeditors宣布确认了一起网络攻击事件...
2022年3月10日 23:40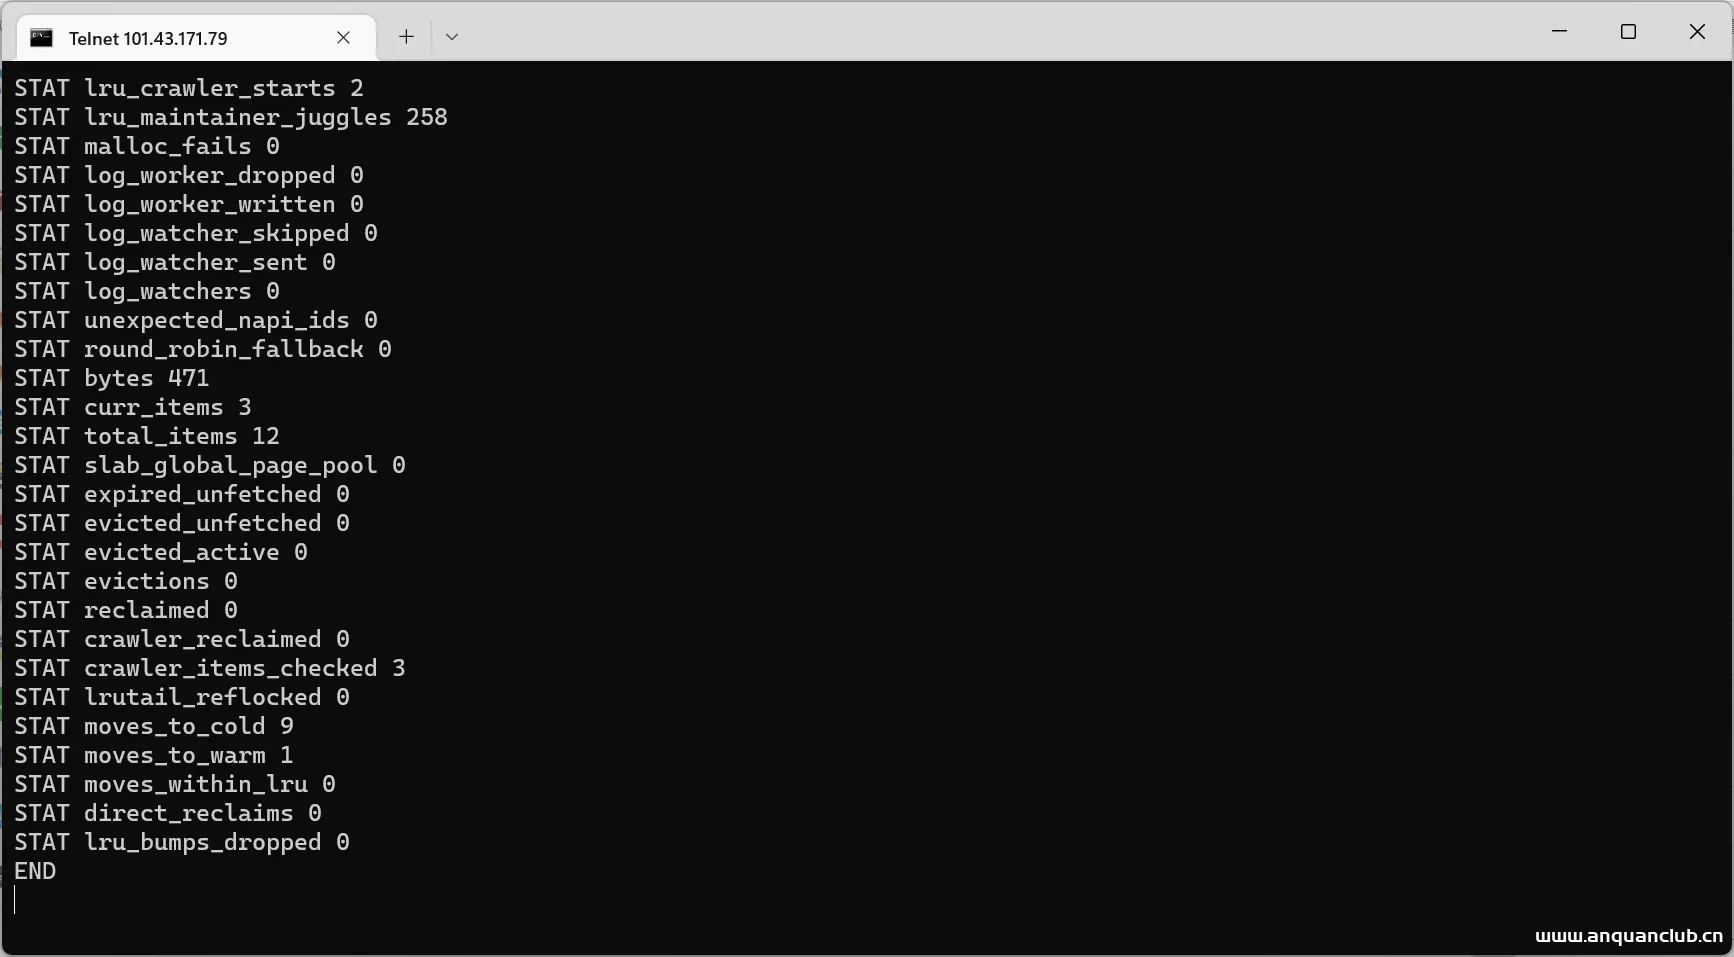
linux memcached未授权访问漏洞,Memcache未授权访问漏洞利用及修复
漏洞简介 漏洞名称:Memcache未授权访问漏洞 漏洞描述:memcache未授权访问漏洞,默认的 11211 端口不需要密码即可访问,攻击者可获取数据库中信息,造成严重的信息泄露。 漏洞成因:由于memcac...

 2023年1月13日 19:07

每日云安全技术资讯20220222
绿盟云原生安全研究仓库 http://github.com/Metarget/ 红蓝对抗中的云原生漏洞挖掘及利用实录 http://security.tencent.com/index.php/blog/msg/183 浅谈云安全之K8S http://www.anquanke.com/p...
2022年3月10日 23:32CVE-2022-48166: Wavlink WL-WN530HG4 M30HG4.V5030.201217 – Information Disclosure
漏洞标题 CVE-2022-48166: Wavlink WL-WN530HG4 M30HG4.V5030.201217 - Information Disclosure 漏洞描述 An access control issue in Wavlink WL-WN530HG4 M30HG4.V5030.201217 allows unauthe...
2022年6月13日 21:53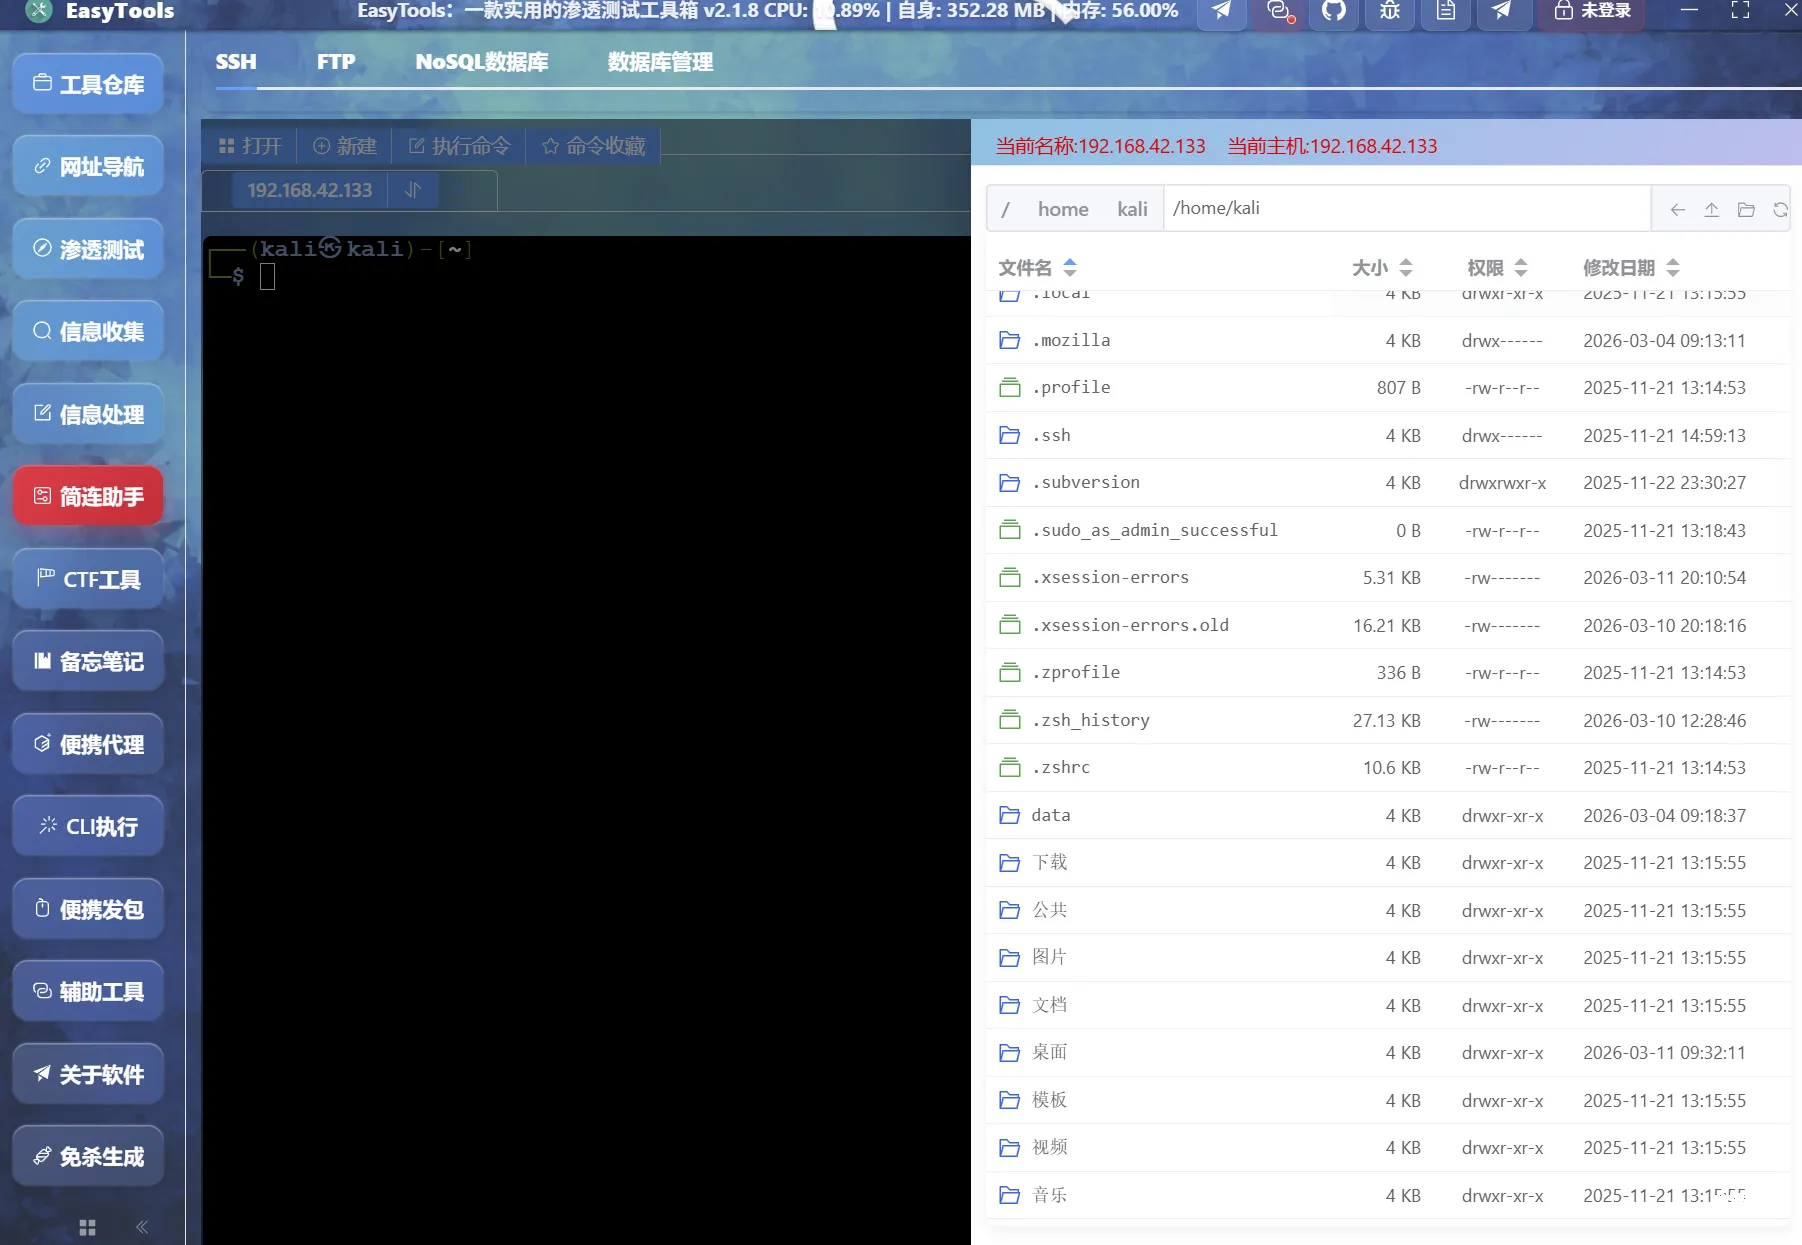
EasyTools渗透测试工具箱V2.1.8更新(1.优化端口扫描规则,提高扫描效率; 2.重新设计ssh、ftp界面; 3.优化各数据库数据展示)
前言 最近在使用简练助手的时间发现ssh文件管理不是很舒服,然后顺手更新一波简练助手模块,在此汇报一下更新变化: 优化端口扫描规则,提高扫描效率; 重新设计ssh、ftp界面,优化上传下载逻辑;...
2026年3月15日 12:27CVE-2021-33690: SAP NetWeaver Development Infrastructure – Server Side Request Forgery
漏洞标题 CVE-2021-33690: SAP NetWeaver Development Infrastructure - Server Side Request Forgery 漏洞描述 Server-Side Request Forgery (SSRF) vulnerability has been detected in the S...
2021年8月11日 22:10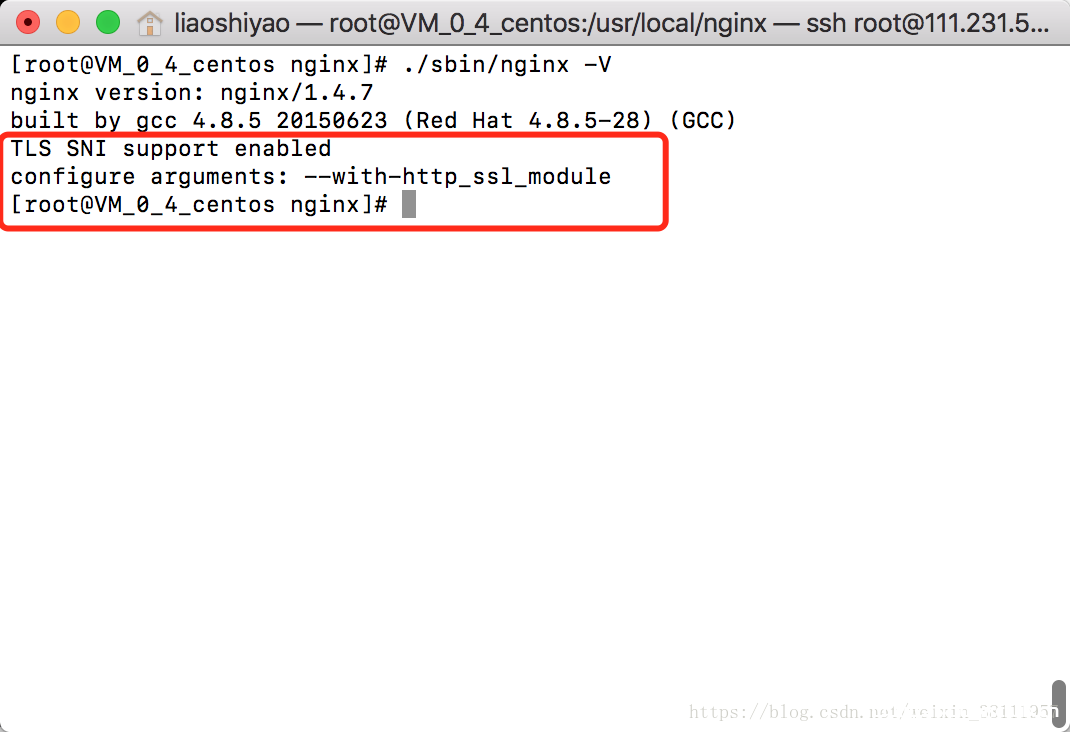
Nginx配置SSL证书出错解决方案_nginx
这篇文章主要介绍了Nginx配置SSL证书出错解决方案,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、引言 当我们的Linux服务器上当中发...
2022年12月29日 20:28
2026年9月18日 11:46
2026年9月17日 18:46
2026年9月17日 11:45
2026年9月16日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月17日 18:19
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

