
最新发布第234页

CVE-2022-22965: Spring – Remote Code Execution
漏洞标题 CVE-2022-22965: Spring - Remote Code Execution 漏洞描述 Spring MVC and Spring WebFlux applications running on Java Development Kit 9+ are susceptible to remote code execut...
 2022年7月5日 14:34
CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution
漏洞标题 CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution 漏洞描述 CloudPanel 2 before 2.3.1 has insecure file-manager cookie authentication. PoC代码
2023年3月1日 20:58CVE-2023-32315-2: Openfire身份认证绕过漏洞
漏洞标题 CVE-2023-32315-2: Openfire身份认证绕过漏洞 漏洞描述 Openfire is an XMPP server licensed under the Open Source Apache License. Openfire's administrative console, a web...
2023年9月26日 00:09
nginx如何将http访问的网站改成https访问_nginx
这篇文章主要介绍了nginx如何将http访问的网站改成https访问,帮助大家更好的理解和使用nginx,感兴趣的朋友可以了解下 目录1. 背景2. 预备知识https:证书体系:3. 操作过程3.1 证书生成3.2 ng...
2022年10月4日 20:14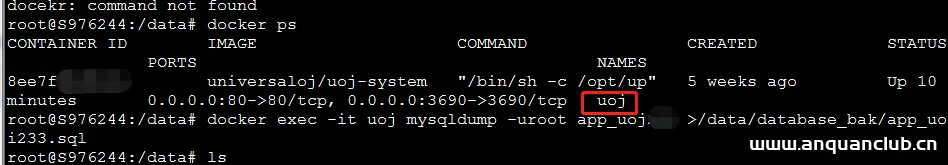
docker 使用mysqldump命令备份导出项目中的mysql数据_docker
这篇文章主要介绍了docker 使用mysqldump命令备份导出项目中的mysql数据本文通过命令给大家介绍的非常详细,具有一定的参考借鉴价值,需要的朋友可以参考下 mysqldump命令 介绍:一个数据库备份...
2026年5月18日 11:45CVE-2024-8877: Riello Netman 204 – SQL Injection
漏洞标题 CVE-2024-8877: Riello Netman 204 - SQL Injection 漏洞描述 The three endpoints /cgi-bin/db_datalog_w.cgi, /cgi-bin/db_eventlog_w.cgi, and /cgi-bin/db_multimetr_w.cgi are vu...
2024年12月17日 14:34CVE-2023-29919: SolarView Compact <= 6.00 - Local File Inclusion
漏洞标题 CVE-2023-29919: SolarView Compact <= 6.00 - Local File Inclusion 漏洞描述 There is an arbitrary read file vulnerability in SolarView Compact 6.00 and below, attackers c...
2023年4月20日 02:46CVE-2020-36708: WordPress Epsilon Framework Themes <=2.4.8 - Remote Code Execution
漏洞标题 CVE-2020-36708: WordPress Epsilon Framework Themes <=2.4.8 - Remote Code Execution 漏洞描述 WordPress themes including Shapely <= 1.2.7, NewsMag <= 2.4.1, Activel...
2020年7月23日 01:37CVE-2022-2187: WordPress Contact Form 7 Captcha <0.1.2 - Cross-Site Scripting
漏洞标题 CVE-2022-2187: WordPress Contact Form 7 Captcha <0.1.2 - Cross-Site Scripting 漏洞描述 WordPress Contact Form 7 Captcha plugin before 0.1.2 contains a reflected cross-s...
2022年12月13日 20:45bugbounty技巧聚合20210818
漏洞报告 MTN Grou #1060518 No rate limit in otp code sending Mail.ru #1255676 Blind XSS Stored and CORS misconfiguration в отчете 'События' сервиса top.mail.ru...
2022年3月10日 23:32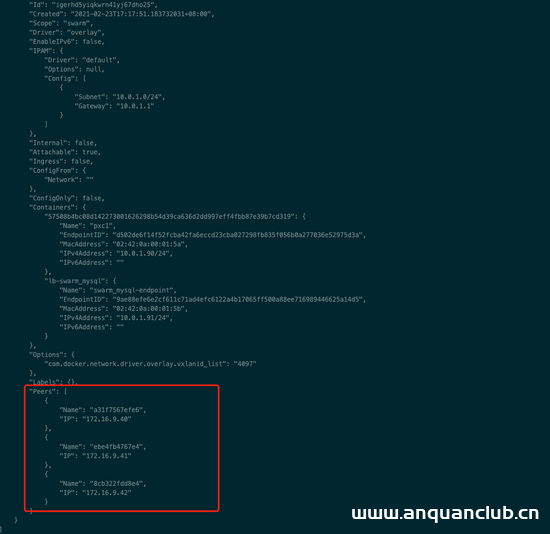
docker安装pxc集群的详细教程_docker
这篇文章主要介绍了docker安装pxc集群的详细教程,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录前言前期准备创建目录创建custom.cnf创建cer...
2022年9月17日 10:40Adobe ColdFusion-任意文件读取(CVE-2010-2861)
漏洞标题 Adobe ColdFusion-任意文件读取(CVE-2010-2861) 漏洞描述 【漏洞对象】Adobe ColdFusion 【涉及版本】9,9.0.1,9.0.2 【漏洞描述】 Adobe ColdFusion8、9版本中存在一处目录穿越漏洞...
2010年8月31日 10:09CVE-2021-46071: ehicle Service Management System 1.0 – Cross-Site Scripting
漏洞标题 CVE-2021-46071: ehicle Service Management System 1.0 - Cross-Site Scripting 漏洞描述 Vehicle Service Management System 1.0 contains a stored cross-site scripting vulnerabi...
2021年3月29日 19:12CVE-2024-32735: CyberPower – Missing Authentication
漏洞标题 CVE-2024-32735: CyberPower - Missing Authentication 漏洞描述 An issue regarding missing authentication for certain utilities exists in CyberPower PowerPanel Enterprise pri...
2024年10月12日 22:09CVE-2020-29583: ZyXel USG – Hardcoded Credentials
漏洞标题 CVE-2020-29583: ZyXel USG - Hardcoded Credentials 漏洞描述 A hardcoded credential vulnerability was identified in the 'zyfwp' user account in some Zyxel firewall...
2020年12月5日 13:14bugbounty技巧聚合20220211
漏洞报告 自动填充导致信息泄露1900$ http://hackerone.com/reports/1083922 垂直越权 800$ http://hackerone.com/reports/1392032 Spring Boot信息泄露 5000$ http://hackerone.com/reports/10...
2022年3月10日 23:32
2026年11月11日 11:45
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

