
最新发布第252页
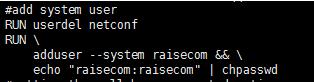
使用docker更改容器内root密码的操作_docker
这篇文章主要介绍了使用docker更改容器内root密码的操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 1.在制作dockerfile的时候使用如下命令设置ssh密码 RUN echo “root...
 2022年6月28日 20:47

CVE-2023-23492: Login with Phone Number – Cross-Site Scripting
漏洞标题 CVE-2023-23492: Login with Phone Number - Cross-Site Scripting 漏洞描述 Login with Phone Number, versions < 1.4.2, is affected by an reflected XSS vulnerability in the ...
2023年5月19日 10:09CVE-2015-3035: TP-LINK – Local File Inclusion
漏洞标题 CVE-2015-3035: TP-LINK - Local File Inclusion 漏洞描述 TP-LINK is susceptible to local file inclusion in these products: Archer C5 (1.2) with firmware before 150317, Arche...
2015年9月2日 12:08Atlassian Jira 模板注入漏洞(CVE-2019-11581)
漏洞标题 Atlassian Jira 模板注入漏洞(CVE-2019-11581) 漏洞描述 Atlassian JIRA Server和JIRA Data Center中存在安全漏洞。多个版本受到影响。 PoC代码 暂无
2019年12月6日 17:57CVE-2025-3102: SureTriggers – All-in-One Automation Platform ≤ 1.0.78 – Authentication Bypass
漏洞标题 CVE-2025-3102: SureTriggers – All-in-One Automation Platform ≤ 1.0.78 - Authentication Bypass 漏洞描述 The SureTriggers- All-in-One Automation Platform plugin for WordPr...
2025年1月6日 23:04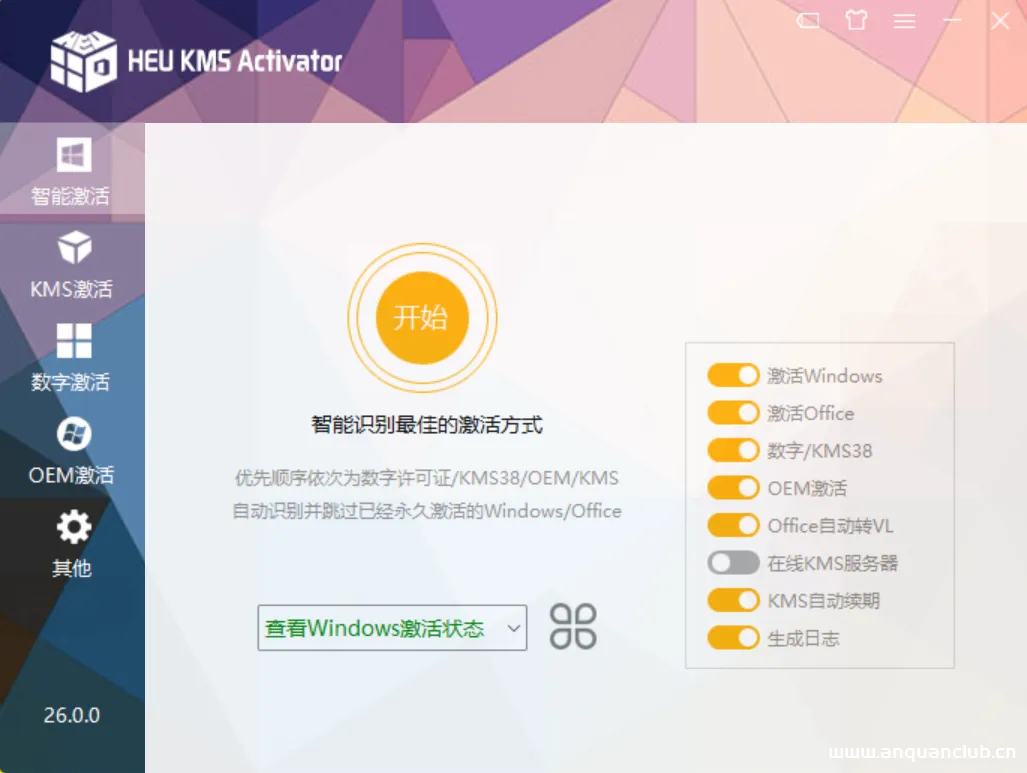
Windows激活工具下载 使用教程
应用价绍 HEU KMS Activator,简洁高效的全能KMS/OEM激活工具,适用所有Windows, Office版本,无需联网即可一键激活,支持UEFI的KMS激活工具。KMS服务是微软对Windows, Office等产品的批量许可...

 2023年1月13日 19:24
CVE-2010-1954: Joomla! Component iNetLanka Multiple root 1.0 – Local File Inclusion
漏洞标题 CVE-2010-1954: Joomla! Component iNetLanka Multiple root 1.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the iNetLanka Multiple root (com_multir...
2010年11月4日 22:13Cisco RV132W RV134W 路由器信息泄露(CVE-2018-0127)
漏洞标题 Cisco RV132W RV134W 路由器信息泄露(CVE-2018-0127) 漏洞描述 Cisco RV132W ADSL2+Wireless-N VPN路由器和Cisco RV134W VDSL2 Wireless ACVPN路由器的web界面中存在漏洞,使得未经验...
2018年11月14日 09:39Aspera Faspex CVE-2022-47986 远程代码执行漏洞
漏洞标题 Aspera Faspex CVE-2022-47986 远程代码执行漏洞 漏洞描述 Aspera Faspex CVE-2022-47986 远程 PoC代码 暂无
2022年3月19日 18:48CVE-2023-4415: Ruijie RG-EW1200G Router Background – Login Bypass
漏洞标题 CVE-2023-4415: Ruijie RG-EW1200G Router Background - Login Bypass 漏洞描述 A vulnerability was found in Ruijie RG-EW1200G 07161417 r483. It has been rated as critical. Aff...
2023年6月6日 04:22CVE-2020-25540: ThinkAdmin 6 – Local File Inclusion
漏洞标题 CVE-2020-25540: ThinkAdmin 6 - Local File Inclusion 漏洞描述 ThinkAdmin version 6 is affected by a local file inclusion vulnerability because an unauthorized attacker can ...
2020年9月6日 14:42CVE-2023-6549: Citrix Netscaler ADC & Gateway – Out-Of-Bounds Memory Read
漏洞标题 CVE-2023-6549: Citrix Netscaler ADC & Gateway - Out-Of-Bounds Memory Read 漏洞描述 The vulnerability would enable an attacker to remotely obtain sensitive information ...
2023年5月15日 10:30CVE-2024-1183: Gradio – Server Side Request Forgery
漏洞标题 CVE-2024-1183: Gradio - Server Side Request Forgery 漏洞描述 An SSRF (Server-Side Request Forgery) vulnerability exists in the gradio-app/gradio repository, allowing attac...
2024年6月19日 21:51CVE-2024-3850: Uniview NVR301-04S2-P4 – Cross-Site Scripting
漏洞标题 CVE-2024-3850: Uniview NVR301-04S2-P4 - Cross-Site Scripting 漏洞描述 Uniview NVR301-04S2-P4 contains a reflected cross-site scripting vulnerability via the PATH of LAPI. ...
2024年11月20日 11:30CVE-2015-2068: Magento Server Mass Importer – Cross-Site Scripting
漏洞标题 CVE-2015-2068: Magento Server Mass Importer - Cross-Site Scripting 漏洞描述 Magento Server Mass Importer plugin contains multiple cross-site scripting vulnerabilities whic...
2015年1月1日 15:28CVE-2010-1607: Joomla! Component WMI 1.5.0 – Local File Inclusion
漏洞标题 CVE-2010-1607: Joomla! Component WMI 1.5.0 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in wmi.php in the Webmoney Web Merchant Interface (aka WMI o...
2010年4月21日 22:06
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
2026年11月3日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

