
最新发布第252页
匿名者泄露雀巢10GB敏感数据,作为其仍在俄罗斯运营的惩罚
3月22日,匿名者黑客组织在推特账户上发布了瑞士饮品和食品巨头雀巢公司的一份数据库,约有10GB敏感数据泄露,包括公司电子邮件、密码,以及与商业客户相关的数据。同时,匿名者黑客组织还呼吁...
 2022年3月27日 14:55

CVE-2018-19386: SolarWinds Database Performance Analyzer 11.1.457 – Cross-Site Scripting
漏洞标题 CVE-2018-19386: SolarWinds Database Performance Analyzer 11.1.457 - Cross-Site Scripting 漏洞描述 SolarWinds Database Performance Analyzer 11.1.457 contains a reflected cr...
2018年6月8日 06:21CVE-2025-20281: Cisco ISE – Remote Code Execution
漏洞标题 CVE-2025-20281: Cisco ISE - Remote Code Execution 漏洞描述 A vulnerability in a specific API of Cisco ISE and Cisco ISE-PIC could allow an unauthenticated, remote attacker...
2025年10月12日 07:56CVE-2021-36888: WordPress Image Hover Ultimate – Unauthenticated Settings Update
漏洞标题 CVE-2021-36888: WordPress Image Hover Ultimate - Unauthenticated Settings Update 漏洞描述 Unauthenticated Arbitrary Options Update vulnerability leading to full website co...
2021年6月15日 03:18CVE-2020-24391: Mongo-Express – Remote Code Execution
漏洞标题 CVE-2020-24391: Mongo-Express - Remote Code Execution 漏洞描述 Mongo-Express before 1.0.0 is susceptible to remote code execution because it uses safer-eval to validate us...
2020年6月12日 17:20CVE-2019-0604: Microsoft SharePoint – Remote Code Execution
漏洞标题 CVE-2019-0604: Microsoft SharePoint - Remote Code Execution 漏洞描述 Microsoft SharePoint contains a remote code execution caused by failure to check the source markup of ...
2019年3月31日 07:34CVE-2020-14181: Jira Server and Data Center – Information Disclosure
漏洞标题 CVE-2020-14181: Jira Server and Data Center - Information Disclosure 漏洞描述 Jira Server and Data Center is susceptible to information disclosure. An attacker can enumera...
2020年9月7日 18:44CVE-2025-46822: Java-springboot-codebase 1.1 – Arbitrary File Read
漏洞标题 CVE-2025-46822: Java-springboot-codebase 1.1 - Arbitrary File Read 漏洞描述 OsamaTaher/Java-springboot-codebase is a collection of Java and Spring Boot code snippets, appl...
2025年6月8日 01:17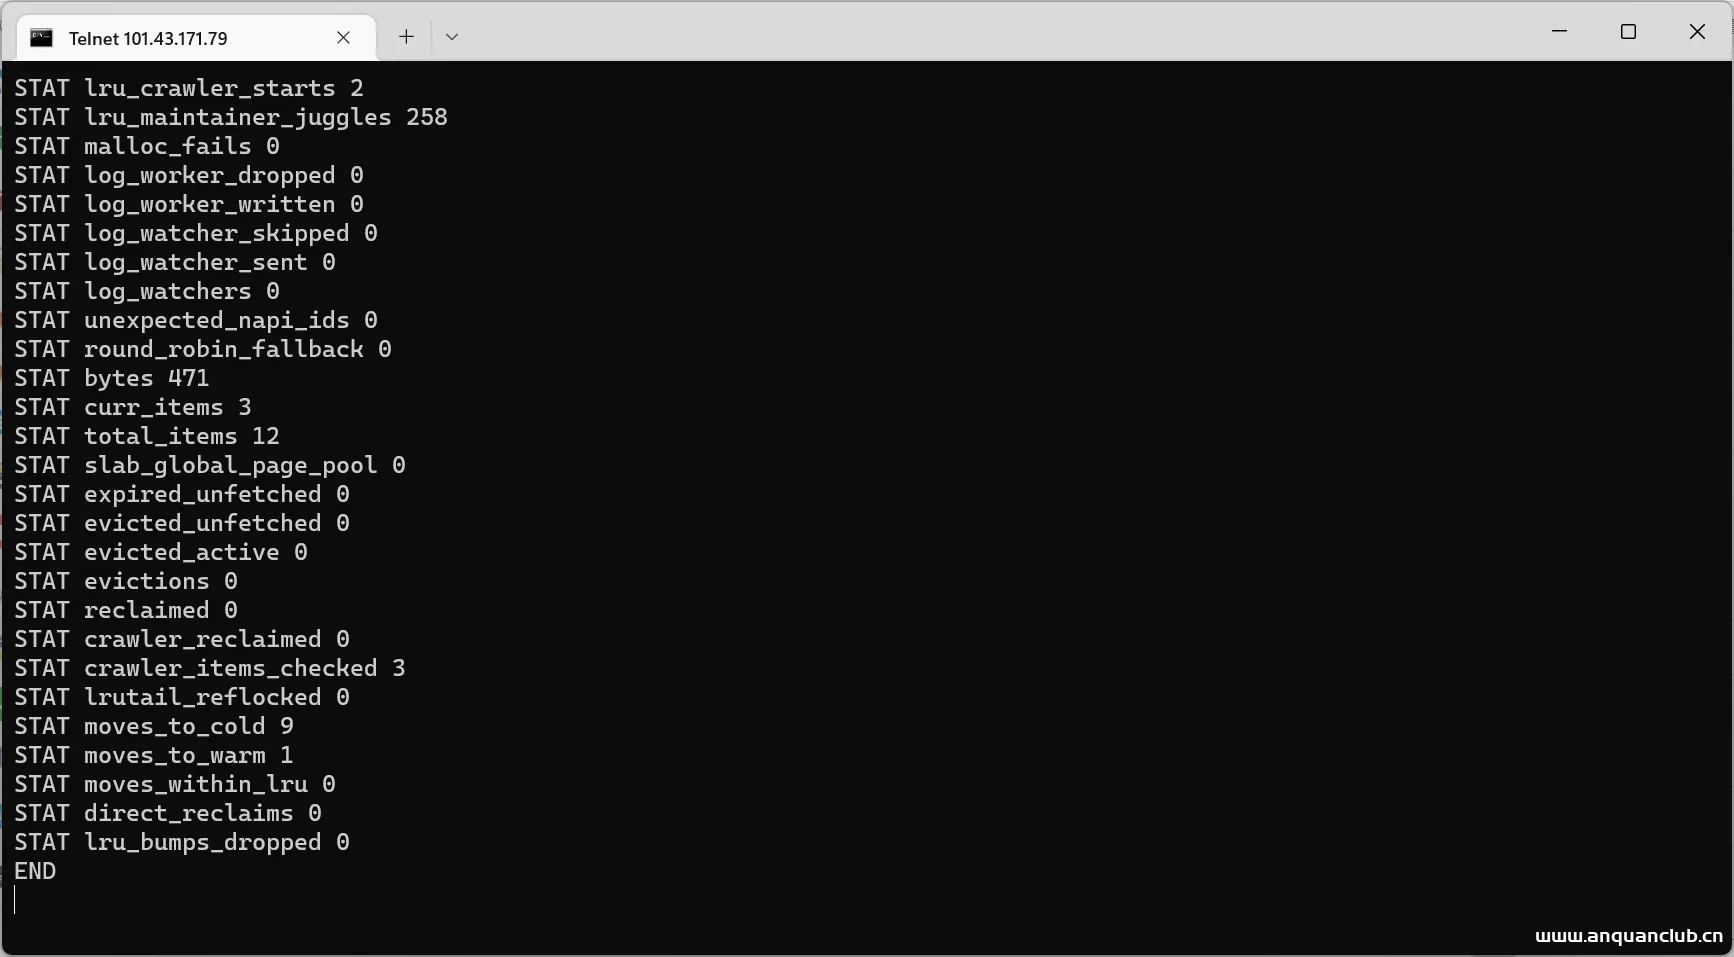
linux memcached未授权访问漏洞,Memcache未授权访问漏洞利用及修复
漏洞简介 漏洞名称:Memcache未授权访问漏洞 漏洞描述:memcache未授权访问漏洞,默认的 11211 端口不需要密码即可访问,攻击者可获取数据库中信息,造成严重的信息泄露。 漏洞成因:由于memcac...

 2023年1月13日 19:07
Apache Airflow CVE-2022-24288 命令注入漏洞
漏洞标题 Apache Airflow CVE-2022-24288 命令注入漏洞 漏洞描述 Apache Airflow存在命令注入漏洞,此漏洞是缺乏校验导致的。 PoC代码 暂无
2022年6月21日 21:22CVE-2021-44077: Zoho ManageEngine ServiceDesk Plus – Remote Code Execution
漏洞标题 CVE-2021-44077: Zoho ManageEngine ServiceDesk Plus - Remote Code Execution 漏洞描述 Zoho ManageEngine ServiceDesk Plus before 11306, ServiceDesk Plus MSP before 10530, and...
2021年4月9日 07:59CVE-2021-24750: WordPress Visitor Statistics (Real Time Traffic) <4.8 -SQL Injection
漏洞标题 CVE-2021-24750: WordPress Visitor Statistics (Real Time Traffic) <4.8 -SQL Injection 漏洞描述 WordPress Visitor Statistics (Real Time Traffic) plugin before 4.8 does no...
2021年3月24日 21:42CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection
漏洞标题 CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection 漏洞描述 In the latest version (2.8.2 as of writing the article) and below, the plugin...
2024年5月19日 09:05CVE-2025-24514: Ingress-Nginx Controller – Configuration Injection via Unsanitized `auth-url` Annotation
漏洞标题 CVE-2025-24514: Ingress-Nginx Controller - Configuration Injection via Unsanitized `auth-url` Annotation 漏洞描述 A security issue was discovered in ingress-nginx https-//...
2025年6月13日 22:00CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion
漏洞标题 CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion 漏洞描述 Suprema BioStar before 2.8.2 Video Extension allows remote attackers can read arbitrary files fro...
2020年7月26日 09:51CVE-2020-0618: Microsoft SQL Server Reporting Services – Remote Code Execution
漏洞标题 CVE-2020-0618: Microsoft SQL Server Reporting Services - Remote Code Execution 漏洞描述 Microsoft SQL Server Reporting Services is vulnerable to a remote code execution vu...
2020年9月25日 23:49
2026年11月11日 11:45
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

