
最新发布第253页

CVE-2020-5405: Spring Cloud Config – Local File Inclusion
漏洞标题 CVE-2020-5405: Spring Cloud Config - Local File Inclusion 漏洞描述 Spring Cloud Config versions 2.2.x prior to 2.2.2, 2.1.x prior to 2.1.7, and older unsupported versions ...
 2020年4月20日 03:35
CVE-2022-0651: WordPress Plugin WP Statistics <= 13.1.5 - SQL Injection
漏洞标题 CVE-2022-0651: WordPress Plugin WP Statistics <= 13.1.5 - SQL Injection 漏洞描述 The WP Statistics WordPress plugin is vulnerable to SQL Injection due to insufficient e...
2022年5月9日 13:01CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta – Arbitrary File Upload
漏洞标题 CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta - Arbitrary File Upload 漏洞描述 Unrestricted file upload vulnerability in includes/up...
2015年3月21日 15:14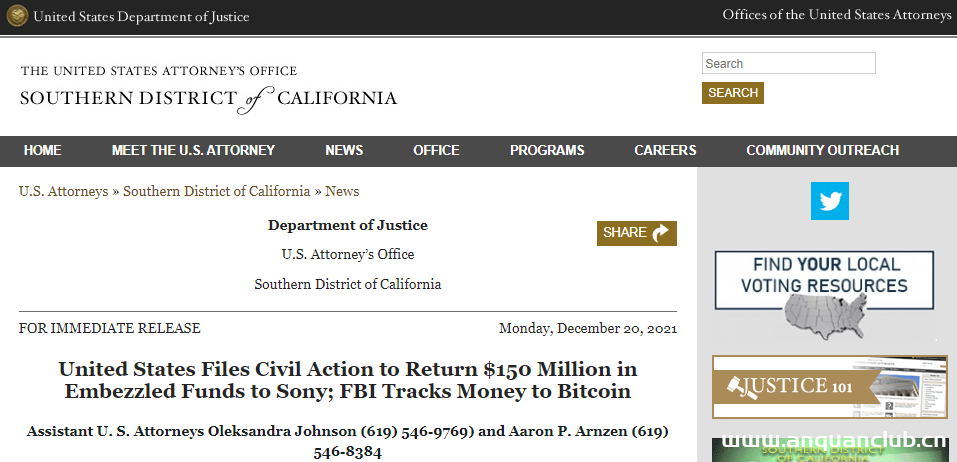
美国扣押并归还索尼1.54亿美元被盗资金
12月20日,美国司法部发布了一则新闻,称美国已采取行动,保护并最终归还了索尼超过1.54亿美元的资金,这些资金据称是索尼人寿保险股份有限公司(下称索尼人寿)内部一名员工窃取的。 根据...
2022年3月10日 23:39
docker比赛提交常用命令小结_docker
这篇文章主要介绍了docker比赛提交常用命令小结,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 登录账户 export DOCKER_REGISTRY=registry.cn-ha...
2022年9月19日 20:54
越权测试小技巧
越权测试小技巧 /v2/user/1234 ---> 401 Unauthorized 绕过小技巧 大写绕过 /v2/USER/1234 ---> 200 OK 添加json后缀绕过 /v2/user/1234.json ----> 200 OK 路径穿越绕过 /v2/user/111...
2022年3月10日 23:37CVE-2025-1562: Recover WooCommerce Cart Abandonment, Newsletter, Email Marketing, Marketing Automation By FunnelKit – Broken Access Control
漏洞标题 CVE-2025-1562: Recover WooCommerce Cart Abandonment, Newsletter, Email Marketing, Marketing Automation By FunnelKit - Broken Access Control 漏洞描述 The Recover WooCommerc...
2025年4月25日 18:42CVE-2023-27639: PrestaShop TshirteCommerce – Directory Traversal
漏洞标题 CVE-2023-27639: PrestaShop TshirteCommerce - Directory Traversal 漏洞描述 The Custom Product Designer (tshirtecommerce) module for PrestaShop allows HTTP requests to be fo...
2023年5月17日 03:10CVE-2022-0412: WordPress TI WooCommerce Wishlist <1.40.1 - SQL Injection
漏洞标题 CVE-2022-0412: WordPress TI WooCommerce Wishlist <1.40.1 - SQL Injection 漏洞描述 WordPress TI WooCommerce Wishlist plugin before 1.40.1 contains a SQL injection vulner...
2022年8月28日 22:35
平台某项目-服务器SSH密钥与日志和命令记录泄露
对于特殊的路径,我比较喜欢收集,然后批量扫子域名,来获取到敏感信息,在之前的渗透里面,机缘巧合下,拿到了一次最贵的信息泄露的漏洞 路径链接如下 /.bashrc 个人配置记录 /.ssh/authorized...
2022年3月10日 23:34CVE-2021-24215: Controlled Admin Access WordPress Plugin <= 1.4.0 - Improper Access Control & Privilege Escalation
漏洞标题 CVE-2021-24215: Controlled Admin Access WordPress Plugin <= 1.4.0 - Improper Access Control & Privilege Escalation 漏洞描述 An Improper Access Control vulnerability...
2021年12月17日 06:57CVE-2008-7269: UC Gateway Investment SiteEngine v5.0 – Open Redirect
漏洞标题 CVE-2008-7269: UC Gateway Investment SiteEngine v5.0 - Open Redirect 漏洞描述 Open redirect vulnerability in api.php in SiteEngine 5.x allows user-assisted remote attacker...
2008年8月18日 06:47CVE-2008-6982: Devalcms 1.4a – Cross-Site Scripting
漏洞标题 CVE-2008-6982: Devalcms 1.4a - Cross-Site Scripting 漏洞描述 Devalcms 1.4a contains a cross-site scripting vulnerability in the currentpath parameter of the index.php file...
2008年4月18日 01:50CVE-2008-1061: WordPress Sniplets <=1.2.2 - Cross-Site Scripting
漏洞标题 CVE-2008-1061: WordPress Sniplets <=1.2.2 - Cross-Site Scripting 漏洞描述 WordPress Sniplets 1.1.2 and 1.2.2 plugin contains a cross-site scripting vulnerability which ...
2008年2月26日 23:58CVE-2023-40931: Nagios XI v5.11.0 – SQL Injection
漏洞标题 CVE-2023-40931: Nagios XI v5.11.0 - SQL Injection 漏洞描述 A SQL injection vulnerability in Nagios XI from version 5.11.0 up to and including 5.11.1 allows authenticated a...
2023年11月29日 23:13CVE-2025-31125: Vite Development Server – Path Traversal
漏洞标题 CVE-2025-31125: Vite Development Server - Path Traversal 漏洞描述 Path traversal vulnerability in Vite development server's @fs endpoint allows attackers to access fi...
2025年12月30日 11:00
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
2026年11月3日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

