
最新发布第254页

CVE-2024-8859: Mlflow < 2.17.0 - Local File Inclusion
漏洞标题 CVE-2024-8859: Mlflow < 2.17.0 - Local File Inclusion 漏洞描述 Mlflow before 2.17.0 is susceptible to local file inclusion due to path traversal in GitHub repository ml...
 2024年4月10日 00:21
CVE-2004-1602: ProFTPD 1.2.x – Username Enumeration via Timing Attack
漏洞标题 CVE-2004-1602: ProFTPD 1.2.x - Username Enumeration via Timing Attack 漏洞描述 ProFTPD versions 1.2.x (including 1.2.8 and 1.2.10) are vulnerable to timing attacks that al...
2004年8月26日 09:19CVE-2025-2746: Kentico Xperience 13 CMS – Staging Service Authentication Bypass (WT-2025-0011)
漏洞标题 CVE-2025-2746: Kentico Xperience 13 CMS - Staging Service Authentication Bypass (WT-2025-0011) 漏洞描述 Before Kentico Xperience 13 Hotfix 173, this vulnerability can be e...
2025年2月8日 23:11CVE-2004-0656: Pure-FTPd ≤ 1.0.18 – DoS via Connection Limit Exhaustion
漏洞标题 CVE-2004-0656: Pure-FTPd ≤ 1.0.18 - DoS via Connection Limit Exhaustion 漏洞描述 Pure-FTPd versions ≤ 1.0.18 are vulnerable to denial of service through connection limit...
2004年7月7日 14:07CVE-2020-5405: Spring Cloud Config – Local File Inclusion
漏洞标题 CVE-2020-5405: Spring Cloud Config - Local File Inclusion 漏洞描述 Spring Cloud Config versions 2.2.x prior to 2.2.2, 2.1.x prior to 2.1.7, and older unsupported versions ...
2020年4月20日 03:35CVE-2022-0651: WordPress Plugin WP Statistics <= 13.1.5 - SQL Injection
漏洞标题 CVE-2022-0651: WordPress Plugin WP Statistics <= 13.1.5 - SQL Injection 漏洞描述 The WP Statistics WordPress plugin is vulnerable to SQL Injection due to insufficient e...
2022年5月9日 13:01CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta – Arbitrary File Upload
漏洞标题 CVE-2015-4455: WordPress Plugin Aviary Image Editor Addon For Gravity Forms 3.0 Beta - Arbitrary File Upload 漏洞描述 Unrestricted file upload vulnerability in includes/up...
2015年3月21日 15:14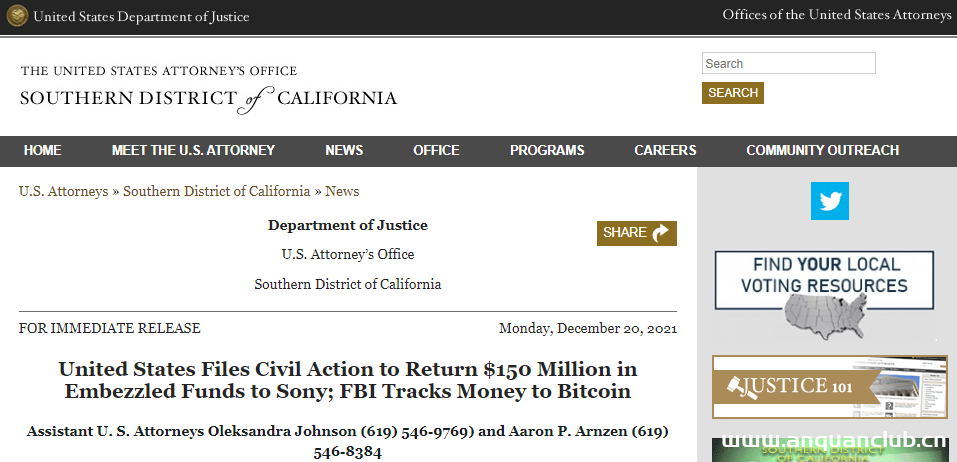
美国扣押并归还索尼1.54亿美元被盗资金
12月20日,美国司法部发布了一则新闻,称美国已采取行动,保护并最终归还了索尼超过1.54亿美元的资金,这些资金据称是索尼人寿保险股份有限公司(下称索尼人寿)内部一名员工窃取的。 根据...
2022年3月10日 23:39
越权测试小技巧
越权测试小技巧 /v2/user/1234 ---> 401 Unauthorized 绕过小技巧 大写绕过 /v2/USER/1234 ---> 200 OK 添加json后缀绕过 /v2/user/1234.json ----> 200 OK 路径穿越绕过 /v2/user/111...
2022年3月10日 23:37CVE-2025-1562: Recover WooCommerce Cart Abandonment, Newsletter, Email Marketing, Marketing Automation By FunnelKit – Broken Access Control
漏洞标题 CVE-2025-1562: Recover WooCommerce Cart Abandonment, Newsletter, Email Marketing, Marketing Automation By FunnelKit - Broken Access Control 漏洞描述 The Recover WooCommerc...
2025年4月25日 18:42CVE-2023-27639: PrestaShop TshirteCommerce – Directory Traversal
漏洞标题 CVE-2023-27639: PrestaShop TshirteCommerce - Directory Traversal 漏洞描述 The Custom Product Designer (tshirtecommerce) module for PrestaShop allows HTTP requests to be fo...
2023年5月17日 03:10CVE-2022-0412: WordPress TI WooCommerce Wishlist <1.40.1 - SQL Injection
漏洞标题 CVE-2022-0412: WordPress TI WooCommerce Wishlist <1.40.1 - SQL Injection 漏洞描述 WordPress TI WooCommerce Wishlist plugin before 1.40.1 contains a SQL injection vulner...
2022年8月28日 22:35
平台某项目-服务器SSH密钥与日志和命令记录泄露
对于特殊的路径,我比较喜欢收集,然后批量扫子域名,来获取到敏感信息,在之前的渗透里面,机缘巧合下,拿到了一次最贵的信息泄露的漏洞 路径链接如下 /.bashrc 个人配置记录 /.ssh/authorized...
2022年3月10日 23:34CVE-2021-24215: Controlled Admin Access WordPress Plugin <= 1.4.0 - Improper Access Control & Privilege Escalation
漏洞标题 CVE-2021-24215: Controlled Admin Access WordPress Plugin <= 1.4.0 - Improper Access Control & Privilege Escalation 漏洞描述 An Improper Access Control vulnerability...
2021年12月17日 06:57CVE-2008-7269: UC Gateway Investment SiteEngine v5.0 – Open Redirect
漏洞标题 CVE-2008-7269: UC Gateway Investment SiteEngine v5.0 - Open Redirect 漏洞描述 Open redirect vulnerability in api.php in SiteEngine 5.x allows user-assisted remote attacker...
2008年8月18日 06:47CVE-2008-6982: Devalcms 1.4a – Cross-Site Scripting
漏洞标题 CVE-2008-6982: Devalcms 1.4a - Cross-Site Scripting 漏洞描述 Devalcms 1.4a contains a cross-site scripting vulnerability in the currentpath parameter of the index.php file...
2008年4月18日 01:50
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

