
最新发布第257页

CVE-2023-29923: PowerJob <=4.3.2 - Unauthenticated Access
漏洞标题 CVE-2023-29923: PowerJob <=4.3.2 - Unauthenticated Access 漏洞描述 PowerJob V4.3.1 is vulnerable to Insecure Permissions. via the list job interface. PoC代码
 2023年4月23日 18:30
CVE-2023-41265: Qlik Sense Enterprise – HTTP Request Smuggling
漏洞标题 CVE-2023-41265: Qlik Sense Enterprise - HTTP Request Smuggling 漏洞描述 An HTTP Request Tunneling vulnerability found in Qlik Sense Enterprise for Windows for versions May...
2023年5月13日 16:30
佑友防火墙 后台命令执行漏洞
本文转载于公众号:融云攻防实验室,原文地址: 漏洞复现 佑友防火墙 后台命令执行漏洞 佑友防火墙+路由,保障您的网络更安全更稳定。弥补传统路由器因内外人数增加带来的网络延迟和不稳定问题...
2026年2月13日 12:53CVE-2023-3479: Hestiacp <= 1.7.7 - Cross-Site Scripting
漏洞标题 CVE-2023-3479: Hestiacp <= 1.7.7 - Cross-Site Scripting 漏洞描述 Cross-site Scripting (XSS) - Reflected in GitHub repository hestiacp/hestiacp prior to 1.7.8. PoC代码
2023年7月20日 11:22CVE-2021-25161: Aruba Instant Access Point (IAP) – Cross-Site Scripting
漏洞标题 CVE-2021-25161: Aruba Instant Access Point (IAP) - Cross-Site Scripting 漏洞描述 A remote cross-site scripting (xss) vulnerability was discovered in some Aruba Instant Acc...
2021年3月19日 12:05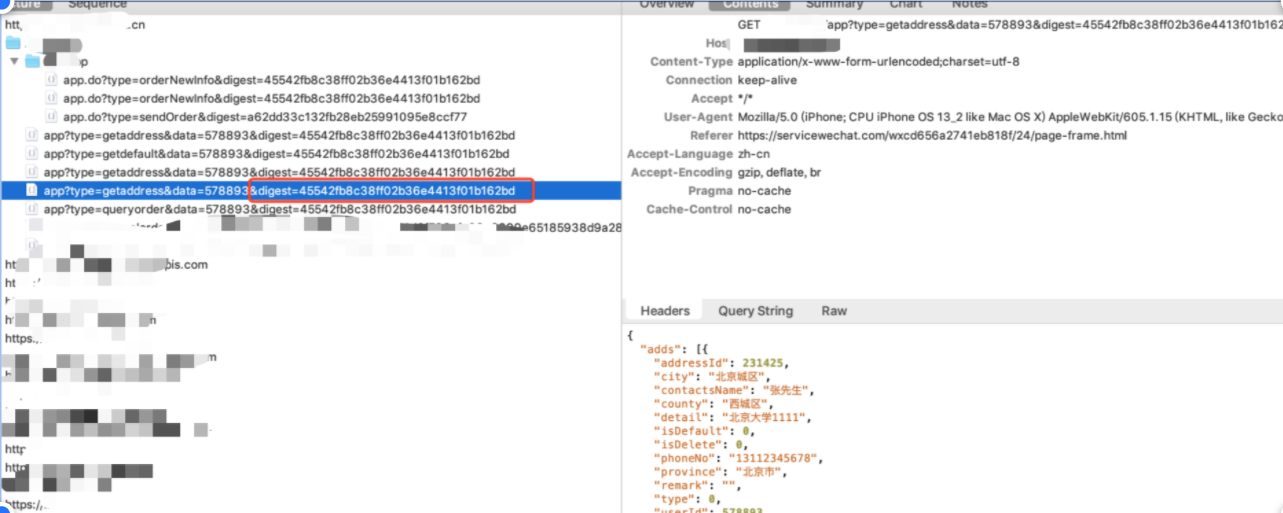
一次小程序端接口越权的分析
之前在挖一个src的时候,有一个资产是小程序 抓包如下 根据地址id查看收货地址 注意到请求里没有cookie,然后url里面这个digest字段比较奇怪,所有的接口都是根据这个参数鉴权的,一般不都应该...
2022年3月10日 23:34CVE-2020-9402: Django SQL Injection
漏洞标题 CVE-2020-9402: Django SQL Injection 漏洞描述 Django 1.11 before 1.11.29, 2.2 before 2.2.11, and 3.0 before 3.0.4 allow SQL injection if untrusted data is used as a toleran...
2020年5月22日 07:45Cartadis Gespage 8.2.1 存在目录遍历漏洞(CVE-2021-33807)
漏洞标题 Cartadis Gespage 8.2.1 存在目录遍历漏洞(CVE-2021-33807) 漏洞描述 Cartadis Gespage 8.2.1版本存在目录遍历漏洞,攻击者可利用此漏洞获取敏感信息。 PoC代码 暂无
2021年6月30日 18:33CVE-2025-1323: WP-Recall – Plugin <= 16.26.10 - Unauthenticated SQL Injection
漏洞标题 CVE-2025-1323: WP-Recall – Plugin <= 16.26.10 - Unauthenticated SQL Injection 漏洞描述 The WP-Recall – Registration, Profile, Commerce & More plugin for WordPress...
2025年10月14日 11:51CVE-2022-26148: Grafana & Zabbix Integration – Credentials Disclosure
漏洞标题 CVE-2022-26148: Grafana & Zabbix Integration - Credentials Disclosure 漏洞描述 Grafana through 7.3.4, when integrated with Zabbix, contains a credential disclosure vul...
2022年12月29日 06:47Atlassian Confluence CVE-2023-22515 权限提升漏洞 (阶段1: 属性修改)
漏洞标题 Atlassian Confluence CVE-2023-22515 权限提升漏洞 (阶段1: 属性修改) 漏洞描述 Atlassian Confluence CVE-2023-22515 权限提升漏洞 (阶段1: 属性修改) 日期: 2024-02-07 | 影响软件:...
2023年8月4日 10:39CVE-2024-2863: LG LED Assistant – Thumbnail Path Traversal File Upload
漏洞标题 CVE-2024-2863: LG LED Assistant - Thumbnail Path Traversal File Upload 漏洞描述 A path traversal vulnerability exists in the endpoint handler for /api/thumbnail in Common....
2024年9月2日 05:52CVE-2020-11930: WordPress GTranslate <2.8.52 - Cross-Site Scripting
漏洞标题 CVE-2020-11930: WordPress GTranslate <2.8.52 - Cross-Site Scripting 漏洞描述 WordPress GTranslate plugin before 2.8.52 contains an unauthenticated reflected cross-site ...
2020年10月7日 11:17CVE-2020-6308: SAP BusinessObjects Business Intelligence Platform – Blind Server-Side Request Forgery
漏洞标题 CVE-2020-6308: SAP BusinessObjects Business Intelligence Platform - Blind Server-Side Request Forgery 漏洞描述 SAP BusinessObjects Business Intelligence Platform (Web Serv...
2020年11月16日 00:55CVE-2021-36260: Hikvision IP camera/NVR – Remote Command Execution
漏洞标题 CVE-2021-36260: Hikvision IP camera/NVR - Remote Command Execution 漏洞描述 Certain Hikvision products contain a command injection vulnerability in the web server due to t...
2021年5月18日 19:16CVE-2024-24328: TotoLink Router setMacFilterRules – Command Injection
漏洞标题 CVE-2024-24328: TotoLink Router setMacFilterRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vulner...
2024年2月2日 07:54
2026年11月7日 11:45
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

