
最新发布第263页

CVE-2023-44353: Adobe ColdFusion WDDX Deserialization Gadgets
漏洞标题 CVE-2023-44353: Adobe ColdFusion WDDX Deserialization Gadgets 漏洞描述 Adobe ColdFusion versions 2023.5 (and earlier) and 2021.11 (and earlier) are affected by an Deserial...
 2023年1月18日 19:05
CVE-2017-12794: Django Debug Page – Cross-Site Scripting
漏洞标题 CVE-2017-12794: Django Debug Page - Cross-Site Scripting 漏洞描述 Django 1.10.x before 1.10.8 and 1.11.x before 1.11.5 has HTML autoescaping disabled in a portion of the t...
2017年4月17日 18:18CVE-2023-2813: WordPress Multiple Themes – Reflected Cross-Site Scripting
漏洞标题 CVE-2023-2813: Wordpress Multiple Themes - Reflected Cross-Site Scripting 漏洞描述 All of the above Aapna WordPress theme through 1.3, Anand WordPress theme through 1.2, A...
2023年10月25日 13:28CVE-2022-0434: WordPress Page Views Count <2.4.15 - SQL Injection
漏洞标题 CVE-2022-0434: WordPress Page Views Count <2.4.15 - SQL Injection 漏洞描述 WordPress Page Views Count plugin prior to 2.4.15 contains an unauthenticated SQL injection v...
2022年5月18日 21:48CVE-2019-20504: Dell KACE Systems Management Appliance (K1000) 6.4.120756 – Remote Code Execution
漏洞标题 CVE-2019-20504: Dell KACE Systems Management Appliance (K1000) 6.4.120756 - Remote Code Execution 漏洞描述 service/krashrpt.php in Quest KACE K1000 Systems Management Appl...
2019年5月21日 04:04Apache Tomcat JK (mod_jk) 连接器-目录遍历(CVE-2018-11759)
漏洞标题 Apache Tomcat JK (mod_jk) 连接器-目录遍历(CVE-2018-11759) 漏洞描述 【漏洞描述】 Apache Tomcat JK(mod_jk) 【涉及版本】1.2.0,1.2.4 【漏洞描述】 由于Apache TomcatWeb服务器(...
2018年5月2日 07:12CVE-2020-11738: WordPress Duplicator 1.3.24 & 1.3.26 – Local File Inclusion
漏洞标题 CVE-2020-11738: WordPress Duplicator 1.3.24 & 1.3.26 - Local File Inclusion 漏洞描述 WordPress Duplicator 1.3.24 & 1.3.26 are vulnerable to local file inclusion vu...
2020年8月7日 02:39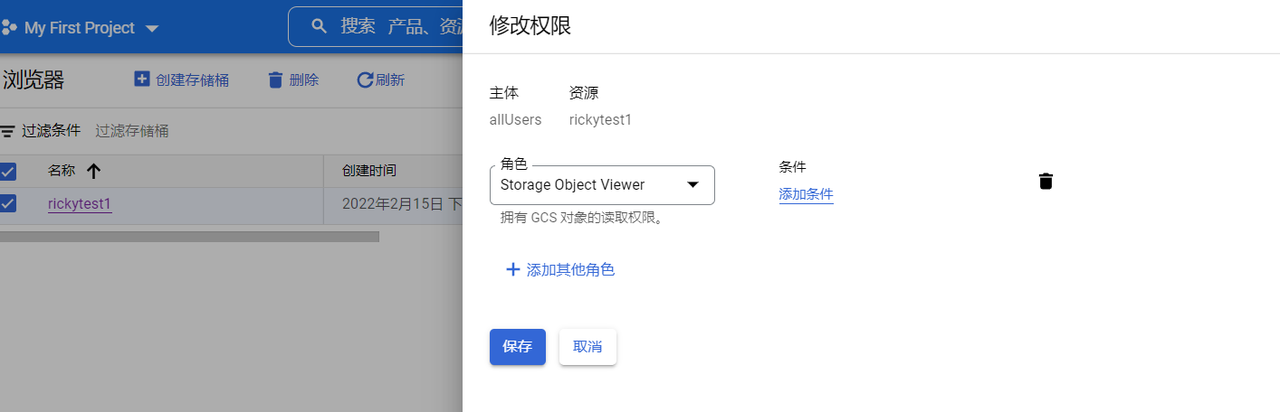
谷歌云 对象存储攻防
本文主要介绍谷歌云对象存储攻防的方式 1、存储桶配置错误-公开访问 当创建的存储桶配置了allUsers拥有GCS对象的读取权限时,该存储桶可以被任何用户公开访问 2、Bucket爆破 当不存在时访问会提...
2022年3月10日 23:38CVE-2021-4374: WordPress Automatic Plugin – Unauthenticated Options Change
漏洞标题 CVE-2021-4374: WordPress Automatic Plugin - Unauthenticated Options Change 漏洞描述 WordPress Automatic Plugin (versions 3.53.2 and below) contains a critical vulnerabilit...
2021年10月9日 17:04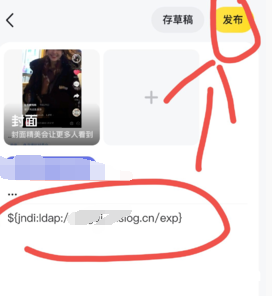
挖洞随手记1
挖洞之捡漏ssrf和log4j的小tips 以发帖为例(通俗易懂) 前言:挖洞要一步一步看,一步一步走 1:咱就是说,发帖 2:然后这个时候宝子们就可以看看有没有请求dnslog 成功(一般情况是没有的,dd...
2022年3月10日 23:30CVE-2022-24716: Icinga Web 2 – Arbitrary File Disclosure
漏洞标题 CVE-2022-24716: Icinga Web 2 - Arbitrary File Disclosure 漏洞描述 Icinga Web 2 is an open source monitoring web interface, framework and command-line interface. Unauthenti...
2022年8月3日 21:35
bugbounty技术聚合20210827
漏洞报告 U.S. Dept Of Defense [#1278891 CVE-2021-29156] LDAP Injection at http://██████ #1300591 Sensitive information on '████████' #1300589 Sensitive information on...
2022年3月10日 23:34CVE-2019-10647: ZZZCMS ZZZPHP 1.6.3 – Remote PHP Code Execution (RCE)
漏洞标题 CVE-2019-10647: ZZZCMS ZZZPHP 1.6.3 – Remote PHP Code Execution (RCE) 漏洞描述 ZZZCMS zzzphp v1.6.3 contains a remote code execution caused by lack of restrictions in inc...
2019年8月15日 14:16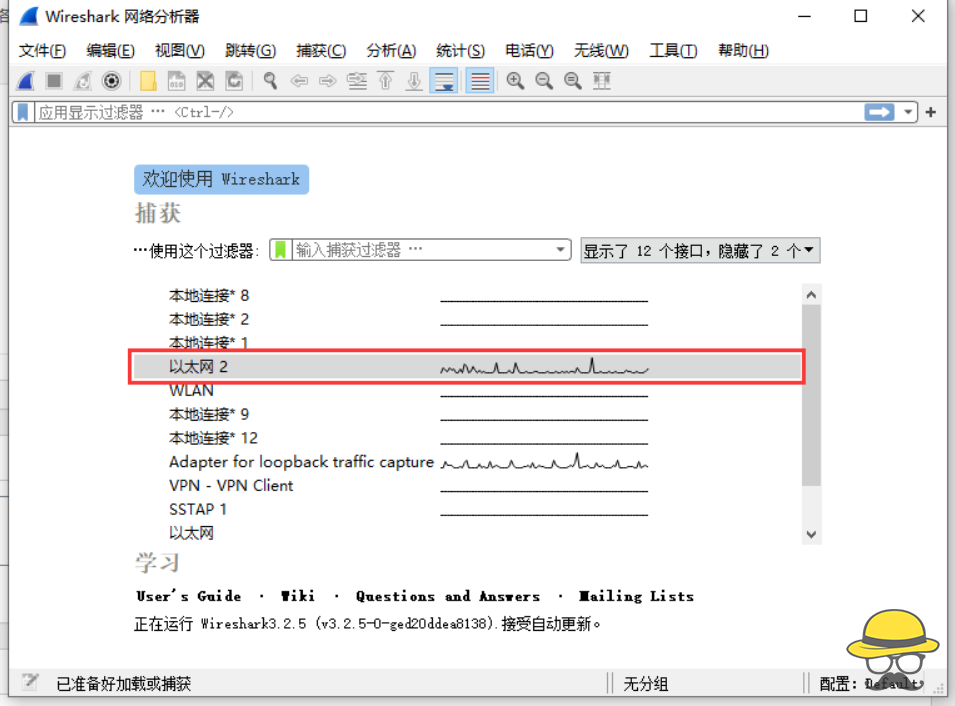
使用Wireshark抓包获取QQ好友的IP地址
介绍 很多人喜欢在互联网上装逼、口嗨,很多骗子在互联网上各种嚣张,通过这个教程可以很好的治一治这些人,本教程教大家如何通过Wireshark获取QQ好友的IP地址。 声明 本教程仅用于教育目的,请...

 2022年4月1日 18:36
CVE-2021-24762: WordPress Perfect Survey <1.5.2 - SQL Injection
漏洞标题 CVE-2021-24762: WordPress Perfect Survey <1.5.2 - SQL Injection 漏洞描述 Perfect Survey WordPress plugin before 1.5.2 does not validate and escape the question_id GET p...
2021年3月5日 02:36CVE-2024-7313: Shield Security Plugin < 20.0.6 - Cross-Site Scripting
漏洞标题 CVE-2024-7313: Shield Security Plugin < 20.0.6 - Cross-Site Scripting 漏洞描述 The Shield Security WordPress plugin before 20.0.6 contains a reflected cross-site script...
2024年3月21日 17:36
2026年11月6日 11:45
2026年11月5日 11:45
2026年11月4日 11:45
2026年11月3日 11:46
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

