
最新发布第278页
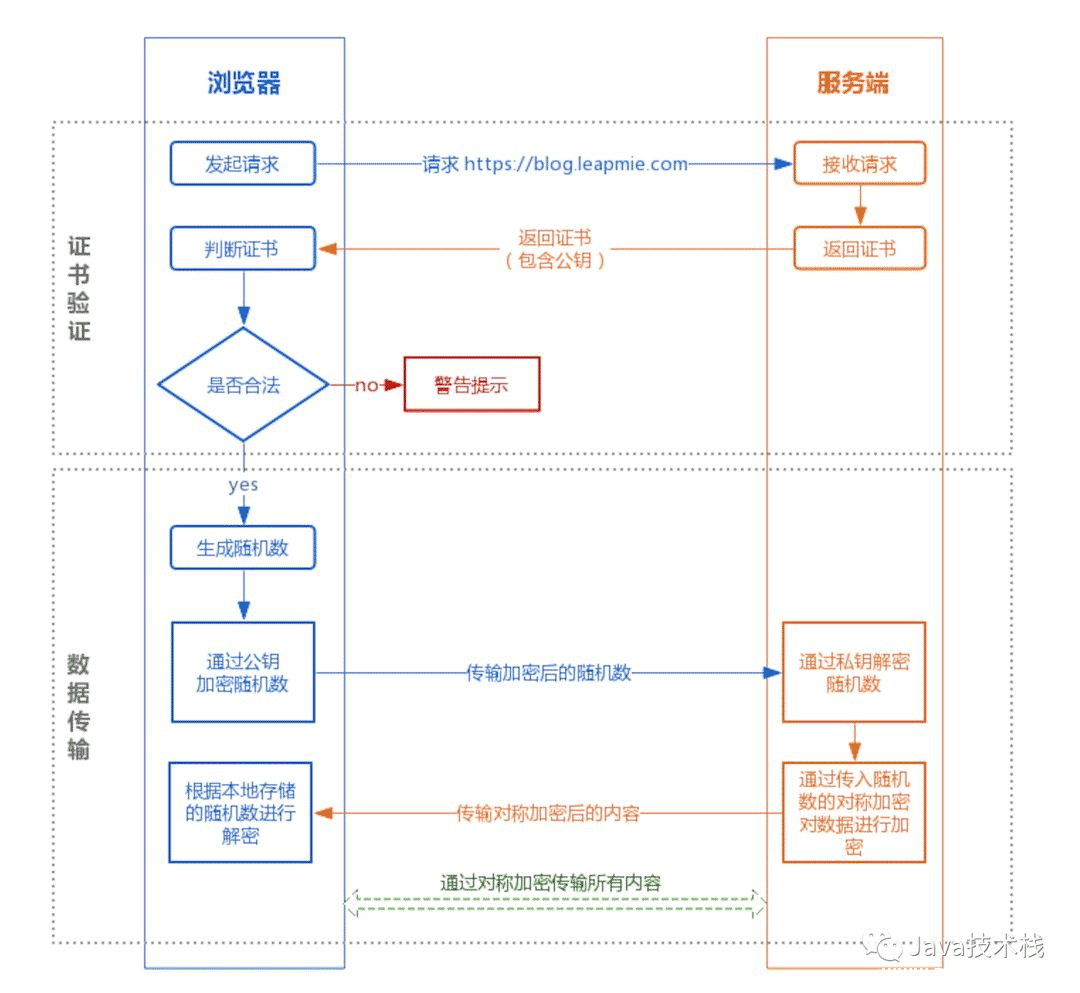
HTTPS 原理详解_服务器其它
这篇干货不错,把HTTPS的原理讲清楚了,而且容易懂,建议大家好好读一下。 随着 HTTPS 建站的成本下降,现在大部分的网站都已经开始用上 HTTPS 协议。大家都知道 HTTPS 比 HTTP 安全,也听说过...
 2024年3月13日 20:44

解决docker安装完成报:bridge-nf-call-iptables is disabled问题_docker
这篇文章主要介绍了解决docker安装完成报:bridge-nf-call-iptables is disabled问题,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 centos机器 docker安装完成后,输入dock...
2023年1月6日 20:56
CVE-2022-22965: Spring – Remote Code Execution
漏洞标题 CVE-2022-22965: Spring - Remote Code Execution 漏洞描述 Spring MVC and Spring WebFlux applications running on Java Development Kit 9+ are susceptible to remote code execut...
2022年7月28日 19:57CVE-2024-47073: DataEase v2.10.2 – JWT Signature Verification Bypass
漏洞标题 CVE-2024-47073: DataEase v2.10.2 - JWT Signature Verification Bypass 漏洞描述 DataEase is an open source data visualization analysis tool that helps users quickly analyze ...
2024年6月5日 12:44
McMenamins 23年间的雇员数据泄露,最早可追溯到1998年
麦克梅纳明斯McMenamins在俄勒冈州和华盛顿州拥有62家酒店、剧院、酒吧和餐馆,其中不少位于经过修复的历史遗迹中,同时该公司是美国50大精酿啤酒厂之一,现今拥有 2700 名员工。近日, McMenam...
2022年3月10日 23:39CVE-2021-27250: D-LINK DAP-2020 webproc 任意文件读取漏洞
漏洞标题 CVE-2021-27250: D-LINK DAP-2020 webproc 任意文件读取漏洞 漏洞描述 This vulnerability allows network-adjacent attackers to disclose sensitive information on affected instal...
2021年10月6日 21:42CVE-2021-34805: FAUST iServer 9.0.018.018.4 – Local File Inclusion
漏洞标题 CVE-2021-34805: FAUST iServer 9.0.018.018.4 - Local File Inclusion 漏洞描述 FAUST iServer before 9.0.019.019.7 is susceptible to local file inclusion because for each URL ...
2021年8月10日 11:24CRMEB开源商城系统 /api/products 存在SQL注入漏洞(CVE-2024-36837)
漏洞标题 CRMEB开源商城系统 /api/products 存在SQL注入漏洞(CVE-2024-36837) 漏洞描述 CRMEB开源商城系统是一款全开源可商用的系统,前后端分离开发,全部100%开源,在小程序、公众号、H5、APP...
2024年4月21日 17:17CVE-2025-24514: Ingress-Nginx Controller – Configuration Injection via Unsanitized `auth-url` Annotation
漏洞标题 CVE-2025-24514: Ingress-Nginx Controller - Configuration Injection via Unsanitized `auth-url` Annotation 漏洞描述 A security issue was discovered in ingress-nginx https-//...
2025年11月30日 15:04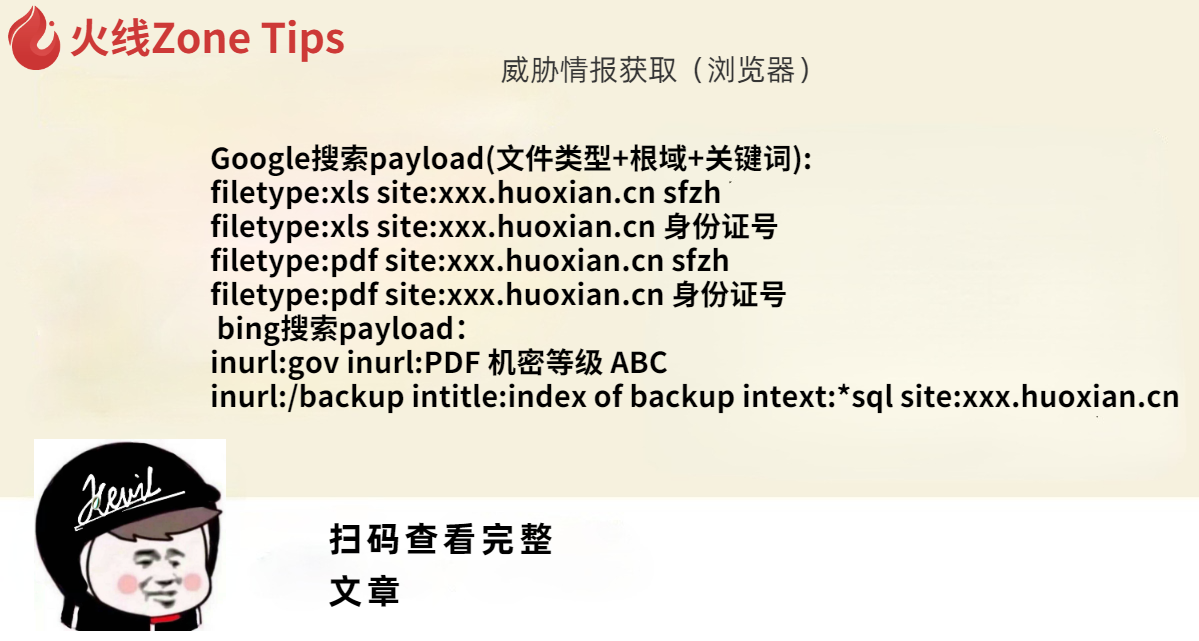
威胁情报获取(浏览器)
Google搜索payload(文件类型+根域+关键词): filetype:xls site:xxx.huoxian.cn sfzh filetype:xls site:xxx.huoxian.cn 身份证号 filetype:pdf site:xxx.huoxian.cn sfzh filetype:pdf site:xxx...
2022年3月10日 23:34CVE-2021-24288: WordPress AcyMailing <7.5.0 - Open Redirect
漏洞标题 CVE-2021-24288: WordPress AcyMailing <7.5.0 - Open Redirect 漏洞描述 WordPress AcyMailing plugin before 7.5.0 contains an open redirect vulnerability due to improper sa...
2021年3月29日 20:47CVE-2021-21287: MinIO Browser API – Server-Side Request Forgery
漏洞标题 CVE-2021-21287: MinIO Browser API - Server-Side Request Forgery 漏洞描述 MinIO Browser API before version RELEASE.2021-01-30T00-20-58Z contains a server-side request forge...
2021年9月13日 21:35如何使用Celery和Docker处理Django中的定期任务_docker
这篇文章主要介绍了使用Celery和Docker处理Django中的定期任务的方法,本文通过实例代码给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 在构建和扩展Dj...
2024年1月29日 20:40Citrix ADC and Gateway CVE-2023-4966 信息泄露漏洞 – 1
漏洞标题 Citrix ADC and Gateway CVE-2023-4966 信息泄露漏洞 - 1 漏洞描述 Citrix ADC and Gateway CVE-2023-4966 信息泄露漏洞 - 1 日期: 2024-02-07 | 影响软件: Citrix ADC | PoC代码 暂无
2023年1月29日 23:54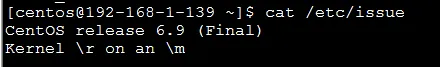
centos 6.9 升级glibc动态库的详细过程_Linux
glibc是gnu发布的libc库,即c运行库,glibc是linux系统中最底层的api,几乎其它任何运行库都会依赖于glibc。这篇文章主要介绍了centos 6.9 升级glibc动态库的详细过程,需要的朋友可以参考下 gli...
2026年9月13日 11:45CVE-2022-22733: Apache ShardingSphere ElasticJob-UI privilege escalation
漏洞标题 CVE-2022-22733: Apache ShardingSphere ElasticJob-UI privilege escalation 漏洞描述 Exposure of Sensitive Information to an Unauthorized Actor vulnerability in Apache Shardi...
2022年12月26日 02:57
2026年11月16日 11:45
2026年11月15日 11:45
2026年11月14日 11:45
2026年11月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

