
最新发布第283页

CVE-2022-27849: WordPress Simple Ajax Chat <20220116 - Sensitive Information Disclosure vulnerability
漏洞标题 CVE-2022-27849: WordPress Simple Ajax Chat <20220116 - Sensitive Information Disclosure vulnerability 漏洞描述 WordPress Simple Ajax Chat before 20220216 is vulnerable ...
 2022年11月1日 08:58
CVE-2021-24838: WordPress AnyComment <0.3.5 - Open Redirect
漏洞标题 CVE-2021-24838: WordPress AnyComment <0.3.5 - Open Redirect 漏洞描述 WordPress AnyComment plugin before 0.3.5 contains an open redirect vulnerability via an API endpoin...
2021年9月4日 16:17CVE-2024-4358: Progress Telerik Report Server – Authentication Bypass
漏洞标题 CVE-2024-4358: Progress Telerik Report Server - Authentication Bypass 漏洞描述 In Progress Telerik Report Server, version 2024 Q1 (10.0.24.305) or earlier, on IIS, an unau...
2024年11月27日 05:48CVE-2024-8856: WP Time Capsule Plugin – Remote Code Execution
漏洞标题 CVE-2024-8856: WP Time Capsule Plugin - Remote Code Execution 漏洞描述 The Backup and Staging by WP Time Capsule plugin for WordPress is vulnerable to arbitrary file uploa...
2024年4月25日 09:38Apache OFBiz webtools/control/ProgramExport 远程代码执行漏洞(CVE-2023-51467)
漏洞标题 Apache OFBiz webtools/control/ProgramExport 远程代码执行漏洞(CVE-2023-51467) 漏洞描述 Apache OFBiz 在 webtools/control/ProgramExport存在代码执行漏洞,攻击者可通过该漏洞...
2023年3月14日 00:47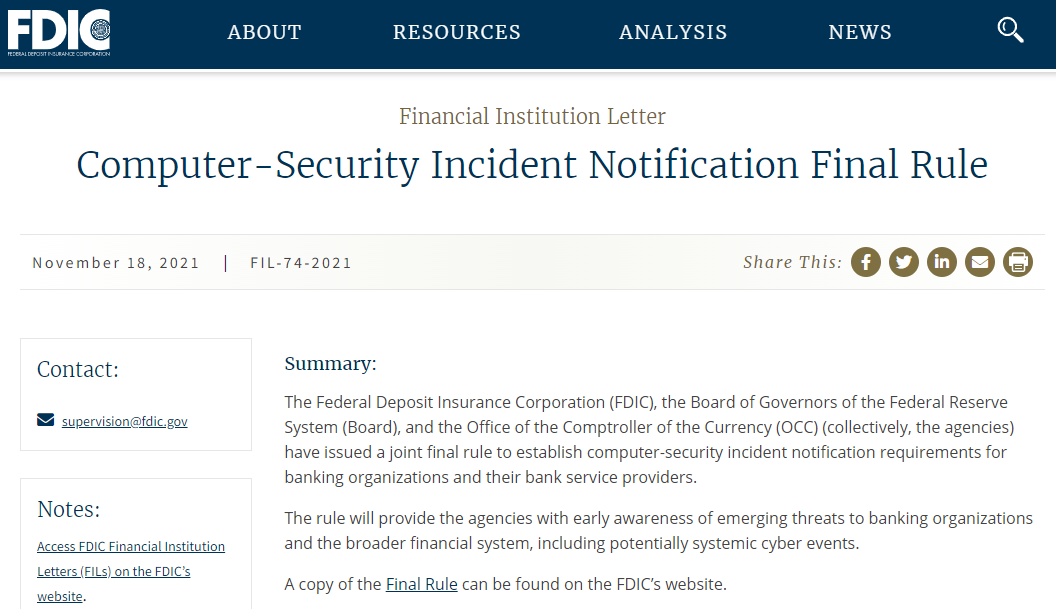
美国新规:银行机构须于36小时内报告计算机安全事件
11月18日,美国银行监管机构发布了一项新规定,要求银行必须在36小时内向监管机构通报重大计算机安全事件。这些事件包括如大规模分布式拒绝服务攻击、恶意软件攻击、硬件及软件的非恶意故障、人...
2022年3月10日 23:38CVE-2018-10942: Prestashop AttributeWizardPro Module – Arbitrary File Upload
漏洞标题 CVE-2018-10942: Prestashop AttributeWizardPro Module - Arbitrary File Upload 漏洞描述 In the Attribute Wizard addon 1.6.9 for PrestaShop allows remote attackers to execute...
2018年3月15日 06:12CVE-2025-27223: TRUfusion Enterprise <= 7.10.4.0 - Authentication Bypass
漏洞标题 CVE-2025-27223: TRUfusion Enterprise <= 7.10.4.0 - Authentication Bypass 漏洞描述 Hard-Coded Cryptographic key allowing to forge session cookies that can be used to ent...
2025年6月7日 06:31CVE-2022-34534: Digital Watchdog DW Spectrum Server 4.2.0.32842 – Information Disclosure
漏洞标题 CVE-2022-34534: Digital Watchdog DW Spectrum Server 4.2.0.32842 - Information Disclosure 漏洞描述 Digital Watchdog DW Spectrum Server 4.2.0.32842 allows attackers to acces...
2022年3月23日 00:12CVE-2020-12259: rConfig 3.9.4 – Cross-Site Scripting
漏洞标题 CVE-2020-12259: rConfig 3.9.4 - Cross-Site Scripting 漏洞描述 rConfig 3.9.4 is vulnerable to reflected XSS. The configDevice.php file improperly validates user input. An a...
2020年2月24日 16:58CVE-2025-55523: Agent-Zero 0.8.0 – 0.9.4 – Arbitrary File Download
漏洞标题 CVE-2025-55523: Agent-Zero 0.8.0 - 0.9.4 - Arbitrary File Download 漏洞描述 Agent-Zero v0.8.0 - 0.9.4 contains a path traversal caused by improper validation in /api/downl...
2025年1月25日 14:18CVE-2021-27748: IBM WebSphere HCL Digital Experience – Server-Side Request Forgery
漏洞标题 CVE-2021-27748: IBM WebSphere HCL Digital Experience - Server-Side Request Forgery 漏洞描述 IBM WebSphere HCL Digital Experience is vulnerable to server-side request forge...
2021年2月13日 18:15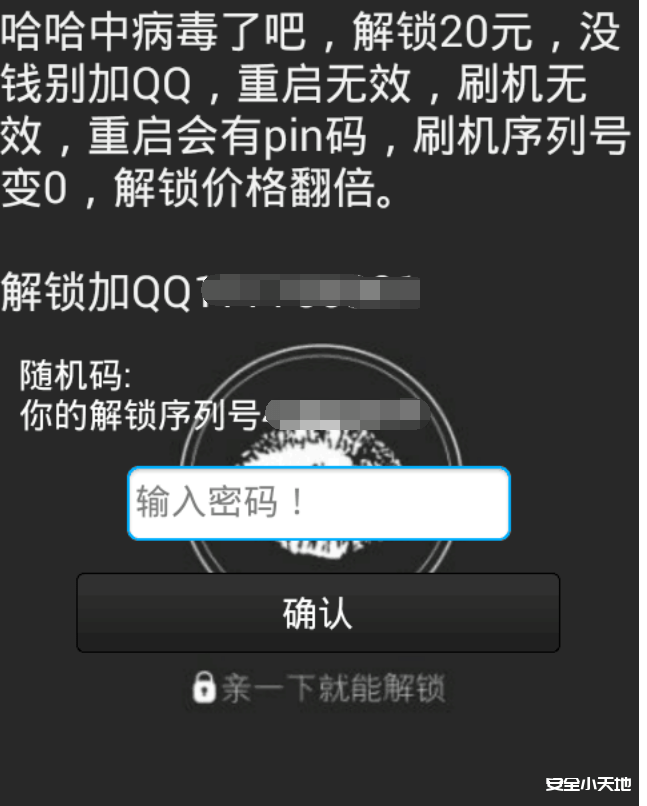
2023年最新锁机软件解除教程
第一种 唤醒手机语音助手,让他清理后台(最简单最实用 90%解锁 安卓版本高的最推荐使用) 第二种 用另一部手机打电话给那部被锁的手机,然后出现接电话那个界面,然后马上退出到桌面,到锁机软...

 2023年9月12日 15:37
CVE-2021-24370: WordPress Fancy Product Designer <4.6.9 - Arbitrary File Upload
漏洞标题 CVE-2021-24370: WordPress Fancy Product Designer <4.6.9 - Arbitrary File Upload 漏洞描述 WordPress Fancy Product Designer plugin before 4.6.9 is susceptible to an arbit...
2021年4月24日 03:47CVE-2021-44529: Ivanti EPM Cloud Services Appliance Code Injection
漏洞标题 CVE-2021-44529: Ivanti EPM Cloud Services Appliance Code Injection 漏洞描述 Ivanti EPM Cloud Services Appliance (CSA) before version 4.6.0-512 is susceptible to a code inj...
2021年6月10日 13:49CVE-2021-44152: Reprise License Manager 14.2 – Authentication Bypass
漏洞标题 CVE-2021-44152: Reprise License Manager 14.2 - Authentication Bypass 漏洞描述 Reprise License Manager (RLM) 14.2 does not verify authentication or authorization and allows...
2021年7月21日 11:21
2026年10月16日 11:45
2026年10月15日 11:45
2026年10月14日 11:45
2026年10月13日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月20日 16:22
2026年9月20日 11:48
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

