
最新发布第30页

CVE-2024-0799: Arcserve Unified Data Protection – Authentication Bypass
漏洞标题 CVE-2024-0799: Arcserve Unified Data Protection - Authentication Bypass 漏洞描述 An authentication bypass vulnerability exists in Arcserve Unified Data Protection 9.2 and ...
 2024年4月10日 17:42
CVE-2013-2251: Apache Struts 2 – DefaultActionMapper Prefixes OGNL Code Execution (S2-016)
漏洞标题 CVE-2013-2251: Apache Struts 2 - DefaultActionMapper Prefixes OGNL Code Execution (S2-016) 漏洞描述 In Struts 2 before 2.3.15.1 the information following "action:&quo...
2013年8月9日 15:48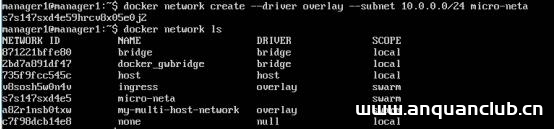
解决Docker network Create加–subnet后遇到问题_docker
这篇文章主要介绍了解决Docker network Create加--subnet后遇到问题。具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 Docker network Create加–subnet后,使用docker networ...
2023年1月7日 20:36CVE-2018-0296: Cisco ASA – Local File Inclusion
漏洞标题 CVE-2018-0296: Cisco ASA - Local File Inclusion 漏洞描述 Cisco Adaptive Security Appliances (ASA) web interfaces could allow an unauthenticated, remote attacker to cause a...
2018年5月23日 06:29CVE-2022-26148: Grafana & Zabbix Integration – Credentials Disclosure
漏洞标题 CVE-2022-26148: Grafana & Zabbix Integration - Credentials Disclosure 漏洞描述 Grafana through 7.3.4, when integrated with Zabbix, contains a credential disclosure vul...
2022年12月29日 06:47CVE-2022-46020: WBCE CMS v1.5.4 – Remote Code Execution
漏洞标题 CVE-2022-46020: WBCE CMS v1.5.4 - Remote Code Execution 漏洞描述 WBCE CMS v1.5.4 can implement getshell by modifying the upload file type. PoC代码
2022年7月11日 03:19CVE-2022-0817: WordPress BadgeOS <=3.7.0 - SQL Injection
漏洞标题 CVE-2022-0817: WordPress BadgeOS <=3.7.0 - SQL Injection 漏洞描述 WordPress BadgeOS plugin through 3.7.0 contains a SQL injection vulnerability. It does not sanitize an...
2022年11月15日 16:15
在 Linux 上使用 Multitail命令的教程_Linux
MultiTail是一个开源的ncurses的实用工具,可用于在一个窗口或单一外壳,显示实时一样的尾巴命令,该命令拆分控制台为更多子窗口的日志文件的最后几行。这篇文章主要介绍了在 Linux 上使用 Mult...
2026年5月6日 11:45CVE-2021-42887: TOTOLINK EX1200T 4.1.2cu.5215 – Authentication Bypass
漏洞标题 CVE-2021-42887: TOTOLINK EX1200T 4.1.2cu.5215 - Authentication Bypass 漏洞描述 TOTOLINK EX1200T 4.1.2cu.5215 is susceptible to authentication bypass. An attacker can bypas...
2021年10月28日 21:13CVE-2021-24286: WordPress Plugin Redirect 404 to Parent 1.3.0 – Cross-Site Scripting
漏洞标题 CVE-2021-24286: WordPress Plugin Redirect 404 to Parent 1.3.0 - Cross-Site Scripting 漏洞描述 The settings page of the plugin did not properly sanitise the tab parameter b...
2021年9月1日 11:55CVE-2025-8286: Güralp Systems FMUS Series – Unauthenticated Access
漏洞标题 CVE-2025-8286: Güralp Systems FMUS Series - Unauthenticated Access 漏洞描述 Güralp Systems FMUS Series Seismic Monitoring Devices expose an unauthenticated Telnet-based ...
2025年12月30日 22:35CVE-2004-0437: Titan FTP Server 3.01 – DoS via LIST Command Disconnection
漏洞标题 CVE-2004-0437: Titan FTP Server 3.01 - DoS via LIST Command Disconnection 漏洞描述 Titan FTP Server version 3.01 build 163 (and possibly other older versions) contains a v...
2004年12月17日 00:22CVE-2020-2551: Oracle WebLogic Server – Remote Code Execution
漏洞标题 CVE-2020-2551: Oracle WebLogic Server - Remote Code Execution 漏洞描述 Oracle WebLogic Server (Oracle Fusion Middleware (component: WLS Core Components) is susceptible to ...
2020年6月23日 04:30CVE-2024-24116: Ruijie RG-NBS2009G-P – Improper Authentication
漏洞标题 CVE-2024-24116: Ruijie RG-NBS2009G-P - Improper Authentication 漏洞描述 An issue in Ruijie RG-NBS2009G-P RGOS v.10.4(1)P2 Release(9736) allows a remote attacker to gain pr...
2024年2月3日 19:20
[极客大挑战 2019]BabySQL – buu刷题笔记
自从前几次网站被日,我对我的网站做了严格的过滤,你们这些黑客死心吧!!! 尝试登录 admin'# ,登录成功,但相较于以前做的那个sql题,这个flag铁定错的 Your password is 'fd7055ec3060d96f...

 2022年4月15日 15:17
bugbounty技巧聚合20220119
漏洞报告 通过 post auth SSRF 窃取管理 JWT (CVE-2021-22056) http://blog.assetnote.io/2022/01/17/workspace-one-access-ssrf/ 挖洞技巧 Top 10 web hacking techniques of 2021 - PortSwigg...
2022年3月10日 23:33
2026年9月14日 11:45
2026年9月13日 11:45
2026年9月12日 12:55
2026年9月11日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年9月2日 09:46
2026年8月16日 20:18
2026年8月11日 13:39
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

