
最新发布第310页
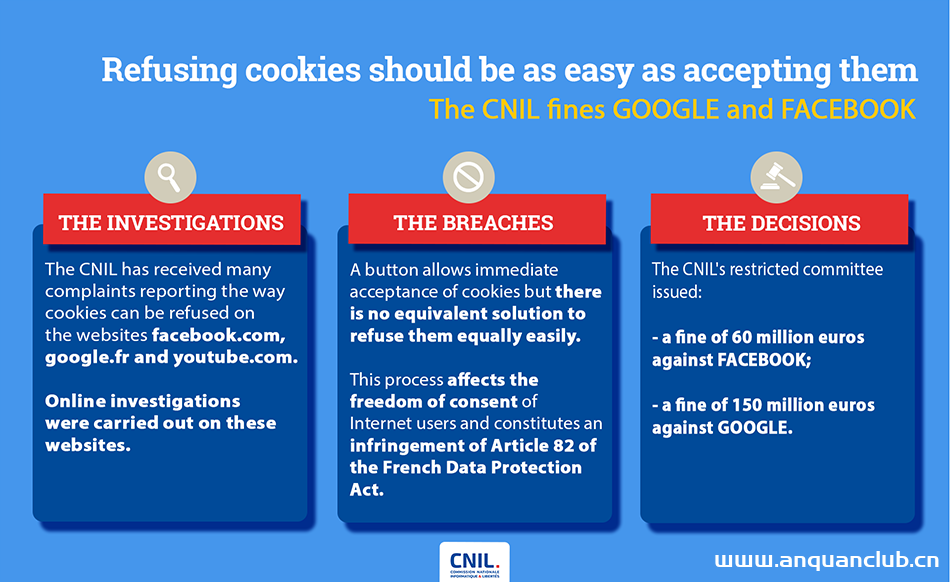
法国罚谷歌脸书共2.1亿欧元,因用户无法简单拒绝Cookie
上周,法国数据保护监管机构国家信息自由委员会(CNIL)对Facebook和谷歌分别处以了1.5亿欧元和6000万欧元的罚款,因为它们违反了《法国数据保护法》,未能为用户提供拒绝Cookie的简单方式。CNI...
 2022年3月10日 23:39

Linux dirname命令的具体使用_Linux
这篇文章主要介绍了Linux dirname命令的具体使用,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 01. 命令概述 dirn...
2024年4月21日 20:06
CVE-2023-48084: Nagios XI < 5.11.3 - SQL Injection
漏洞标题 CVE-2023-48084: Nagios XI < 5.11.3 - SQL Injection 漏洞描述 SQL injection vulnerability in Nagios XI before version 5.11.3 via the bulk modification tool. PoC代码
2023年7月13日 17:40CVE-2018-9206: Blueimp jQuery-File-Upload v9.22.0 – Unrestricted File Upload
漏洞标题 CVE-2018-9206: Blueimp jQuery-File-Upload v9.22.0 - Unrestricted File Upload 漏洞描述 Blueimp jQuery-File-Upload v9.22.0 contains an unauthenticated arbitrary file upload ...
2018年1月21日 21:28CVE-2022-25061: TP-Link TL-WR840N – Command Injection
漏洞标题 CVE-2022-25061: TP-Link TL-WR840N - Command Injection 漏洞描述 The TP-Link TL-WR840N(ES)_V6.20_180709 router contains a command injection vulnerability in the oal_setIp6De...
2022年9月5日 19:39CVE-2021-24750: WordPress Visitor Statistics (Real Time Traffic) <4.8 -SQL Injection
漏洞标题 CVE-2021-24750: WordPress Visitor Statistics (Real Time Traffic) <4.8 -SQL Injection 漏洞描述 WordPress Visitor Statistics (Real Time Traffic) plugin before 4.8 does no...
2021年9月30日 12:57CVE-2020-24903: Cute Editor for ASP.NET 6.4 – Cross-Site Scripting
漏洞标题 CVE-2020-24903: Cute Editor for ASP.NET 6.4 - Cross-Site Scripting 漏洞描述 Cute Editor for ASP.NET 6.4 contains a cross-site scripting vulnerability. An attacker can inje...
2020年7月23日 00:41
ubuntu20.04中文输入法安装步骤_Linux
这篇文章主要介绍了ubuntu20.04中文输入法安装步骤,文中通过图文介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 本文安装谷歌输入法...
2023年8月29日 21:16CVE-2022-30525: Zyxel Firewall – OS Command Injection
漏洞标题 CVE-2022-30525: Zyxel Firewall - OS Command Injection 漏洞描述 An OS command injection vulnerability in the CGI program of Zyxel USG FLEX 100(W) firmware versions 5.00 thr...
2022年11月6日 20:51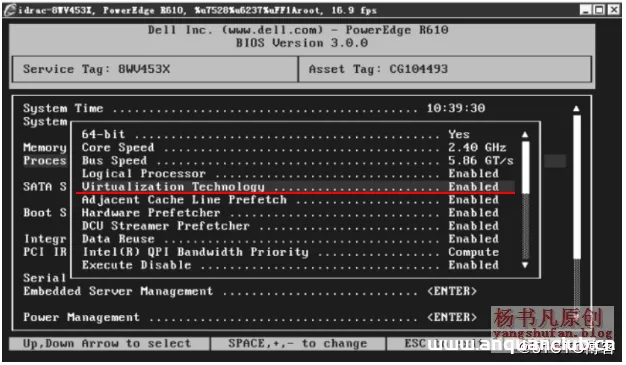
在CentOS7搭建KVM虚拟化平台(三种方式)_Kvm
这篇文章主要介绍了在CentOS7搭建KVM虚拟化平台(三种方式),文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 KVM 全...
2026年8月21日 11:45CVE-2021-44152: Reprise License Manager 14.2 – Authentication Bypass
漏洞标题 CVE-2021-44152: Reprise License Manager 14.2 - Authentication Bypass 漏洞描述 Reprise License Manager (RLM) 14.2 does not verify authentication or authorization and allows...
2021年6月11日 14:14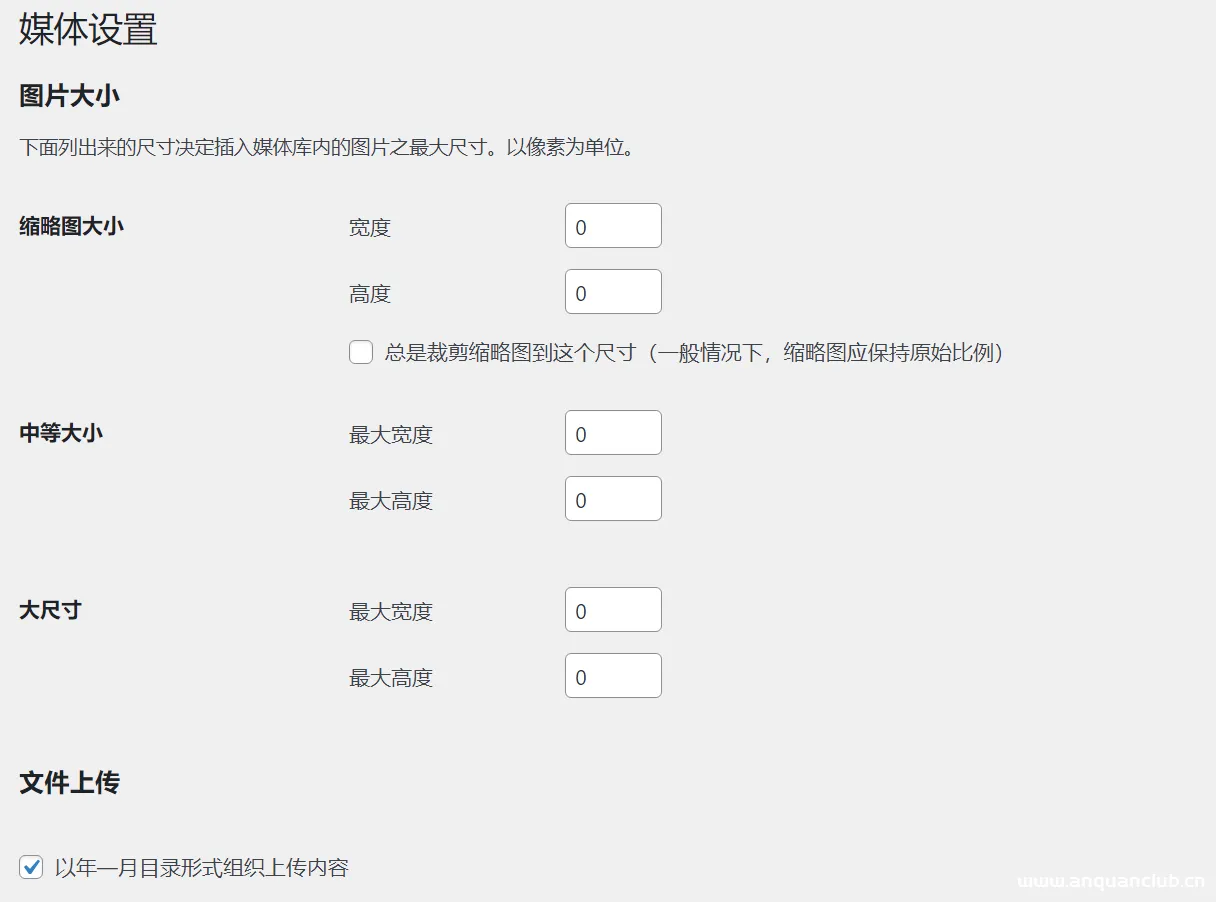
wordpress彻底关闭自动生成缩略图,节约服务器资源空间(附清理缩略图脚本)
前言 WordPress上传图片如何禁止自动生成缩略图呢?我们在使用WordPress程序的时候上传的图片会自动生成缩略图,还会占用我们的空间内容。那么我们如何来禁止呢?今天安全小天地给大家总结了禁...

 2023年1月13日 19:33
BIBLIOsoft BIBLIOpac 2008(CVE-2018-16139)
漏洞标题 BIBLIOsoft BIBLIOpac 2008(CVE-2018-16139) 漏洞描述 BIBLIOsoft BIBLIOpac2008通过bin/wxis.exe/BIBLIOpac/的db或action参数包含一个跨站点脚本漏洞,该漏洞允许远程攻击者注入任意w...
2018年6月5日 12:07
【技术分享】去除logo免费生成网站的水印 方法通用
声明 本文章仅供技术科普,对案例中涉及的网站并无恶意,如需原图,请前往官网下载!!! 请勿用作非法用途,如有违反,概不负责!如有侵权,联系站长! 相关阅读 案例 1、打开百度,搜索logo在...
2023年1月13日 19:10CVE-2024-51378: CyberPanel – Command Injection
漏洞标题 CVE-2024-51378: CyberPanel - Command Injection 漏洞描述 CyberPanel contains a command injection vulnerability in the /ftp/getresetstatus and /dns/getresetstatus endpoints....
2024年11月2日 00:54CVE-2022-24181: PKP Open Journal Systems 2.4.8-3.3 – Cross-Site Scripting
漏洞标题 CVE-2022-24181: PKP Open Journal Systems 2.4.8-3.3 - Cross-Site Scripting 漏洞描述 PKP Open Journal Systems 2.4.8 to 3.3 contains a cross-site scripting vulnerability whic...
2022年1月16日 09:42
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

