
最新发布第324页

CVE-2022-0867: WordPress ARPrice <3.6.1 - SQL Injection
漏洞标题 CVE-2022-0867: WordPress ARPrice <3.6.1 - SQL Injection 漏洞描述 WordPress ARPrice plugin prior to 3.6.1 contains a SQL injection vulnerability. It fails to properly sa...
 2022年3月11日 16:11
Apache Flink 文件读取(CVE-2020-17519)
漏洞标题 Apache Flink 文件读取(CVE-2020-17519) 漏洞描述 【漏洞对象】Apache Flink 【涉及版本】Flink部分版本(1.11.0, 1.11.1, 1.11.2) \【漏洞描述】ApacheFlink是一个开源的流处理框架...
2020年4月9日 13:10CVE-2018-14013: Synacor Zimbra Collaboration Suite Collaboration <8.8.11 - Cross-Site Scripting
漏洞标题 CVE-2018-14013: Synacor Zimbra Collaboration Suite Collaboration <8.8.11 - Cross-Site Scripting 漏洞描述 Synacor Zimbra Collaboration Suite Collaboration before 8.8.11 ...
2018年10月21日 11:56CVE-2025-30406: Gladinet CentreStack < 16.4.10315.56368 Use of Hard-coded Key Leads to Unauthenticated RCE
漏洞标题 CVE-2025-30406: Gladinet CentreStack < 16.4.10315.56368 Use of Hard-coded Key Leads to Unauthenticated RCE 漏洞描述 Gladinet CentreStack through 16.1.10296.56315 (fixed...
2025年9月19日 14:31CVE-2019-8943: WordPress Core 5.0.0 – Crop-image Shell Upload
漏洞标题 CVE-2019-8943: WordPress Core 5.0.0 - Crop-image Shell Upload 漏洞描述 WordPress through 5.0.3 allows Path Traversal in wp_crop_image(). An attacker (who has privileges to...
2019年5月23日 23:43CVE-2023-30194: Prestashop posstaticfooter <= 1.0.0 - SQL Injection
漏洞标题 CVE-2023-30194: Prestashop posstaticfooter <= 1.0.0 - SQL Injection 漏洞描述 Prestashop posstaticfooter <= 1.0.0 is vulnerable to SQL Injection via posstaticfooter::...
2023年12月3日 07:51CVE-2020-10548: rConfig 3.9.4 – SQL Injection
漏洞标题 CVE-2020-10548: rConfig 3.9.4 - SQL Injection 漏洞描述 rConfig 3.9.4 and previous versions have unauthenticated devices.inc.php SQL injection. Because nodes' password...
2020年5月29日 04:21CVE-2018-3810: Oturia WordPress Smart Google Code Inserter <3.5 - Authentication Bypass
漏洞标题 CVE-2018-3810: Oturia WordPress Smart Google Code Inserter <3.5 - Authentication Bypass 漏洞描述 Oturia Smart Google Code Inserter plugin before 3.5 for WordPress allow...
2018年12月21日 08:41
以隐私安全为由,苹果、谷歌反对美国国会拟议的反垄断法案
美国国会目前正在审议两项反垄断法案——《美国创新与在线选择法案(American Innovation And Choice Online Act)》和《开放应用市场法案(Open App Markets Act)》,旨在约束苹果、谷歌在内的大...
2022年3月10日 23:39CVE-2012-1226: Dolibarr ERP/CRM 3.2 Alpha – Multiple Directory Traversal Vulnerabilities
漏洞标题 CVE-2012-1226: Dolibarr ERP/CRM 3.2 Alpha - Multiple Directory Traversal Vulnerabilities 漏洞描述 Multiple directory traversal vulnerabilities in Dolibarr CMS 3.2.0 Alpha ...
2012年8月30日 12:43
美英澳联合总结2021年勒索软件态势并提供缓解建议
近日,美国、英国和澳大利亚的网络安全当局联合撰写发布了一份网络安全公告,警告2021年全球勒索软件呈现的趋势表明全球化威胁将继续增加。该报告分享了观察到的网络犯罪行为、趋势以及缓解建议...
2022年3月10日 23:40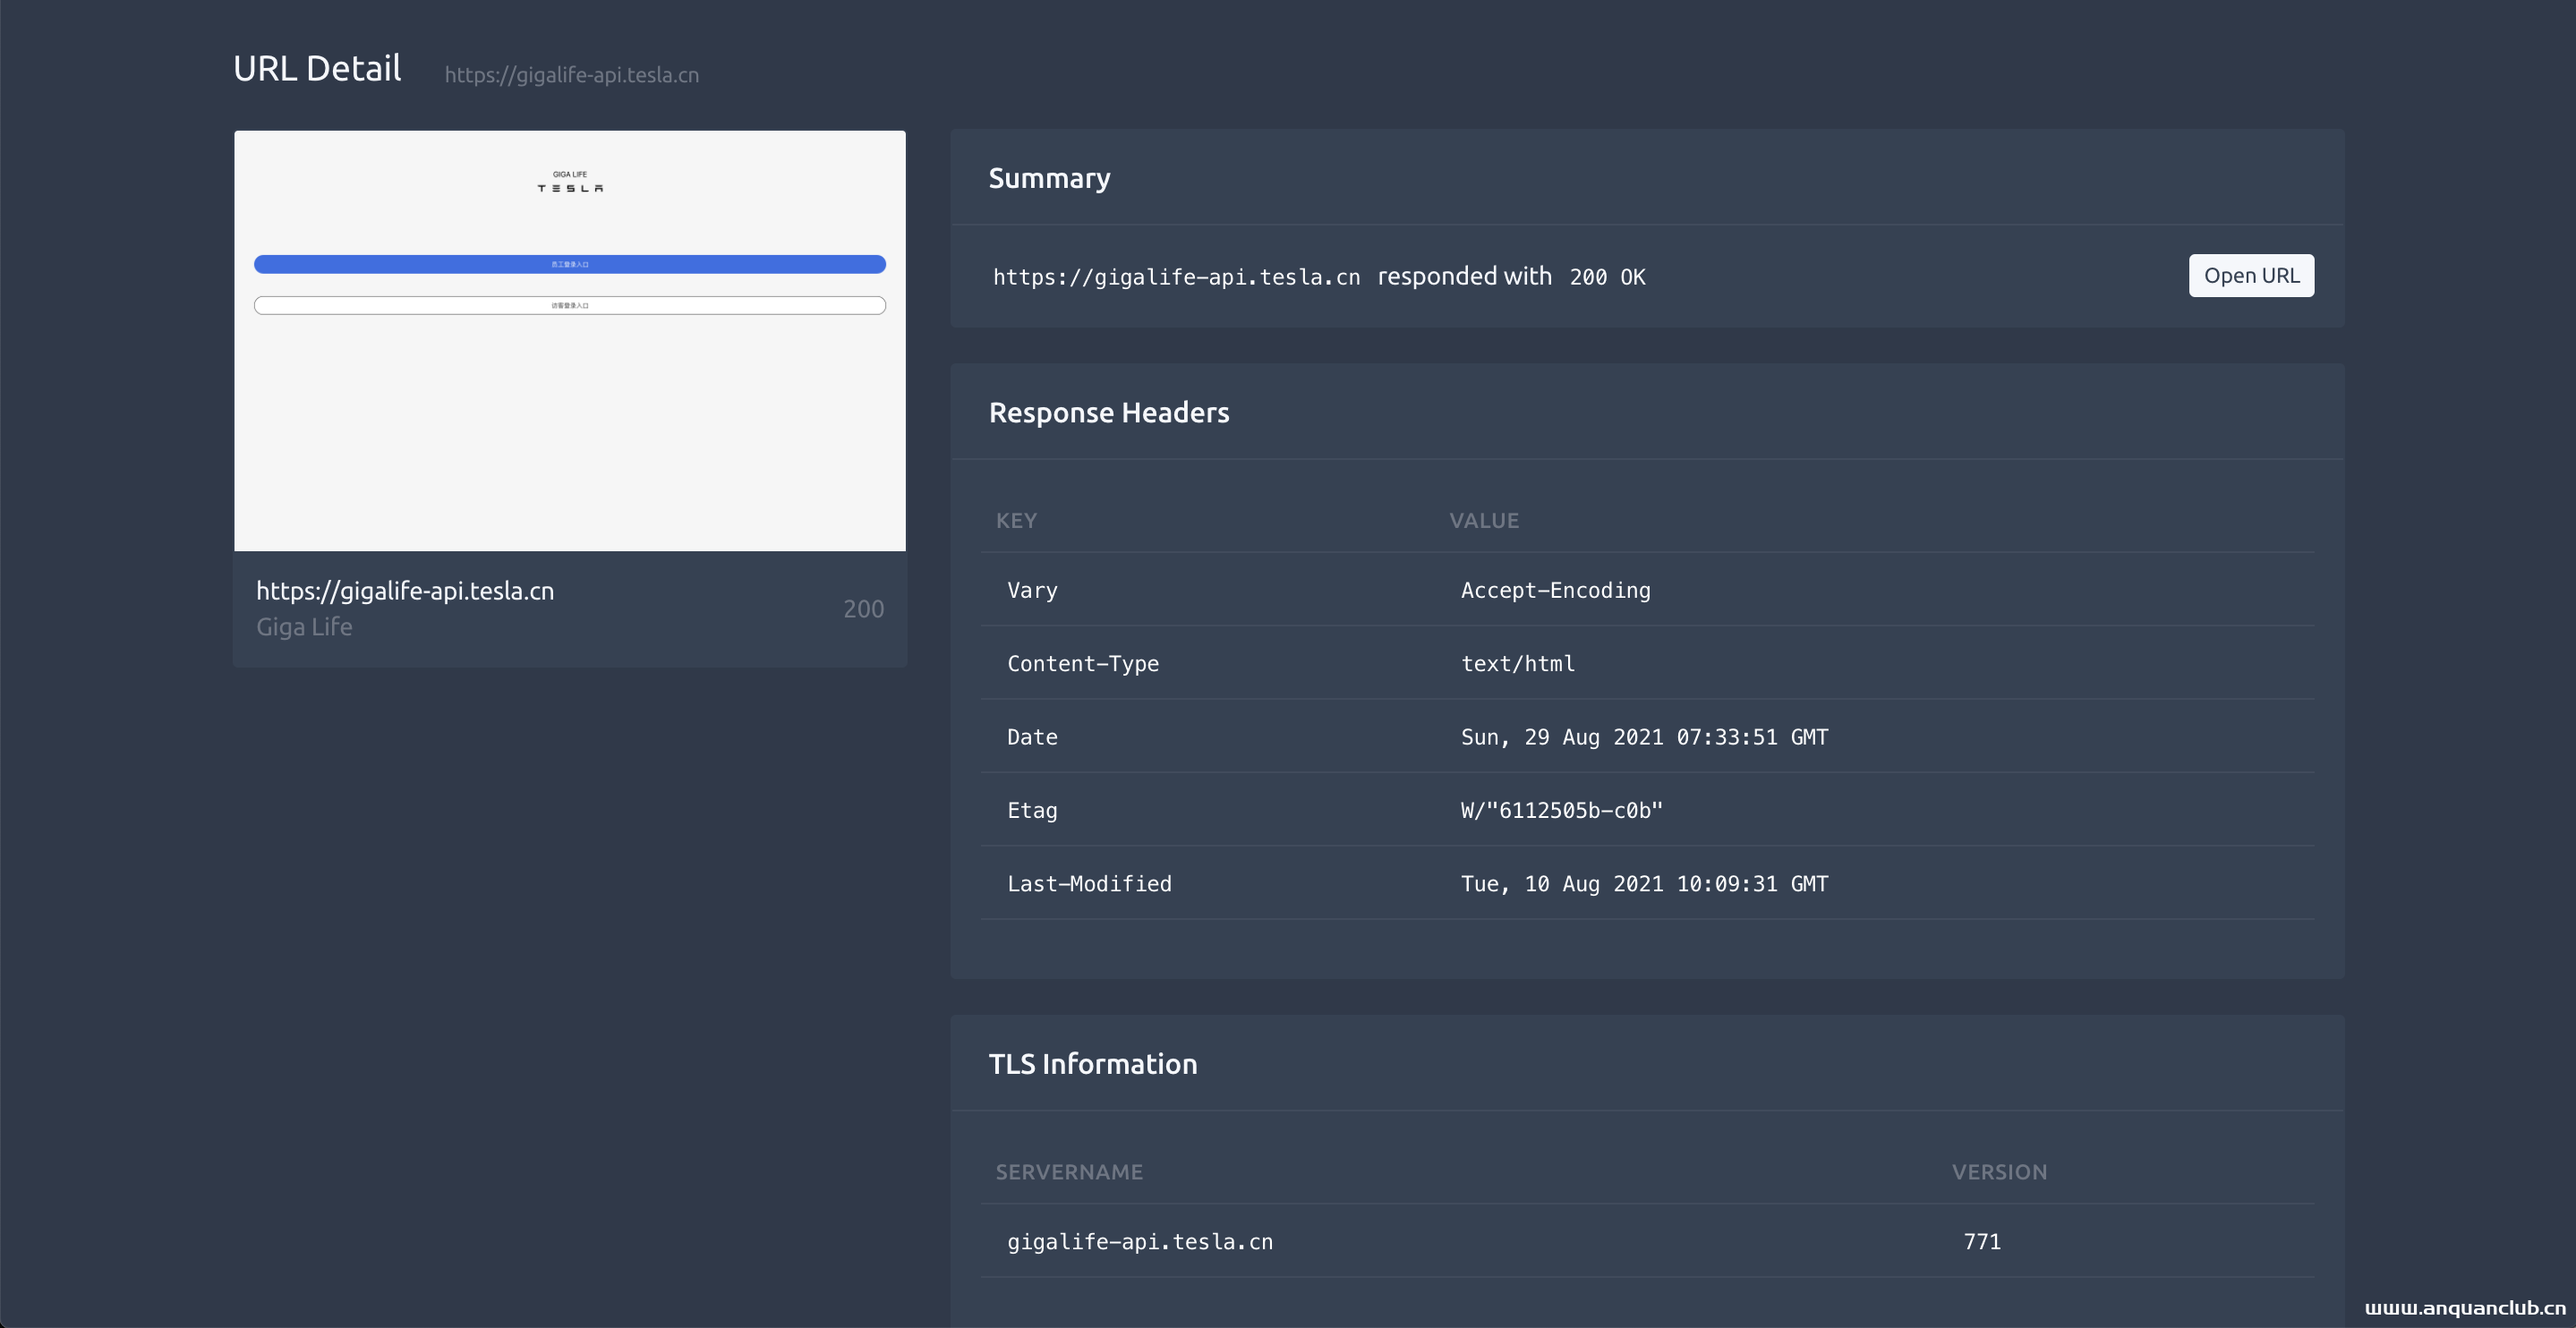
信息收集系列之网站快照
0x01 前言 似乎有20天没更新信息收集系列文章,水一篇。在我们渗透/挖洞过程中,网站快照总能帮我们快速甄别有趣的资产。 市面上也有很多工具可以对网站进行截图,例如aquatone、EyeWitness、go...
2022年3月10日 23:32CVE-2024-24328: TotoLink Router setMacFilterRules – Command Injection
漏洞标题 CVE-2024-24328: TotoLink Router setMacFilterRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vulner...
2024年7月10日 17:17CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover
漏洞标题 CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover 漏洞描述 The Motors theme for WordPress is vulnerable to pri...
2025年12月29日 16:41
bugbounty技巧聚合20211123
漏洞报告 【Shopify 1,600 USD】Staff who only have apps and channels permission can do a takeover account at the wholesale store (Bypass get invitation link) http://hackerone.com/re...
2022年3月10日 23:38CVE-2021-43831: Gradio < 2.5.0 - Arbitrary File Read
漏洞标题 CVE-2021-43831: Gradio < 2.5.0 - Arbitrary File Read 漏洞描述 Files on the host computer can be accessed from the Gradio interface PoC代码
2021年12月2日 15:12
2026年11月10日 11:45
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

