
最新发布第334页

Cacti CVE-2023-39361 SQL注入漏洞
漏洞标题 Cacti CVE-2023-39361 SQL注入漏洞 漏洞描述 Cacti CVE-2023-39361 SQL注入漏洞 日期: 2024-02-07 | 影响软件: Cacti | PoC代码 暂无
 2023年6月15日 21:23
CVE-2023-4490: WordPress Job Portal < 2.0.6 - SQL Injection
漏洞标题 CVE-2023-4490: WordPress Job Portal < 2.0.6 - SQL Injection 漏洞描述 The WP Job Portal WordPress plugin before 2.0.6 does not sanitise and escape the city parameter bef...
2023年11月11日 13:14Cacti CVE-2023-39361 SQL注入漏洞
漏洞标题 Cacti CVE-2023-39361 SQL注入漏洞 漏洞描述 Cacti CVE-2023-39361 SQL注入漏洞 日期: 2024-02-07 | 影响软件: Cacti | PoC代码 暂无
2023年6月28日 02:37CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion
漏洞标题 CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion 漏洞描述 Suprema BioStar before 2.8.2 Video Extension allows remote attackers can read arbitrary files fro...
2020年11月23日 23:07Cisco IOS XE ebui_wsma_http 接口权限绕过漏洞(CVE-2023-20198)
漏洞标题 Cisco IOS XE ebui_wsma_http 接口权限绕过漏洞(CVE-2023-20198) 漏洞描述 Cisco IOS XE 是一个开放灵活的操作系统,针对未来的工作进行了优化。作为适用于企业有线和无线接入、聚合...
2023年9月15日 15:28Arcserve Unified Data Protection CVE-2024-0801 拒绝服务漏洞
漏洞标题 Arcserve Unified Data Protection CVE-2024-0801 拒绝服务漏洞 漏洞描述 Arcserve Unified Data Protection存在拒绝服务漏洞,此漏洞是由于EdgeServiceConsoleImpl接口对用户的请求验...
2024年2月27日 02:04CVE-2016-0957: Adobe AEM Dispatcher <4.15 - Rules Bypass
漏洞标题 CVE-2016-0957: Adobe AEM Dispatcher <4.15 - Rules Bypass 漏洞描述 Dispatcher before 4.1.5 in Adobe Experience Manager 5.6.1, 6.0.0, and 6.1.0 does not properly implemen...
2016年11月16日 17:20CVE-2008-1547: Microsoft OWA Exchange Server 2003 – ‘redir.asp’ Open Redirection
漏洞标题 CVE-2008-1547: Microsoft OWA Exchange Server 2003 - 'redir.asp' Open Redirection 漏洞描述 Open redirect vulnerability in exchweb/bin/redir.asp in Microsoft Outlo...
2008年1月26日 23:12CVE-2023-4116: PHPJabbers Taxi Booking 2.0 – Cross Site Scripting
漏洞标题 CVE-2023-4116: PHPJabbers Taxi Booking 2.0 - Cross Site Scripting 漏洞描述 A vulnerability classified as problematic was found in PHP Jabbers Taxi Booking 2.0. Affected by...
2023年10月7日 07:21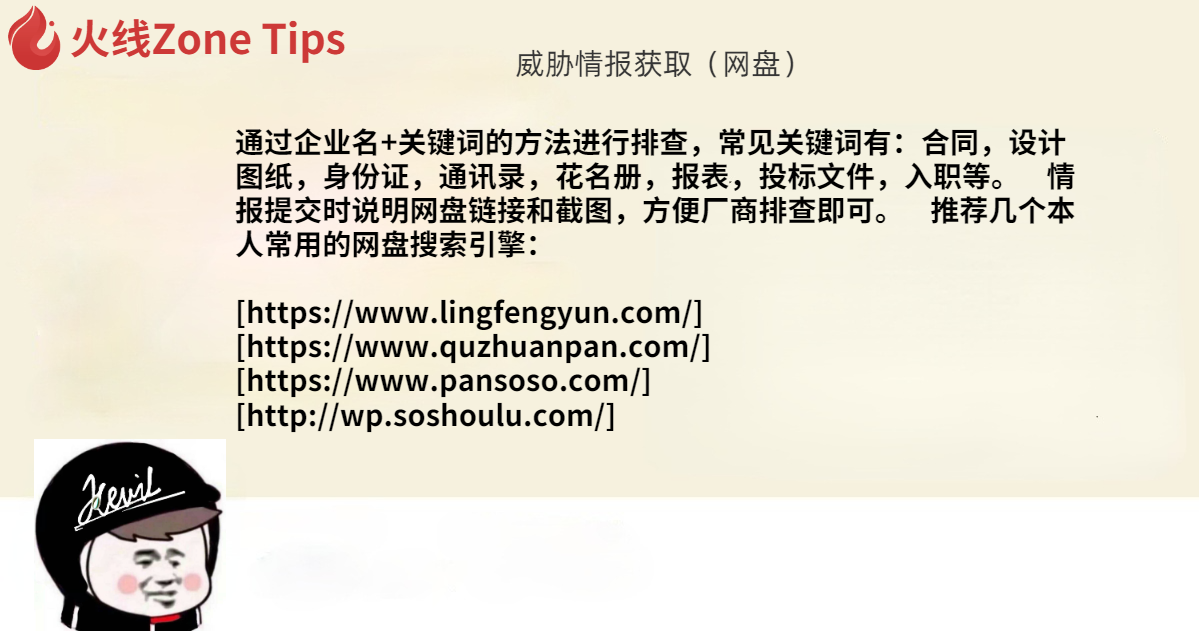
威胁情报获取(网盘)
通过企业名+关键词的方法进行排查,常见关键词有:合同,设计图纸,身份证,通讯录,花名册,报表,投标文件,入职等。 情报提交时说明网盘链接和截图,方便厂商排查即可。 推荐几个本人常用的...
2022年3月10日 23:35CVE-2025-31131: Yeswiki < 4.5.2 - Unauthenticated Path Traversal
漏洞标题 CVE-2025-31131: Yeswiki < 4.5.2 - Unauthenticated Path Traversal 漏洞描述 YesWiki is a wiki system written in PHP. The squelette parameter is vulnerable to path travers...
2025年9月21日 05:45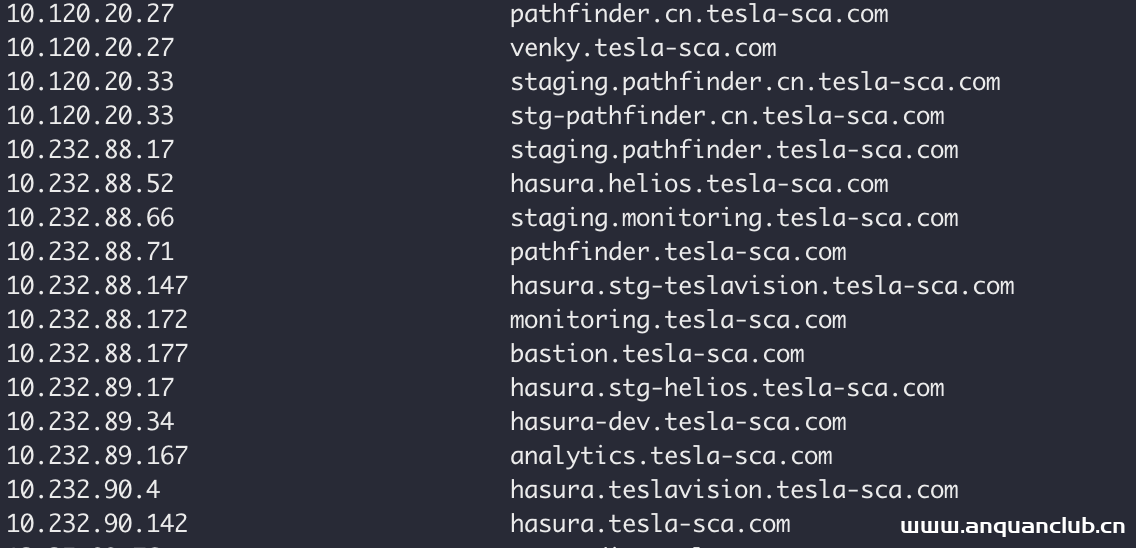
【今日思考题】当我们遇到解析到内网IP的域名的时候,可以干什么?
思考题?:当我们遇到这些解析到内网IP的域名的时候,可以干什么? 提示1: 可参考【搬运工】版块帖子 http://zone.huoxian.cn/t/porter?sort=newest 文字来源于- 火线 Zone-云安全社区,安全小天...
2022年3月10日 23:35CVE-2015-5354: Novius OS 5.0.1-elche – Open Redirect
漏洞标题 CVE-2015-5354: Novius OS 5.0.1-elche - Open Redirect 漏洞描述 Novius OS 5.0.1 (Elche) allows remote attackers to redirect users to arbitrary web sites and conduct phishing...
2015年11月24日 23:24CVE-2022-0148: WordPress All-in-one Floating Contact Form <2.0.4 - Cross-Site Scripting
漏洞标题 CVE-2022-0148: WordPress All-in-one Floating Contact Form <2.0.4 - Cross-Site Scripting 漏洞描述 WordPress All-in-one Floating Contact Form, Call, Chat, and 50+ Social ...
2022年11月10日 00:13CVE-2022-2487: Wavlink WN535K2/WN535K3 – OS Command Injection
漏洞标题 CVE-2022-2487: Wavlink WN535K2/WN535K3 - OS Command Injection 漏洞描述 Wavlink WN535K2 and WN535K3 routers are susceptible to OS command injection which affects unknown co...
2022年10月21日 00:04CRMEB开源商城系统 /api/products 存在SQL注入漏洞(CVE-2024-36837)
漏洞标题 CRMEB开源商城系统 /api/products 存在SQL注入漏洞(CVE-2024-36837) 漏洞描述 CRMEB开源商城系统是一款全开源可商用的系统,前后端分离开发,全部100%开源,在小程序、公众号、H5、APP...
2024年4月21日 17:17
2026年10月18日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

