
最新发布第340页

CVE-2021-24762: WordPress Perfect Survey <1.5.2 - SQL Injection
漏洞标题 CVE-2021-24762: WordPress Perfect Survey <1.5.2 - SQL Injection 漏洞描述 Perfect Survey WordPress plugin before 1.5.2 does not validate and escape the question_id GET p...
 2021年4月25日 23:55
CVE-2021-25028: WordPress Event Tickets < 5.2.2 - Open Redirect
漏洞标题 CVE-2021-25028: WordPress Event Tickets < 5.2.2 - Open Redirect 漏洞描述 WordPress Event Tickets < 5.2.2 is susceptible to an open redirect vulnerability. The plugin...
2021年8月16日 08:02
介绍一个SQL注入自定义payload工具
http://github.com/ggg4566/SQLEXP SQL 注入利用工具,存在waf的情况下自定义编写tamper脚本 dump数据. 对于SQL注入漏洞利用通常情况下我们使用SQLMAP,在waf存在的场景下想利用自己独有的paylo...
2022年3月10日 23:37CVE-2020-9484: Apache Tomcat Remote Command Execution
漏洞标题 CVE-2020-9484: Apache Tomcat Remote Command Execution 漏洞描述 When using Apache Tomcat versions 10.0.0-M1 to 10.0.0-M4, 9.0.0.M1 to 9.0.34, 8.5.0 to 8.5.54 and 7.0.0 to 7...
2020年5月31日 15:15CVE-2024-43971: Sunshine Photo Cart <= 3.2.5 - Reflected Cross-Site Scripting
漏洞标题 CVE-2024-43971: Sunshine Photo Cart <= 3.2.5 - Reflected Cross-Site Scripting 漏洞描述 WP Sunshine Sunshine Photo Cart versions up to 3.2.5 contain a reflected cross-si...
2024年1月2日 02:34CVE-2024-24329: TotoLink Router setPortForwardRules – Command Injection
漏洞标题 CVE-2024-24329: TotoLink Router setPortForwardRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vuln...
2024年9月3日 14:53CVE-2021-46387: Zyxel ZyWALL 2 Plus Internet Security Appliance – Cross-Site Scripting
漏洞标题 CVE-2021-46387: Zyxel ZyWALL 2 Plus Internet Security Appliance - Cross-Site Scripting 漏洞描述 ZyXEL ZyWALL 2 Plus Internet Security Appliance contains a cross-site scrip...
2021年1月2日 12:12CVE-2022-22242: Juniper Web Device Manager – Cross-Site Scripting
漏洞标题 CVE-2022-22242: Juniper Web Device Manager - Cross-Site Scripting 漏洞描述 Juniper Web Device Manager (J-Web) in Junos OS contains a cross-site scripting vulnerability. Th...
2022年1月16日 05:10CVE-2014-4544: Podcast Channels < 0.28 - Cross-Site Scripting
漏洞标题 CVE-2014-4544: Podcast Channels < 0.28 - Cross-Site Scripting 漏洞描述 The Podcast Channels WordPress plugin was affected by an unauthenticated reflected cross-site scr...
2014年12月29日 11:06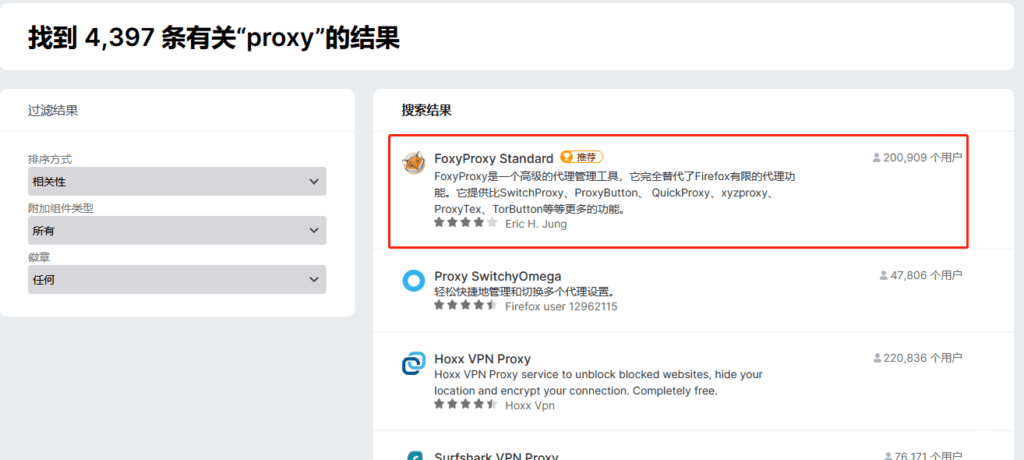
squid代理服务器+认证+浏览器扩展分流
squid代理服务器+认证+浏览器扩展分流 1.安装squidUbuntusudo apt-get updatesudo apt-get install squidcentossudo yum updatesudo yum install squid2.安装htpass工具htpasswd 是 Apache HTT...
 2024年1月27日 15:56
CVE-2020-11530: WordPress Chop Slider 3 – Blind SQL Injection
漏洞标题 CVE-2020-11530: WordPress Chop Slider 3 - Blind SQL Injection 漏洞描述 WordPress Chop Slider 3 plugin contains a blind SQL injection vulnerability via the id GET parameter...
2020年4月10日 12:44CVE-2023-2252: Directorist < 7.5.4 - Local File Inclusion
漏洞标题 CVE-2023-2252: Directorist < 7.5.4 - Local File Inclusion 漏洞描述 Directorist before 7.5.4 is susceptible to Local File Inclusion as it does not validate the file para...
2023年1月25日 05:56CVE-2021-24827: WordPress Asgaros Forum <1.15.13 - SQL Injection
漏洞标题 CVE-2021-24827: WordPress Asgaros Forum <1.15.13 - SQL Injection 漏洞描述 WordPress Asgaros Forum plugin before 1.15.13 is susceptible to SQL injection. The plugin does...
2021年9月8日 21:22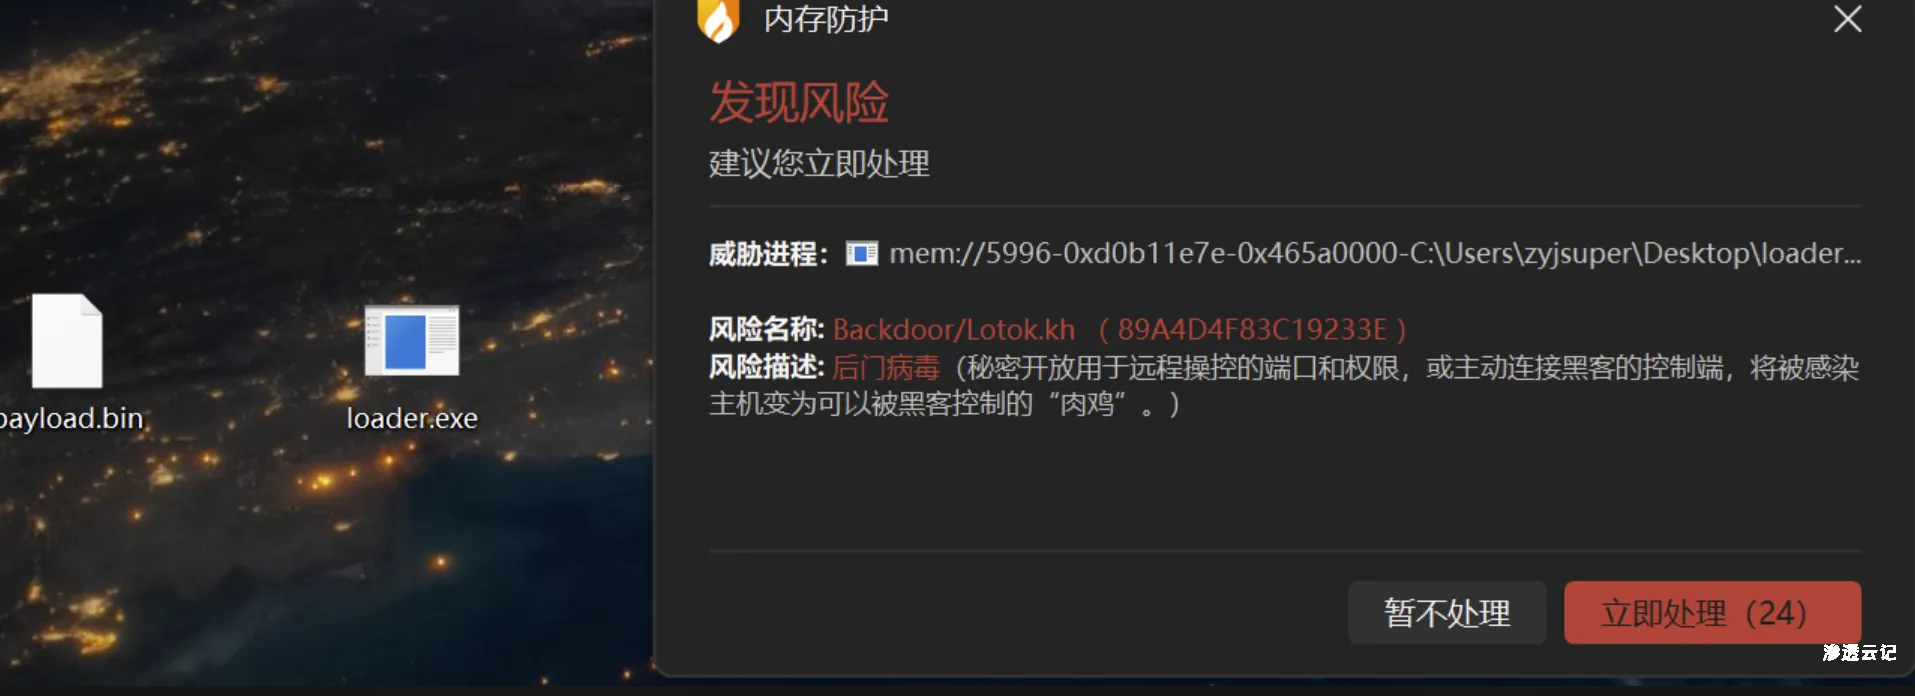
【工具更新】EasyShell v2.6 版本更新,1. 新增邮件钓鱼模块,支持stageless客户端一键添加邮件压缩包、2.修复shellcode内存告警情况等bug
更新说明 感谢各位师傅们的热心测试,发现了诸多bug,目前已经修复的有: 修复shellcode执行火绒内存告警的bug 优化屏幕截屏,设置为低中高三挡 优化文件管理展示 更新linux旧系统交互式shell执...

 2026年8月5日 23:23
CVE-2024-1512: MasterStudy LMS WordPress Plugin <= 3.2.5 - SQL Injection
漏洞标题 CVE-2024-1512: MasterStudy LMS WordPress Plugin <= 3.2.5 - SQL Injection 漏洞描述 The MasterStudy LMS WordPress Plugin for Online Courses and Education plugin for WordP...
2024年7月8日 12:55CVE-2020-3952: VMware vCenter Server LDAP Broken Access Control
漏洞标题 CVE-2020-3952: VMware vCenter Server LDAP Broken Access Control 漏洞描述 Under certain conditions, vmdir that ships with VMware vCenter Server, as part of an embedded or e...
2020年2月15日 21:35
2026年10月18日 11:45
2026年10月18日 11:45
漏洞复现
漏洞复现,安全小天地的技术文章仅供参考,此文所提供的信息只为网络安全人员对自己所负责的网站、服务器等(包括但不限于)进行检测或维护参考,未经授权请勿利用文章中的技术资料对任何计算机系统进行入侵操作。利用此文所提供的信息而造成的直接或间接后果和损失,均由使用者本人负责。本文所提供的工具仅用于学习,禁止用于其他!!!
2026年4月23日 14:09
2026年3月6日 17:21
2026年3月1日 15:46
2026年2月13日 12:53

2026年10月18日 20:40
2026年9月20日 16:22
2026年8月16日 20:18
渗透测试实战
在渗透测试项目中,外网的信息收集是至关重要的一个环节,外网打点信息收集全面了,可能会有四两拨千斤效果,直接突破外网边界进入内网。 子域名是域名信息收集的一个重要部分,在防御措施严密情况下我们无法直接拿下主域名,那么就可以采用迂回战术拿下子域名,然后无限靠近主域名。
2026年4月24日 17:11
2026年4月7日 21:49
2026年3月2日 20:39
2026年2月13日 12:53

